
subzy
 pentestpad/subzy
Subdomain takeover vulnerability checker
misconfigurationpenetration-testingreconnaissance+2
pentestpad/subzySubdomain takeover vulnerability checker
 dc4ts/changetower
Lightweight web page change monitor written in Go. Detects updates on target URLs and sends notifications via Telegram or other services, ideal for…
 jul10l1r4/getrails
Get trails lib: Get all urls indexed of target
 crowsec-edtech/cve-2026-87902
Python PoC exploiting CVE-2026-87902, an unauthenticated path traversal in WordPress locate_template() leading to LFI and PEAR-based RCE, with safe…
 mheranco/cve-2025-44136
Proof-of-concept exploit for unauthenticated reflected XSS in MapTiler Tileserver-php v2.0 via the 'layer' GET parameter, enabling arbitrary HTML/JS…
 orange0mint/cve-2025-10035_goanywhere
CVE-2025-10035_GoAnywhere Get RCE
 hacip/cve-2023-33405
Proof-of-concept exploit for an open redirect vulnerability (CVE-2023-33405) in BlogEngine.NET CMS versions 3.3.8.0 and earlier, demonstrating…
 fauzanwijaya/cve-2002-0748
Proof of concept for LabVIEW Web Server HTTP Get Newline DoS vulnerability
 dgtlmoon/changedetection.io
Best and simplest tool for website change detection, web page monitoring, and website change alerts. Perfect for tracking content changes, price…
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
 shinthink/cve-2026-15282
Instant Appointment <= 1.2 — Unauthenticated Arbitrary File Upload to RCE via add_service_front AJAX | CVSS 9.8
 permanet/permanet
Cryptographically verifiable web archiving. Playwright capture → SHA-256 Merkle hash → Bitcoin-anchored OpenTimestamps → permanent Arweave storage.
 itinerisltd/trellis-cve-2018-6389
Mitigate CVE-2018-6389 WordPress load-scripts / load-styles attacks
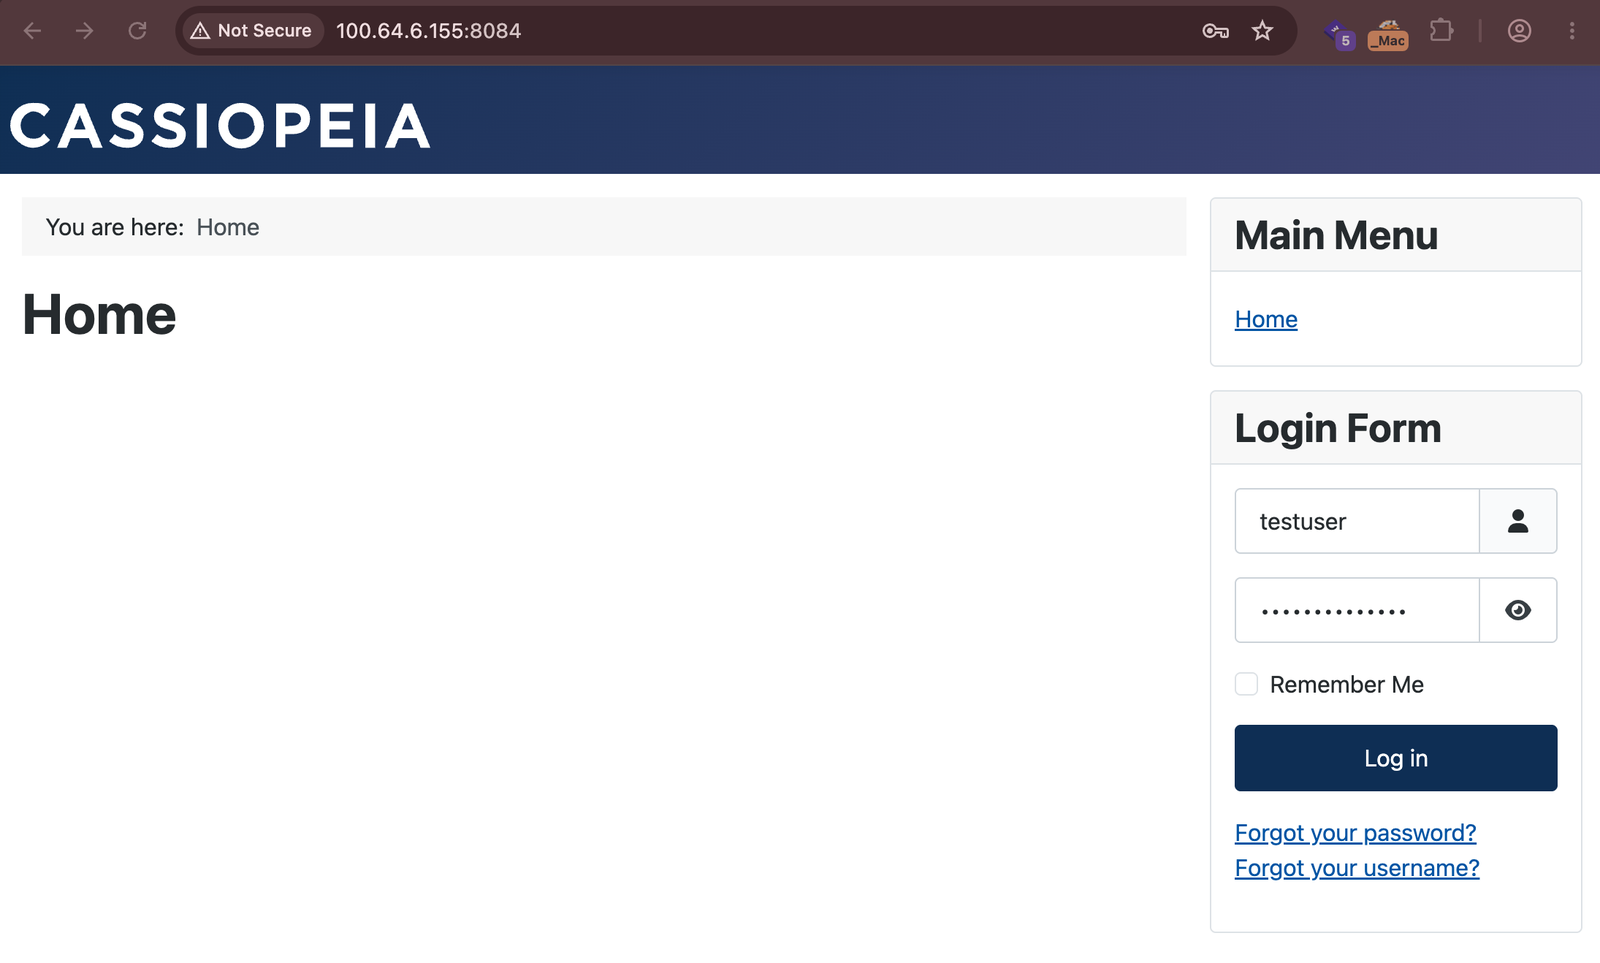 toanln-cov/cve-2026-76569
Reflected XSS via search GET Parameter in Phoca Download
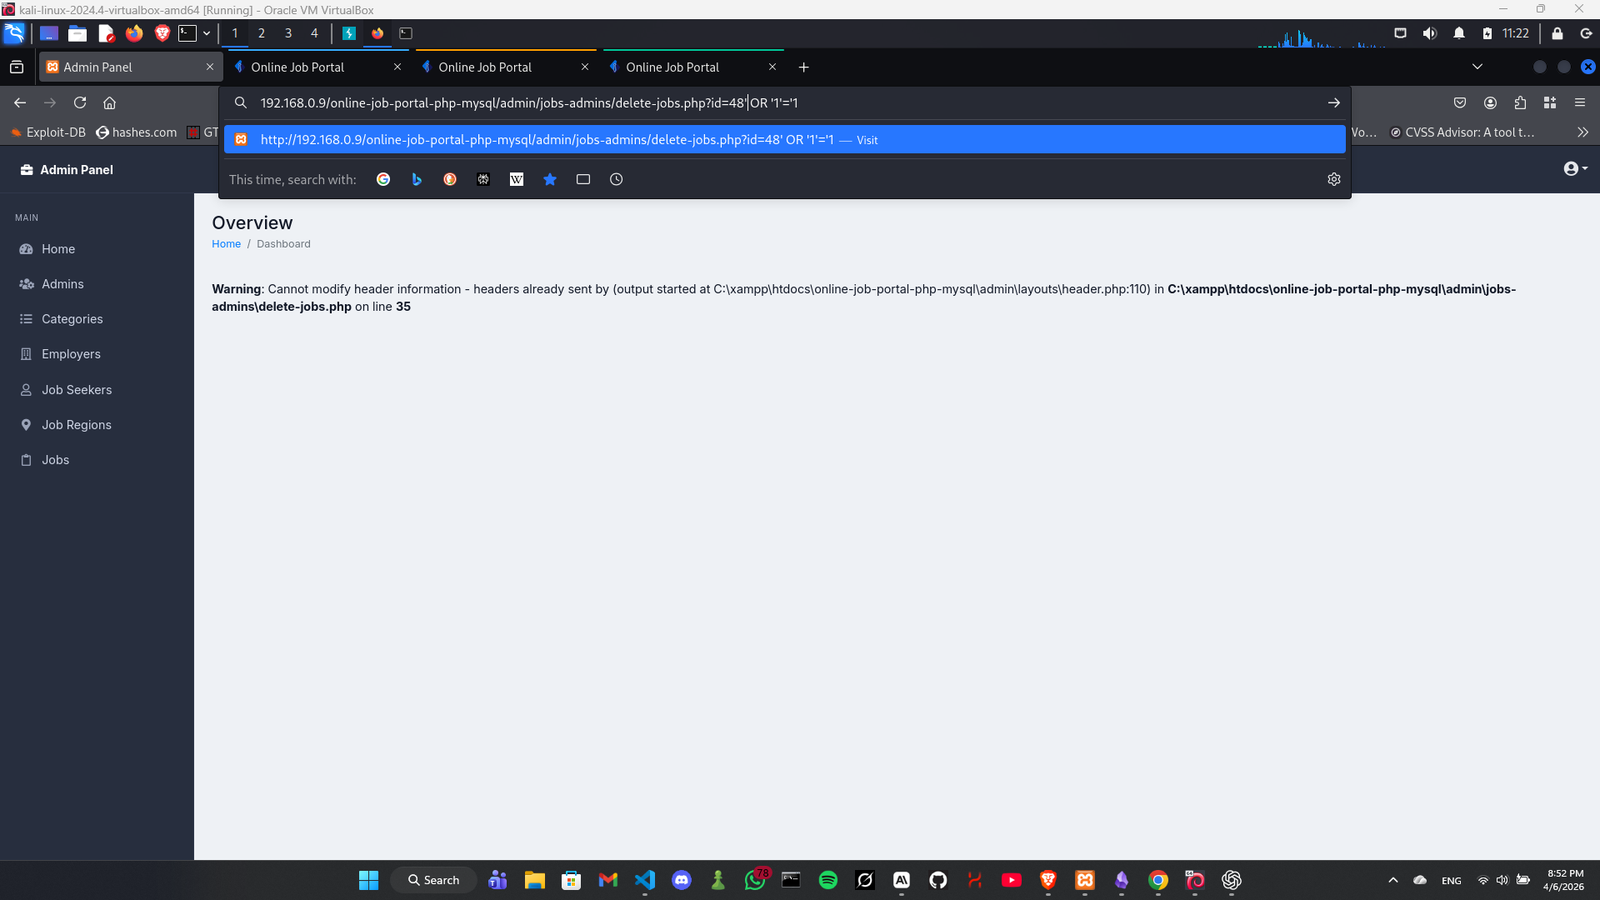 xmyronn/cve-2026-7028-sqli
Proof-of-concept exploit for SQL injection in CodeAstro Online Job Portal allowing authenticated deletion of all job records via crafted GET request.
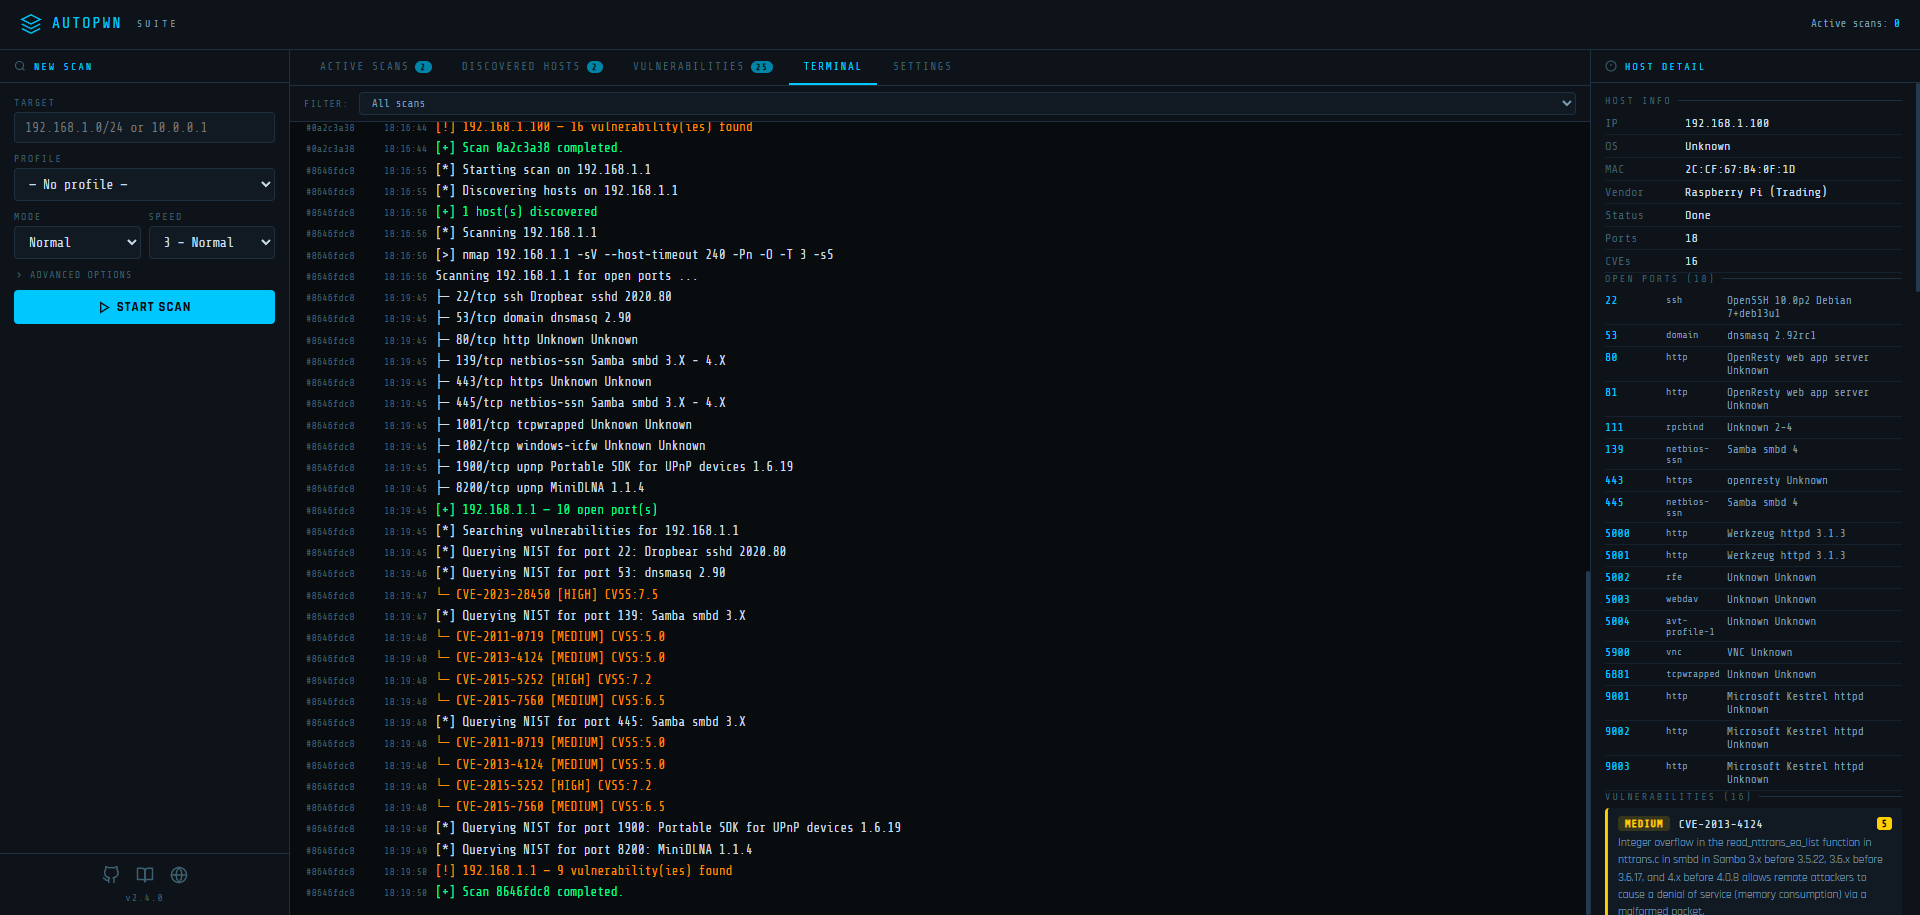 gamehunterkaan/autopwn-suite
AutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.
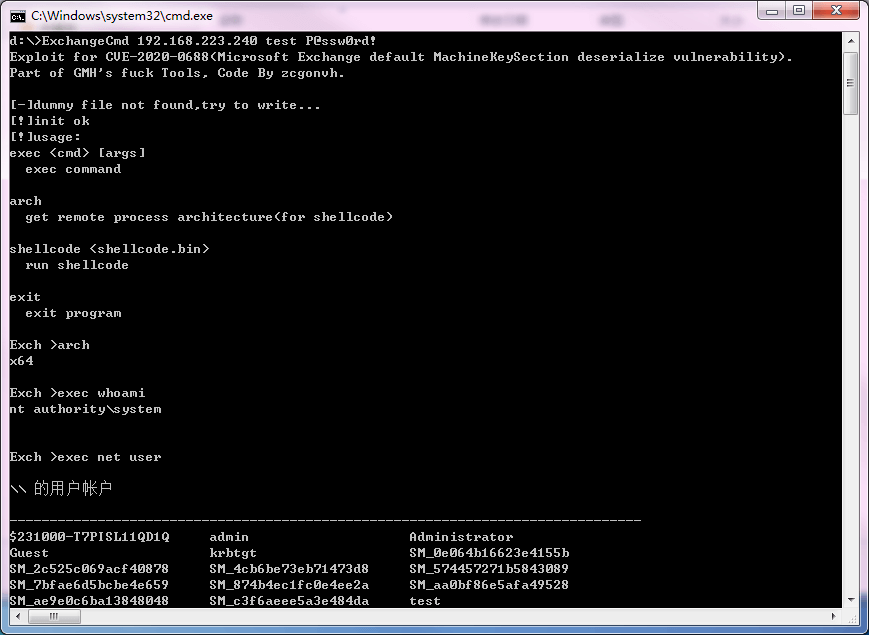 zcgonvh/cve-2020-0688
Exploit and detect tools for CVE-2020-0688
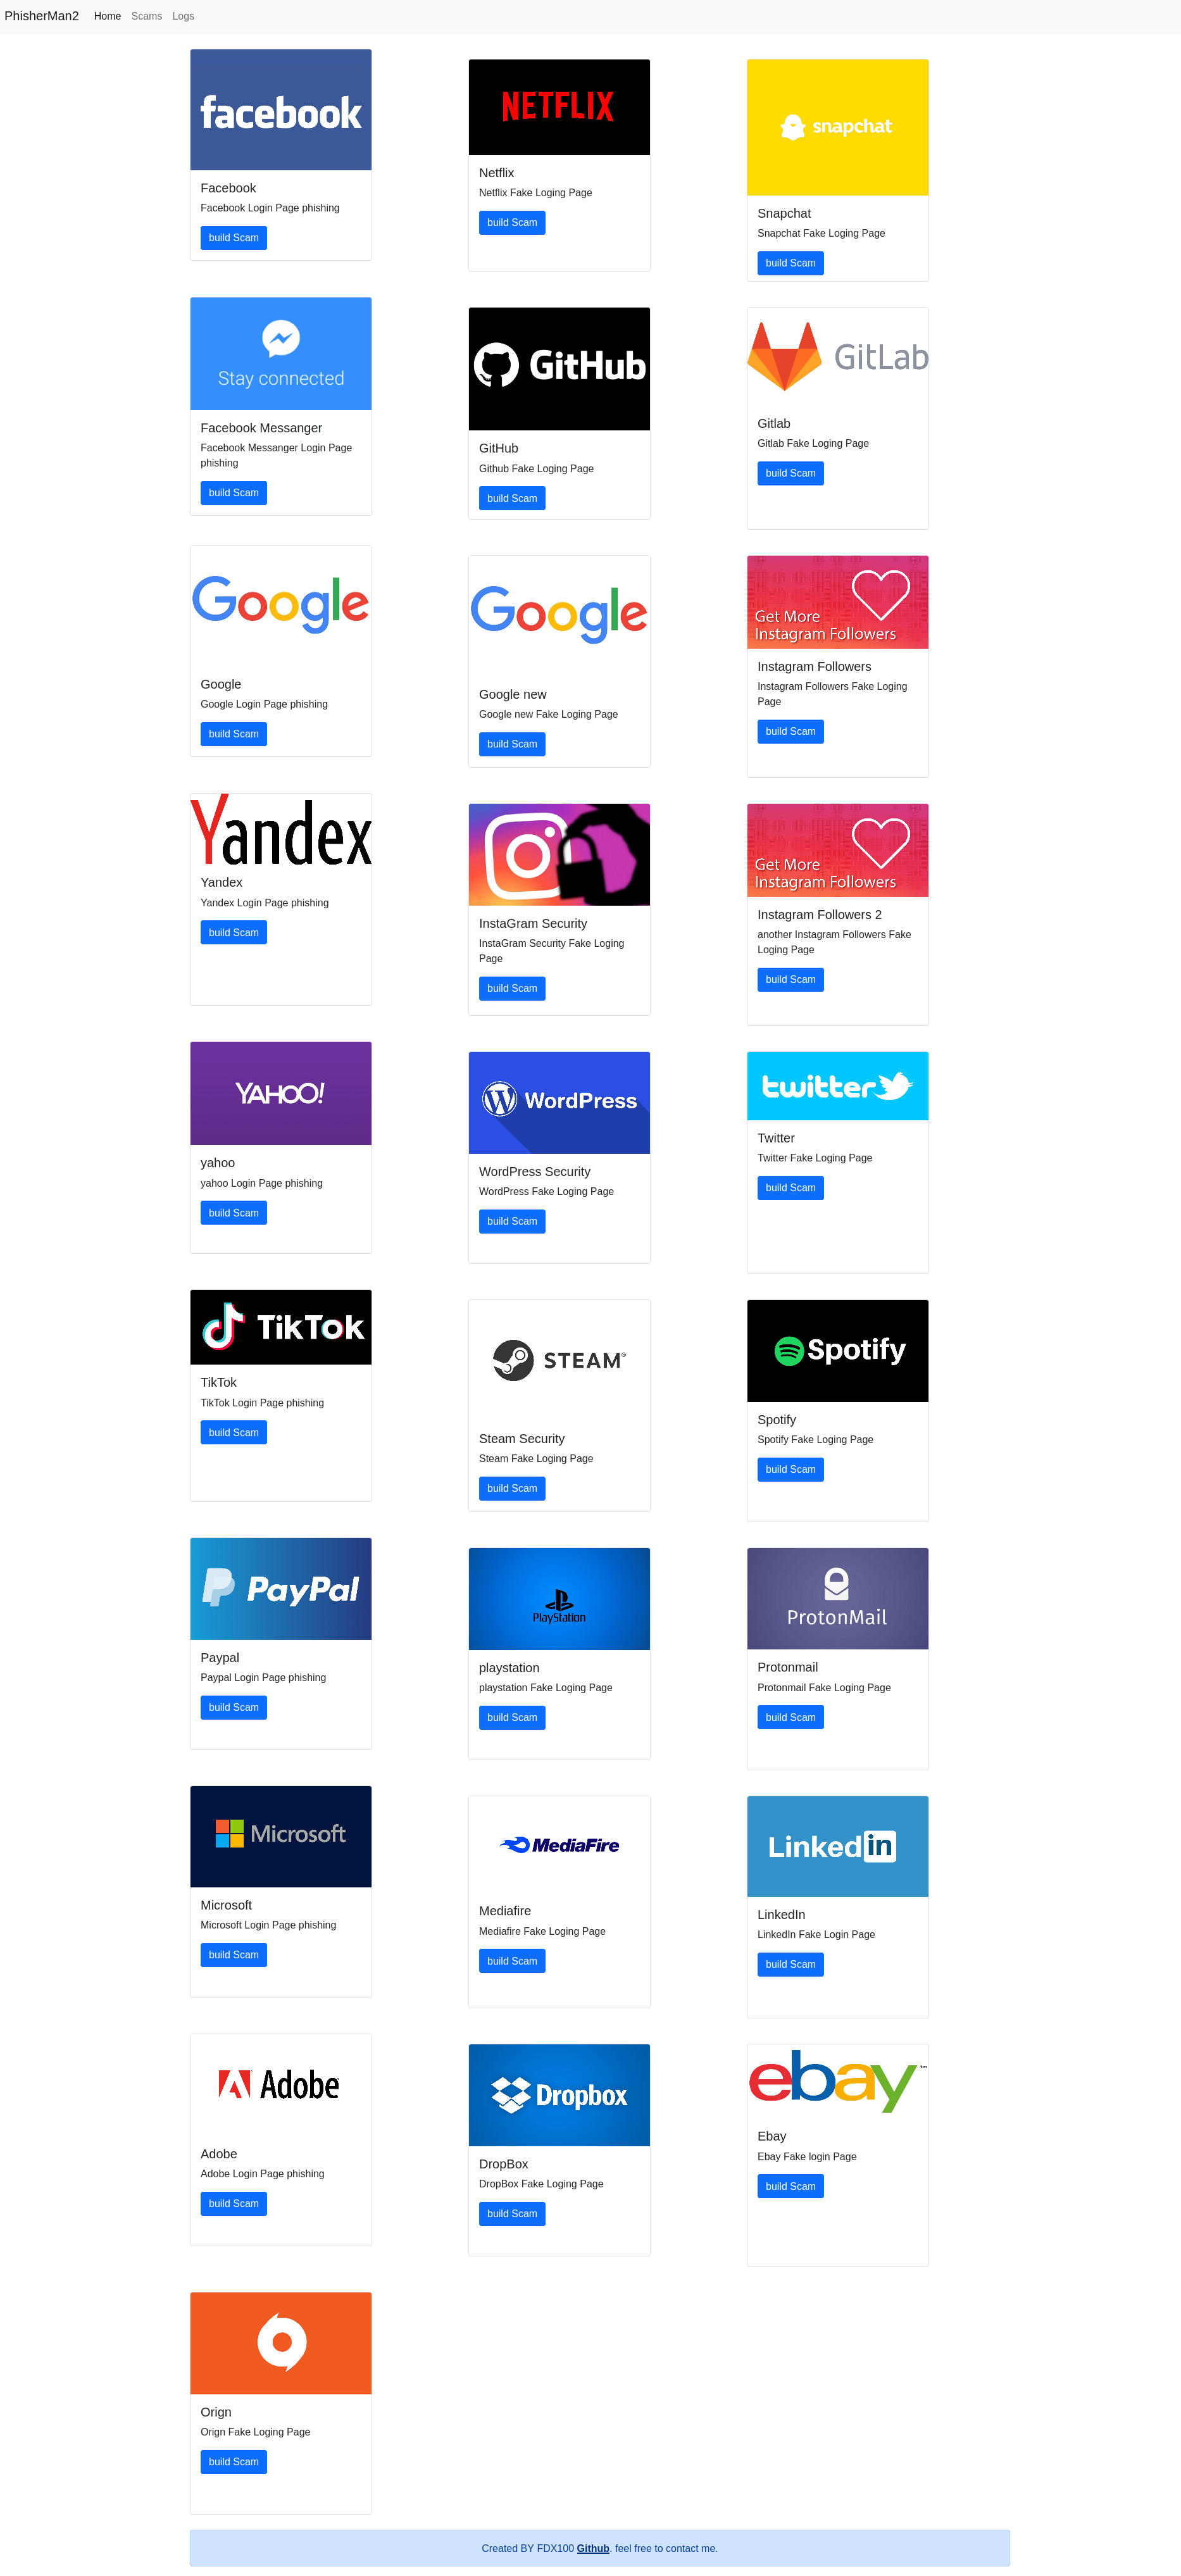 fdx100/phisher-man
Samples Phishing tools made for Linux it contains 30 different type of Phishing Pages made with flask