

CVE-2022-21907-Vulnerability-PoC
 michelep/cve-2022-21907-vulnerability-poc
CVE-2022-21907 Vulnerability PoC
exploitationpenetration-testingremote-access-tool+2
28
michelep/cve-2022-21907-vulnerability-pocCVE-2022-21907 Vulnerability PoC
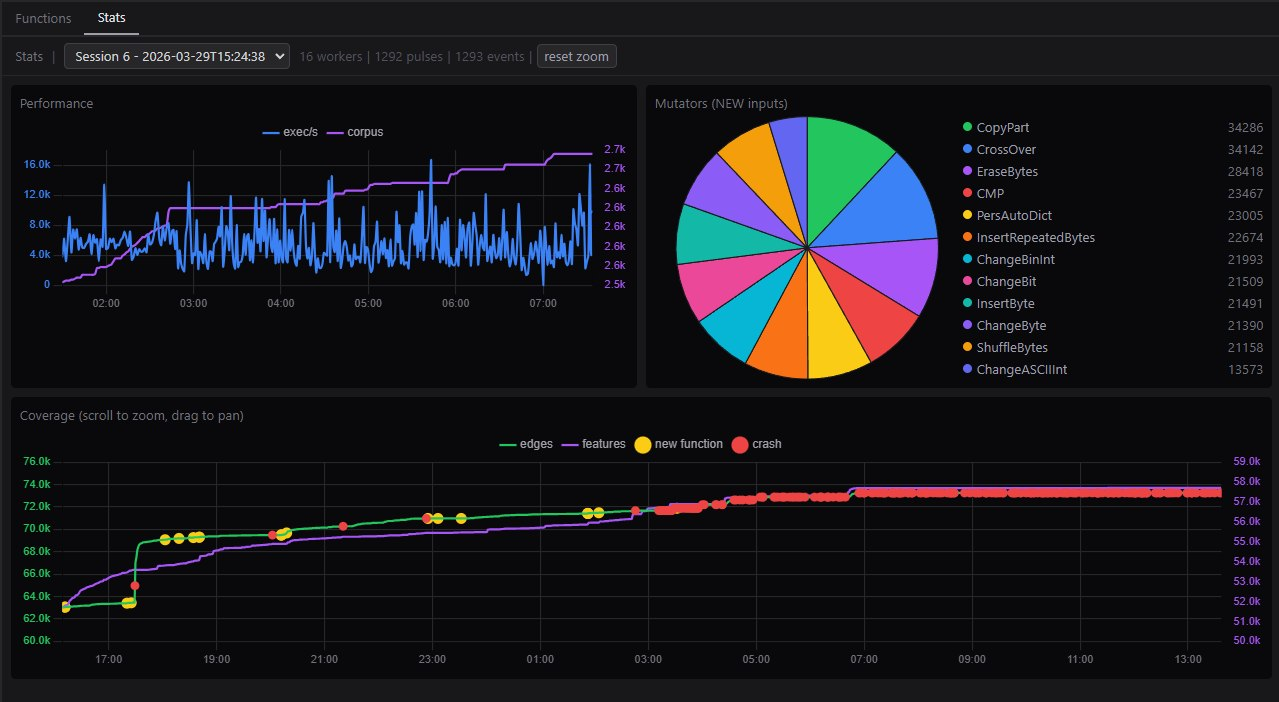 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server
 cappricio-securities/burpflow
BurpFlow is one of the best Burp Suite automation tools for bug bounty hunters and penetration testers, widely used to load recon data via proxy and…
 michele0303/undetected-httpx
Stop getting 403 Forbidden. A specialized httpx-like toolkit for WAF evasion.
 r3dxpl0it/rtspserver-code-execution-vulnerability
RTSPServer Code Execution Vulnerability CVE-2018-4013
 soltanali0/cve-2024-40725
exploit CVE-2024-40725 (Apache httpd) with
 zemarkhos/cve-2025-55315-poc-exploit
CVE-2025-55315 PoC Exploit
 rhasan-com/cve-2026-23918
Apache HTTP/2 double-free vulnerability PoC (CVE-2026-23918)
 zha0gongz1/cve-2021-31166
PoC for CVE-2021-31166, a remote HTTP.sys use-after-free triggered remotely. Although it was defined as remote command execution, it can only cause…
 jfoz1010/cve-2024-24549
Proof of concept of the CVE-2024-24549, Exploit in Python.
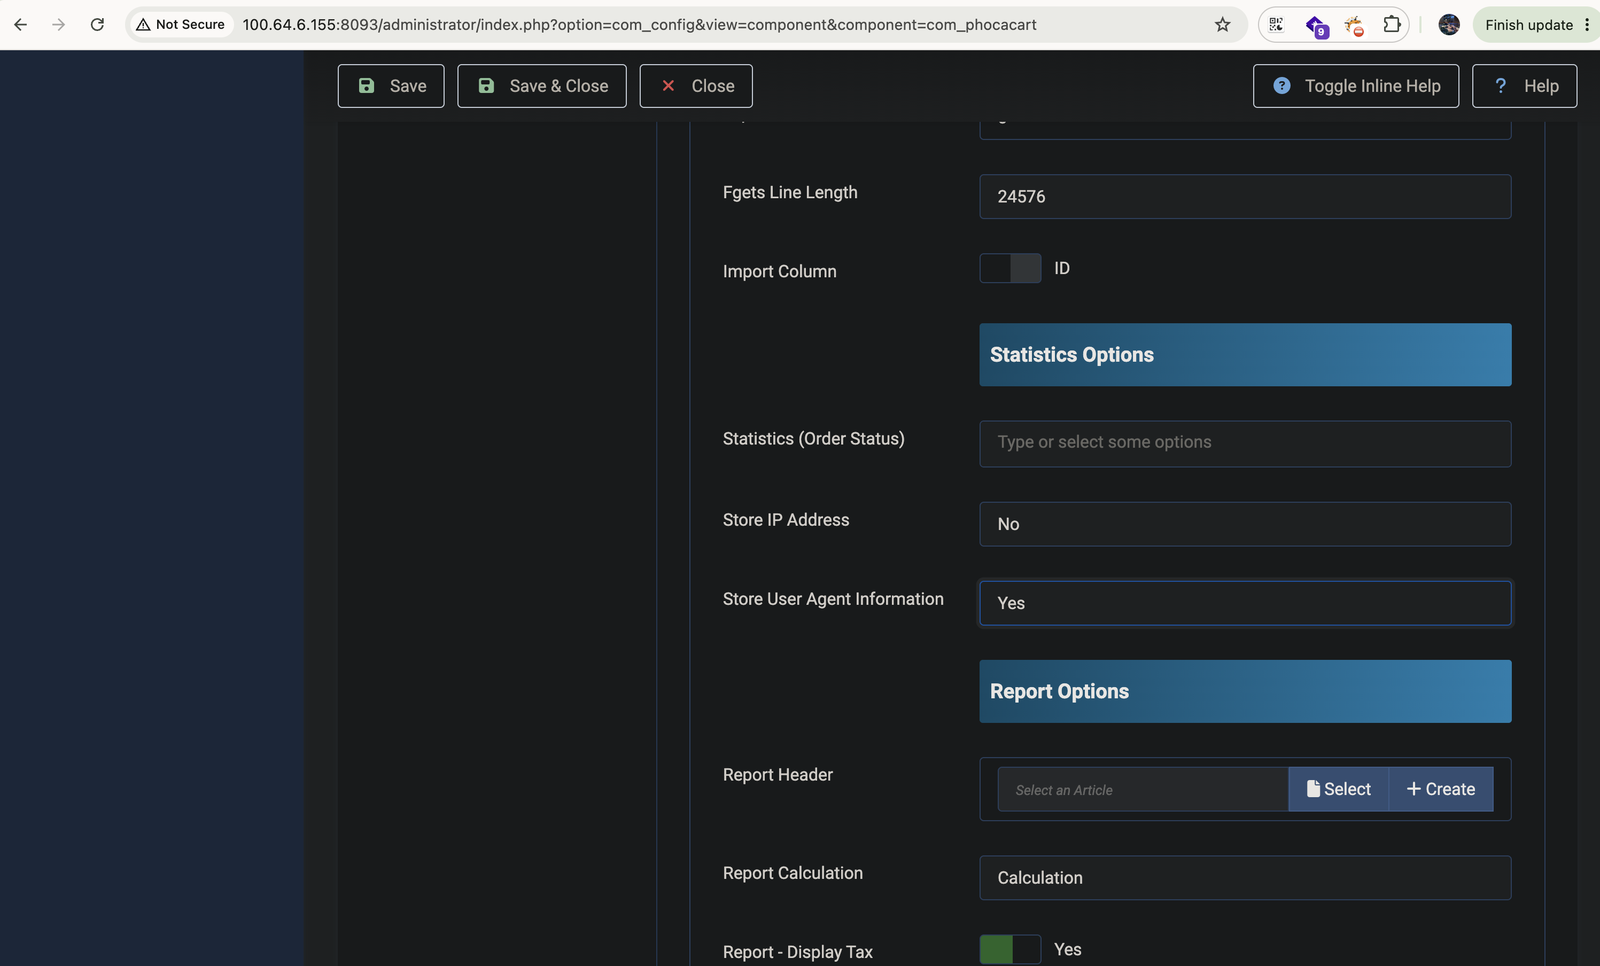 toanln-cov/cve-2026-76564
Stored XSS via User-Agent in Admin Order View in PhocaCart
 samael0x4/cve-2026-21962
Unauthenticated vulnerability that may allow remote attackers to compromise confidentiality and integrity, potentially leading to full system…
 oscerd/cve-2026-66908
Proof-of-concept reproducer for Apache Camel JWT authentication bypass (CVE-2026-66908) demonstrating missing iss/aud validation in…
 cynepmyx/nginx-rift-check
Detects the CVE-2026-42945 rewrite pattern in nginx configs: rewrite with ? in the replacement plus an unnamed capture consumed in the same location
 sanr01/cve-2021-41773-exploit-lab
CVE-2021-41773 Exploit Lab
 nu0l/nginx-rift
CVE-2026-42945 NGINX 堆溢出漏洞扫描与验证工具