
Log4j_CVE-2021-44228
 vorburger/log4j_cve-2021-44228
Curated resource hub for Log4j CVE-2021-44228, covering detection, mitigation, exploitation, and dependency management strategies for the critical…
curated-resourceseducationexploitation+3
3
vorburger/log4j_cve-2021-44228Curated resource hub for Log4j CVE-2021-44228, covering detection, mitigation, exploitation, and dependency management strategies for the critical…
 e4zyy/project-cve-2026-65351
Browser resource exhaustion payload that crashes target systems via memory, GPU, audio, and rendering overload. Designed for authorized security…
 brynax/cve-2026-50787
Security advisory detailing CVE-2026-50787, an uncontrolled resource consumption vulnerability in e-SIC Livre CAPTCHA generation, enabling remote…
 fdjy1234/cve-2022-41404-dos-protection
Windows Apache Tomcat resource limits implementation guide for CVE-2022-41404 DoS vulnerability protection
 f4rber/cve-2020-36287
The dashboard gadgets preference resource of the Atlassian gadgets plugin used in Jira Server and Jira Data Center before version 8.13.5, and from…
 aeyesec/cve-2024-27316_poc
Proof-of-concept exploit for CVE-2024-27316, an HTTP/2 CONTINUATION flood vulnerability in Apache httpd, demonstrating resource exhaustion via…
 ixsly/cve-2022-41401
Proof-of-concept exploit for CVE-2022-41401, a server-side request forgery (SSRF) vulnerability in OpenRefine <= v3.5.2, enabling unauthorized…
 kirubel-cve/cve-2026-36957
Proof-of-concept for CVE-2026-36957, a denial-of-service vulnerability in Dbit Router firmware via HTTP flood on the Boa web server, causing resource…
 shaheryar773/mitigate-cve-2026-23869-react-server-component-loops
Technical troubleshooting repository for fixing infinite rendering vulnerability loops and resource exhaustion threats under CVE-2026-23869 cleanly.
 g-rubert/wordpress_dos
Proof-of-concept for Denial of Service (DoS) attacks against WordPress 4.9.8 and 5.5 via unauthenticated requests to vulnerable admin pages, causing…
 echosecure/vuln-chain-lab
PoC Docker lab: chaining file upload bypass + stored XSS to create admin accounts. Educational resource for pen testers.
 saykino/cve-2025-56223
Documentation of CVE-2025-56223, a denial-of-service vulnerability in Ascertia SigningHub's Upload Document API, allowing unrestricted file uploads…
 shoucheng3/undertow-io__undertow_cve-2014-7816_1-0-16-final
Proof-of-concept exploit for CVE-2014-7816 targeting Undertow Java web server, demonstrating a directory traversal vulnerability in the HTTP server's…
 dovankha/cve-2024-35468
Proof-of-concept exploit for SQL injection vulnerability in SourceCodester Human Resource Management System 1.0, enabling unauthenticated admin login…
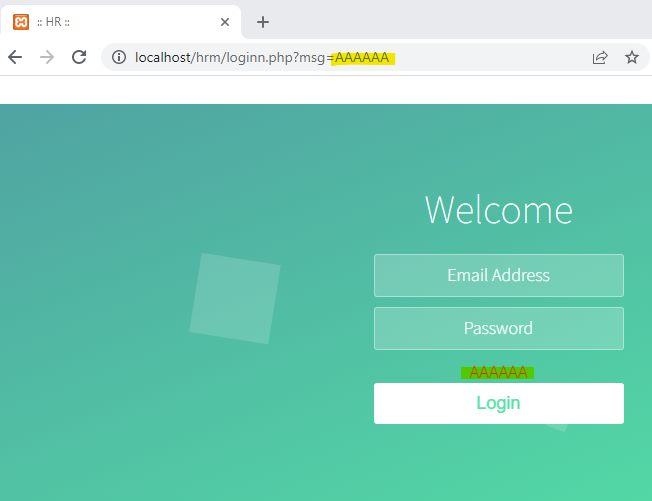 nursec747/cve-2022-46104---poc
Proof-of-concept exploit for CVE-2022-46104 demonstrating a reflected XSS vulnerability in the Human Resource Management System login page.
 dovankha/cve-2024-34221
Proof-of-concept for CVE-2024-34221: insecure permission vulnerability in SourceCodester Human Resource Management System 1.0 allowing unauthorized…
 redfox-security/unveiling-moniker-link-cve-2024-21413-navigating-the-latest-cybersecurity-landscape
Educational resource analyzing CVE-2024-21413 (Moniker Link) and its implications, providing insights into the vulnerability and broader…
 borewit/svg-sanitizer
Java library that sanitizes SVG files by stripping JavaScript, inline event handlers, and script tags while blocking external resource loading to…