owasp-java-encoder
The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…

The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…

OWASP knowledge base and validator for HTTP security response headers, providing recommendations, statistics, and automated configuration checks.

The OWASP SecureTea Project provides a one-stop security solution for various devices (personal computers / servers / IoT devices)

⚠️ This repo is no longer in use. Please refer to https://github.com/OWASP/www-project-vulnerable-web-applications-directory

The WASM Based Security Toolkit for the Web First Paradigm

Intentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…

The Web Security Testing Guide is a comprehensive Open Source guide to testing the security of web applications and web services.

Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…

Curated directory of Node.js security tools, static analyzers, vulnerability scanners, and educational resources covering OWASP Top 10, supply chain…

Modular penetration testing framework integrating multiple tools for automated web application security assessment, aligned with OWASP Testing Guide,…

OWASP Mutillidae II is a free, open-source, deliberately vulnerable web application providing a target for web-security training. This is an…

bluemonday: a fast golang HTML sanitizer (inspired by the OWASP Java HTML Sanitizer) to scrub user generated content of XSS

vAPI is Vulnerable Adversely Programmed Interface which is Self-Hostable API that mimics OWASP API Top 10 scenarios through Exercises.

The Secure Coding Dojo is a platform for delivering secure coding knowledge.

YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…

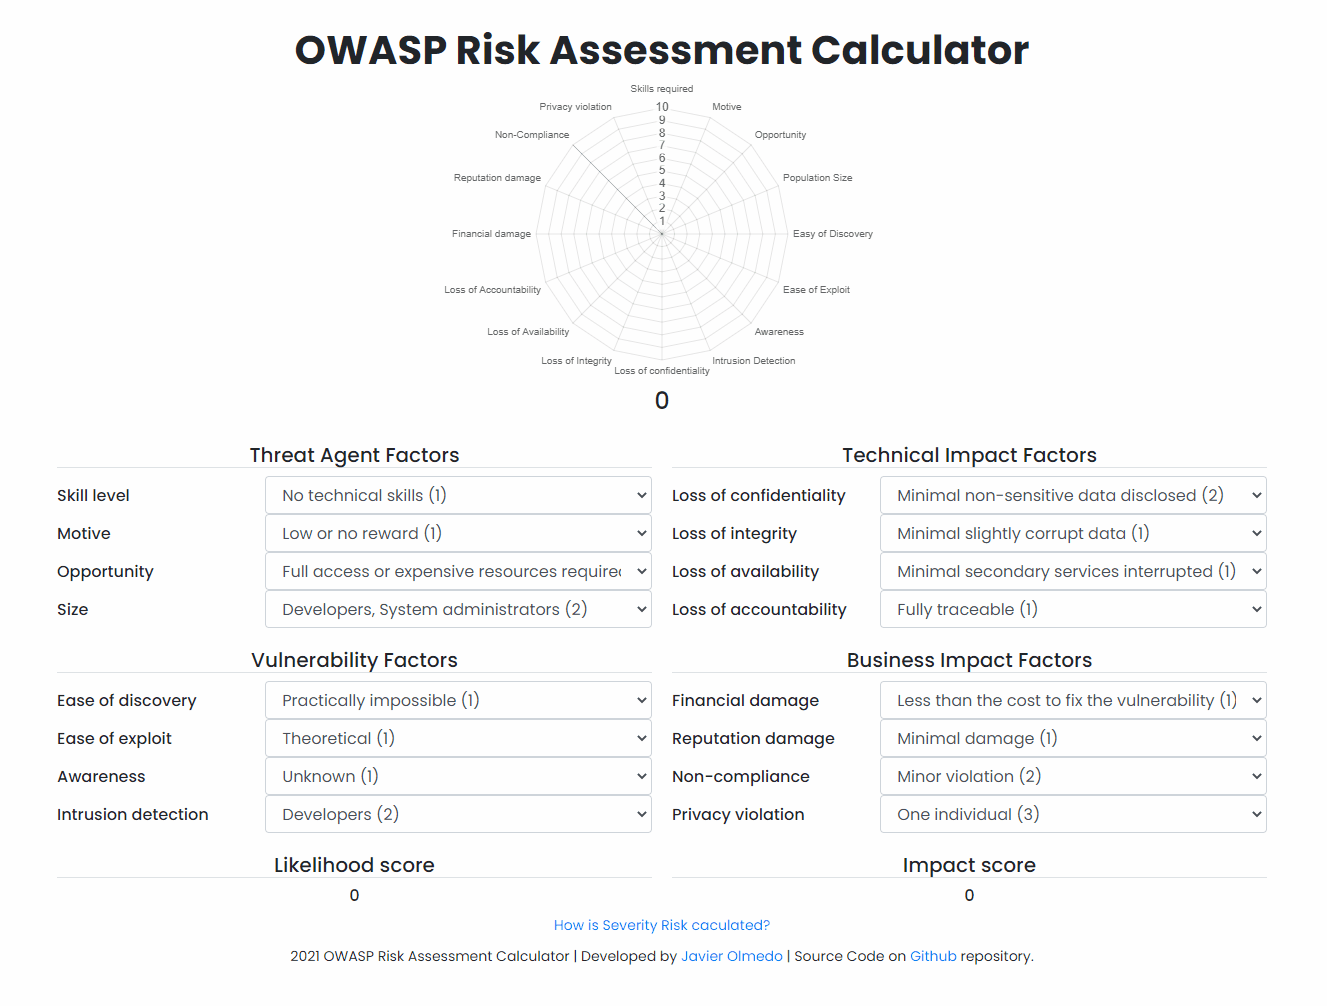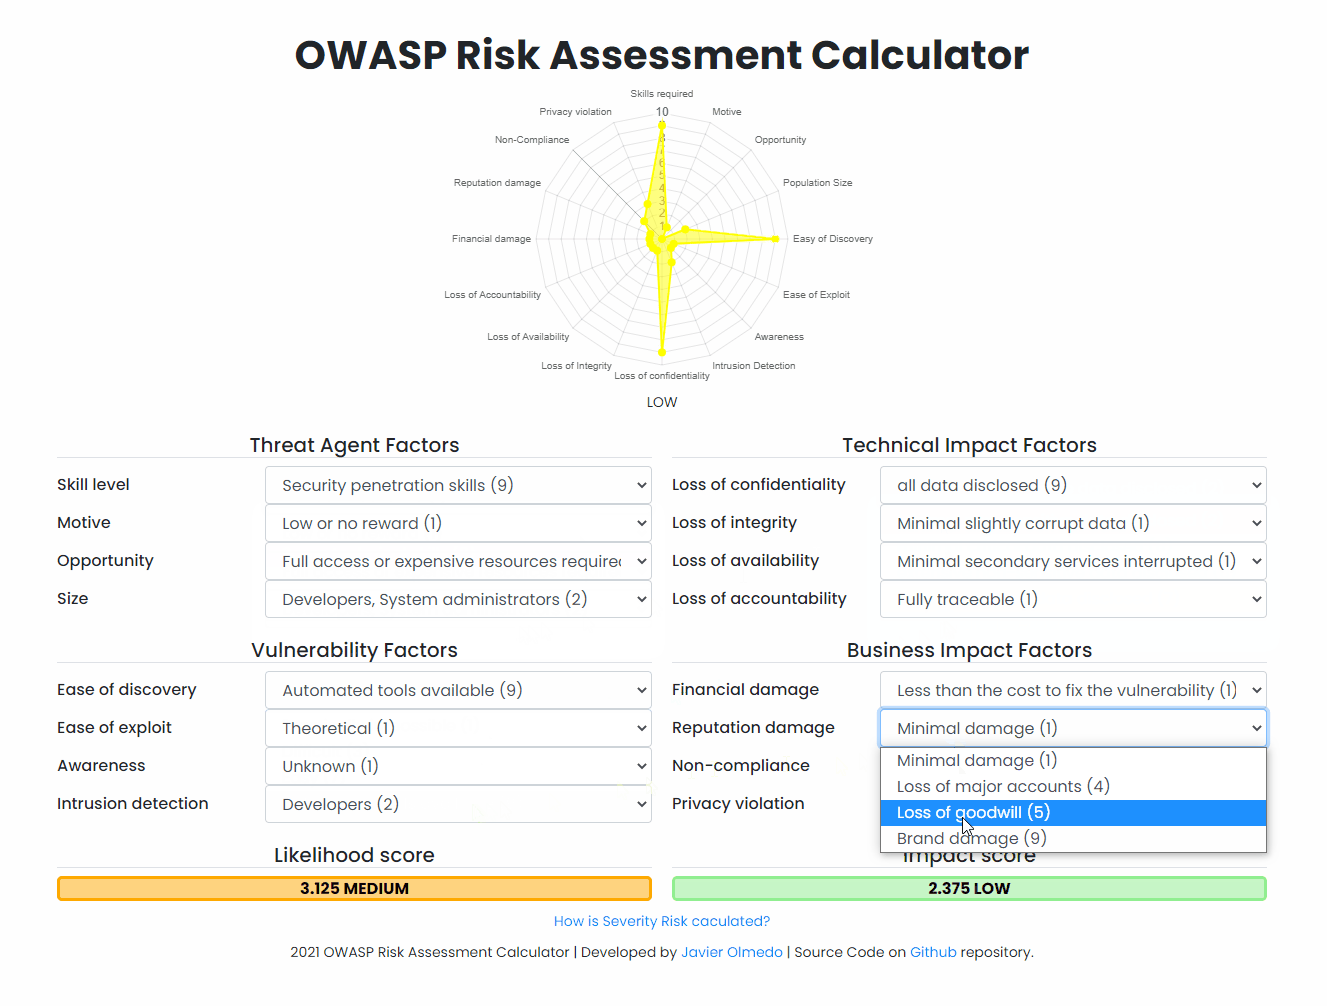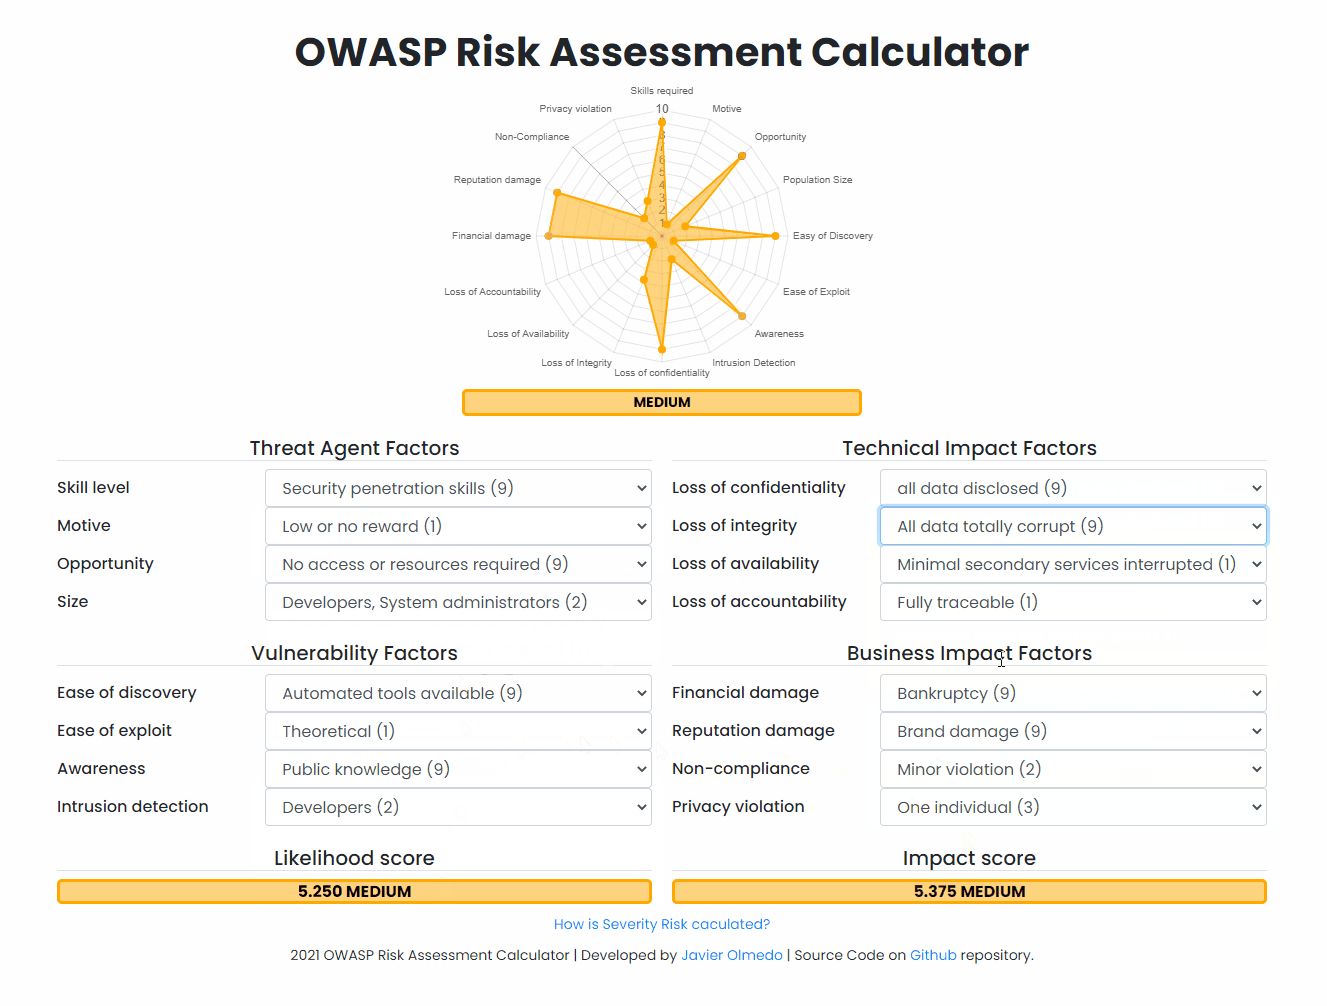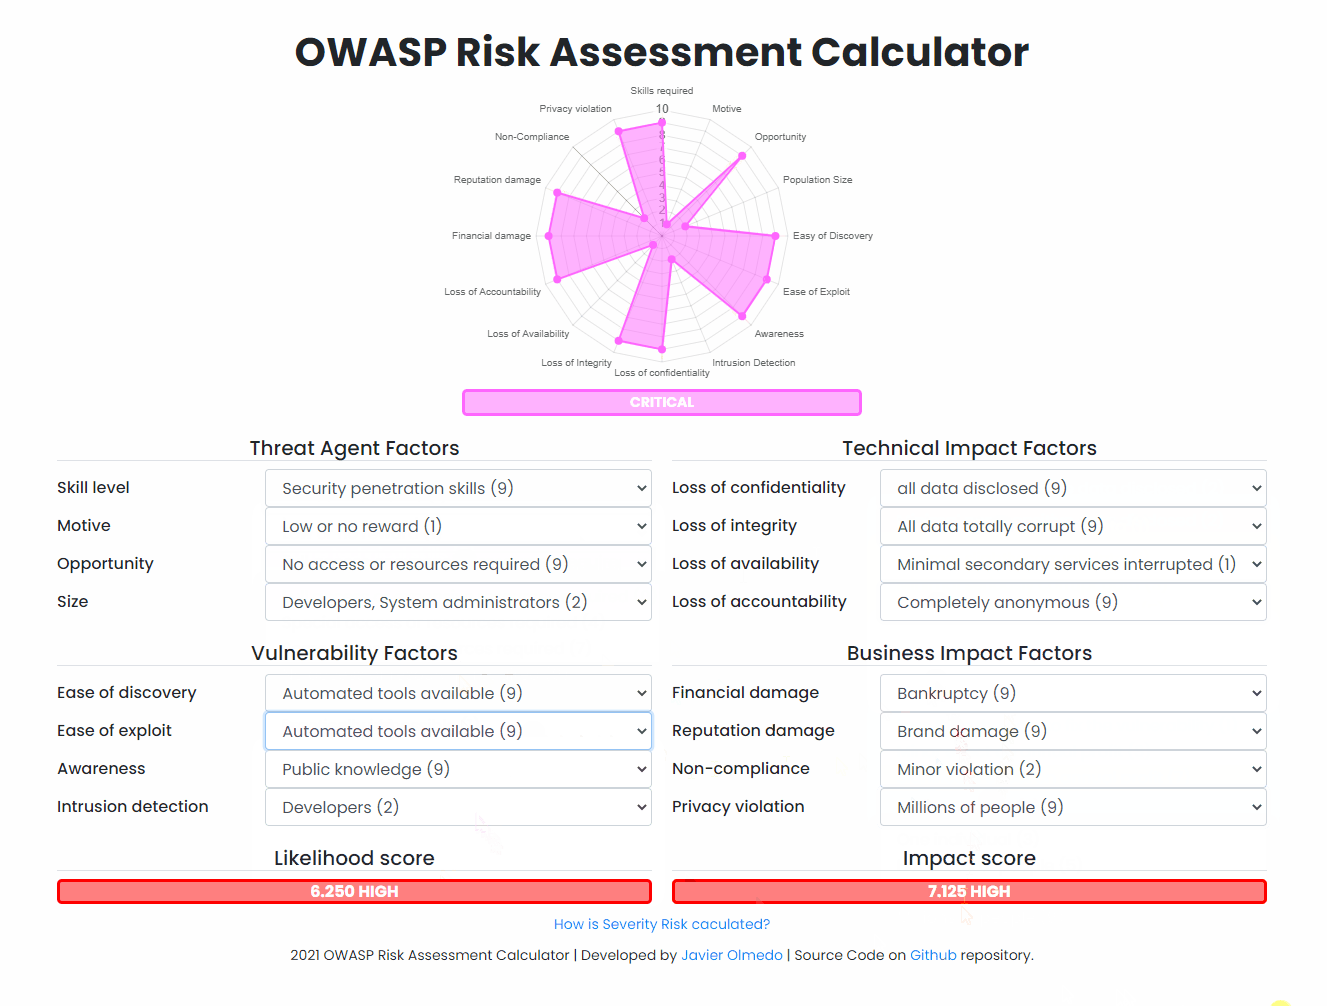
🧮 An online calculator to assess the risk of web vulnerabilities based on OWASP Risk Assessment

Curated collection of payloads for ethical security testing and bug bounty hunting, covering common web vulnerabilities and attack vectors.

Client-side workbench that auto-detects, recursively decodes, and analyses unknown or layered data, extracting indicators and CWE-tagged security…