
Mass-Assigner
Automated tool to probe for mass assignment vulnerabilities by extracting parameters from one HTTP request and applying them to another, with support…

Automated tool to probe for mass assignment vulnerabilities by extracting parameters from one HTTP request and applying them to another, with support…

The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…

API Scraper Agent for Web API's

Burp extension for wordpress security scanning

Terminal-based HTTP intercepting proxy with TUI for capturing, inspecting, and modifying requests in real time, plus a Repeater for resending and…

Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…

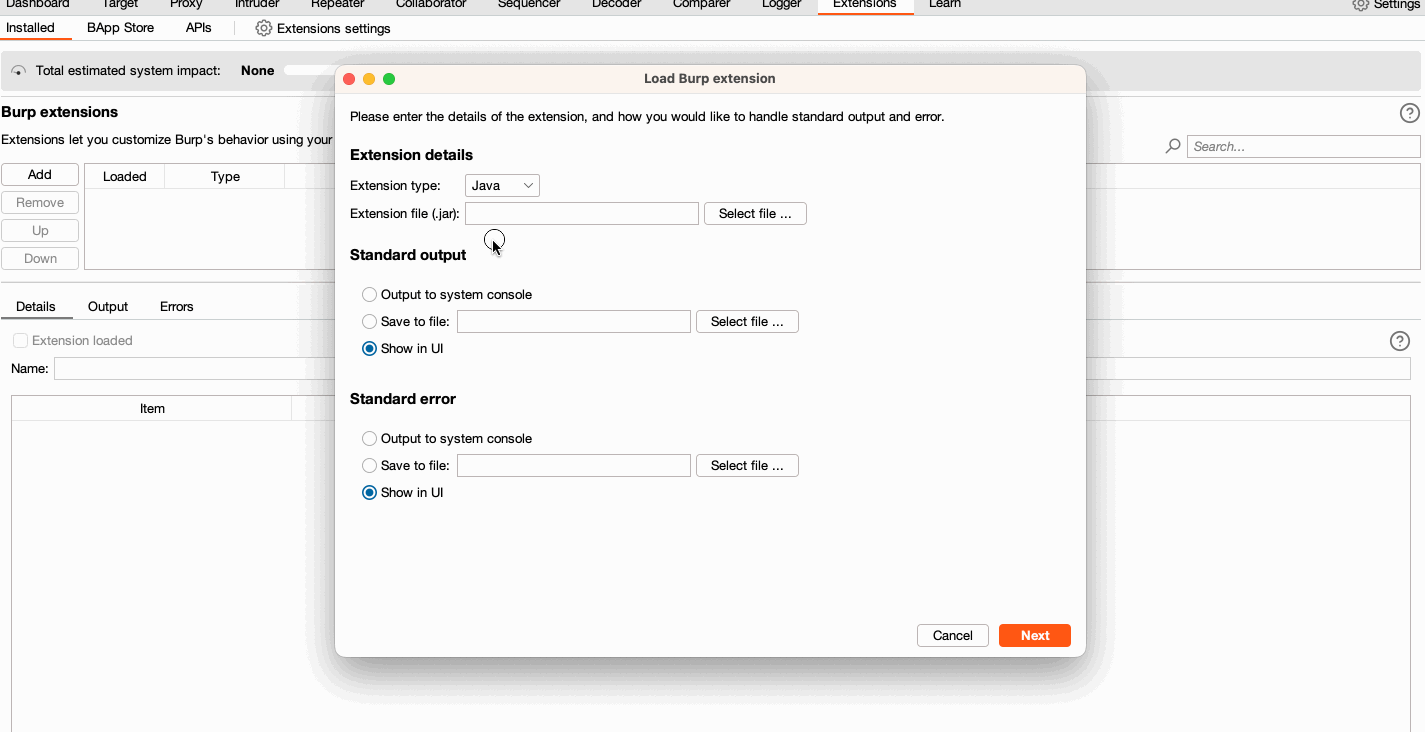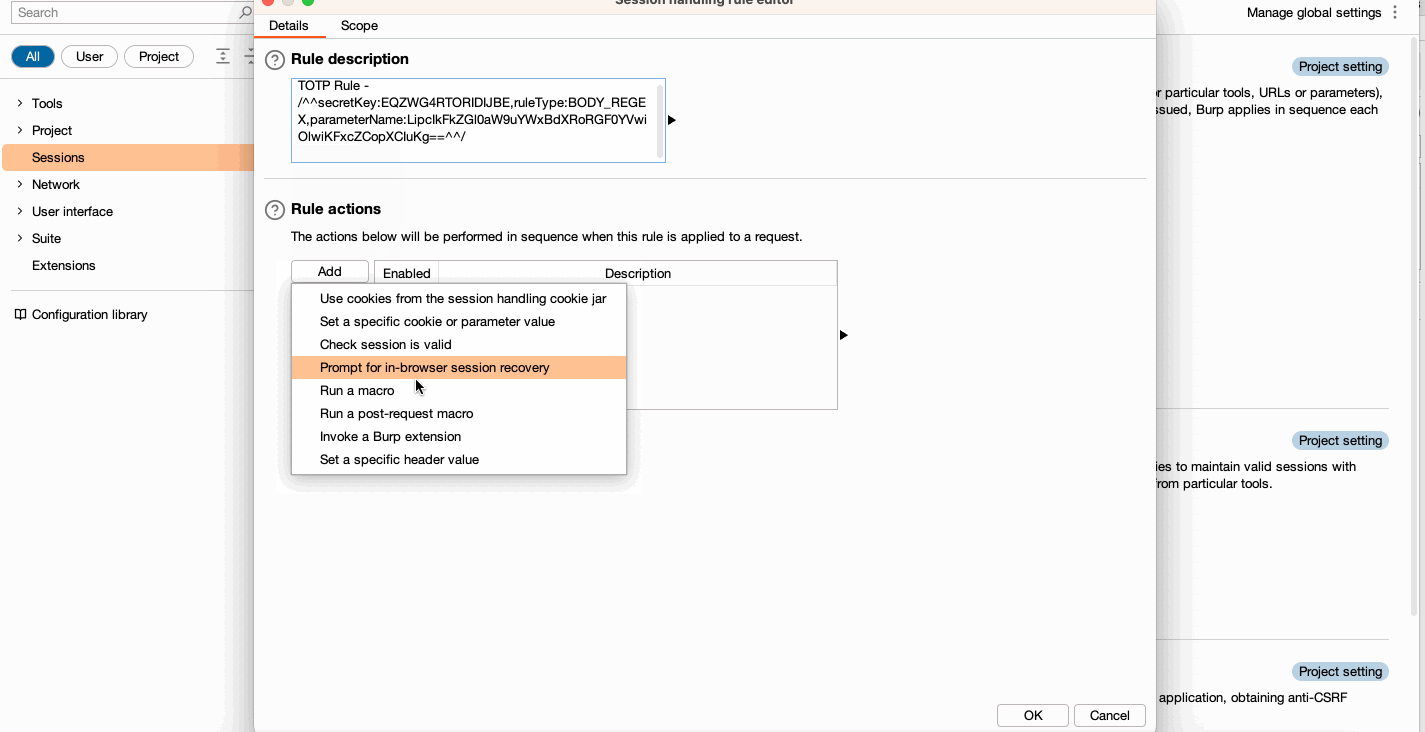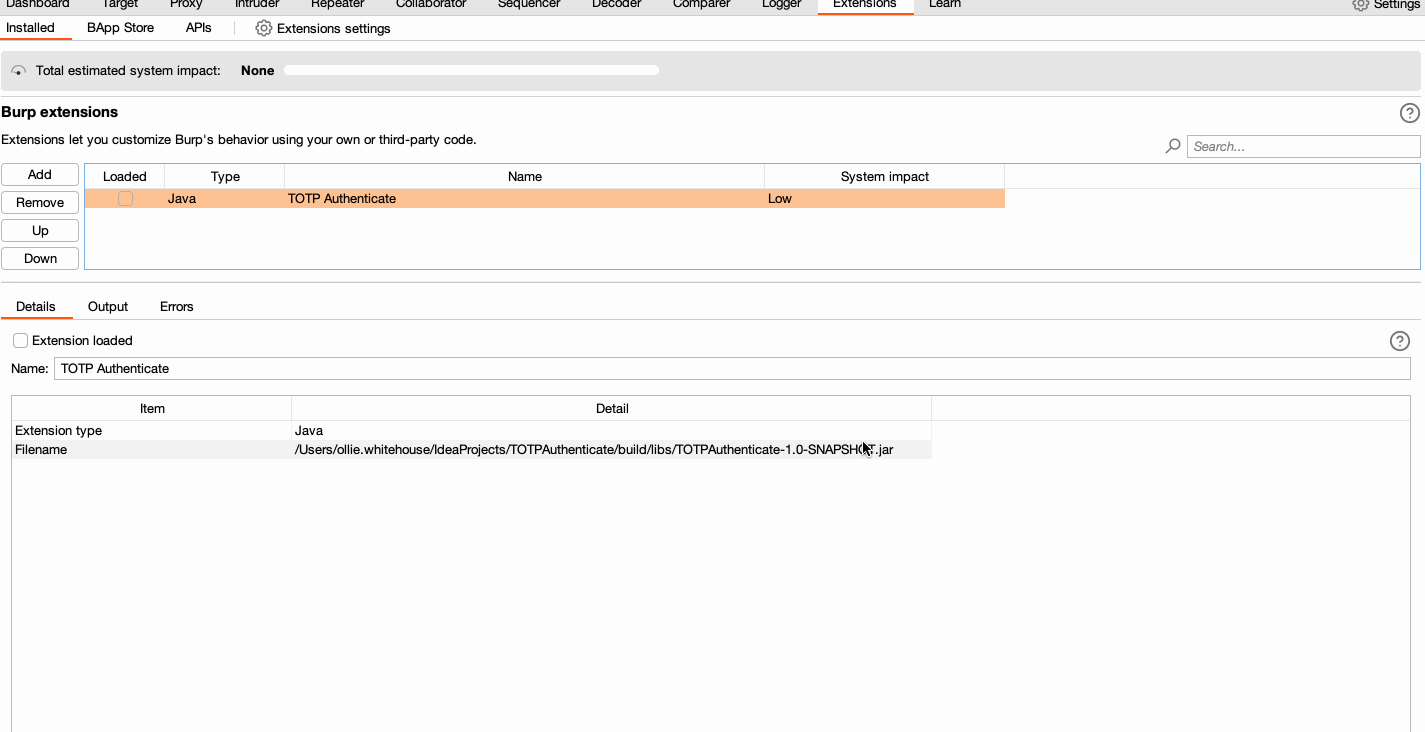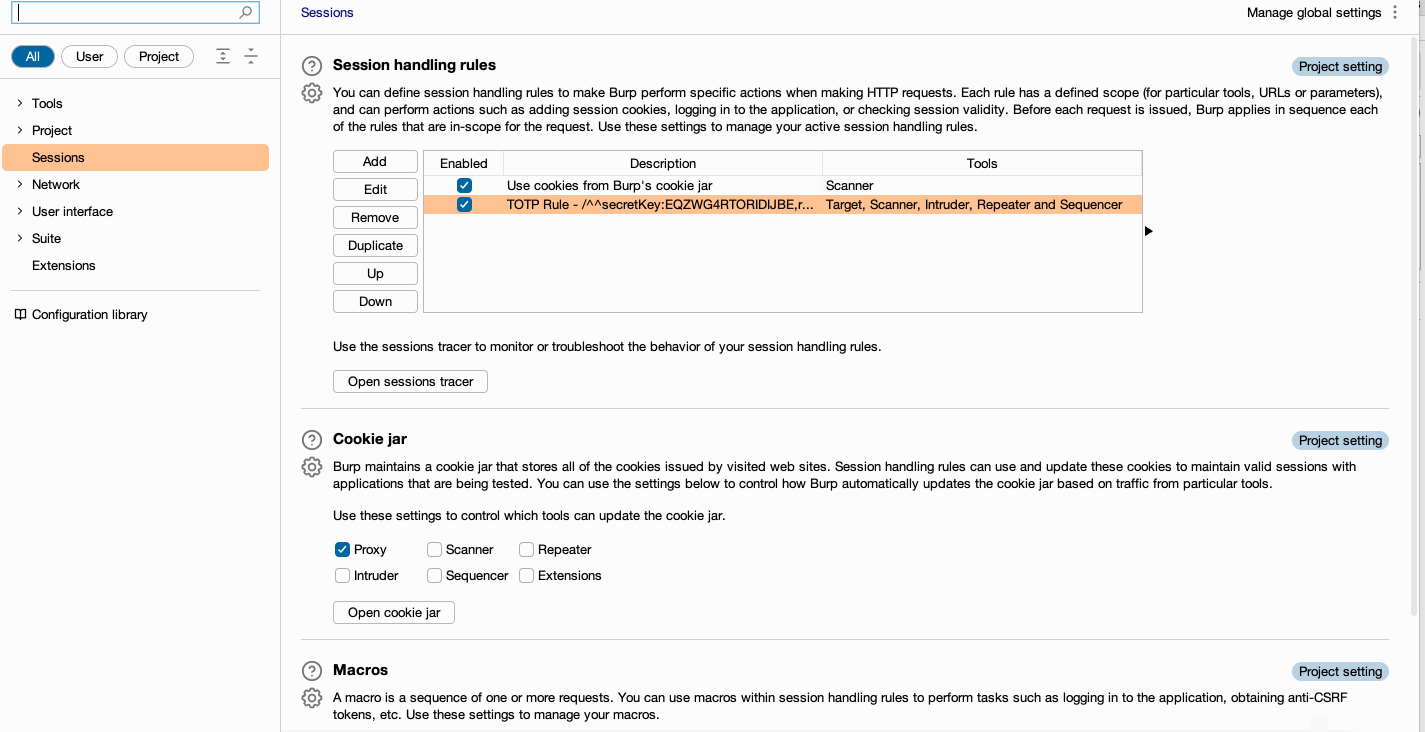
This extension, for Burp Suite Enterprise Edition, utilizes session handling rules to provide a TOTP token to outgoing requests.

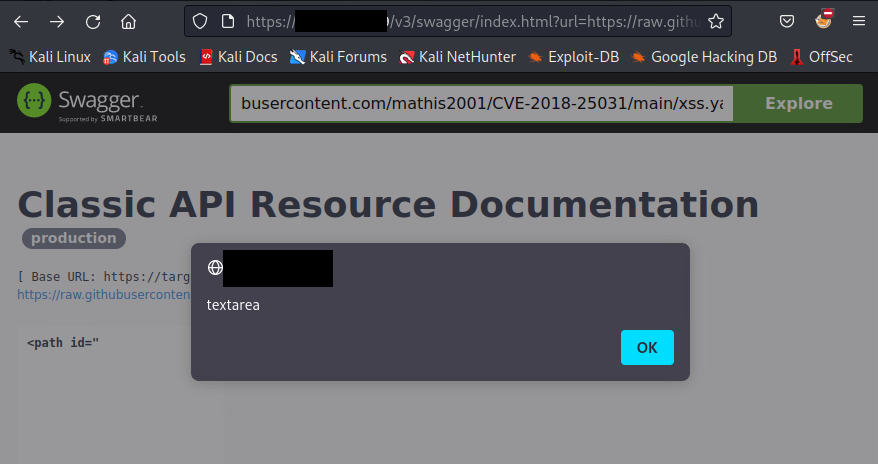
CVE-2018-25031 tests

Asynchronous WordPress security scanner with WAF bypass via headless browser. Enumerates plugins, themes, users, and multisite installations with…

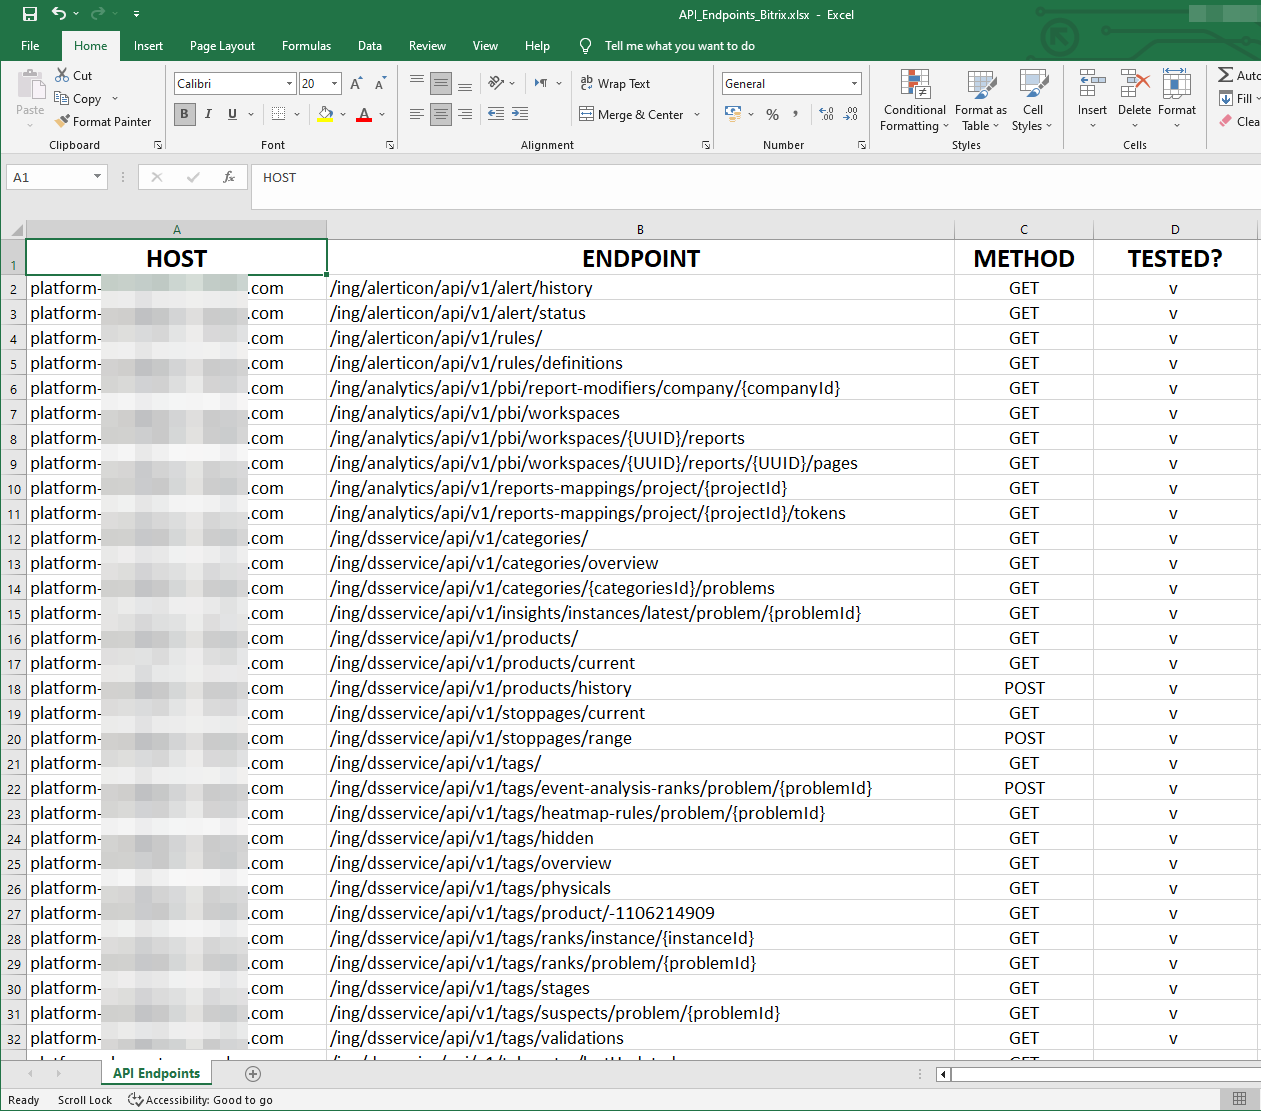
A Multi-Processing Tool for collecting and extracting information to an Excel file from a Burp Suite output file.

A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.

批量url检测Spring-Cloud-Gateway-CVE-2022-22947

OAuth Request Crafter

REST API automation for Burp Suite Community Edition. Drop-in Java extension exposing send/repeat/history endpoints over a local HTTP API.

Standalone authorized universal HTTP PoC for CVE-2026-75157

Reproducible BOLA/IDOR PoC against Onlook's tRPC API (CVE-2026-65013), with a 12-step exploit chain, vulnerable and patched Docker targets, and…

A Test API for testing the POC against CVE-2022-1388

Spring4Shell , Spring Framework RCE (CVE-2022-22965) , Burpsuite Plugin