
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/tkmru/lazycsrf
Payload GenerationVulnerability AnalysisWeb Application ExploitationWeb SecurityPenetration TestingArchived
GitHubtkmru/lazycsrf

lazyCSRF

A more useful CSRF PoC generator on Burp Suite

View Repository
9215414 years agoReviewed by Kitploit
Share

LazyCSRF

GitHub release License: MIT

LazyCSRF is a more useful CSRF PoC generator that runs on Burp Suite.

No longer maintenance🙇

When I started developing lazyCSRF, I mistakenly thought that the CSRF PoC generator built into Burp Professional could not generate PoC using XHR and did not support PUT requests, etc. I am still dissatisfied with the burp built-in CSRF PoC generator, but I think it is sufficient for needs now. I'm going to finish the maintenance now because I have other attractive themes. I'll do maintenance again when I have some free time.


Motivation

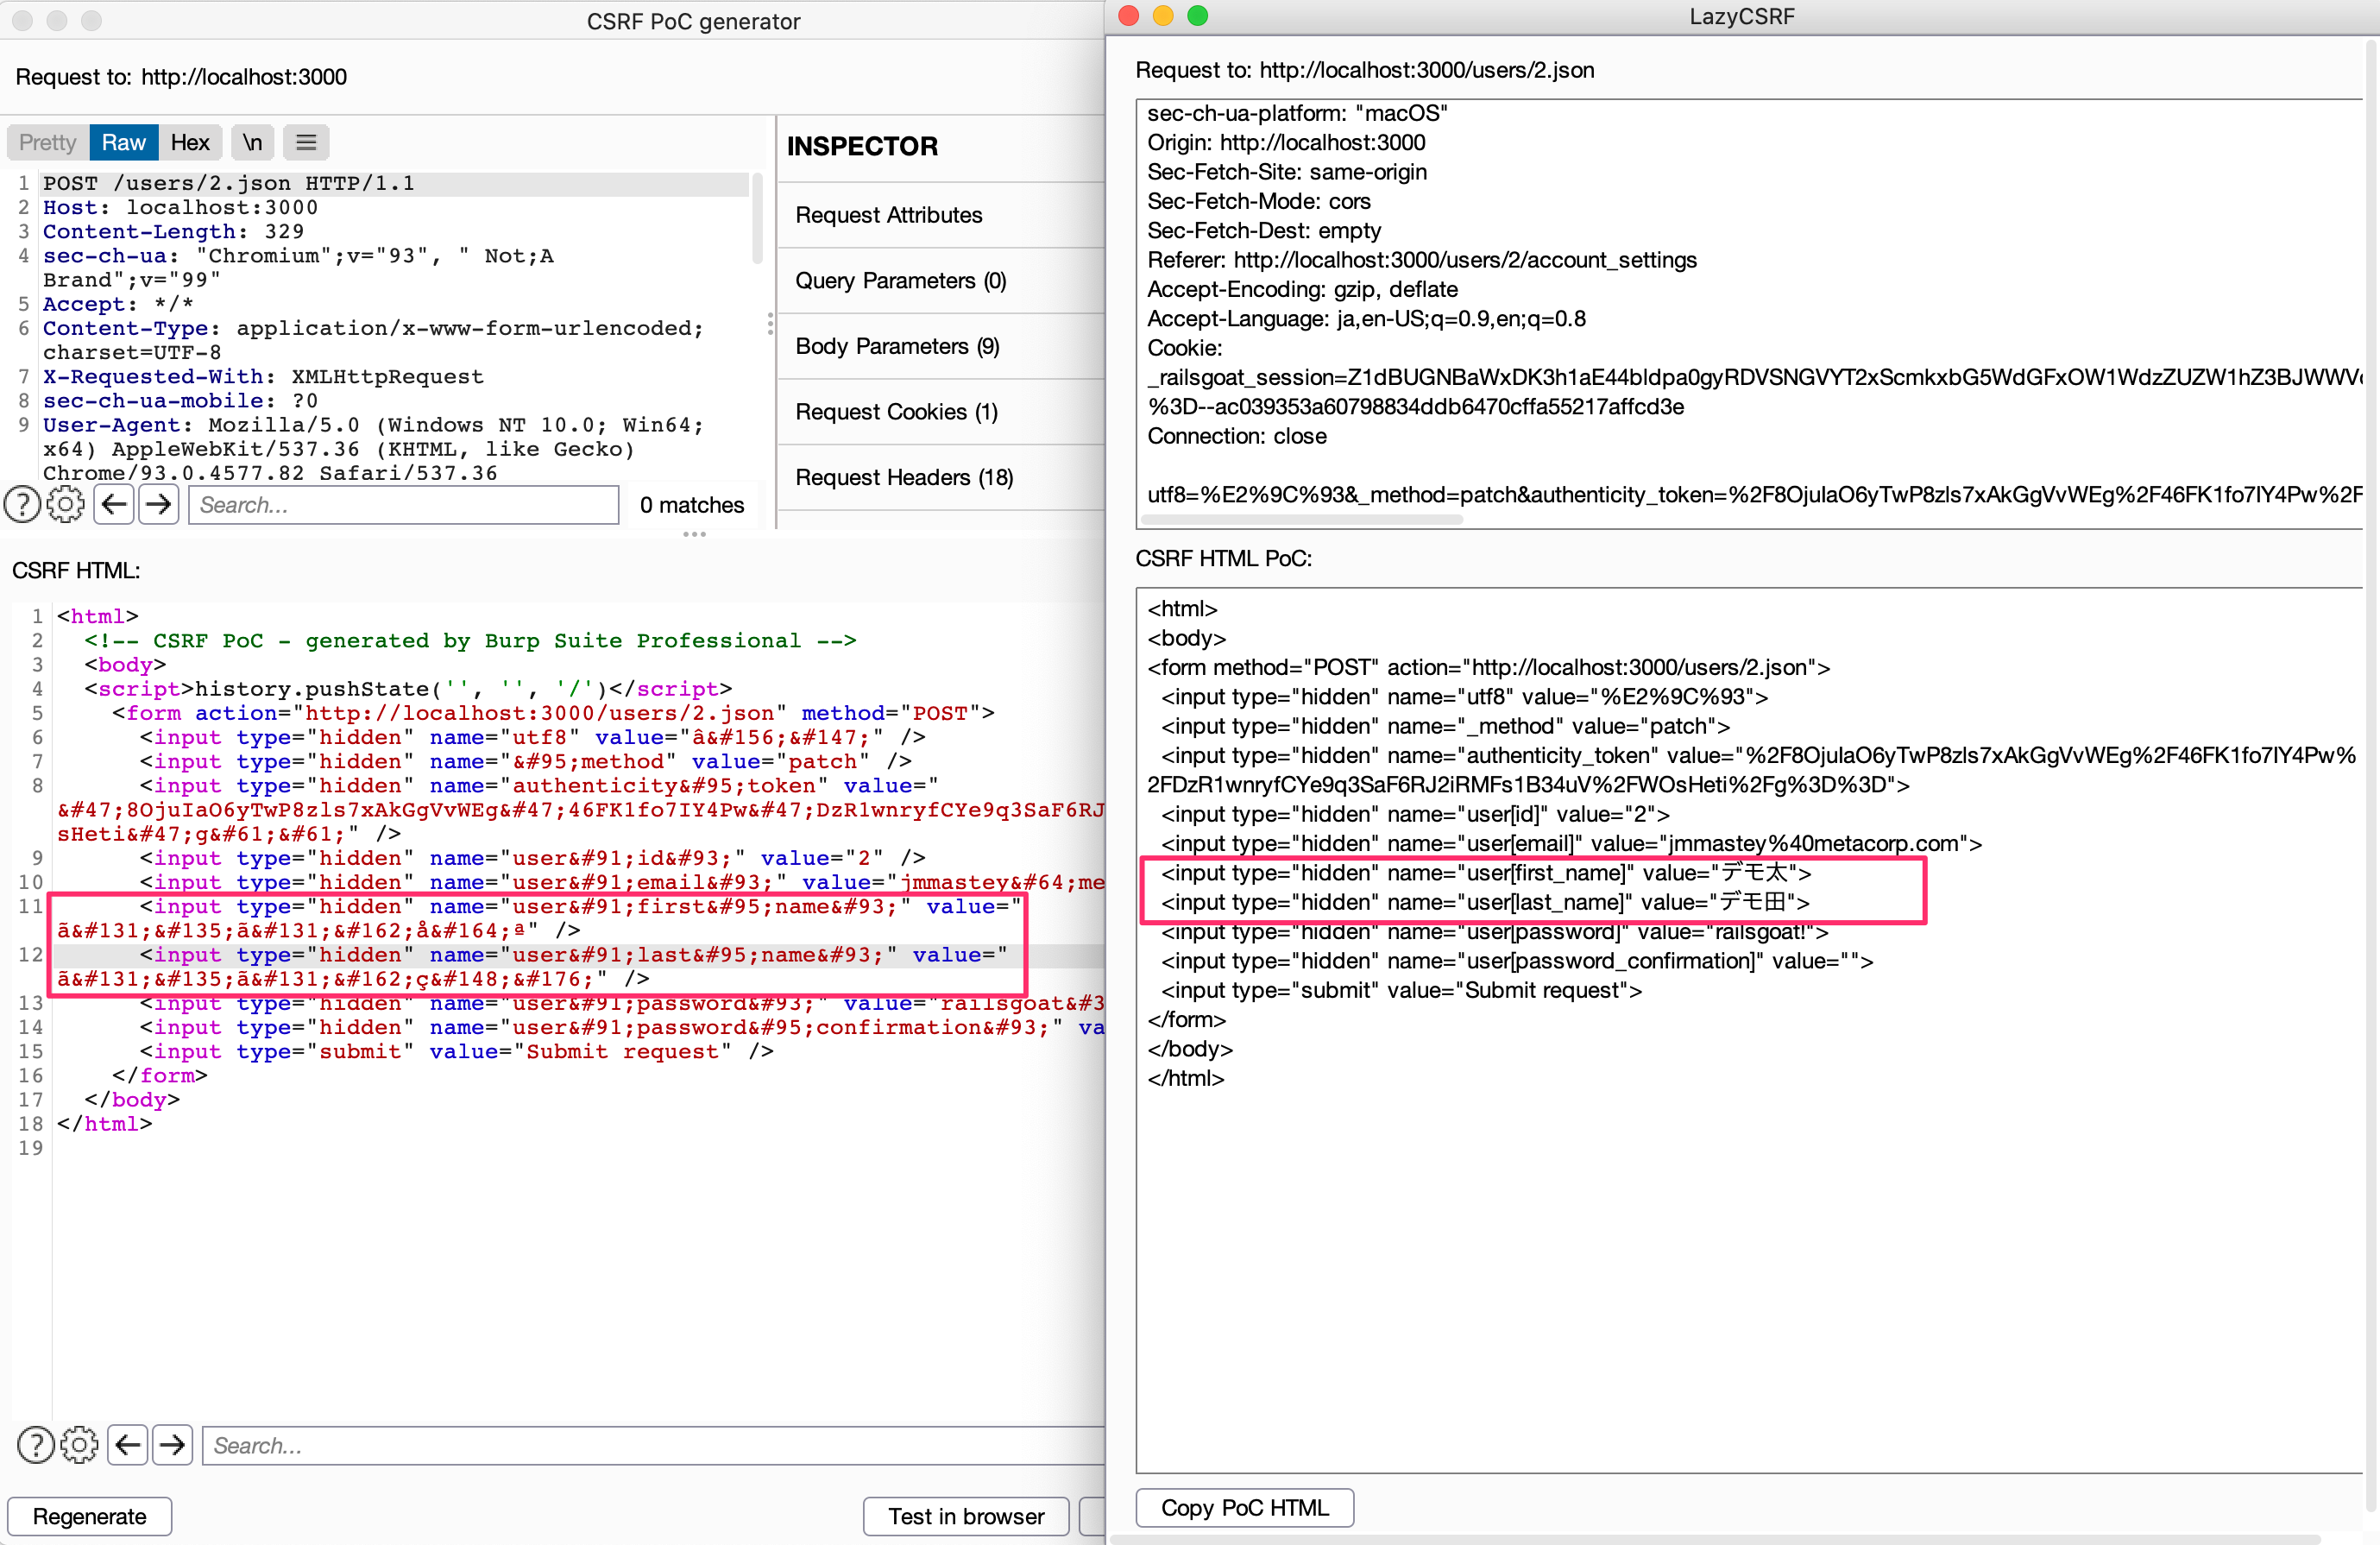
Burp Suite is an intercepting HTTP Proxy, and it is the defacto tool for performing web application security testing. The feature of Burp Suite that I like the most is Generate CSRF PoC. However, the function to automatically determine the content of request is broken, and it will try to generate PoC using form even for PoC that cannot be represented by form, such as cases using JSON for parameters or PUT requests. In addition, multibyte characters that can be displayed in Burp Suite itself are often garbled in the generated CSRF PoC. These were the motivations for creating LazyCSRF.

Features

  • Automatically switch to PoC using XMLHttpRequest
    • In case the parameter is JSON
    • In case the request is a PUT/PATCH/DELETE
  • Support displaying multibyte characters (like Japanese)
  • Generating CSRF PoC with Burp Suite Community Edition (of course, it also works in Professional Edition)

Difference in display of multibyte characters

The following image shows the difference in the display of multibyte characters between Burp's CSRF PoC generator and LazyCSRF. LazyCSRF can generate PoC for CSRF without garbling multibyte characters. This is only the case if the characters are not garbled on Burp Suite.

display-japanese

Installation

Download the JAR from GitHub Releases. In Burp Suite, go to the Extensions tab in the Extender tab, and add a new extension. Select the extension type Java, and specify the location of the JAR.

Usage

You can generate a CSRF PoC by selecting Extensions->LazyCSRF->Generate CSRF PoC By LazyCSRF from the menu that opens by right-clicking on Burp Suite.

menu

How to Build

intellij

If you use IntelliJ IDEA, you can build it by following Build -> Build Artifacts -> LazyCSRF:jar -> Build.

Command line

You can build it with maven.

$ mvn install

LICENSE

MIT License

Copyright (C) 2021 tkmru

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    916
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    558
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    370
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    317
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →





