nuclei-CVE-2025-24813

University Project of developing a template for safely testing for the CVE 2025-24813 on a server. It is intentionally made to not leave any lasting…

University Project of developing a template for safely testing for the CVE 2025-24813 on a server. It is intentionally made to not leave any lasting…

PoC for CVE-2019-18394: unauthenticated full-read SSRF in Openfire <= 4.4.2 FaviconServlet

CVE-2026-8732 | WP Maps Pro <= 6.1.0 Unauth Admin Creation

Unauthenticated SSRF in the Chamilo LMS PENS plugin — CVE-2026-34160 / CVSS 8.6

NetLogic is an advanced network analysis and cybersecurity toolkit for traffic inspection, packet analysis, and threat detection

A list of custom Nuclei templates you can use for your scans.

Nuclei template to discover exposed Keycloak reset-credentials endpoints across multiple paths, aiding validation of CVE-2026-18963 exposure.

WordPress security scanner that fingerprints versions, detects reflected XSS across multiple targets concurrently, and supports an authenticated…

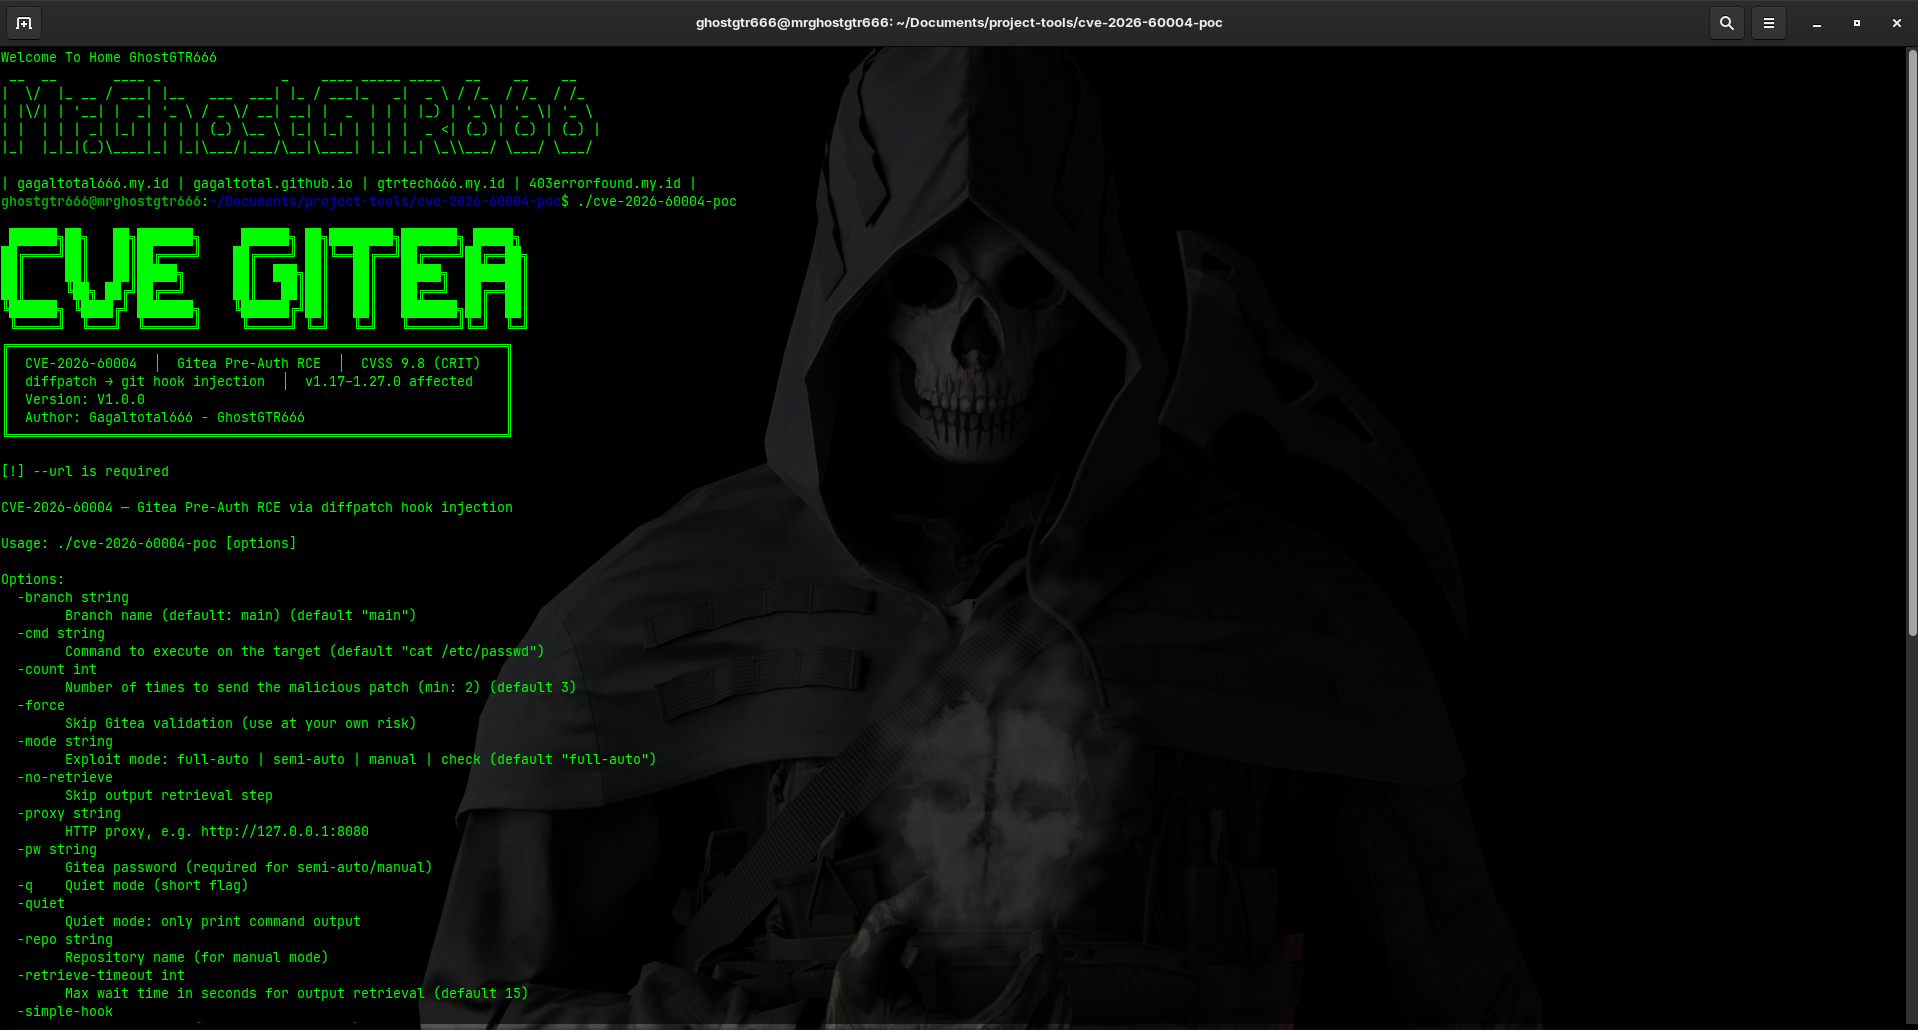
CVE-2026-60004 — Gitea Pre-Auth RCE via diffpatch hook injection

Scanner: CVE-2026-3854 GitHub Enterprise Server Pre-auth RCE via Push Option Injection — Python checker (CISA KEV)

WordPress CVE-2026-63030 and CVE-2026-60137 security tool for detecting exposure to the WP2Shell pre-authentication RCE chain.

CVE-2026-66066 — KindaRails2Shell: Rails Active Storage/libvips Arbitrary File Read → RCE. MATLAB/HDF5 dual-identity file → SECRET_KEY_BASE theft →…

Proof-of-concept demonstrating an authenticated blind SSRF in Matomo's SiteContentDetector, allowing internal network reconnaissance and requests to…

Apache HTTP Server 2.4.49 Path Traversal Vulnerability Reproduction

BurpSuite plugin for HTTP packet analysis and fuzzing dictionary generation. Extracts parameters, paths, and files from requests, counts frequency,…

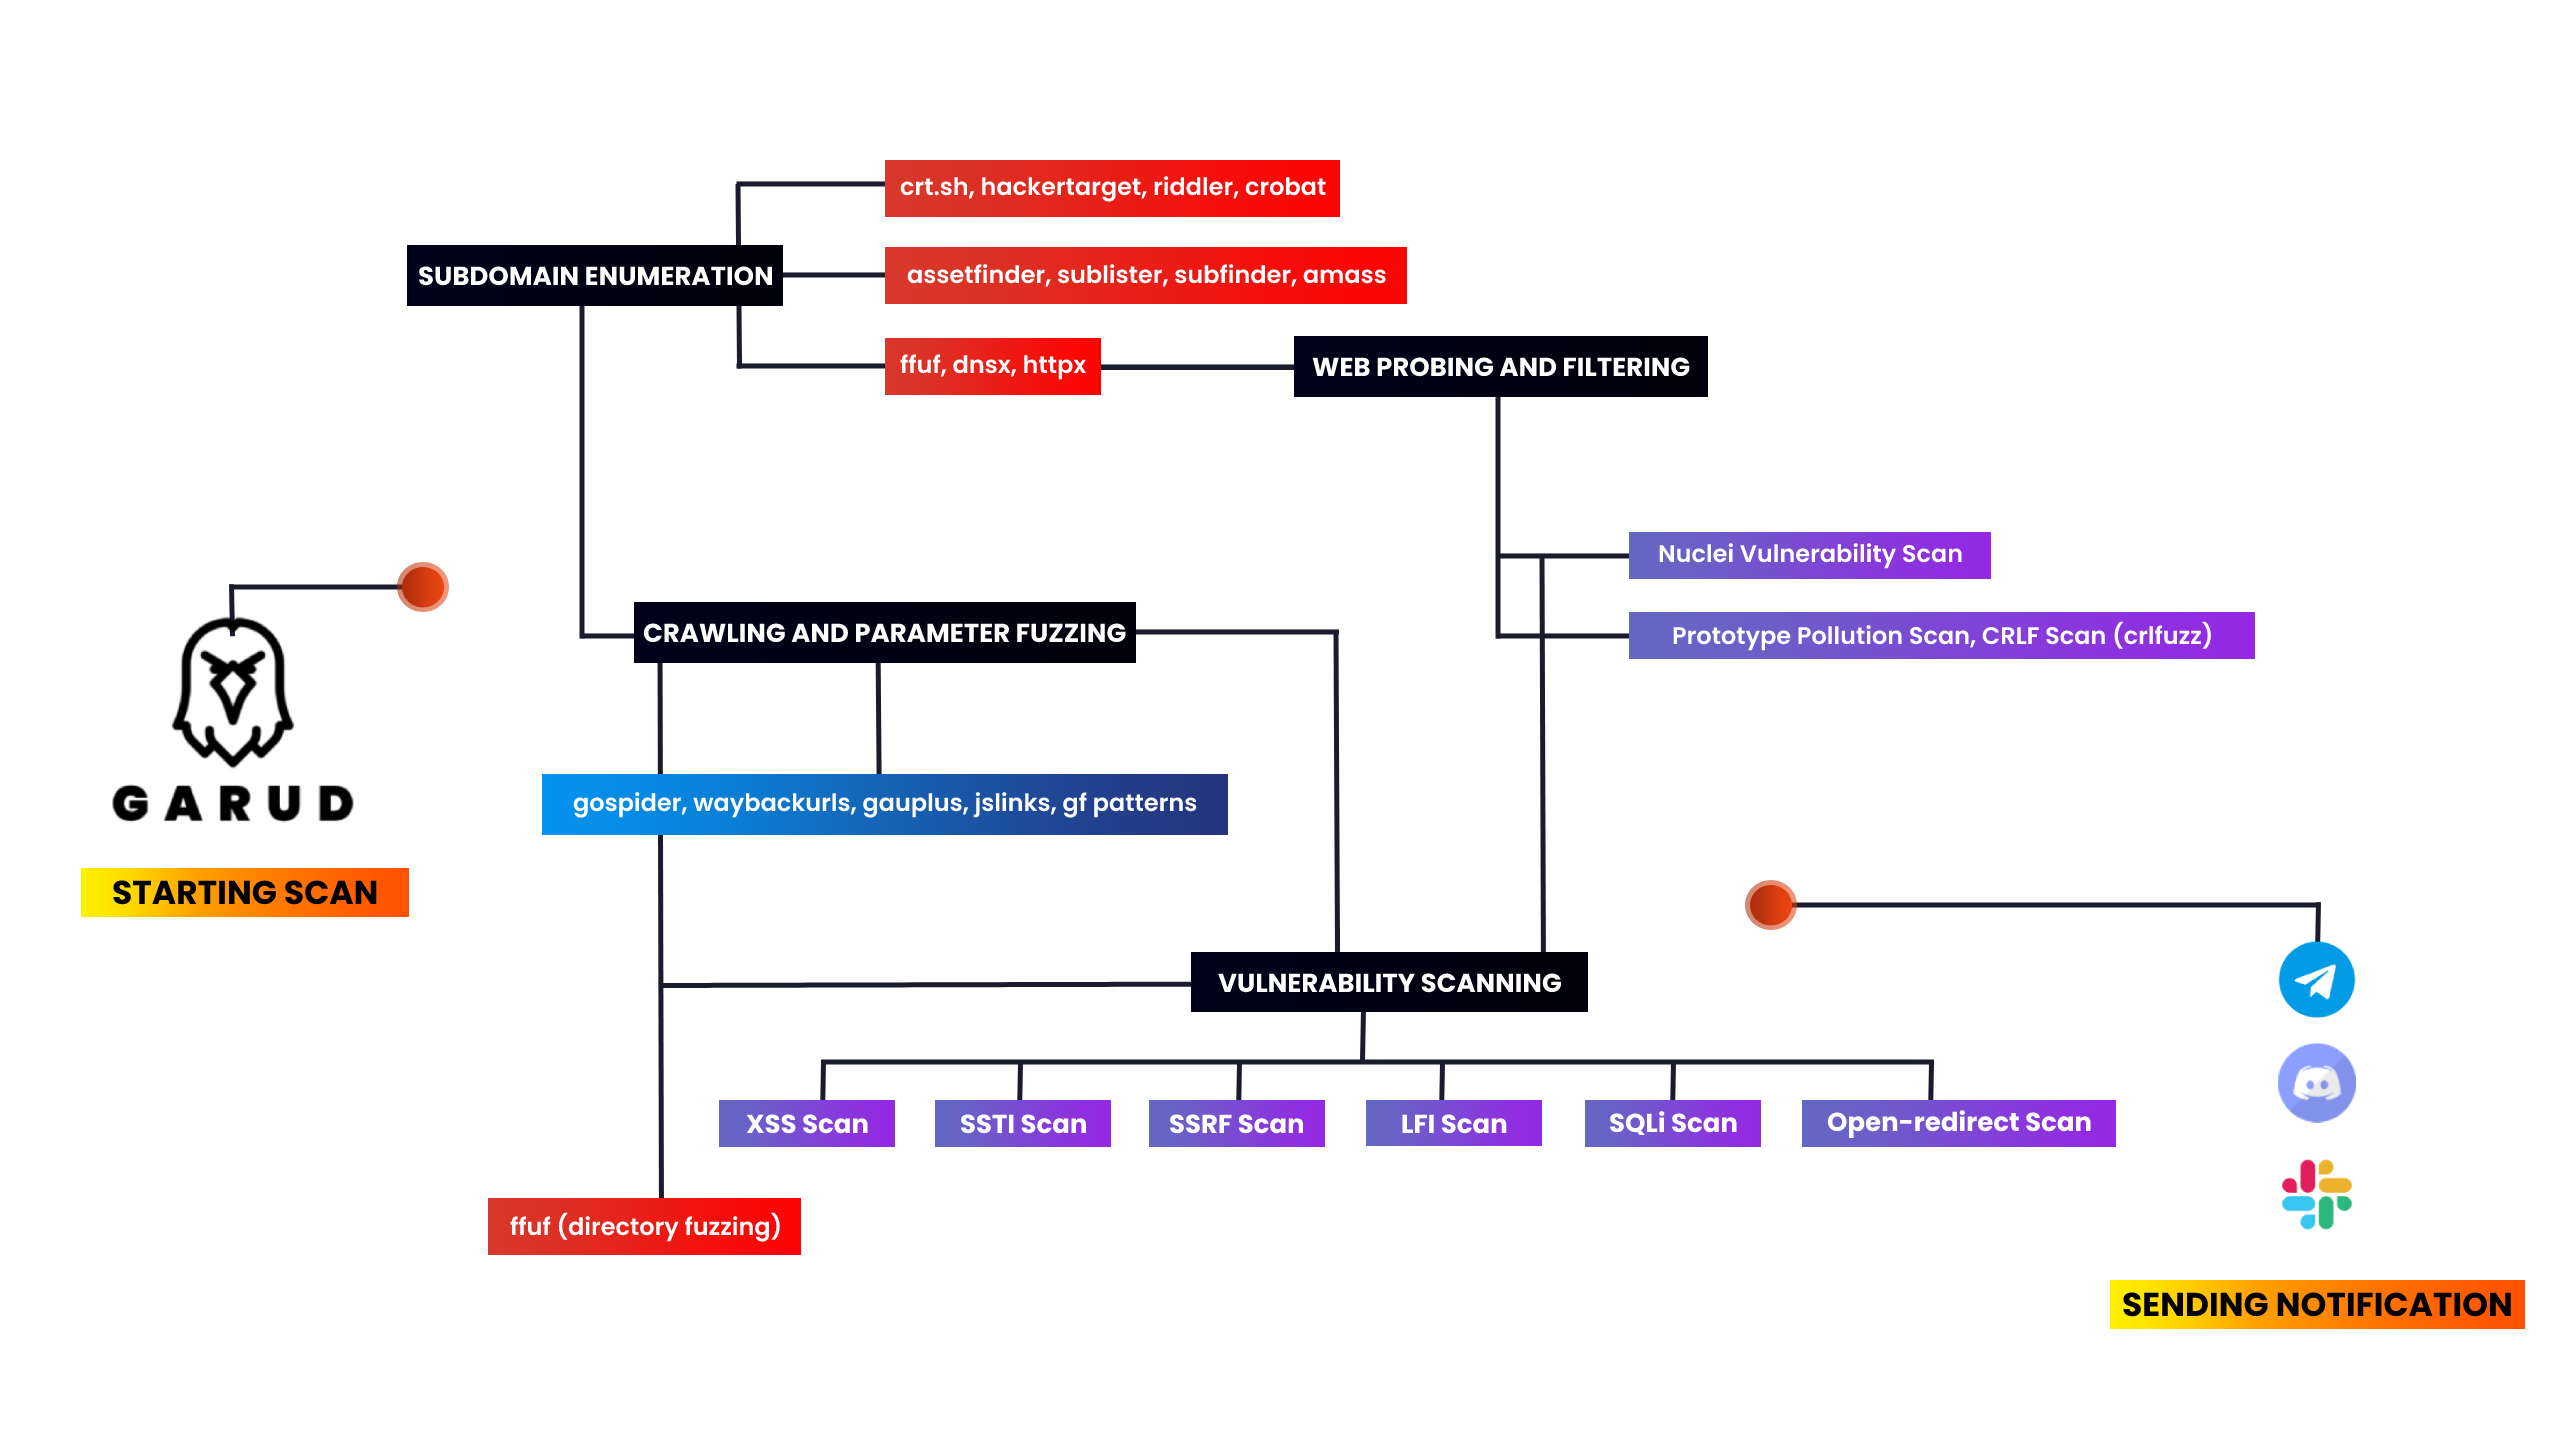
An automation tool that scans sub-domains, sub-domain takeover, then filters out XSS, SSTI, SSRF, and more injection point parameters and scans for…

Scans internet-exposed cPanel/WHM instances for CVE-2026-41940 authentication bypass, probing HTTPS on port 2087 and matching response markers to…

Detection tool for cPanel/WHM CVE-2026-41940 (CRLF injection auth bypass). Verify vulnerability on servers you own or have permission to test. For…