
owasp-java-encoder
The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…

The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…

Autonomous AI red team agent for penetration testing with 13+ specialized agents, 120+ OWASP test cases, and MITRE ATT&CK integration. Supports 15+…

The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.

Hunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.

Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…

Collaborative application security testing between humans and agents via CLI and MCP

Open-source API security platform for continuous API discovery, vulnerability testing, and runtime threat detection. Integrates with CI/CD pipelines…

An open source threat modeling tool from OWASP

Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…

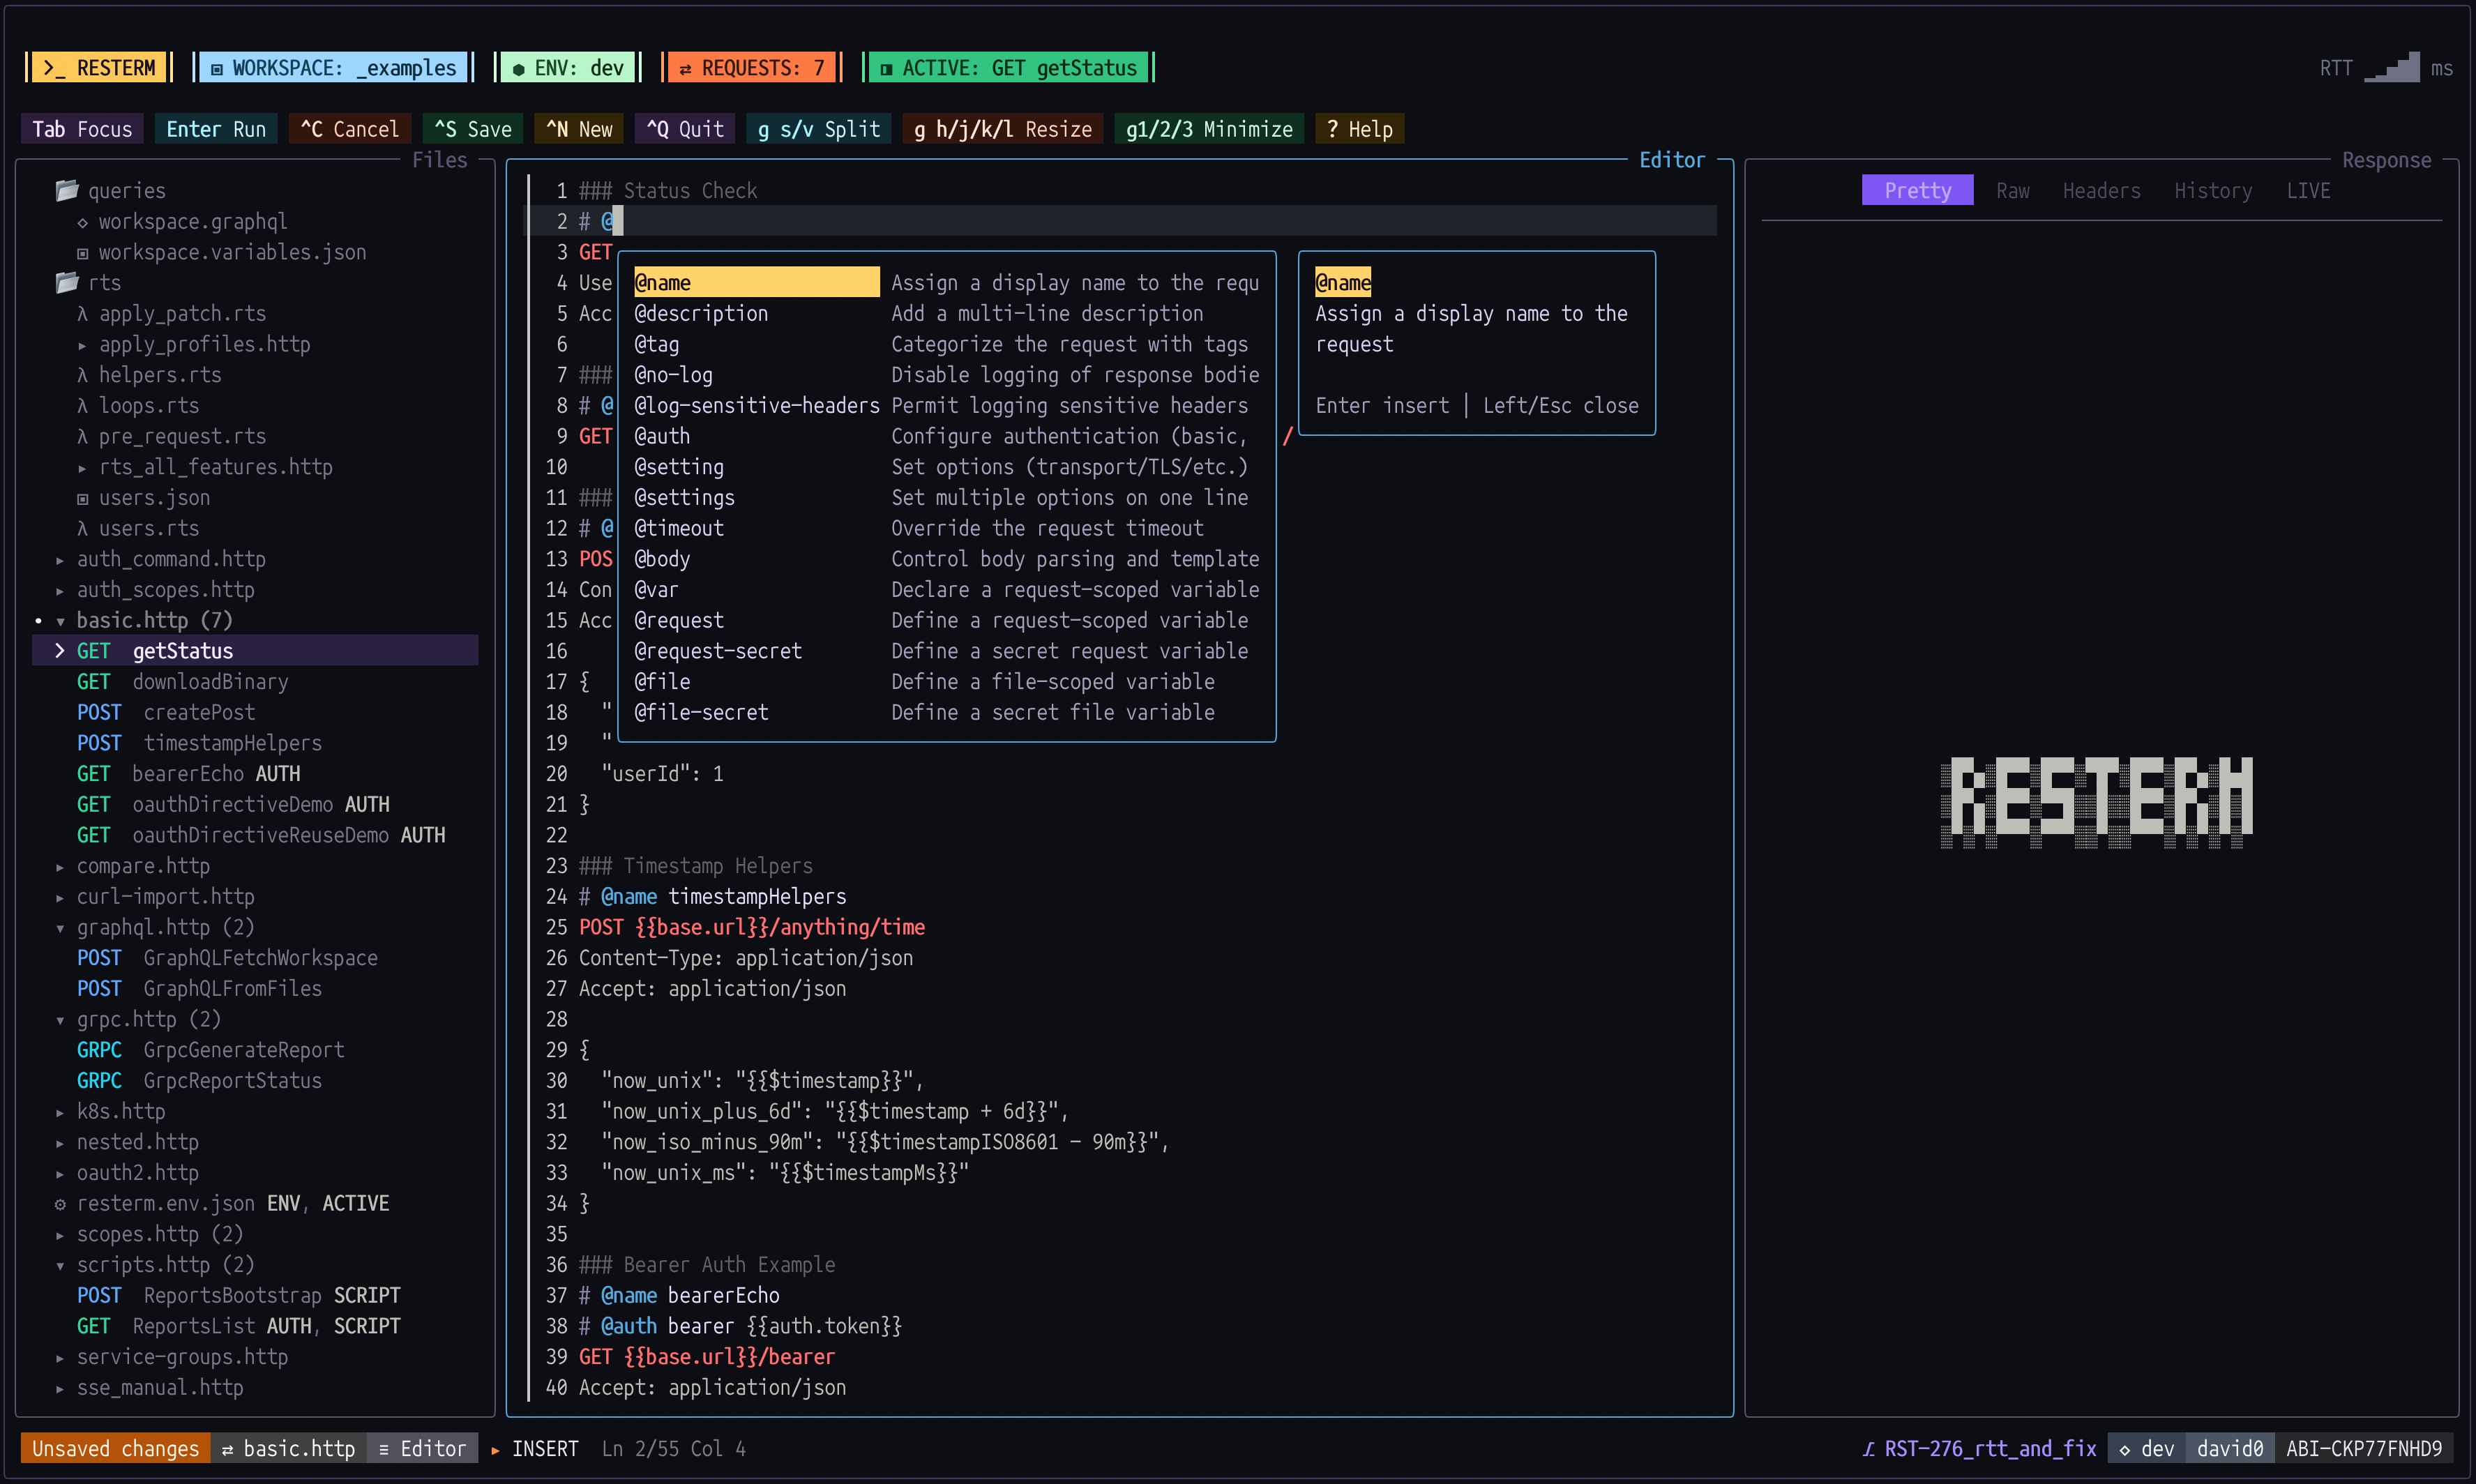
Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…

Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies

Vulnerability Assessment Scanner with Report Generation

German OWASP Day conference site & presentation archive

OWASP Community Pages are a place where OWASP can accept community contributions for security-related content.

Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…

Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.

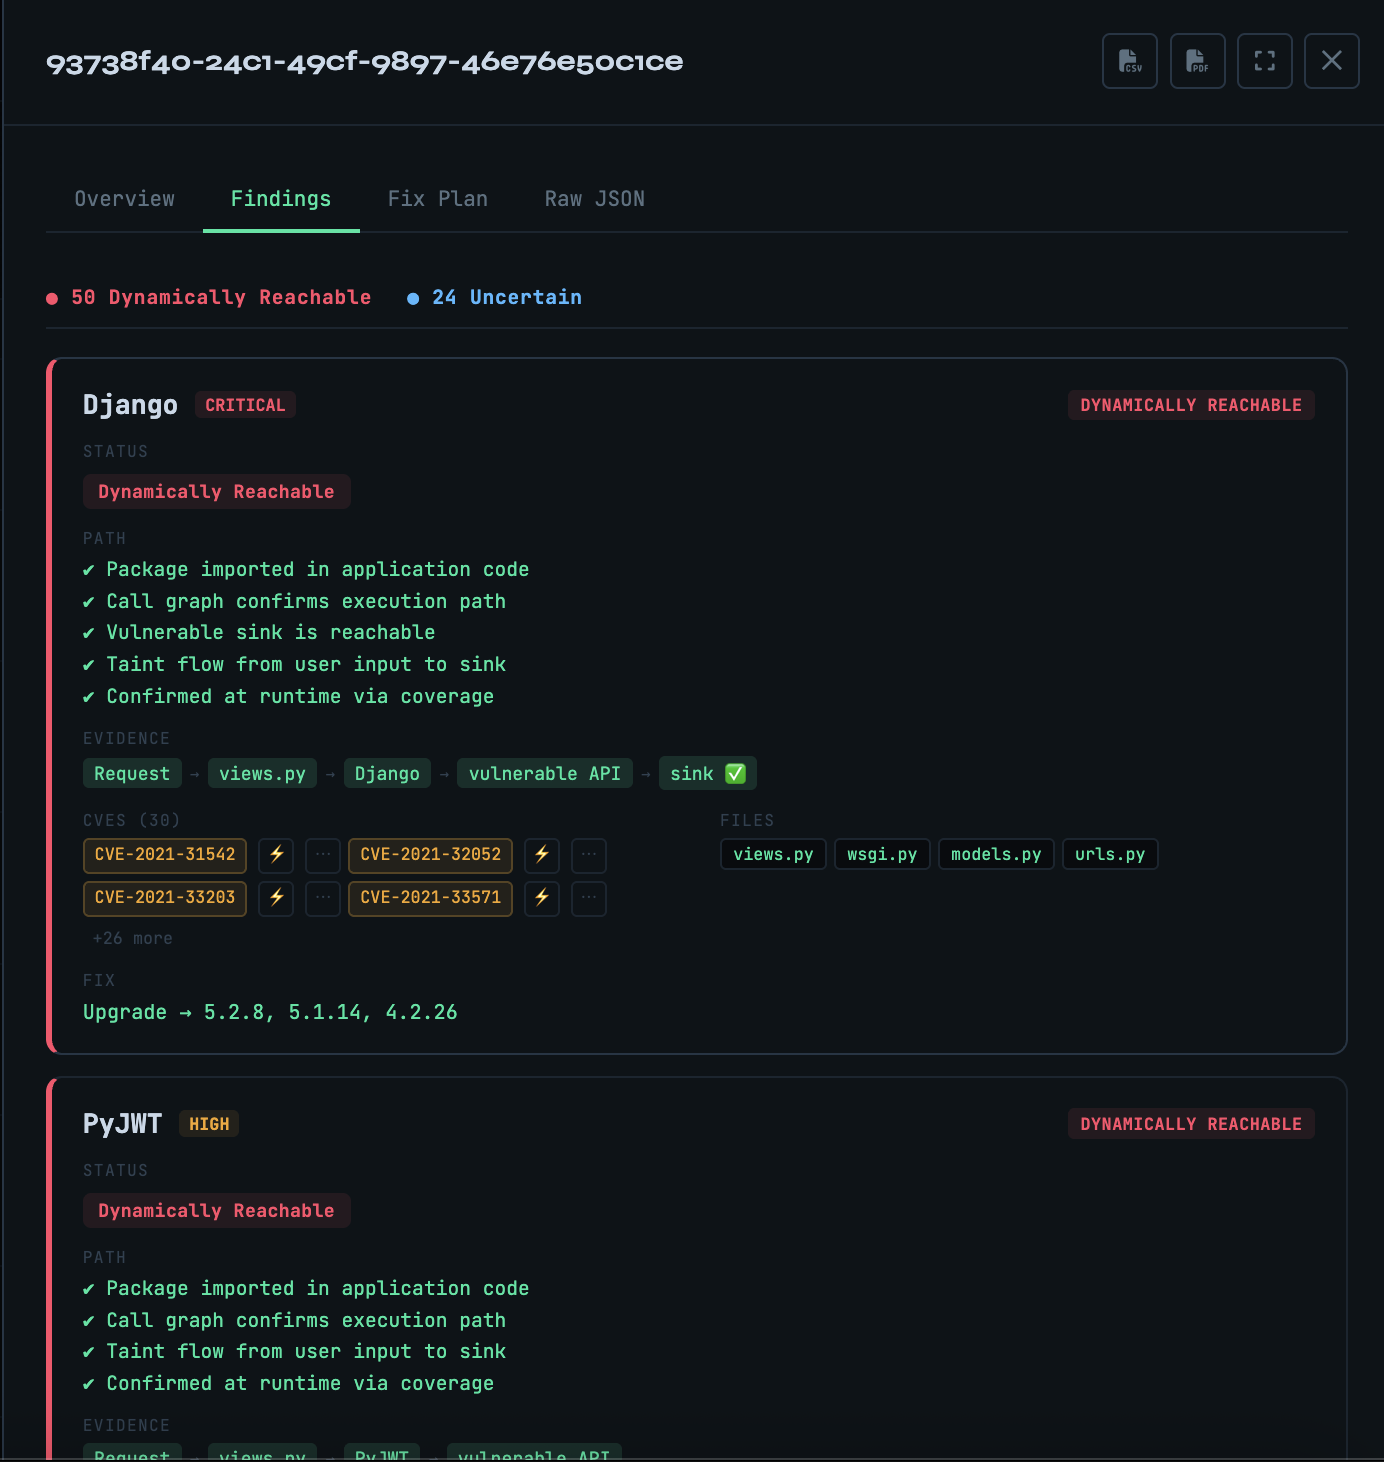
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.

Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.