
CheatSheetSeries
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
api-securityauthenticationcloud-security+6
33.3k
owasp/cheatsheetseriesThe OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 owasp-noir/noir
Hunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.
 owasp/www-community
OWASP Community Pages are a place where OWASP can accept community contributions for security-related content.
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 owasp/owasp-java-encoder
The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…
 cyberstrikeus/cyberstrike
Autonomous AI red team agent for penetration testing with 13+ specialized agents, 120+ OWASP test cases, and MITRE ATT&CK integration. Supports 15+…
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
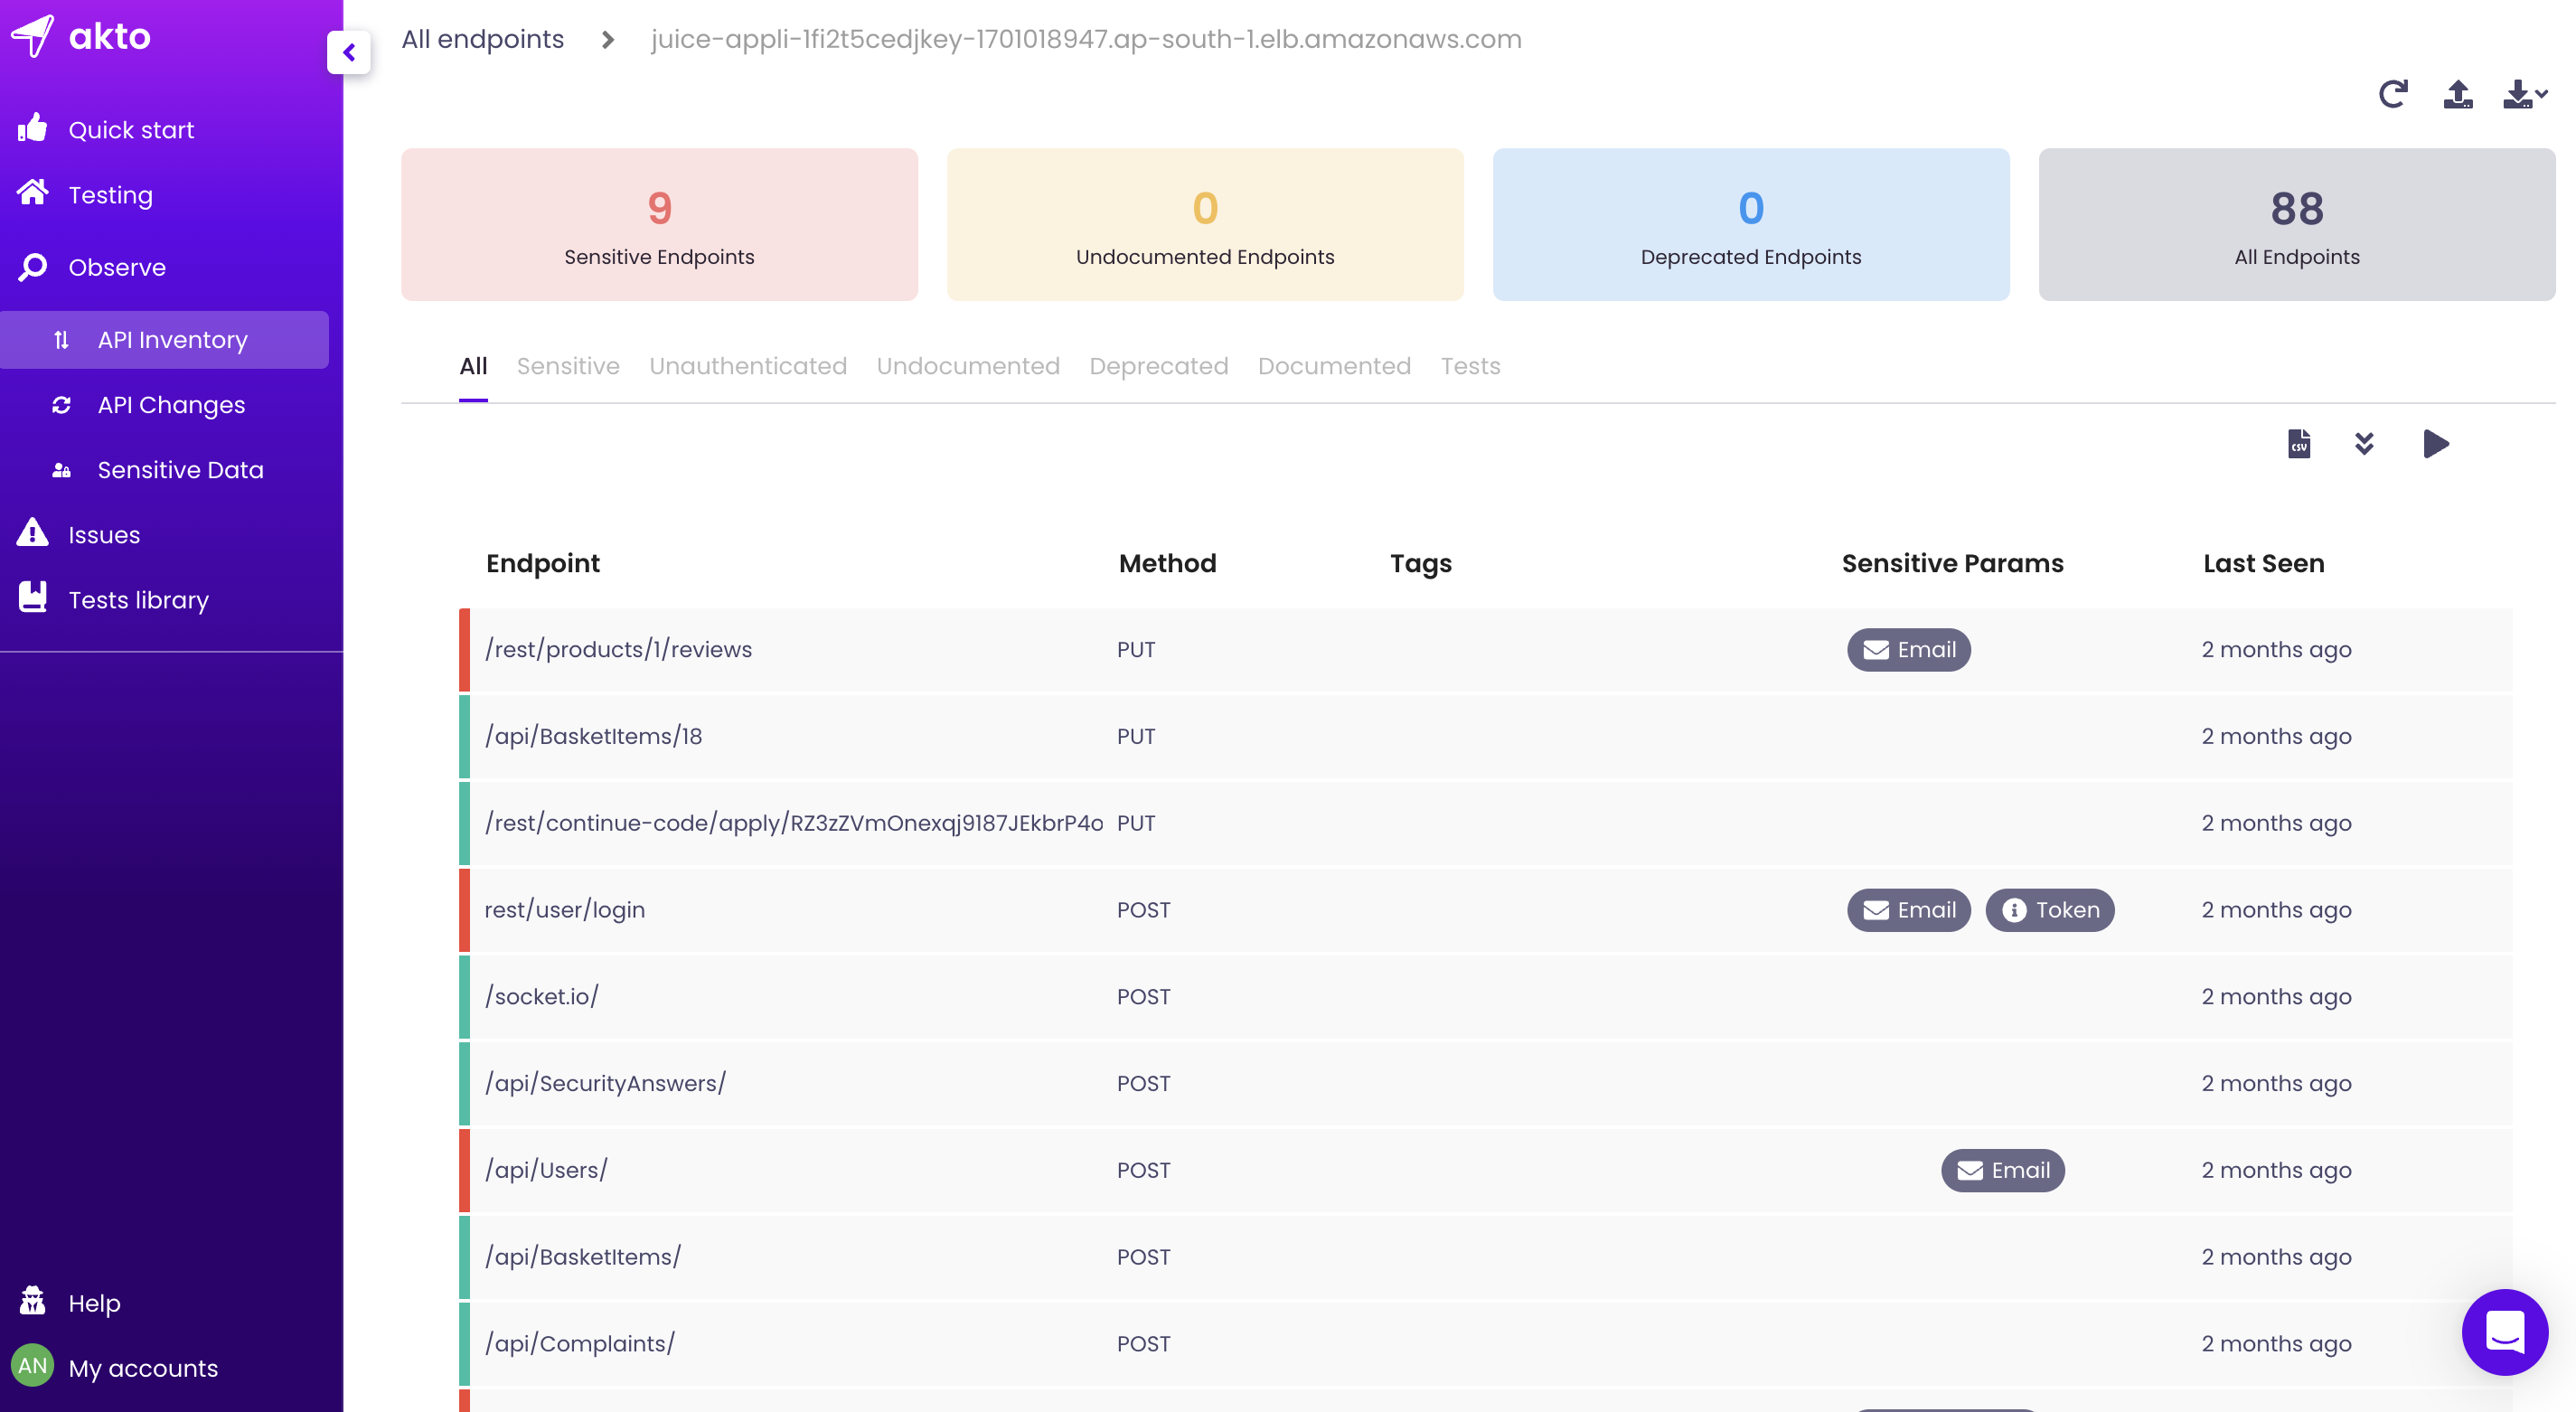 akto-api-security/akto
Open-source API security platform for continuous API discovery, vulnerability testing, and runtime threat detection. Integrates with CI/CD pipelines…
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
 juice-shop/multi-juicer
Host and manage multiple Juice Shop instances for security trainings and Capture The Flags
 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…