
owasp-java-encoder
The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…

The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…


🔧 Fix vulnerable versions in Next.js and React RSC apps with one command to secure against CVE-2025-66478. Improve your app's safety effortlessly.

A powerfull websites compiler/obfuscator for optimization or intellectual property protection purposes.

All the materials for Gareth Heyes' Black Hat talk: CSS: the bomb inside your inbox.

This repository documents CVE-2026-48849, a Stored Cross-Site Scripting (XSS), HTML Injection, and CSS Injection vulnerability discovered in…

CVE-2026-42897 - Exchange Health Checker blind spot: outbound IIS URL Rewrite rules silently ignored, making EOMT mitigations invisible in diagnostic…

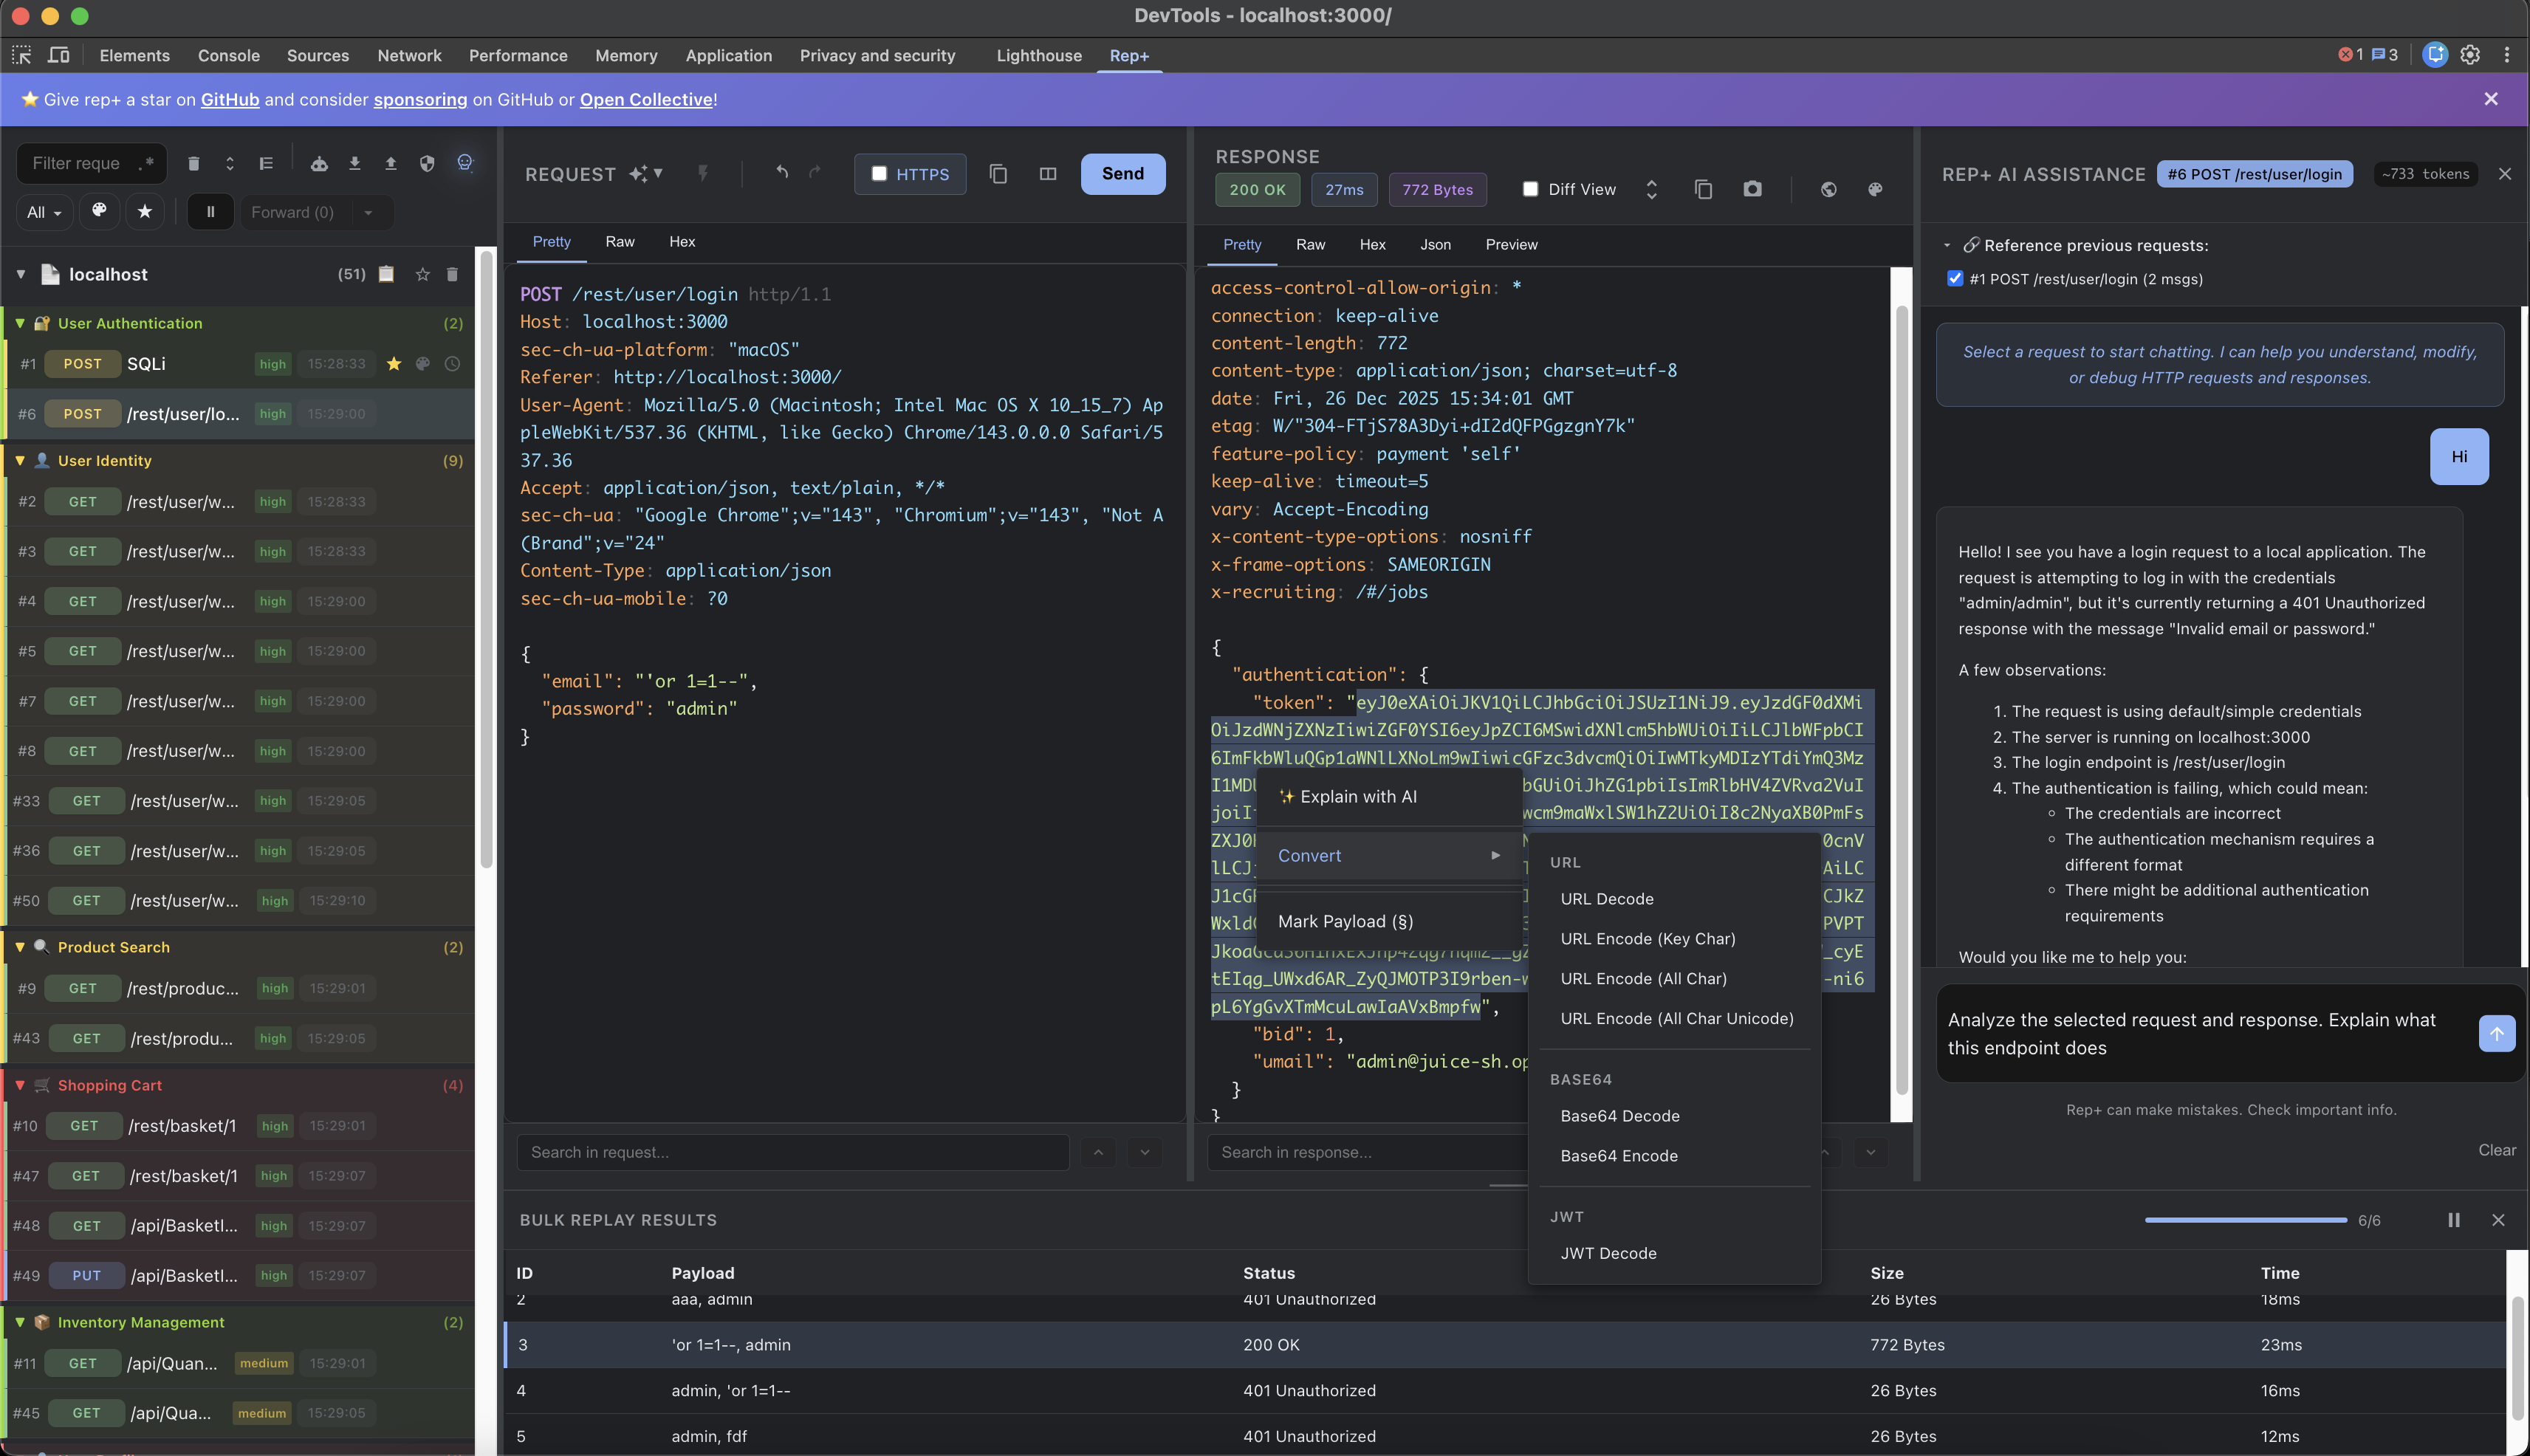
rep+ — Burp-style HTTP Repeater for Chrome DevTools with built‑in AI to explain requests and suggest attacks

Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…

Java library for fast, configurable HTML sanitization from untrusted sources. Uses policy-driven scanning to remove malicious JavaScript and CSS,…

Fast, configurable HTML sanitization library for preventing XSS and malicious code injection from untrusted user input. Provides a policy-driven API…

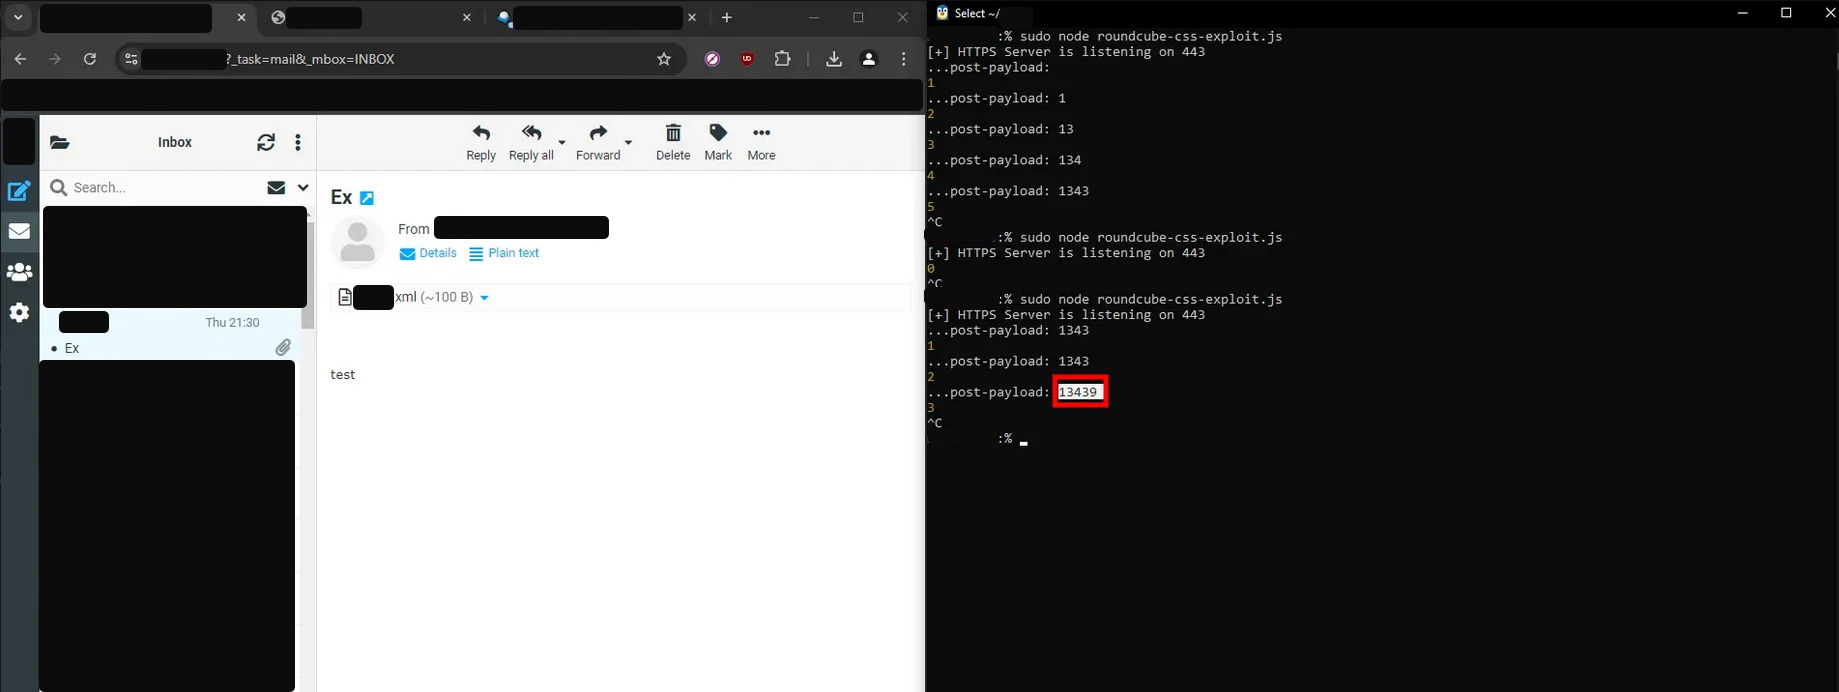
POC for Roundcube vulnerabilities CVE-2024-42008 and CVE-2024-42010

Mitigate CVE-2018-6389 WordPress load-scripts / load-styles attacks

Chrome extension and Express server that exploits keylogging abilities of CSS.