

CVE-2021-41773-Apache-Path-Traversal-Lab
 1833ravikumar-max/cve-2021-41773-apache-path-traversal-lab
Docker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
ctfeducationexploitation+6
1833ravikumar-max/cve-2021-41773-apache-path-traversal-labDocker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
 polosss/by-poloss..-..cve-2026-19125
Verified proof-of-concept exploiting the EthPress <= 2.3.5 unauthenticated authentication bypass, granting a WordPress administrator session via a…
 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
 tno-s3/wuppiefuzz
A coverage-guided REST API fuzzer developed on top of LibAFL
 e4zyy/project-cve-2026-65351
Browser resource exhaustion payload that crashes target systems via memory, GPU, audio, and rendering overload. Designed for authorized security…
 emo-crab/slinger
An HTTP client specifically developed for security researchers
 yora1928/cve-2026-48908-by-yora
Passive security checker for CVE-2026-48908 affecting SP Page Builder.
 bluedragonsecurity/cve-2011-3192-apache-exploit
CVE-2011-3192 - Remote Apache DOS for Apache versions 1.3.x, 2.0.64 and below and 2.2.19 and below. Developed in 2011 by Antonius (ev1lut10n / w1sdom)
 ebrasha/abdal-cve-2026-63030
Abdal CVE-2026-63030 is a professional WordPress vulnerability scanner designed to detect exposure to CVE-2026-63030 through version analysis and…
 ebrasha/abdal-cve-2026-60137
Abdal CVE-2026-60137 is an advanced WordPress security scanner for identifying systems potentially affected by the CVE-2026-60137 SQL Injection…
 codeb0ssx/cve-2026-15583-poc
Academic proof-of-concept demonstrating CVE-2026-15583 for authorized security research.
 codeb0ssx/cve-2026-46442-poc
Academic proof-of-concept demonstrating CVE-2026-46442 for authorized security research.
 underh0st/cpanel-audit-remediation-tool
Audit and incident response tool for CVE-2026-41940 vulnerability
 ptechamanja/cve-2026-29000-pac4j-jwt-auth-bypass
Proof-of-Concept (PoC) for an authentication bypass vulnerability affecting applications using pac4j-jwt with JWE (JSON Web Encryption).
 p3nt3st3r-star/majordomo-cve-2026-27179
Proof-of-concept and scanner for CVE-2026-27179, demonstrating vulnerability behavior in controlled environments for academic research and defensive…
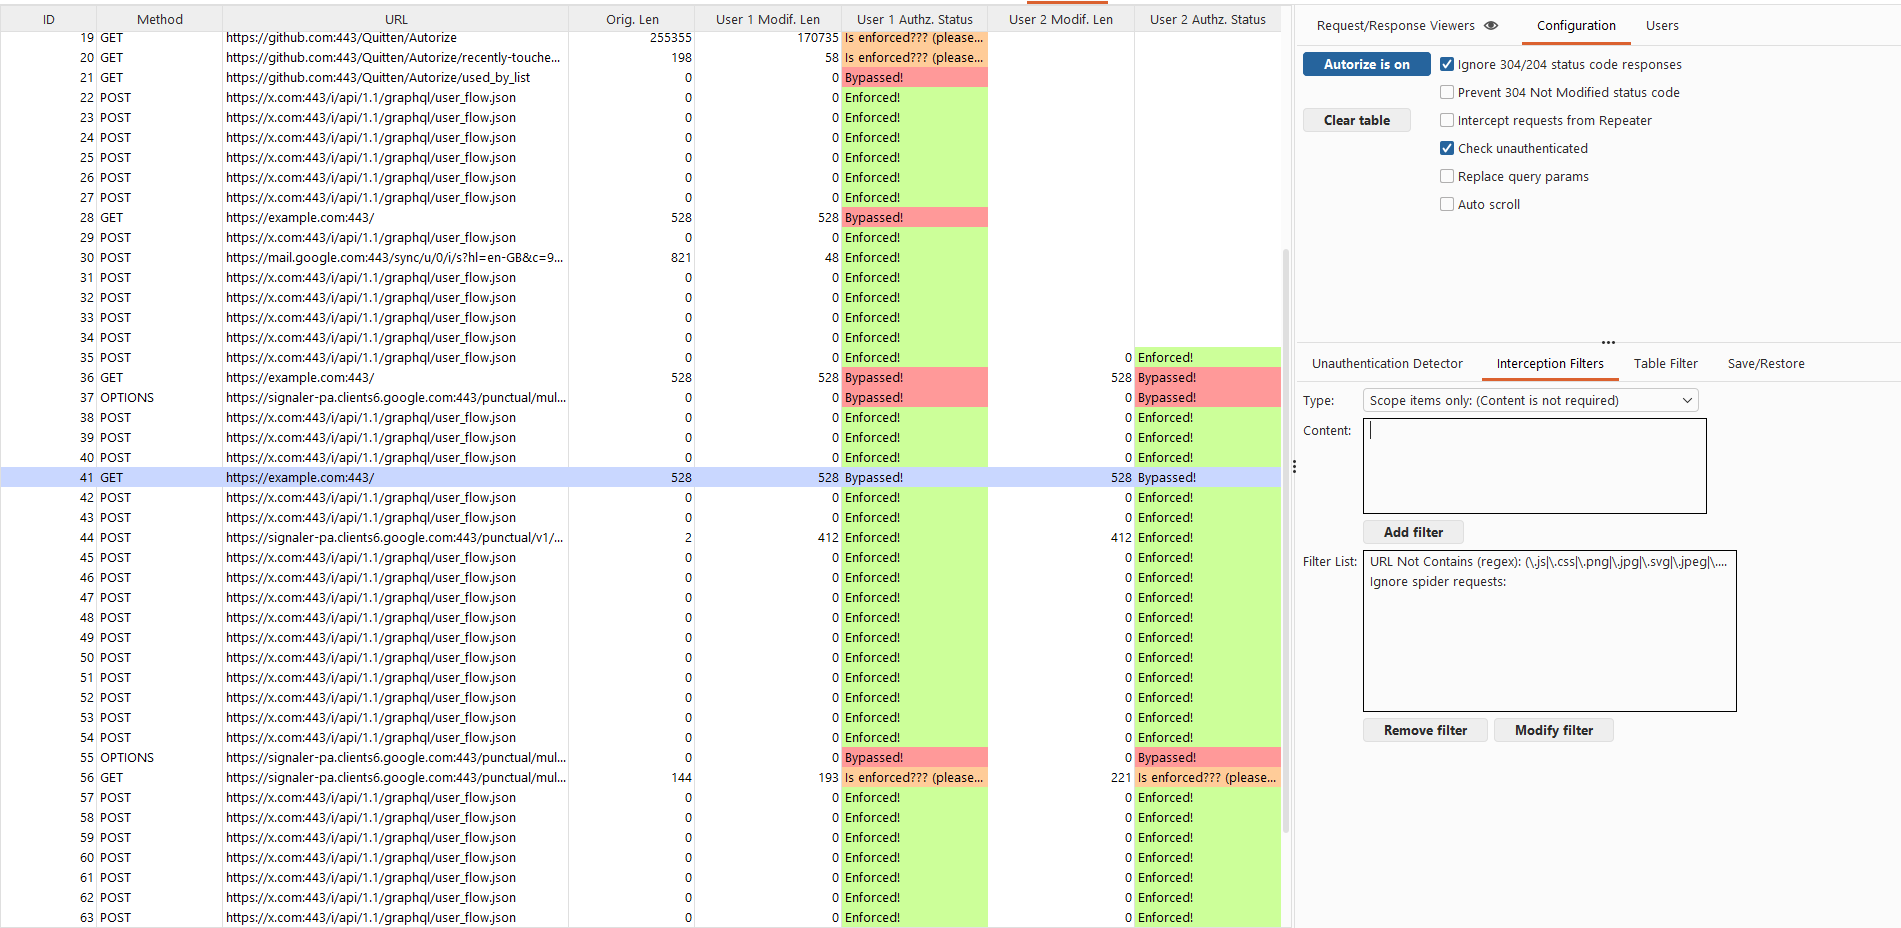 quitten/autorize
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…
 chaitin/mimicry
Active deception tool that transparently migrates attackers from real targets to honeypots during exploitation and post-exploitation, supporting…
 rk-000/apache-hunter
ApacheHunter detects CVE-2024-22393 in Apache Answer servers. Like Wappalyzer but CLI-based. Scans headers, page content, meta tags, and paths to…