

AhsayCBS-Auth-Bypass-RCE
 horizon3ai/ahsaycbs-auth-bypass-rce
A proof of concept exploit for CVE-2026-105133 and CVE-2026-105134 affecting AhsayCBS
authenticationexploitationpayload-development+5
4
horizon3ai/ahsaycbs-auth-bypass-rceA proof of concept exploit for CVE-2026-105133 and CVE-2026-105134 affecting AhsayCBS
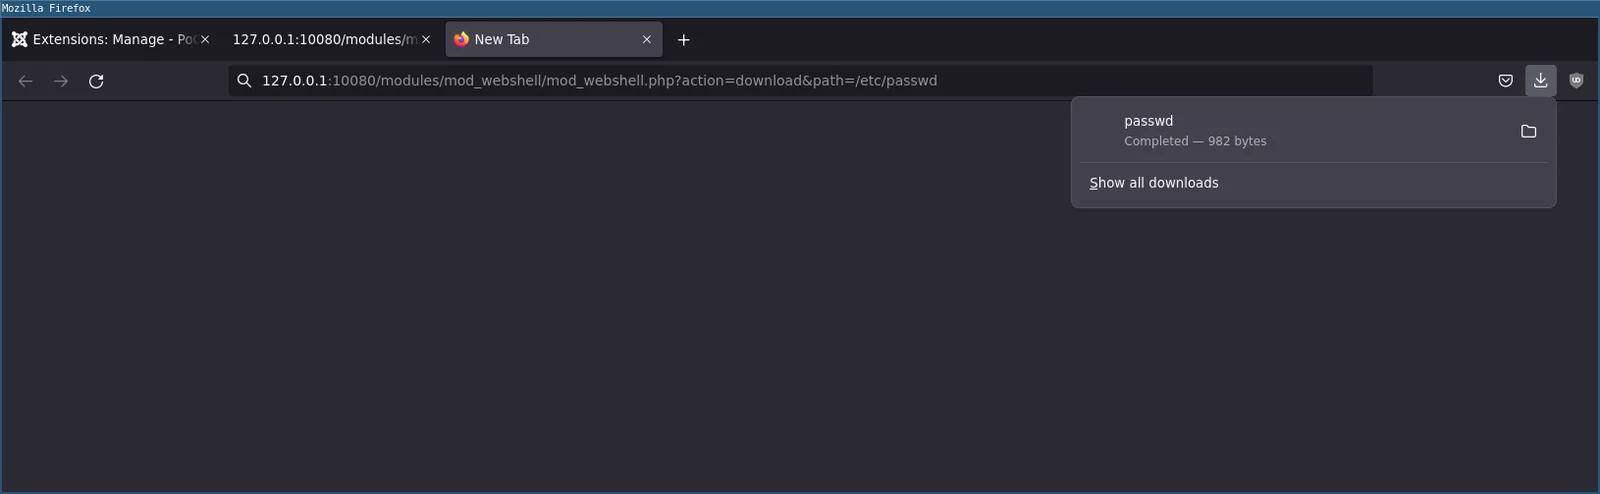 p0dalirius/joomla-webshell-plugin
A webshell plugin and interactive shell for pentesting a Joomla website.
 horizon3ai/cve-2026-102489
Proof-of-concept exploit for CVE-2026-102489 in Zammad: chains a WebSocket session leak into authenticated session hijacking and unauthenticated…
 si13nttt/cve-2025-32432
Python PoC exploiting CVE-2025-32432, an unauthenticated RCE in Craft CMS via Yii DI gadget injection, with assetId scanning, reverse shell, and…
 shadowforge-cyber/cve-2026-104286-poc
Unauthenticated path traversal exploit for CVE-2026-104286 in FortiMail, writing arbitrary files via crafted HTTP/HTTPS requests for red team…
 murrez/cve-2026-102427
Python 3 PoC for CVE-2026-102427, an unauthenticated upload RCE in OrdaSoft Joomla CCK (com_os_cck) via task=getContent and site/uploader.php using a…
 murrez/cve-2026-102425
Python PoC for CVE-2026-102425: unauthenticated RCE in Joomla Balbooa Forms (com_baforms) via field shortcode injection in post-submission PHP…
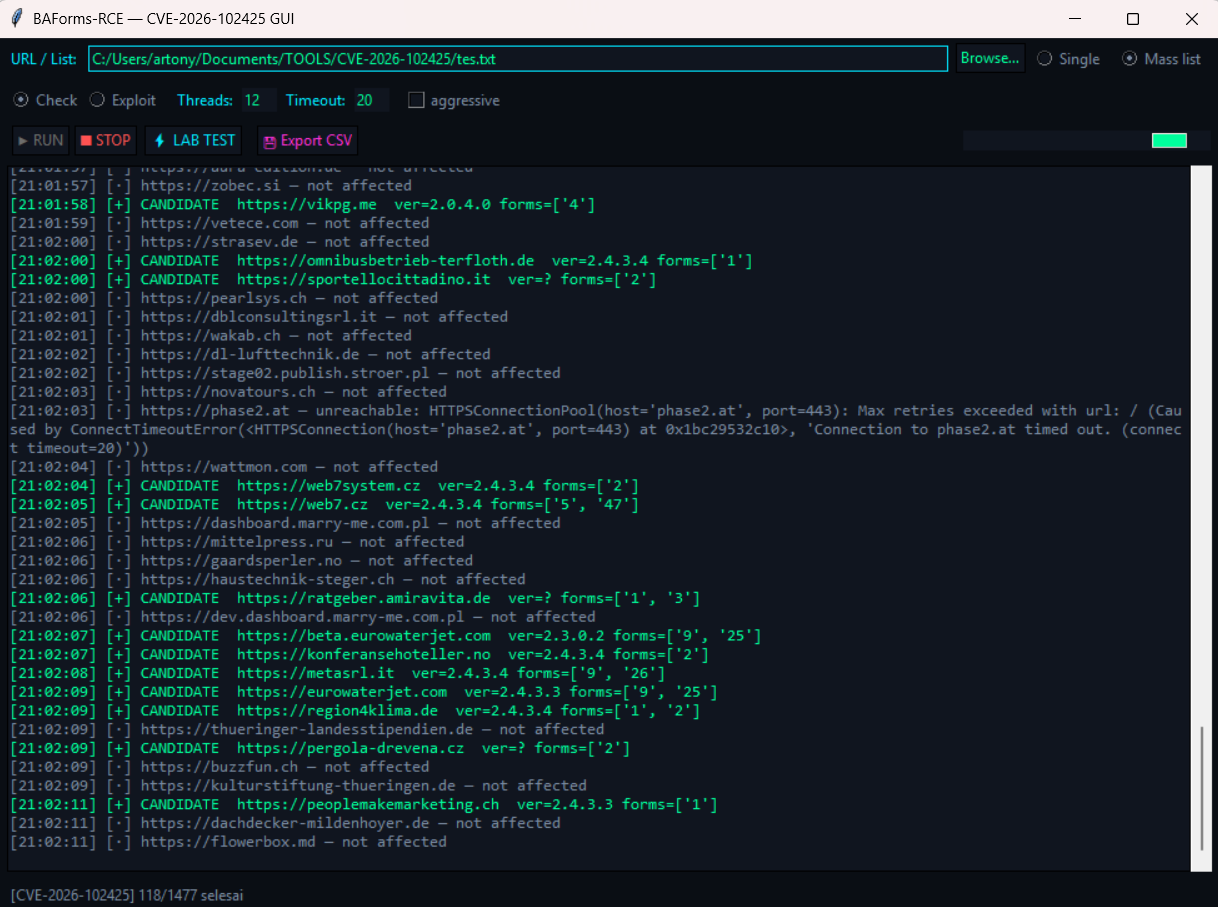 tonydelouvre/cve-2026-102425
GUI scanner and exploit for CVE-2026-102425, an unauthenticated RCE in Balbooa Forms (com_baforms) via PHP shortcode injection, with mass scanning…
 murrez/cve-2026-18143
Python PoC that checks and exploits CVE-2026-18143, an unauthenticated arbitrary file upload in Addify Request a Quote for WooCommerce ≤ 2.9.2 via…
 winrarzipsexploit/cve-2026-48908
Python exploit suite for CVE-2026-48908, an unauthenticated ZIP upload RCE in Joomla SP Page Builder (<=6.6.1), with fingerprinting, batch mode, and…
 si13nttt/cve-2026-22777
Proof-of-concept exploit chaining CRLF injection in ComfyUI-Manager's config endpoint with an arbitrary git install to achieve unauthenticated remote…
 petriqore/cve-2026-26026_poc
PoC script for CVE-2026-26026 GLPI versions 11.0.0 through 11.0.5
 0xtatsuki/cve-2026-31857
Craft CMS RCE via relational conditionals in the control panel
 mrdark-ops/cve-2026-38526
Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticates, uploads a PHP webshell via /admin/tinymce/upload, and executes commands…
 khush-613/cve-2026-44011-poc
Python proof-of-concept exploit for CVE-2026-44011, an authenticated RCE in Craft CMS via Yii behavior injection, with two-stage command output…
 z3rodayhacks/cve-2026-63030-cve-2026-60137
Pre-auth RCE proof-of-concept chaining a WordPress REST batch API auth bypass with WP_Query SQL injection to dump hashes, add admin users, or plant a…
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
 yym8538/cve-2026-60004
Automated proof-of-concept exploit for CVE-2026-60004, a Gitea diffpatch Git hook RCE that plants a post-index-change hook to gain a reverse shell as…