
nmg
 baguette168/nmg
Generates parameterized .NET memory-shell payloads (VPP, MVC route, HttpListener) compatible with Godzilla, Behinder, and AntSword clients for red…
defensive-toolspayload-developmentpayload-generation+8
15
baguette168/nmgGenerates parameterized .NET memory-shell payloads (VPP, MVC route, HttpListener) compatible with Godzilla, Behinder, and AntSword clients for red…
 0xbruno/wsusploit.net
C# proof-of-concept for CVE-2025-59287 targeting WSUS, demonstrating exploitation and providing defensive detection guidance for IIS logs and Windows…
 berraesen/nextjs-middleware-auth-bypass-lab
Bu laboratuvar ortamını sıfırdan kendim oluşturdum. Next.js uygulaması içerisinde giriş, ana sayfa ve admin sayfalarını hazırladım. Middleware ile…
 mauricelambert/cve-2021-31166
CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.
 nu11secur1ty/iis-backdoor
Stealthy IIS backdoor using hidden ISAPI filter for persistent remote access, data exfiltration, and on-the-fly exploit injection via custom HTTP…
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 mauricelambert/cve-2022-21907
CVE-2022-21907: detection, protection, exploitation and demonstration. Exploitation: Powershell, Python, Ruby, NMAP and Metasploit. Detection and…
 stevenvegar/cve-2000-0649
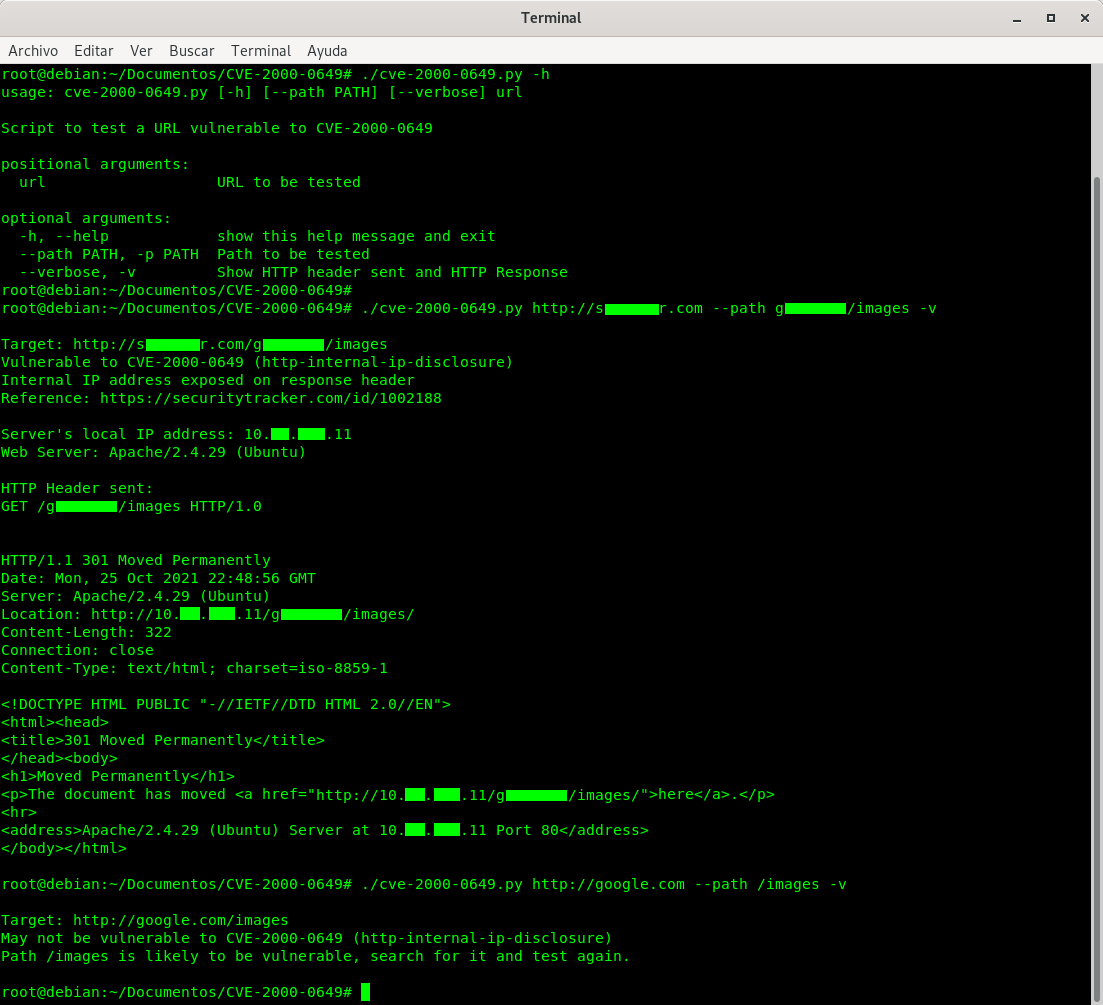
Script fo testing CVE-2000-0649 for Apache and MS IIS servers
 zach115th/toolshellfinder
Scans Windows IIS logs for signs of CVE-2025-53770 & CVE-2025-53771
 killian0713/assignement_3-cve-2017-7269
Educational exploit reproduction of CVE-2017-7269, a buffer overflow in IIS 6.0 WebDAV, with setup guide, vulnerability analysis, and Metasploit…
 renzi25031469/cve-2026-49975-http-2-bomb
Disclosed on June 3, 2026, the "HTTP/2 Bomb" is an unauthenticated remote DoS that combines an HPACK compression bomb with a Slowloris-style hold to…
 saykino/cve-2025-66838
Documentation of CVE-2025-66838: a rate-limiting vulnerability in ARIS file upload API allowing authenticated remote attackers to cause denial of…
 netjbs/cve-2017-0055-poc
This it's a PoC of Departament of justice VDP. By rootkit
 llamakko/cve-2015-7214
Proof-of-concept exploit for CVE-2015-7214 demonstrating Same-Origin Policy bypass in Firefox 42.0 via data and view-source URIs, with local and…
 gpiechnik2/nmap-cve-2022-21907
Repository containing nse script for vulnerability CVE-2022-21907. It is a component (IIS) vulnerability on Windows. It allows remote code execution.…
 corelight/cve-2021-31166
Detection rules (Suricata + Zeek) for CVE-2021-31166 HTTP Protocol Stack vulnerability, providing network-level alerts on exploit attempts against…
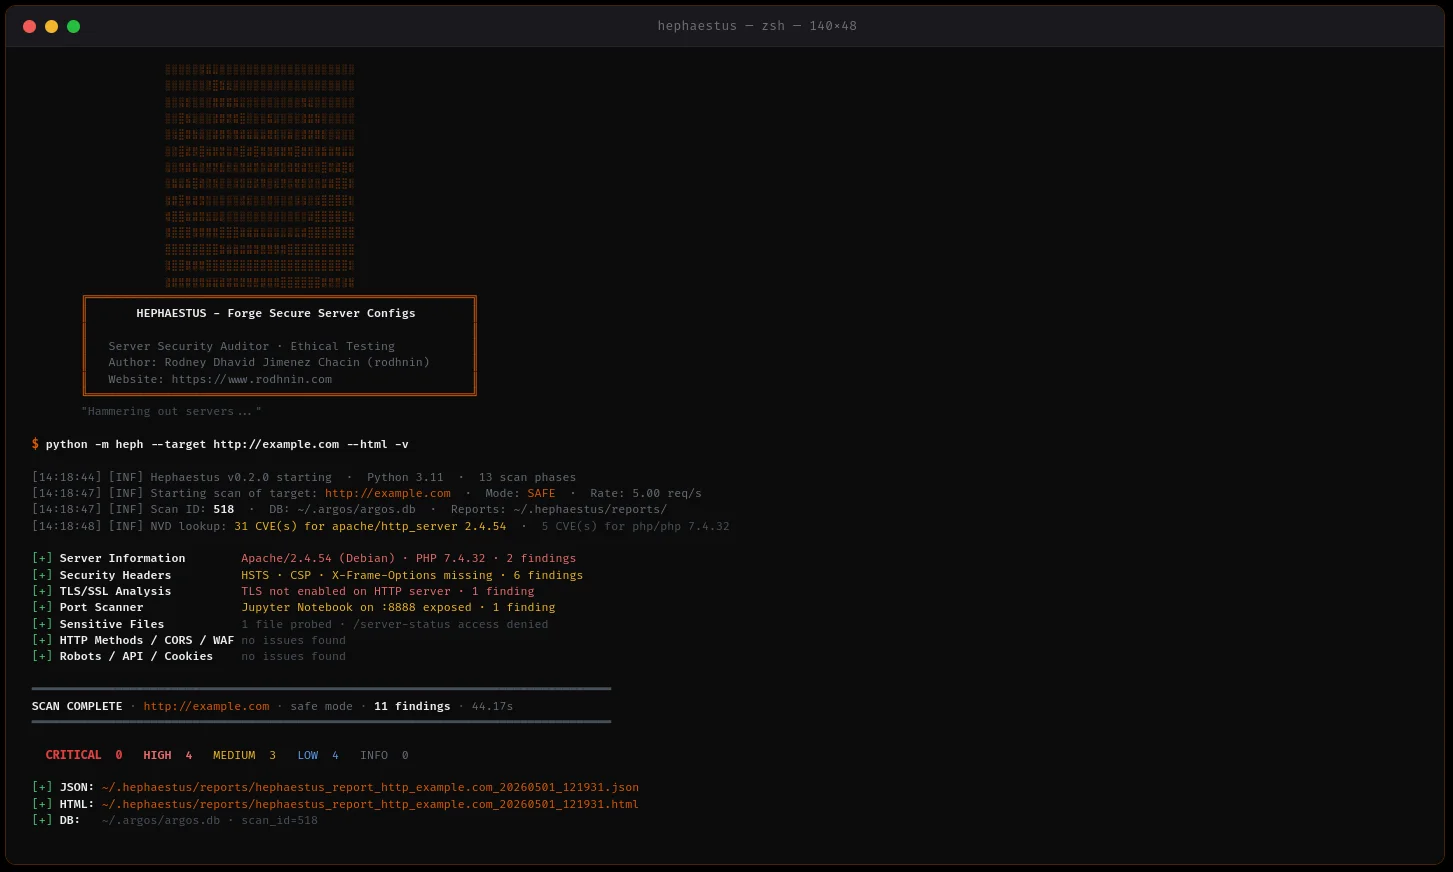 rodhnin/hephaestus-server-forger
server security auditor scanning Apache, Nginx, and IIS configurations with AI-powered hardening guides and professional reporting.
 atiilla/cve-2026-42897
CVE-2026-42897 - Exchange Health Checker blind spot: outbound IIS URL Rewrite rules silently ignored, making EOMT mitigations invisible in diagnostic…