
CVE-2026-42536-PoC
 erberkan/cve-2026-42536-poc
Heap-based Buffer Overflow vulnerability in Apache HTTP Server with mod_xml2enc, xml2StartParse, and untrusted content
exploitationpapers-researchvulnerability-analysis+2
erberkan/cve-2026-42536-pocHeap-based Buffer Overflow vulnerability in Apache HTTP Server with mod_xml2enc, xml2StartParse, and untrusted content
 fortbridge/stylesmuggler
Python PoC reproducing CVE-2026-75650 StyleSmuggler, an unauthenticated Magento RCE via report poisoning and failed-payment rendering, with canary…
 vid4l-07/roxy
Terminal-based HTTP intercepting proxy with TUI for capturing, inspecting, and modifying requests in real time, plus a Repeater for resending and…
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 dylan-chainguard/cve-2026-22732-poc
Proof-of-concept demonstrating CVE-2026-22732, a Spring Security flaw where setIntHeader("Content-Length") drops all security headers, with…
 hakaioffsec/cve-2026-63642
Proof-of-concept exploit scripts for CVE-2026-63642 and CVE-2026-63643, SSRF vulnerabilities in MagicMirror²'s Calendar module allowing…
 bombobombone/cve-2026-73315
Proof-of-concept and technical write-up for CVE-2026-73315, an SSRF in XenForo's PayPal REST webhook handler allowing blind server-side HTTP requests.
 xiaoqimikko/netty-http-check
Offline Java tool that scans application jars to determine exposure to 14 Netty codec-http CVEs, identifying the exact patched version…
 dinosn/cve-2026-75650-magento-validation-lab
Docker lab reproducing the complete CVE-2026-75650 StyleSmuggler unauthenticated HTTP RCE and validating Adobe VULN-39341.
 pavanchow/cve-2026-33234
SSRF via smtplib raw TCP sockets bypassing HTTP blocklist in AutoGPT SendEmailBlock
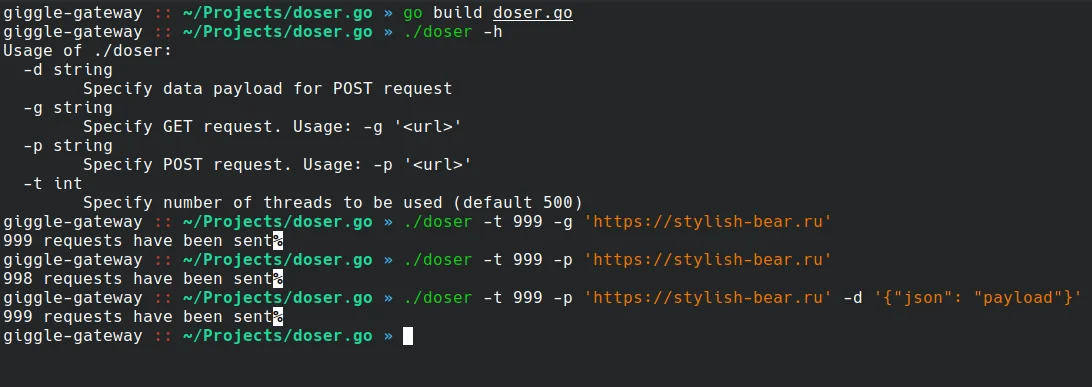 quitten/doser.go
DoS tool for HTTP requests (inspired by hulk but has more functionalities)
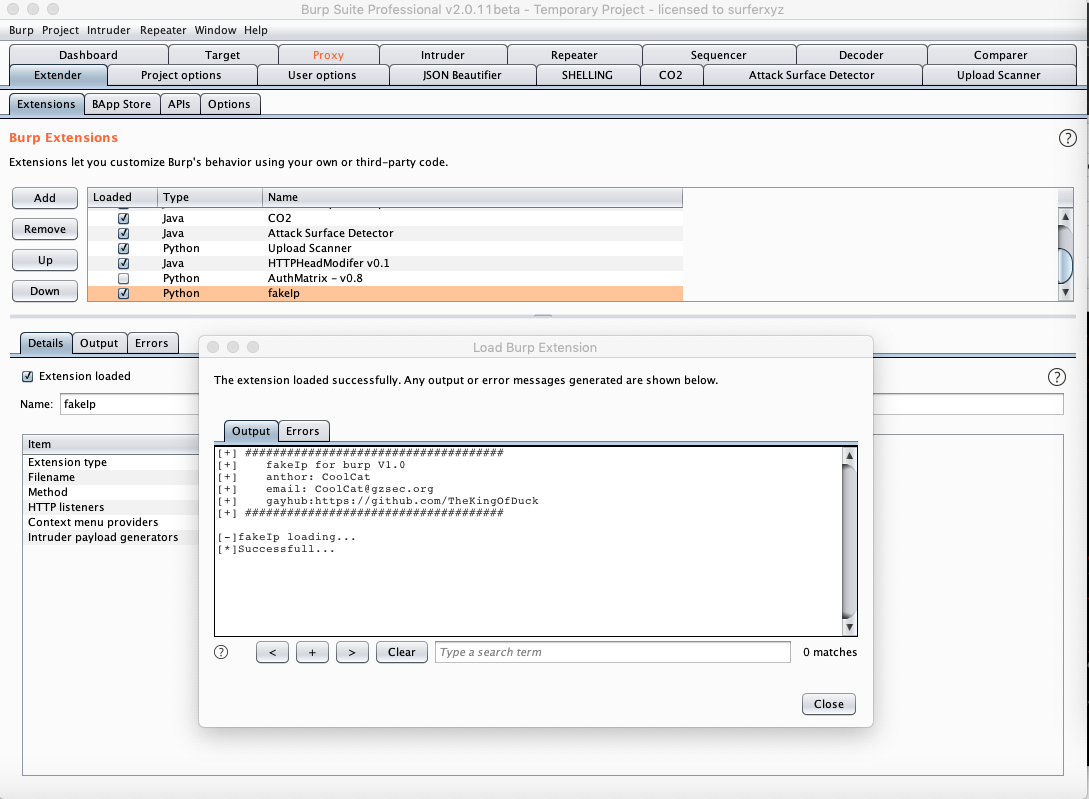 thekingofduck/burpfakeip
Burp Suite extension for spoofing IP addresses in HTTP requests, enabling testing of server-side IP restrictions and bypassing IP-based access…
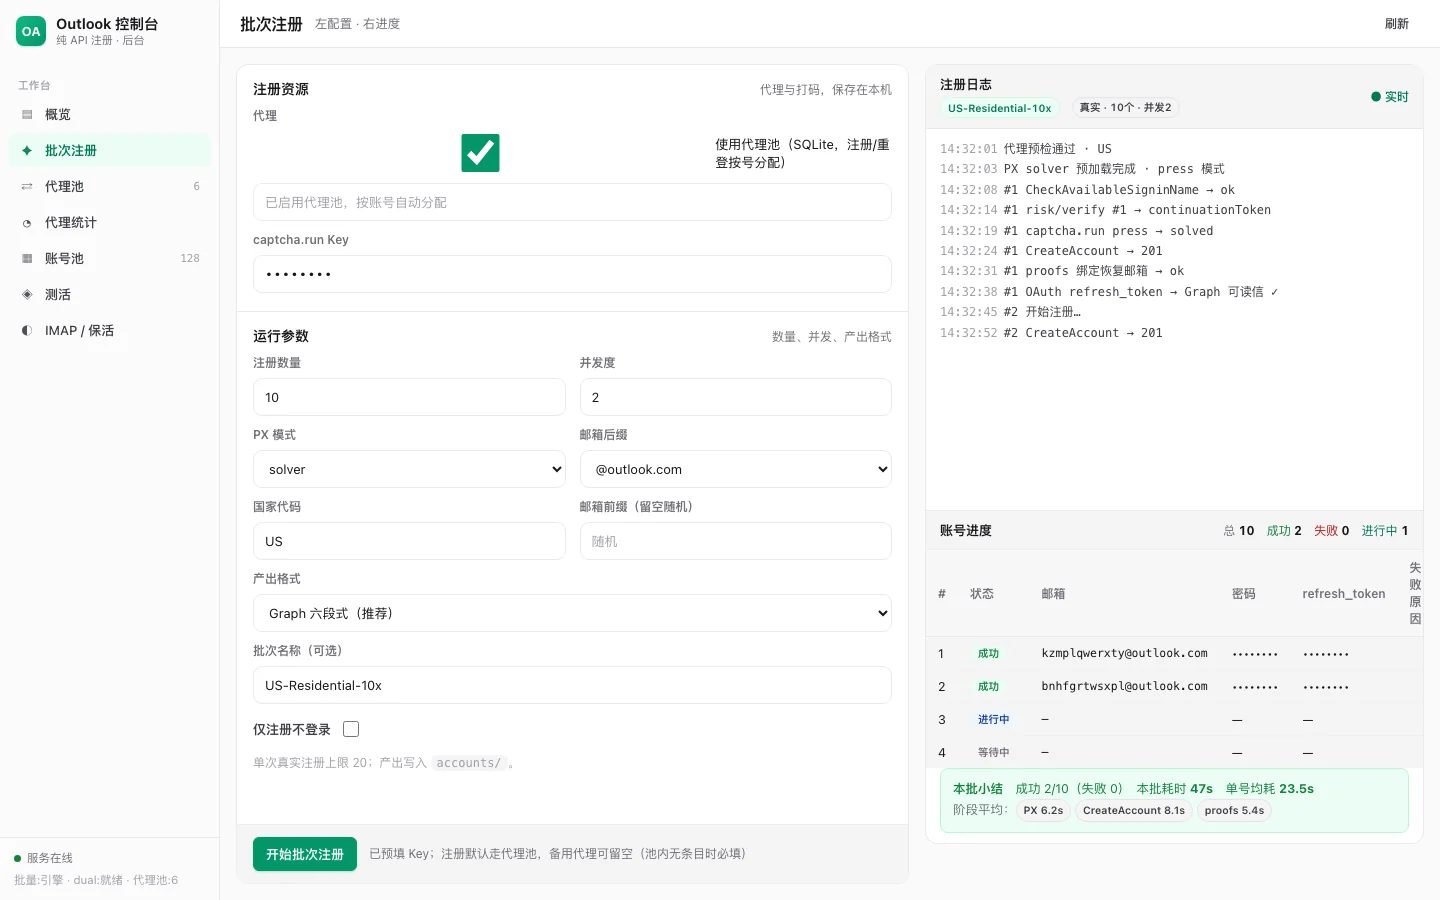 lxf746/outlook-auto-register
Automated Outlook account registration tool using pure HTTP protocol with PerimeterX captcha solving, proxy pool management, and email token…
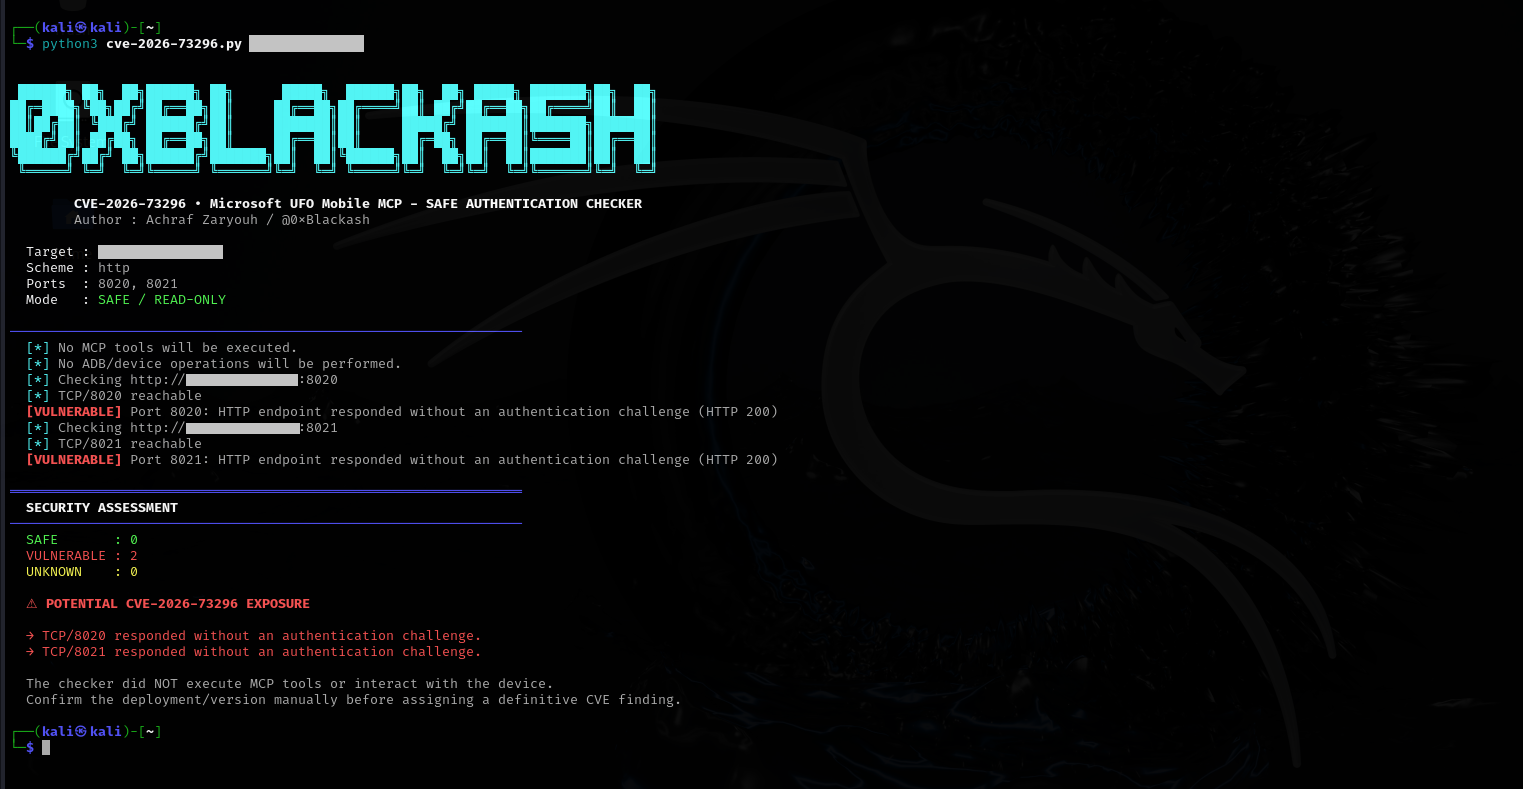 0xblackash/cve-2026-73296
Non-destructive security assessment tool for CVE-2026-73296, checking authentication boundaries on exposed Mobile MCP HTTP servers (ports 8020/8021)…
 vaibhav91one/log4shell-cve-lab
Intentionally vulnerable Log4j 2.14.1 HTTP service for hands-on practice with CVE-2021-44228 (Log4Shell) in an isolated sandbox environment.
 zeetee1235/cve-2026-21962
Verified PoC and analysis for CVE-2026-21962, an access-control bypass in Oracle HTTP Server/WebLogic Proxy Plug-in via URI normalization…
 rshosting/apache-cve-2026-23918-fix
Upgrade to Apache 2.4.67 to fix CVE-2026-23918 vulneribility
 cyfare/cve-2026-23918-apache-http-server-doublefree-poc
Proof-of-concept exploit for CVE-2026-23918, a double-free vulnerability in Apache HTTP Server, demonstrating remote crash via crafted requests.