
CVE-2026-33331
 abhayclasher/cve-2026-33331
Local lab reproducing stored XSS in oRPC's OpenAPI docs generation (CVE-2026-33331), with vulnerable and patched versions for comparison and a…
educationexploitationlabs-practice+3
abhayclasher/cve-2026-33331Local lab reproducing stored XSS in oRPC's OpenAPI docs generation (CVE-2026-33331), with vulnerable and patched versions for comparison and a…
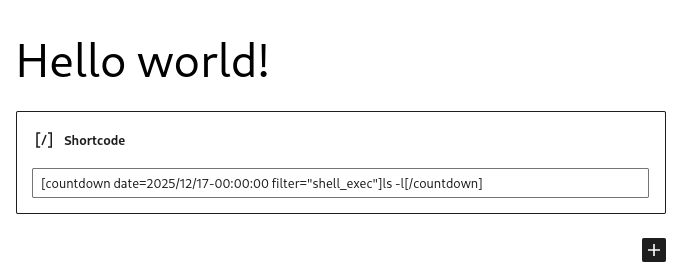 nimisha17/poc-cve-2025-9519
Proof-of-concept exploit for CVE-2025-9519, demonstrating remote code execution in WordPress Easy Timer plugin via a crafted shortcode filter, with…
 ory/oathkeeper
A cloud native Identity & Access Proxy / API (IAP) and Access Control Decision API that authenticates, authorizes, and mutates incoming HTTP(s)…
 kuninogu/drupal-openai-provider-ssrf-cve-2026-13233
CVE-2026-13233 (Drupal OpenAI Provider, SA-CONTRIB-2026-053): response-URL SSRF / local file read. Untrusted upstream, not the prompt. Safe…
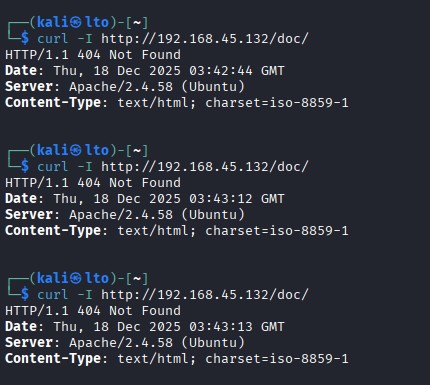 lto7777777/cve-1999-0678
CVE-1999-0678- /doc directory browsable
 m0d0ri205/wargame_re-ls
CTF challenge exploiting CVE-2025-0184 DOCX SSRF vulnerability to access internal admin service and retrieve a flag. Includes exploit generator and…
 emicoecommerce/magento-apsb22-48-security-patches
This repository contains potential security patches for the Magento APSB22-48 and CVE-2022-35698 security vulnerability
 walidriouah/cve-2026-30691
CVE-2026-30691: Stored Cross-Site Scripting (XSS) in @cyntler/react-doc-viewer
 xdrake1010/cve-2017-11882-preventer
CVE-2017-11882 Preventer for .docx files
 garrytan/gstack
Use Garry Tan's exact Claude Code setup: 23 opinionated tools that serve as CEO, Designer, Eng Manager, Release Manager, Doc Engineer, and QA
 olizimmermann/phishcollector
PhishCollector is a research framework for collecting, analysing, and tracking phishing sites.
 josue87/burpmetafinder
Burp Suite extension for extracting metadata from files
 caido/caido
Lightweight web proxy for intercepting, inspecting, and modifying HTTP traffic to audit web applications during penetration testing and bug bounty…
 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…