
chithi
 chithi-dev/chithi
The next generation encrypted file sharing project
authentication-authorizationcloud-securitydata-exfiltration+3
chithi-dev/chithiThe next generation encrypted file sharing project
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 securecodebox/securecodebox
Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…
 caddyserver/caddy
Fast and extensible multi-platform HTTP/1-2-3 web server with automatic HTTPS
 efforg/https-everywhere
A browser extension that encrypts your communications with many websites that offer HTTPS but still allow unencrypted connections.
 raghavd3v/crlfsuite
The most powerful CRLF injection (HTTP Response Splitting) scanner.
 xkiian/awswaf
AWS WAF Solver, full reverse implemented in 100% Python & Golang.
 osxninja/cybersecurity-projects
This repository contains the complete record of my three-year research journey, covering the project from foundational concepts to advanced-level…
 notsosecure/blacklist3r
Audits ASP.NET applications for pre-published machine keys to detect ViewState deserialization vulnerabilities and insecure forms authentication…
 jaeles-project/jaeles-signatures
Default signature for Jaeles Scanner
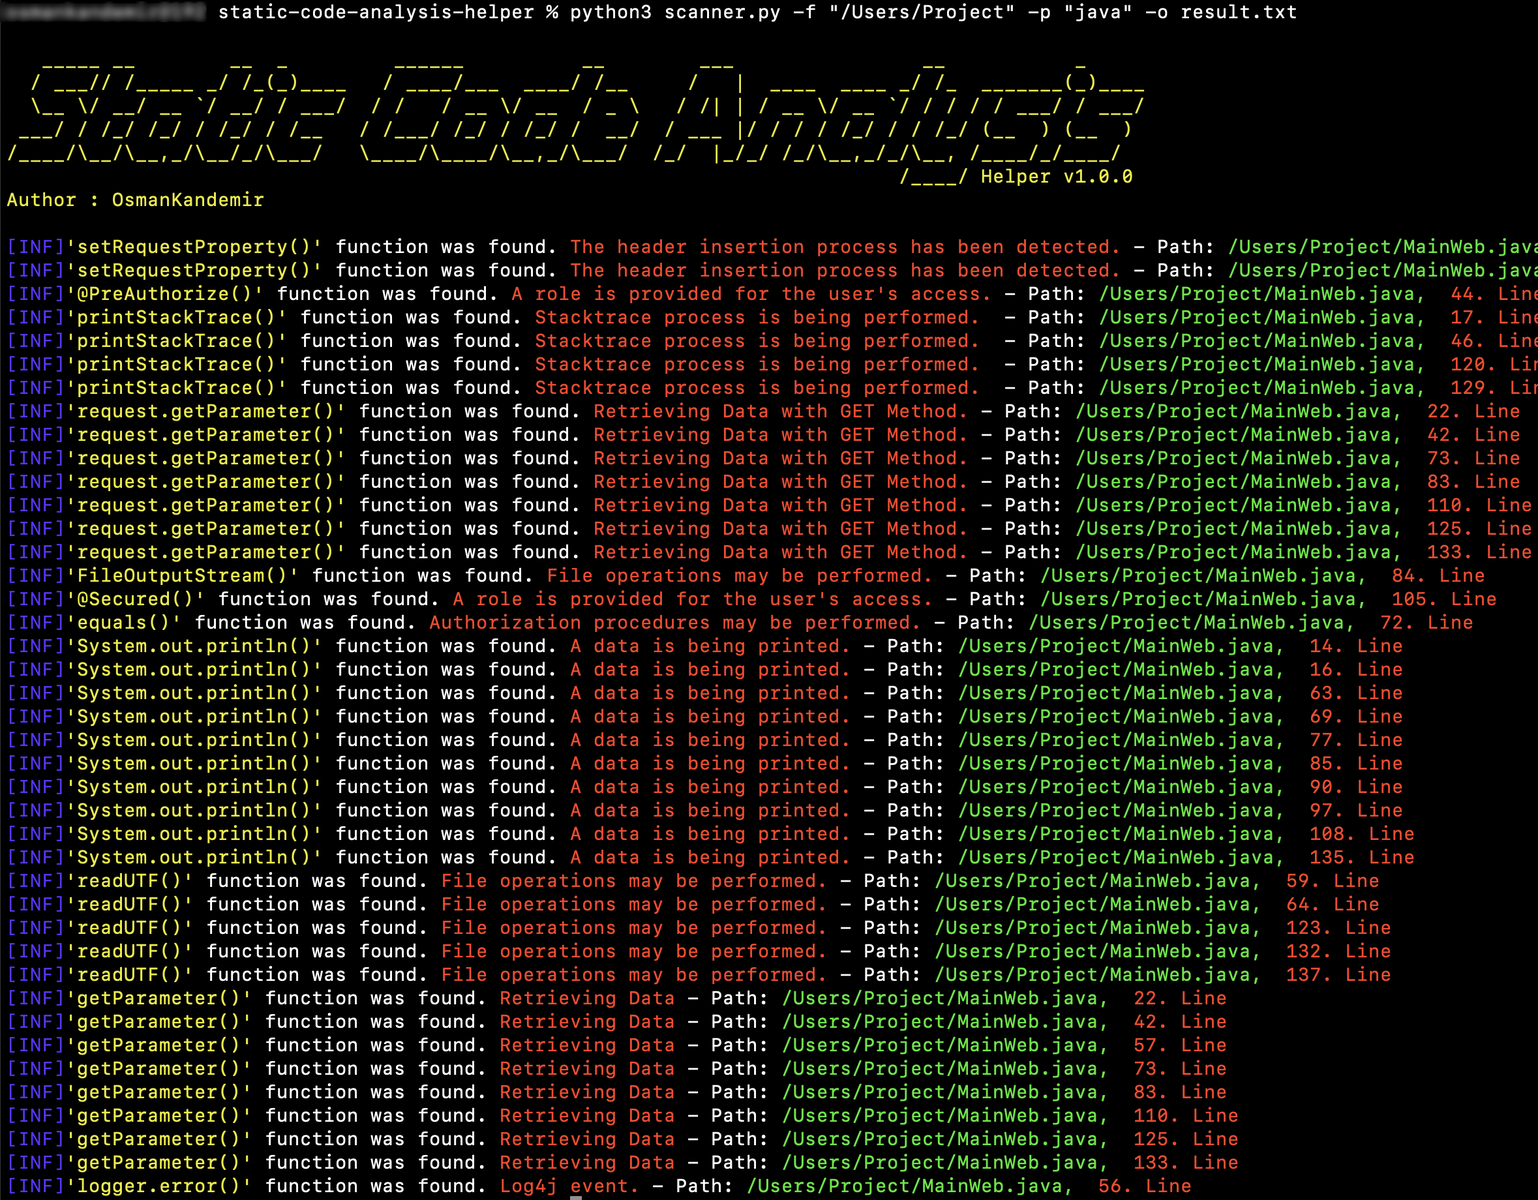 osmankandemir/static-code-analysis-helper
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…
 josue87/burpmetafinder
Burp Suite extension for extracting metadata from files
 beefproject/beef
The Browser Exploitation Framework Project
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
 daryllundy/cve-2025-53770
Network-based vulnerability scanner for detecting systems vulnerable to CVE-2025-53770 (unsafe deserialization). Includes PowerShell and Python…
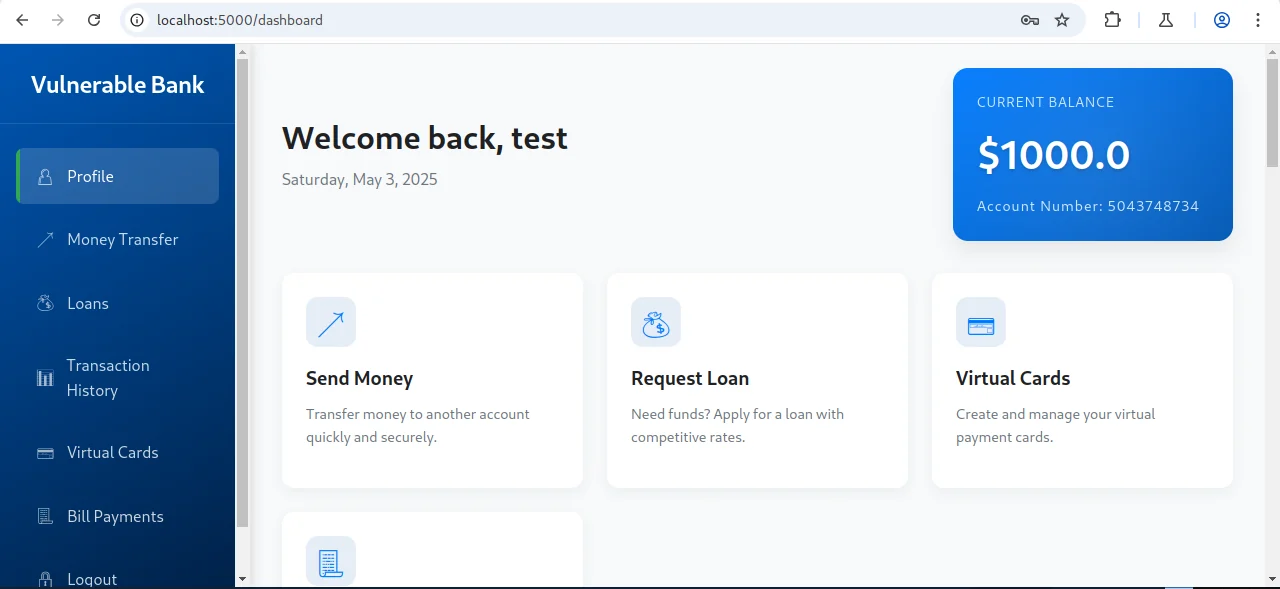 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…