
CVE-2022-41401
 ixsly/cve-2022-41401
Proof-of-concept exploit for CVE-2022-41401, a server-side request forgery (SSRF) vulnerability in OpenRefine <= v3.5.2, enabling unauthorized…
exploitationinformation-gatheringpenetration-testing+2
1
ixsly/cve-2022-41401Proof-of-concept exploit for CVE-2022-41401, a server-side request forgery (SSRF) vulnerability in OpenRefine <= v3.5.2, enabling unauthorized…
 santandersecurityresearch/corsair_scan
Automated CORS misconfiguration scanner that tests Origin header injection, wildcard reflection, and credential leakage across web applications and…
 mindpatch/lorsrf
Fast CLI tool to find the parameters that can be used to find SSRF or Out-of-band resource load :artificial_satellite: :crab:
 nahamsec/resources-for-beginner-bug-bounty-hunters
A list of resources for those interested in getting started in bug bounties
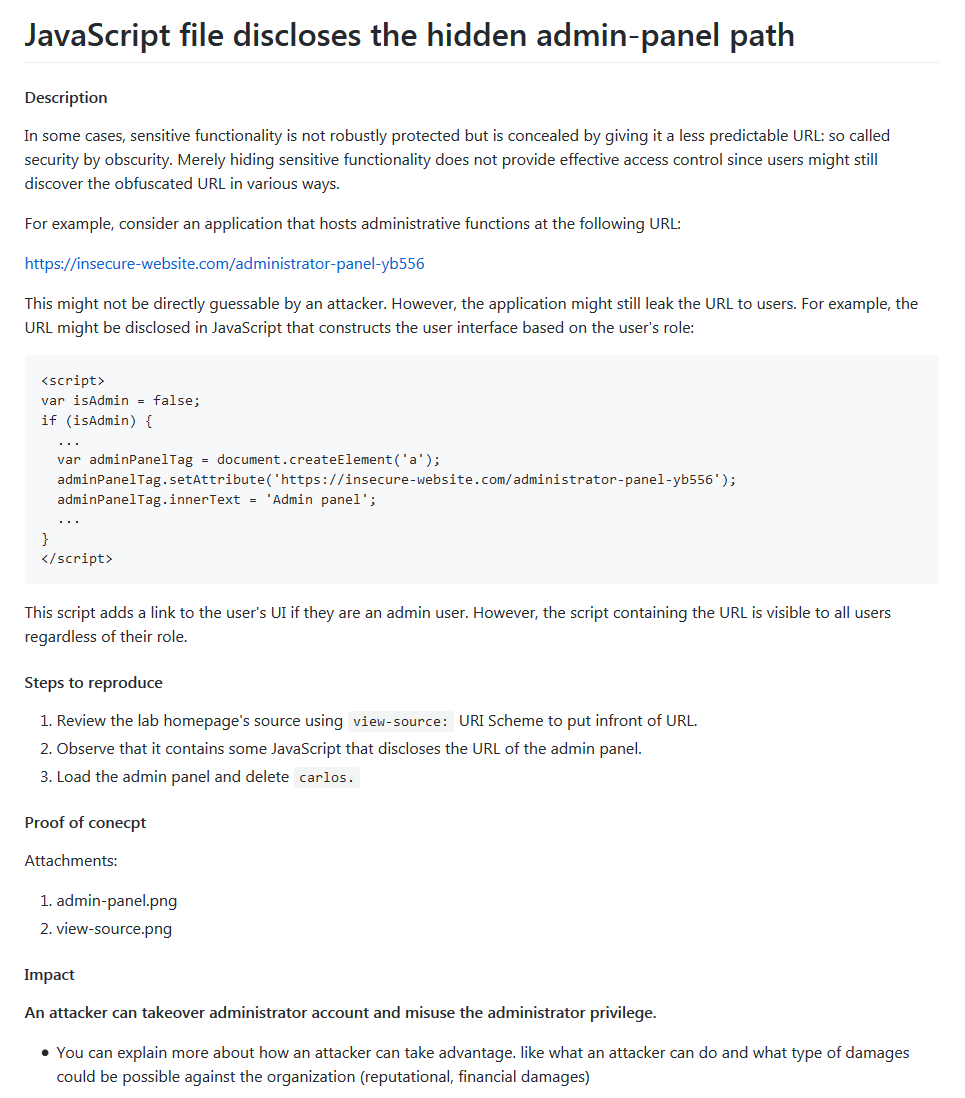
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 bittentech/bug-bounty-beginner-roadmap
This is a resource factory for anyone looking forward to starting bug hunting and would require guidance as a beginner.
 biitts/cve-2026-72001-pangolin-cross-org-auth-bypass
PoC for CVE-2026-72001 — Pangolin < 1.22.0 cross-organization resource authentication bypass via the share-link access-token endpoint (CWE-639, CVSS…
 e4zyy/project-cve-2026-65351
Browser resource exhaustion payload that crashes target systems via memory, GPU, audio, and rendering overload. Designed for authorized security…
 alphaseclab/all-my-collection-repos
All Security Resource Collections Repos That I Published.
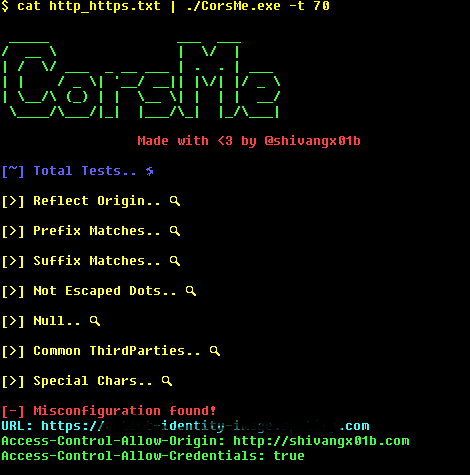 shivangx01b/corsme
Cross Origin Resource Sharing MisConfiguration Scanner
 lylemi/learn-web-hacking
Structured study notes covering web hacking fundamentals, common vulnerabilities, penetration testing techniques, and defensive security, with…
 alkimcoskun/cve-2025-69848-security-advisories
Security advisory for CVE-2025-69848 – Reflected XSS in NetBox ProtectedError handling
 rub-nds/corstest
A simple CORS misconfiguration scanner
 borewit/svg-sanitizer
Java library that sanitizes SVG files by stripping JavaScript, inline event handlers, and script tags while blocking external resource loading to…
 lc/theftfuzzer
TheftFuzzer is a tool that fuzzes Cross-Origin Resource Sharing implementations for common misconfigurations.
 nu11secur1ty/xssight
Educational resource on Cross-site Scripting (XSS) attack techniques, covering non-persistent, persistent, and DOM-based vectors with practical…
 aeyesec/cve-2024-27316_poc
Proof-of-concept exploit for CVE-2024-27316, an HTTP/2 CONTINUATION flood vulnerability in Apache httpd, demonstrating resource exhaustion via…
 george0papasotiriou/cve-2026-11118-http-2-rapid-reset-ddos
Python PoC for CVE-2026-11118 demonstrating HTTP/2 Rapid Reset DDoS via RST_STREAM resource exhaustion; includes vulnerable server simulator and…