
waf-detector
 ammarion/waf-detector
🛡️ High-performance WAF & CDN detection tool. Identify protection layers (Cloudflare, Akamai, AWS, Fastly, and more), run effectiveness and…
defensive-toolsdns-analysisfingerprint-spoofing+8
131
ammarion/waf-detector🛡️ High-performance WAF & CDN detection tool. Identify protection layers (Cloudflare, Akamai, AWS, Fastly, and more), run effectiveness and…
 javascript-obfuscator/javascript-obfuscator
Obfuscates JavaScript and Node.js code with variable renaming, string encryption, control flow flattening, and anti-debugging to protect source code…
 khush-613/cve-2026-44011-poc
Python proof-of-concept exploit for CVE-2026-44011, an authenticated RCE in Craft CMS via Yii behavior injection, with two-stage command output…
 ge0rg3/requests-ip-rotator
A Python library to utilize AWS API Gateway's large IP pool as a proxy to generate pseudo-infinite IPs for web scraping and brute forcing.
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 qin2dim/hcaptcha-challenger
🥂 Gracefully face hCaptcha challenge with multimodal large language model.
 vinylrider/ivantiunlocker
Prevent CVE-2025-22457 and other security problems with Juniper/Ivanti Secure Connect SSL VPN
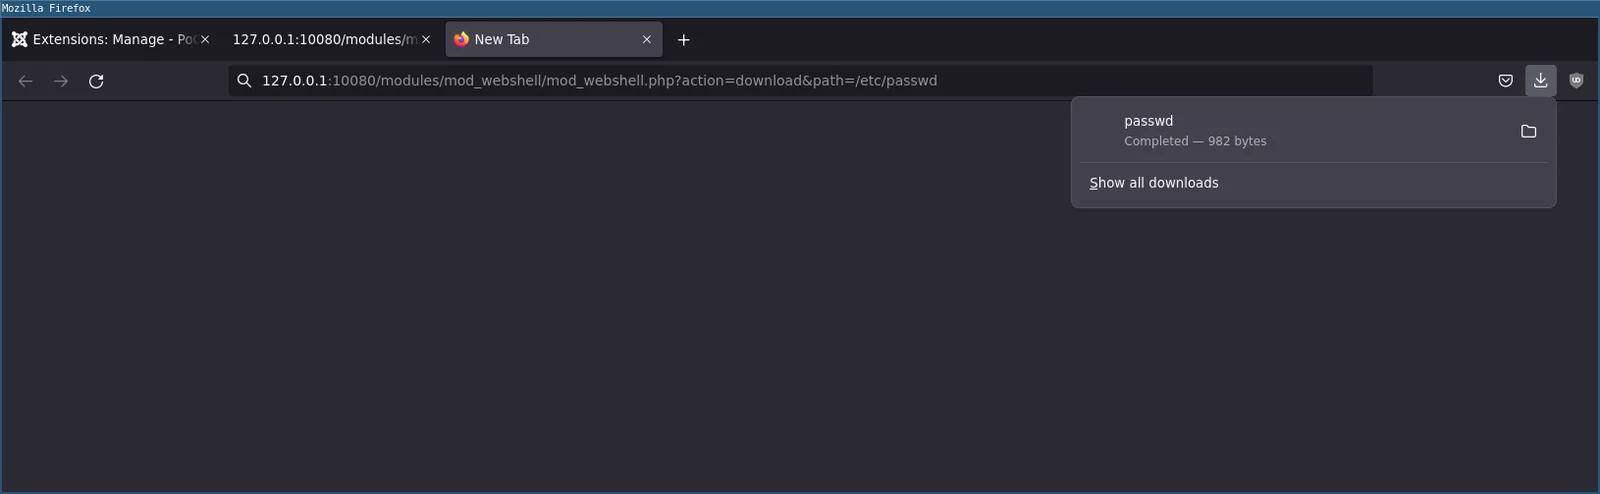 p0dalirius/joomla-webshell-plugin
A webshell plugin and interactive shell for pentesting a Joomla website.
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 dotnetguard/cve-2025-55182-exploit
CVE-2025-55182 — Next.js Flight Deserialization RCE exploit with interactive shell, single-command execution and multi-payload reverse shell chain.…
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 redsection/pfuzz
Modular WAF bypass fuzzer with multi-threading, request manipulation, and payload encoding for red team web application testing.
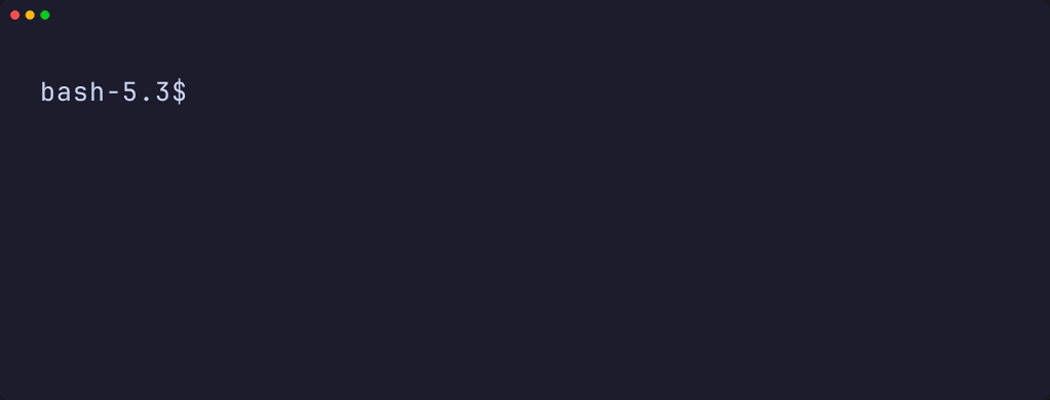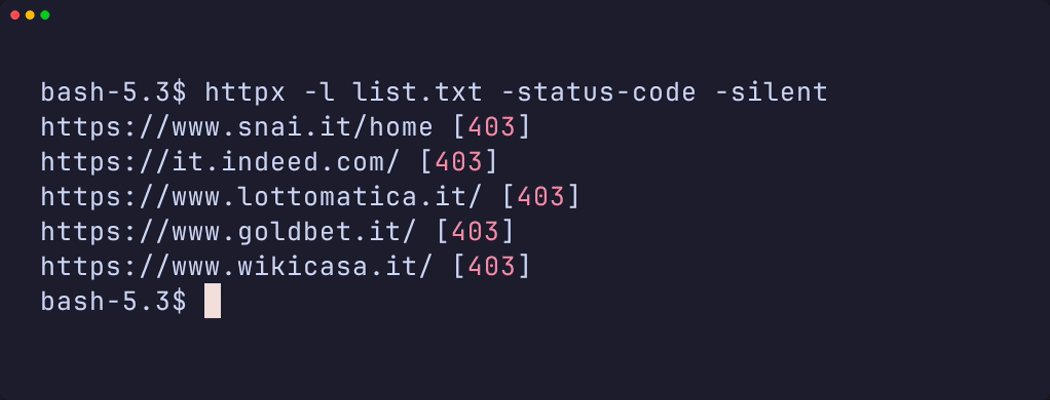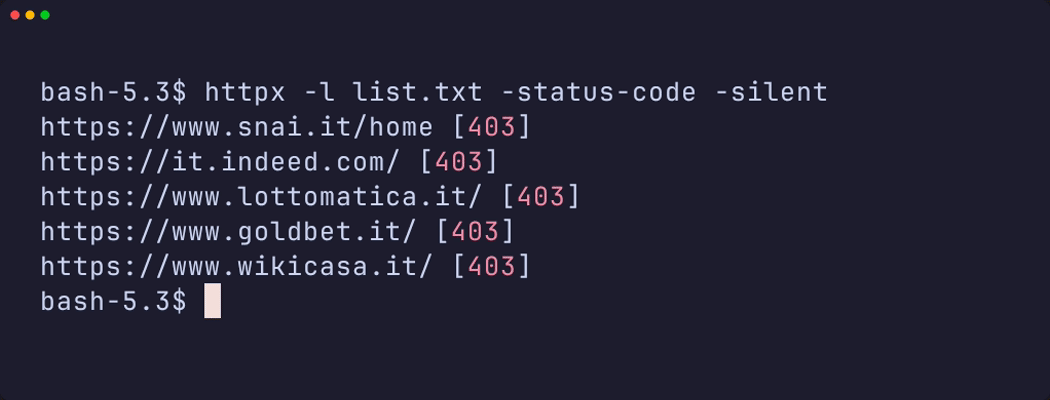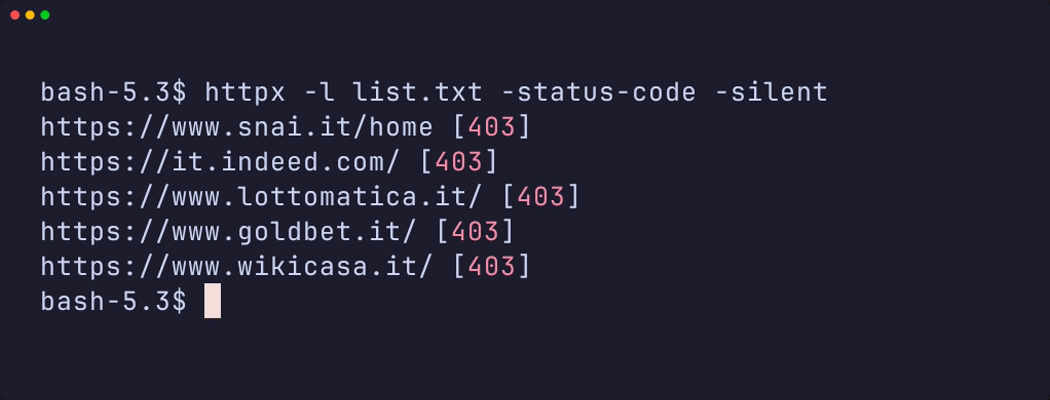 michele0303/undetected-httpx
Stop getting 403 Forbidden. A specialized httpx-like toolkit for WAF evasion.
 mcipekci/wp2shell
Pre-auth RCE PoC for WordPress core — chains CVE-2026-63030 (REST /batch/v1 route-confusion desync) with CVE-2026-60137 (author__not_in SQLi) into an…
 mohamedlahmeri01/vi-bot
Client-side bot detection library with 28 weighted modules, behavioral analysis, browser fingerprinting, honeypots, and server-side verification.…
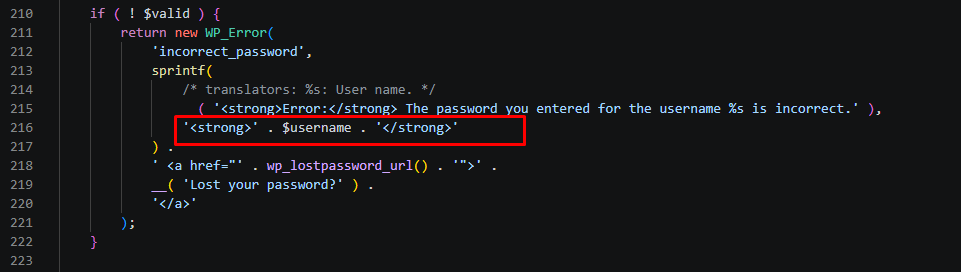 dungsocool/cve-2026-64638
Proof-of-concept exploit for CVE-2026-64638: reflected XSS in WordPress login chained with DOM clobbering to achieve admin account takeover and…
 si13nttt/cve-2026-22777
Proof-of-concept exploit chaining CRLF injection in ComfyUI-Manager's config endpoint with an arbitrary git install to achieve unauthenticated remote…
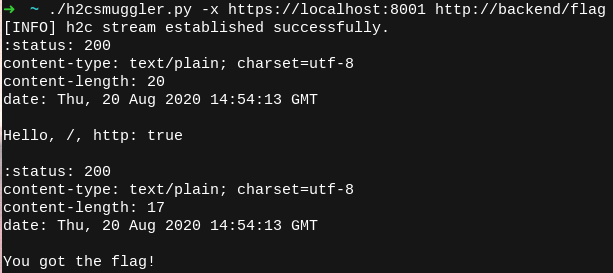 bishopfox/h2csmuggler
HTTP Request Smuggling over HTTP/2 Cleartext (h2c)