
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/rvrsh3ll/azure-app-tools
Phishing ToolsWeb SecurityCloud SecurityCommand and ControlAuthenticationRed TeamingPayload Development
GitHubrvrsh3ll/azure-app-tools

Azure-App-Tools

Collection of tools to use with Azure Applications

View Repository
11317513 years agoReviewed by Kitploit
Share

Azure-App-Tools

Collection of tools to use with Azure Applications. https://azure.microsoft.com/en-us/get-started/apps/

Prerequisites

Azure Powershell Module https://docs.microsoft.com/en-us/powershell/azure/install-az-ps?view=azps-3.8.0

Examples:

Dynamic Device Codes

Original PoC by @MrUn1k0d3r https://gist.github.com/Mr-Un1k0d3r/afef5a80cb72dfeaa78d14465fb0d333.

Dynamically generate device codes on an Azure website. Typically, we have to email a user and the device code has 900 seconds to expire from time of sending the email. By directing the user to a dynamic site, we extend the time we have to recieve tokens based on when the user visits the website and until they sign-in.

Uses FLUX Web3 by defult for CORS-Anywhere so, IP address for sign-in may vary. You may use other services such as Heroku Apps to host Cors-Anywhere. https://github.com/Rob--W/cors-anywhere

az webapp up --location eastus --resource-group mynewresourcegroup --name mynewsubdomain --html --sku FREE

alt text

Static HTML Phishing Page

az webapp up --location eastus --resource-group mynewresourcegroup --name mynewsubdomain --html --sku FREE

Azure IPFS Dropper

Setup Instructions

IIS Redirector

az webapp up --location eastus --resource-group mynewresourcegroup --name mynewsubdomain --html --sku FREE

Navigate to the Azure App Console and copy the applicationHost.xdt back a directory.
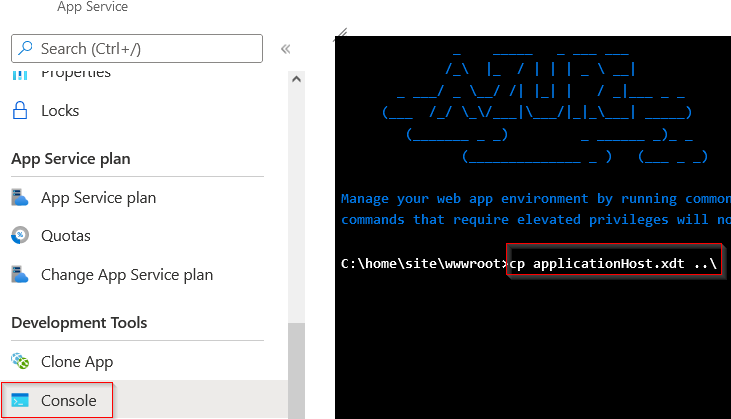
alt text

Python Flask Redirector

The redirector acts as a "dumb" redirector unless you modify the variables in application.py. See below.

Protect your servers with a secret header per my blog at https://medium.com/@rvrsh3ll/hardening-your-azure-domain-front-7423b5ab4f64

Be sure to comment the first HEADER variable and then uncomment HEADER and HEADER_KEY to use magic headers in application.py. HEADER = None #HEADER = "X-Aspnet-Version" #HEADER_KEY = "1.5"

az webapp up --location eastus --resource-group mynewresourcegroup --name mynewsubdomain --SKU FREE


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    500
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    466
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    339
  • 4

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    317
  • 5

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    307
  • 6

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    294

Explore all tools

Browse our collection of tools

View all tools →




