
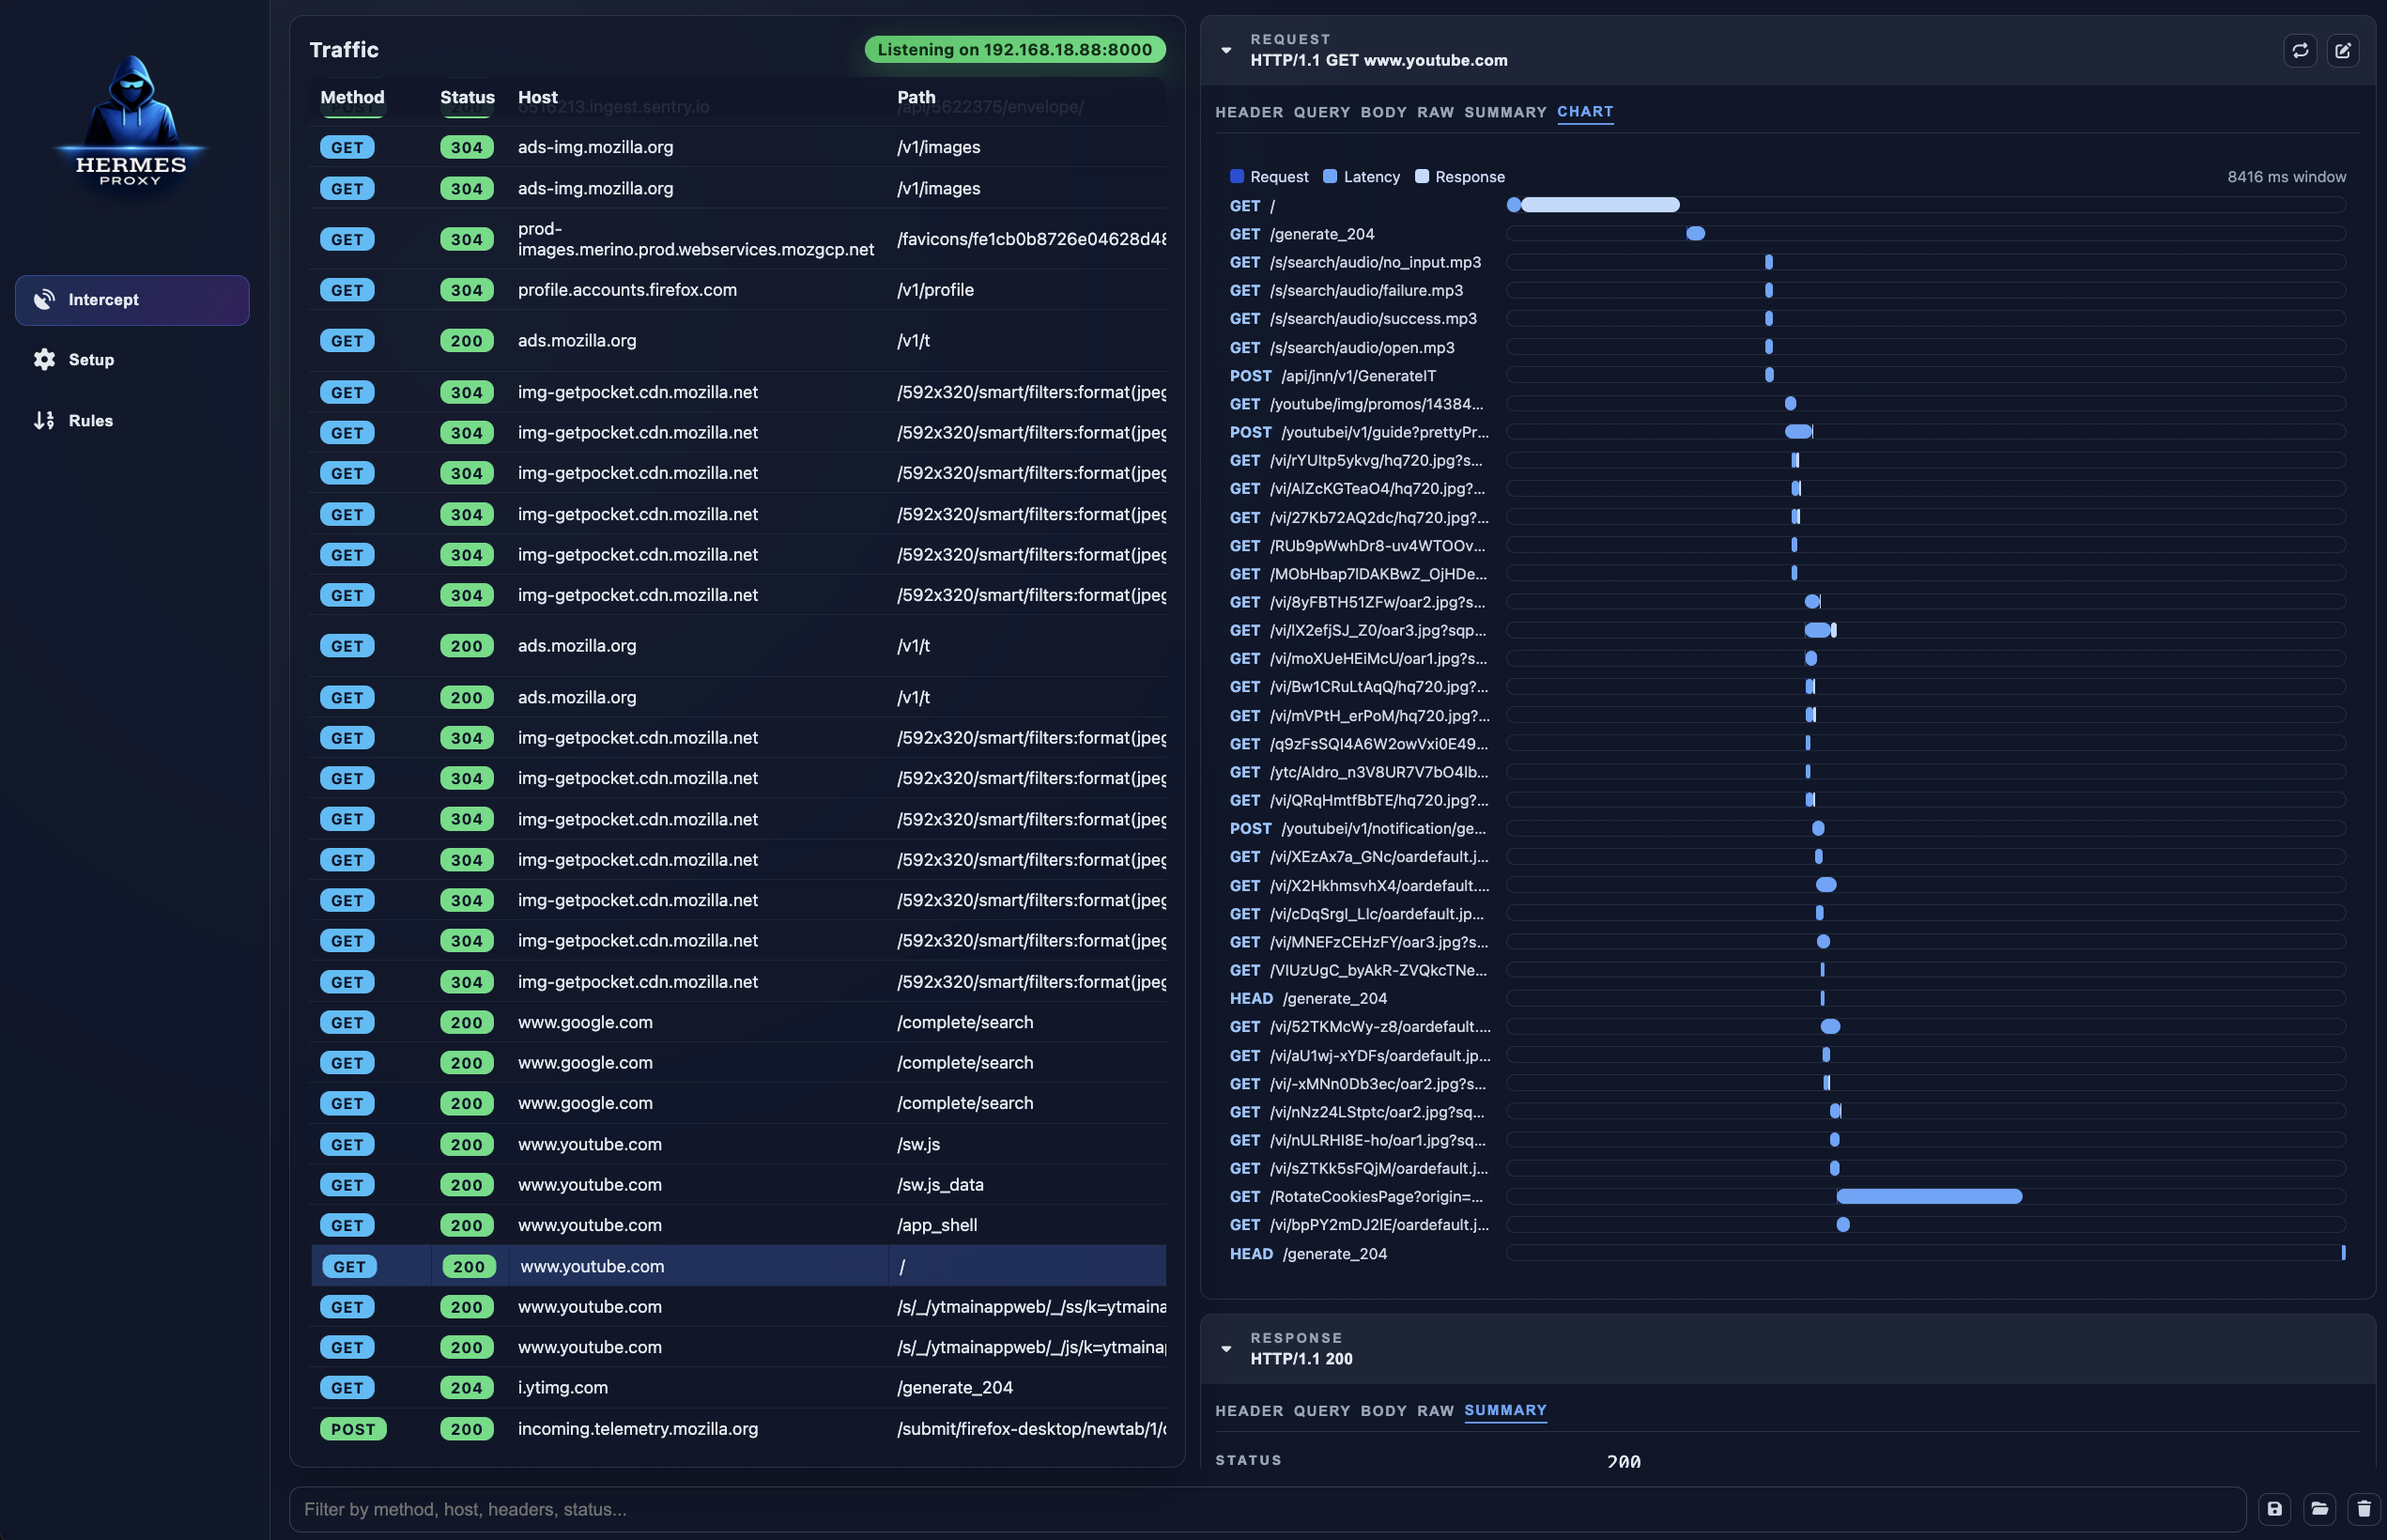
Hermes-Proxy
 jp/hermes-proxy
Hermes Proxy - HTTP Traffic Analyzer
api-security-testingdebuggersdynamic-analysis-sandboxing+3
jp/hermes-proxyHermes Proxy - HTTP Traffic Analyzer
 nccgroup/wcfdser-ngng
A Burp Extender plugin, that will make binary soap objects readable and modifiable.
 emo-crab/slinger
An HTTP client specifically developed for security researchers
 projectdiscovery/collaborator
BurpSuite Standard/Private Collaborator Library
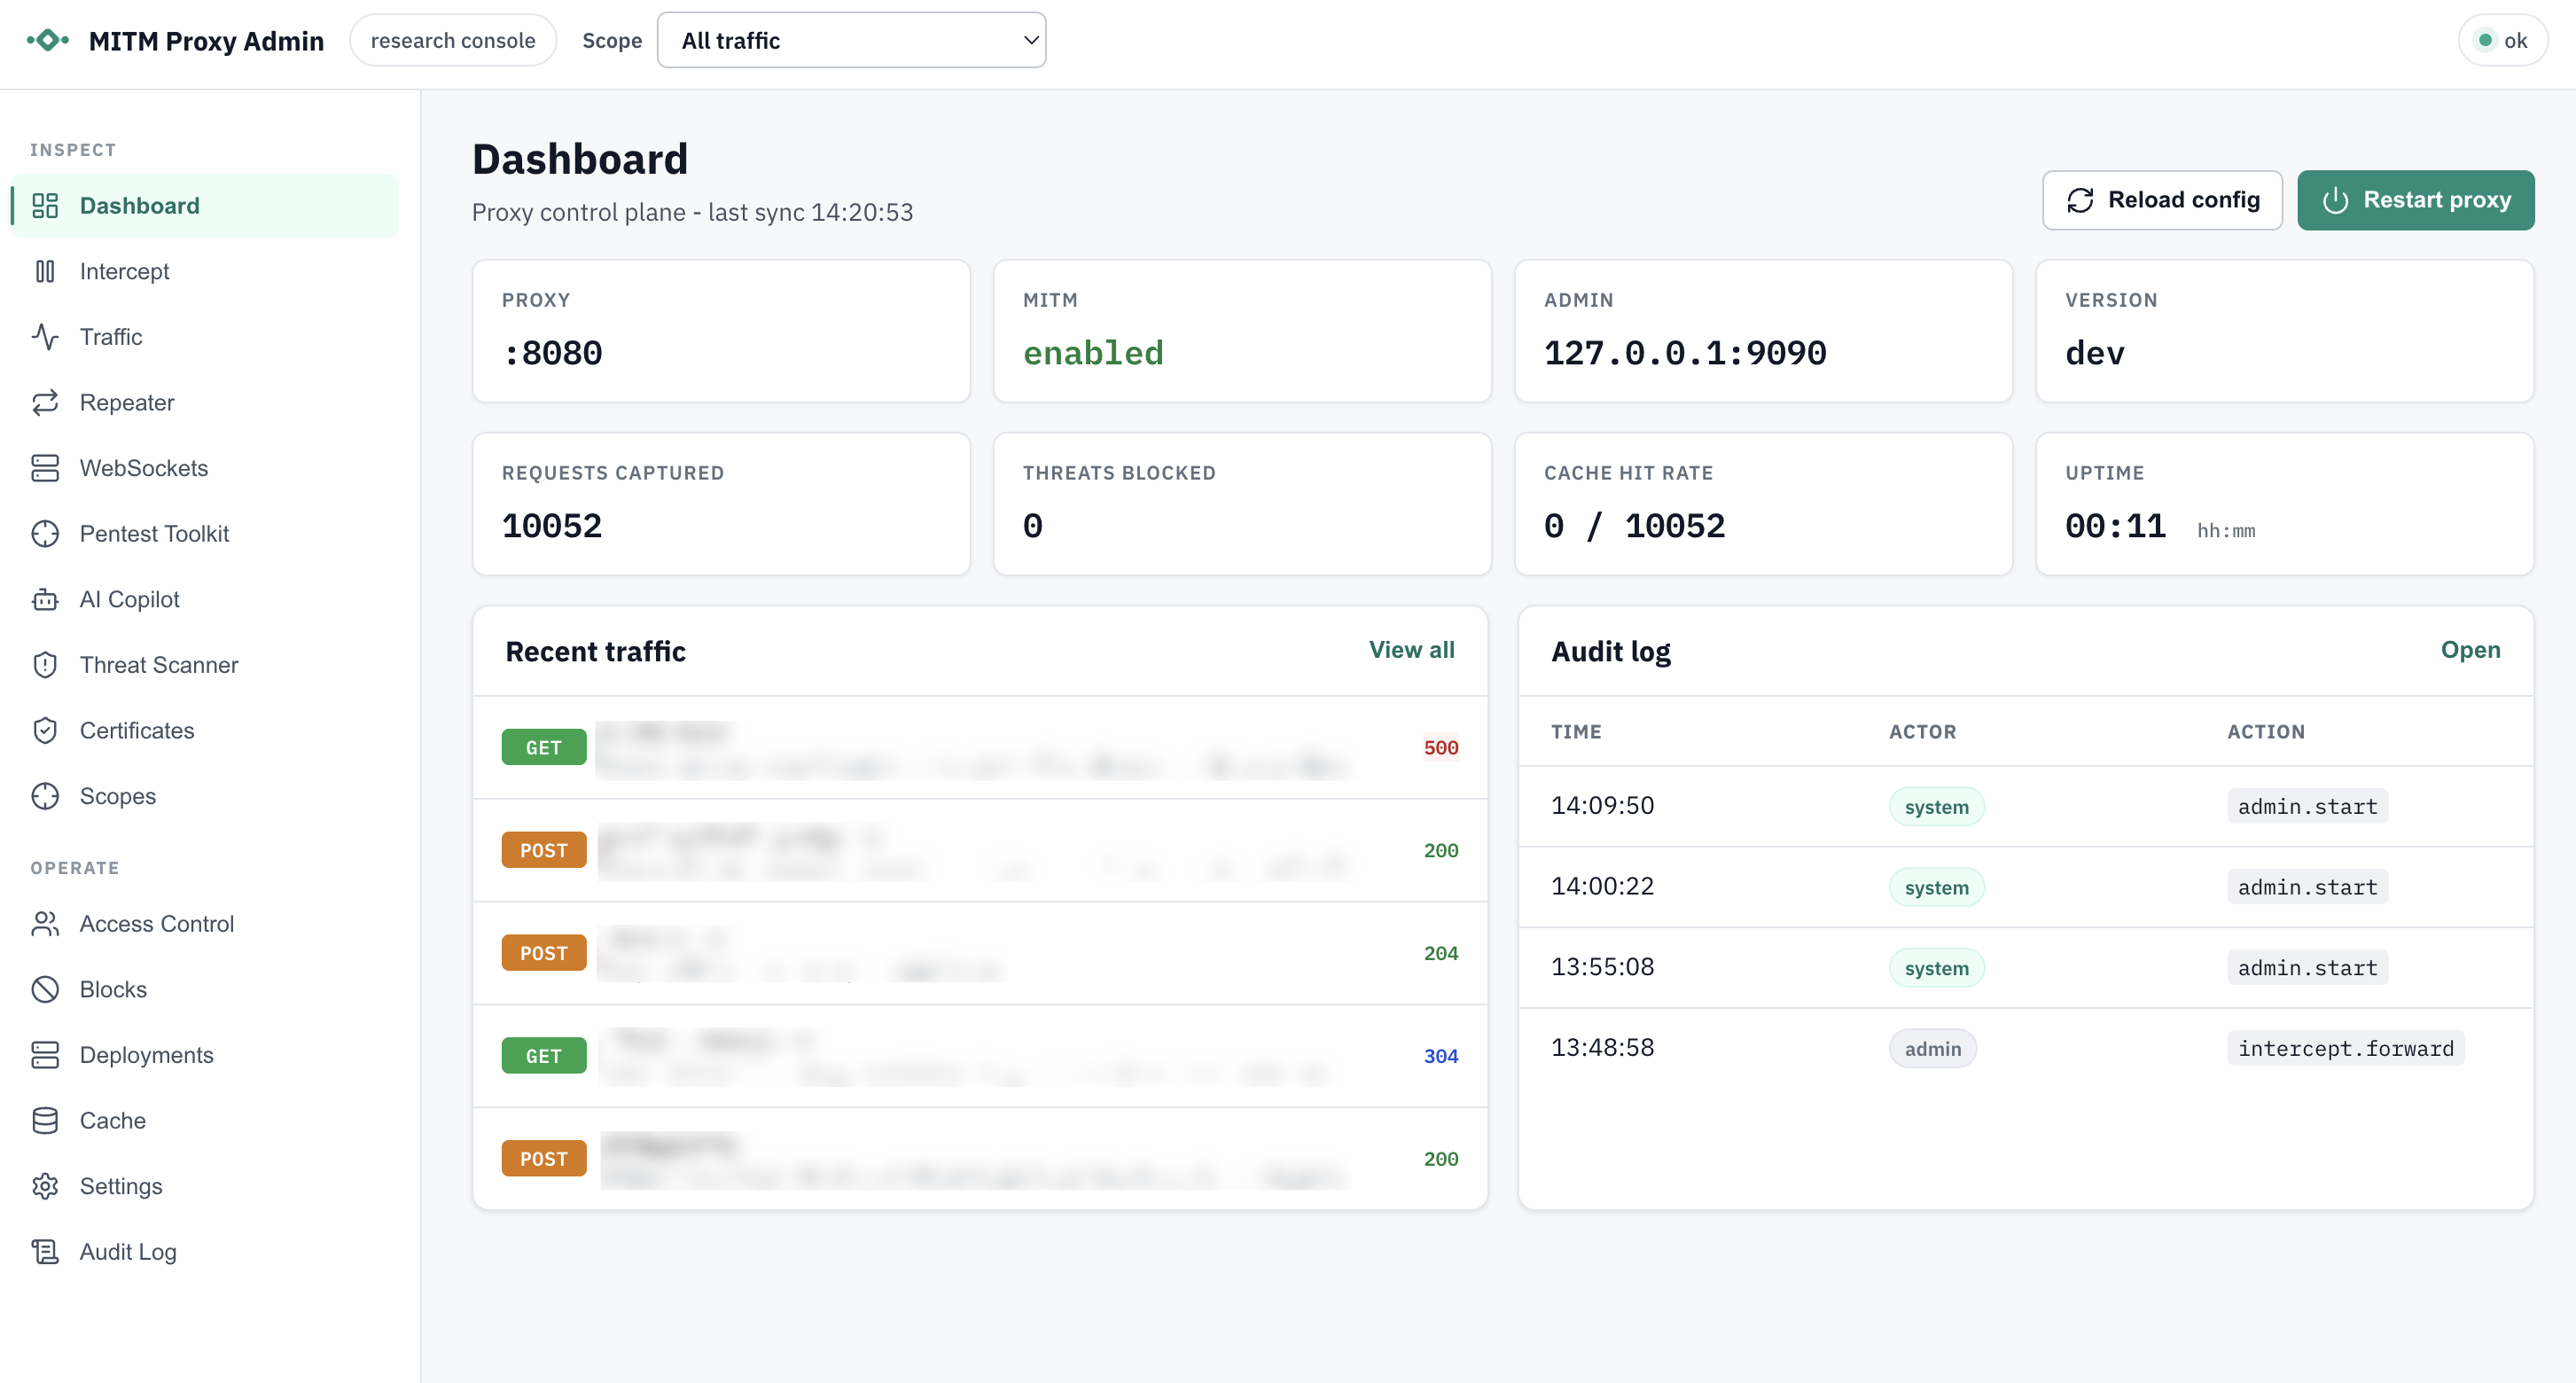 welfordian/mitm-proxy
Go-based MITM HTTP/HTTPS proxy with HTTP/2 and HTTP/1.1 interception, local CA/per-host cert generation, CONNECT/WebSocket tunneling, disk caching,…
 ericmtzmtz/pwnproxy
An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.
 larrypeseckis/burp-cc-bridge
REST API automation for Burp Suite Community Edition. Drop-in Java extension exposing send/repeat/history endpoints over a local HTTP API.
 torxx666/propox
High-performance Rust HTTP/HTTPS proxy with active defense: rate limiting, reputation-based access, WAF (anti-bot, anti-injection, path protection),…
 d0rb/packetpirate
A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
 vid4l-07/roxy
Terminal-based HTTP intercepting proxy with TUI for capturing, inspecting, and modifying requests in real time, plus a Repeater for resending and…
 h2non/toxy
Hackable HTTP proxy for resiliency testing and simulated network conditions
 p0cl4bs/wifi-pumpkin-deprecated
DEPRECATED, wifipumpkin3 -> https://github.com/P0cL4bs/wifipumpkin3
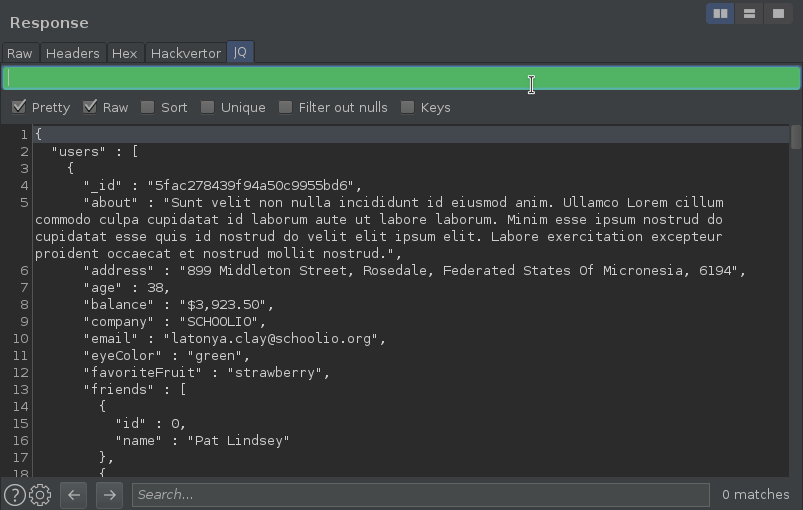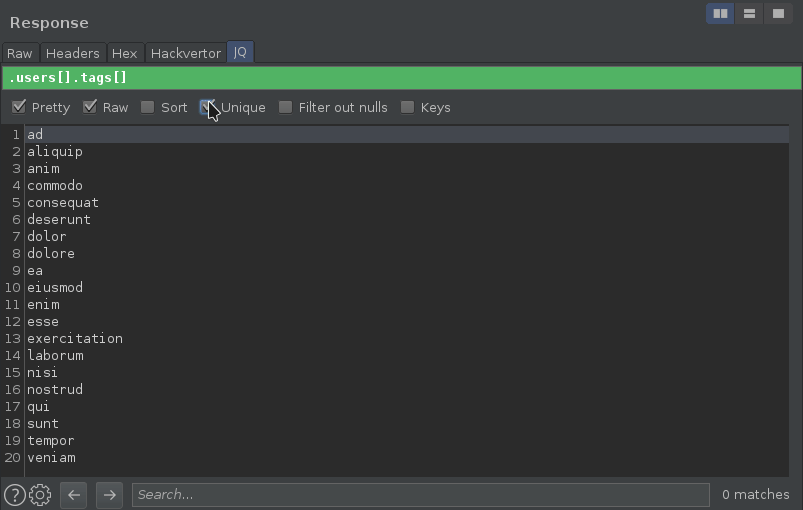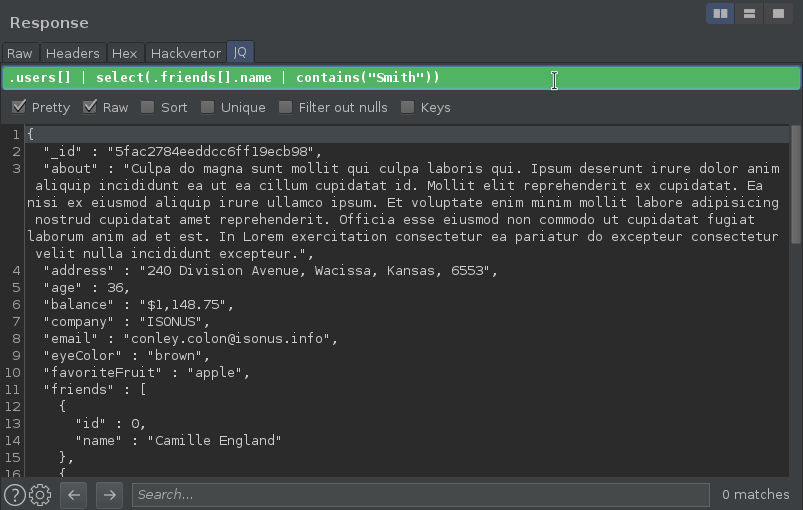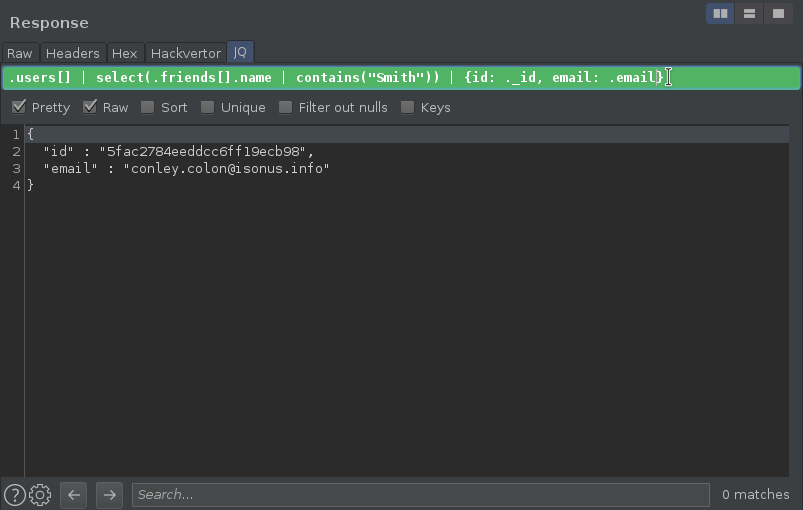 synacktiv/burp-jq
Burp extension to filter JSON on the fly with JQ queries in the HTTP message viewer.
 t3l3machus/pentest-pivoting
A compact guide to network pivoting for penetration testings / CTF challenges.
 p0cl4bs/wifipumpkin3
Powerful framework for rogue access point attack.
 drk1wi/modlishka
Modlishka. Reverse Proxy.
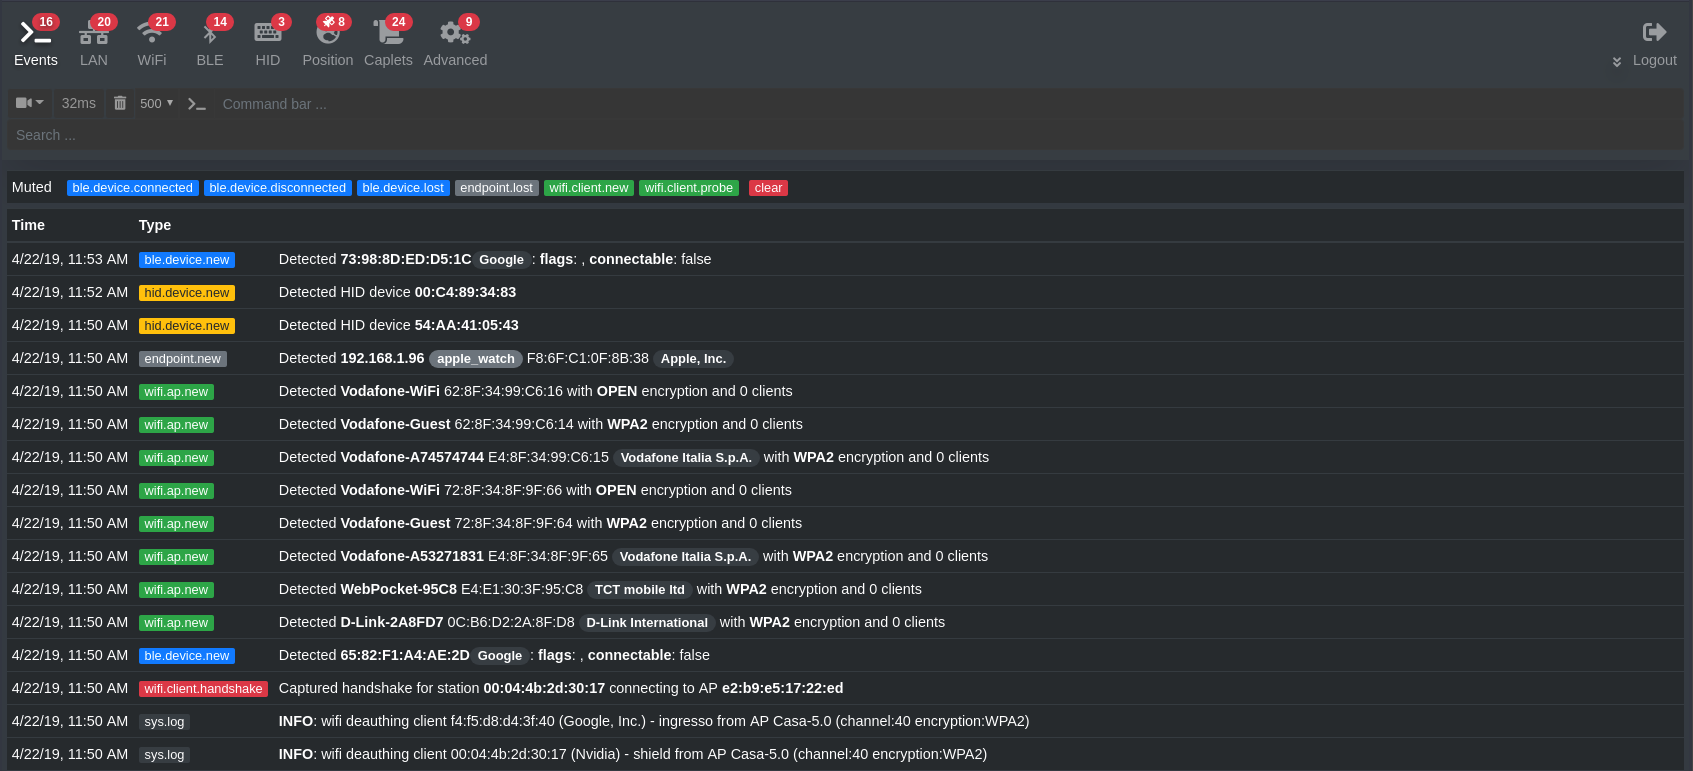 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 nccgroup/blackboxprotobuf
Blackbox Protobuf is a set of tools for working with encoded Protocol Buffers (protobuf) without the matching protobuf definition.