
HUNT
 bugcrowd/hunt
Flags parameters commonly associated with injection, SSRF, path traversal, IDOR, and SSTI, via passive Burp/ZAP scanning; also organizes manual…
curated-resourcespenetration-testingvulnerability-analysis+3
2.3k
bugcrowd/huntFlags parameters commonly associated with injection, SSRF, path traversal, IDOR, and SSTI, via passive Burp/ZAP scanning; also organizes manual…
 vmoranv/jshookmcp
A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.
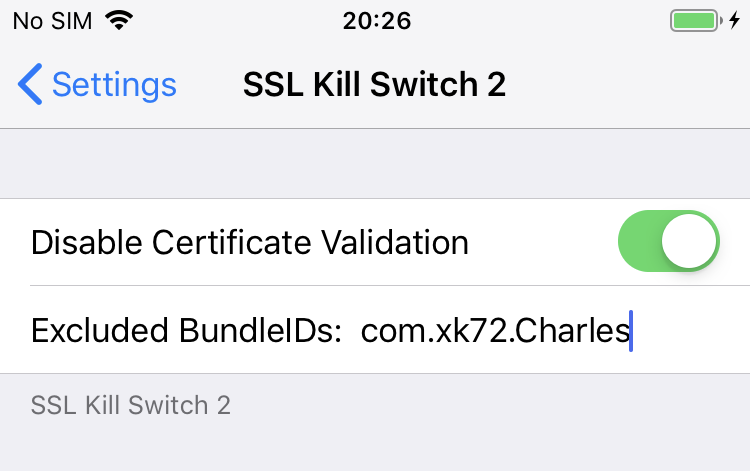 nabla-c0d3/ssl-kill-switch2
Blackbox tool to disable SSL certificate validation - including certificate pinning - within iOS and macOS applications.
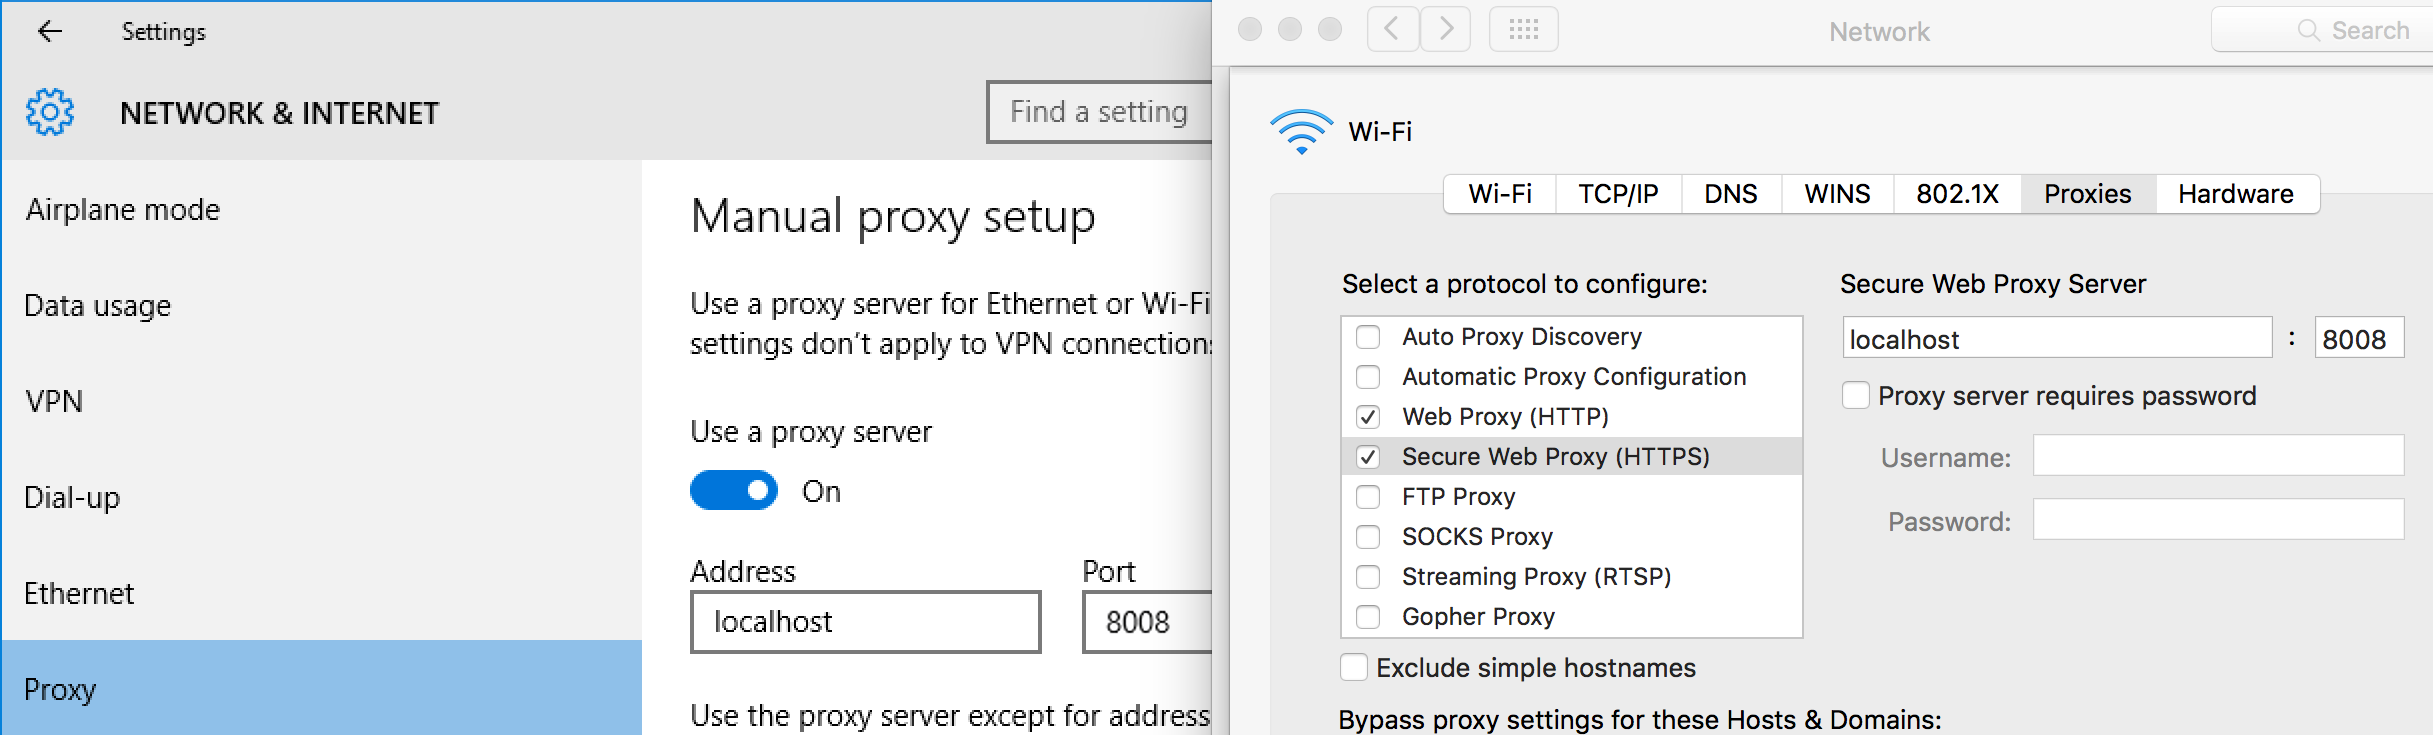 kdzwinel/betwixt
:zap: Web Debugging Proxy based on Chrome DevTools Network panel.
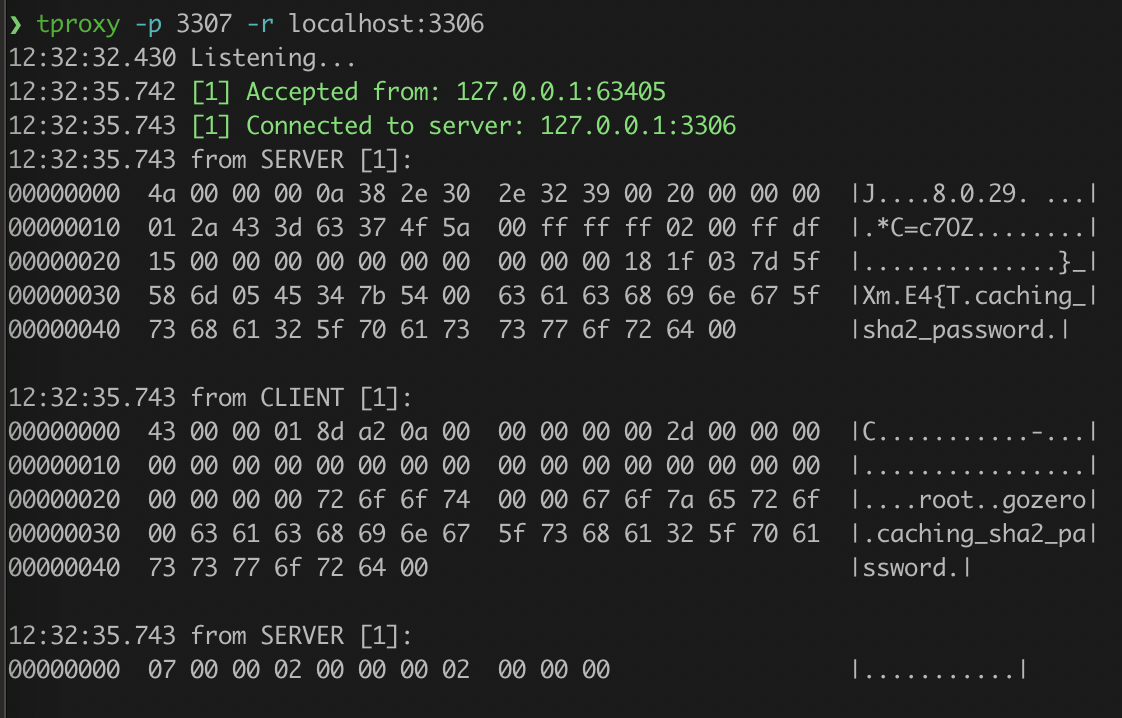 kevwan/tproxy
A cli tool to proxy and analyze TCP connections.
 p0cl4bs/wifipumpkin3
Powerful framework for rogue access point attack.
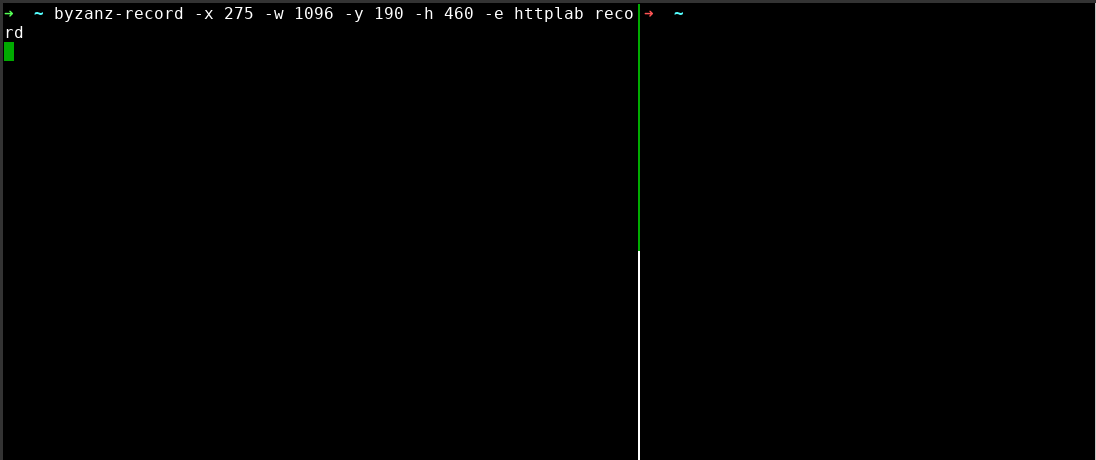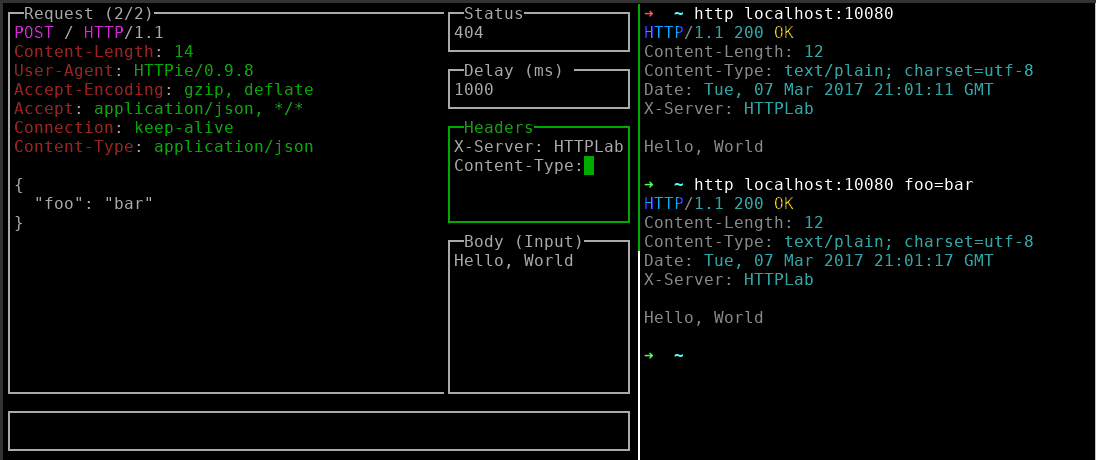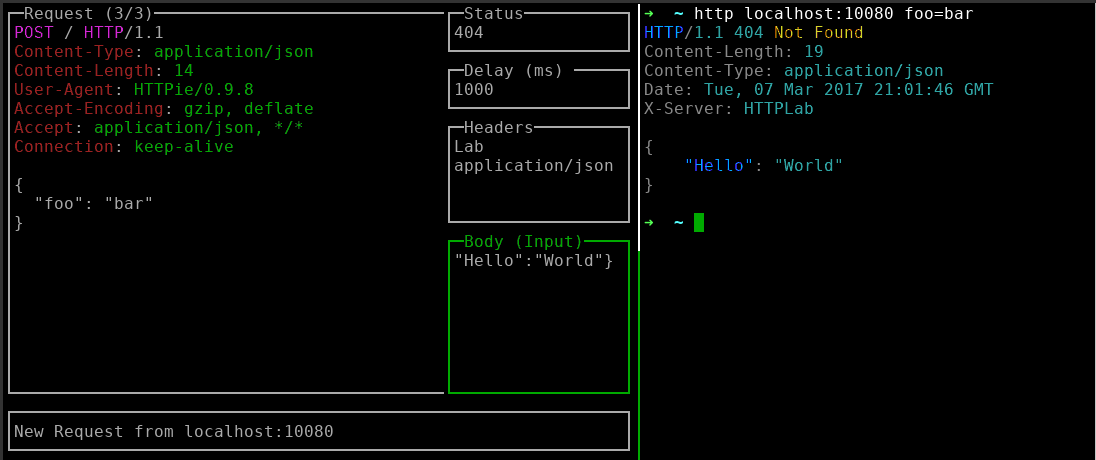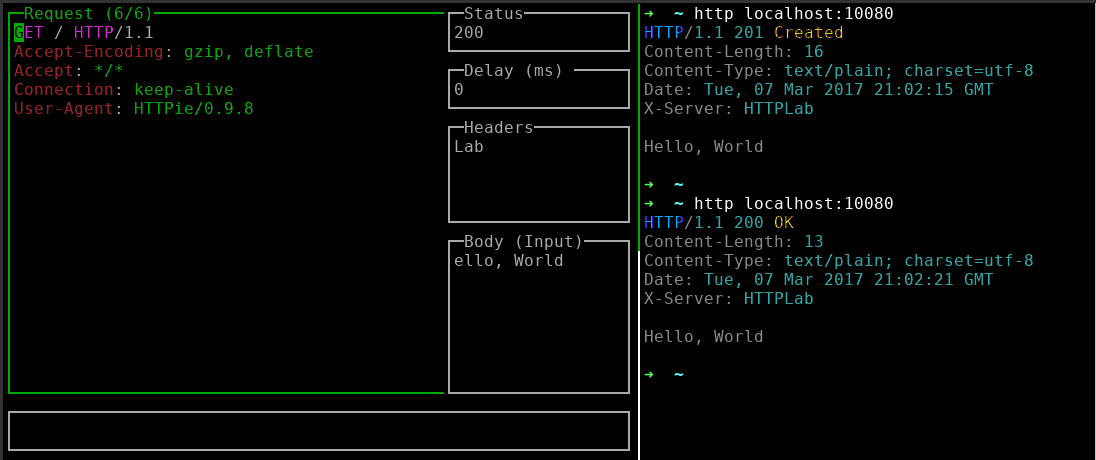 qustavo/httplab
Interactive web server for inspecting HTTP requests and forging responses, with a terminal UI for real-time debugging and API testing.
 federicodotta/brida
The new bridge between Burp Suite and Frida!
 portswigger/bambdas
Bambdas collection for Burp Suite Professional and Community.
 infobyte/evilgrade
Evilgrade is a modular framework that allows the user to take advantage of poor upgrade implementations by injecting fake updates.
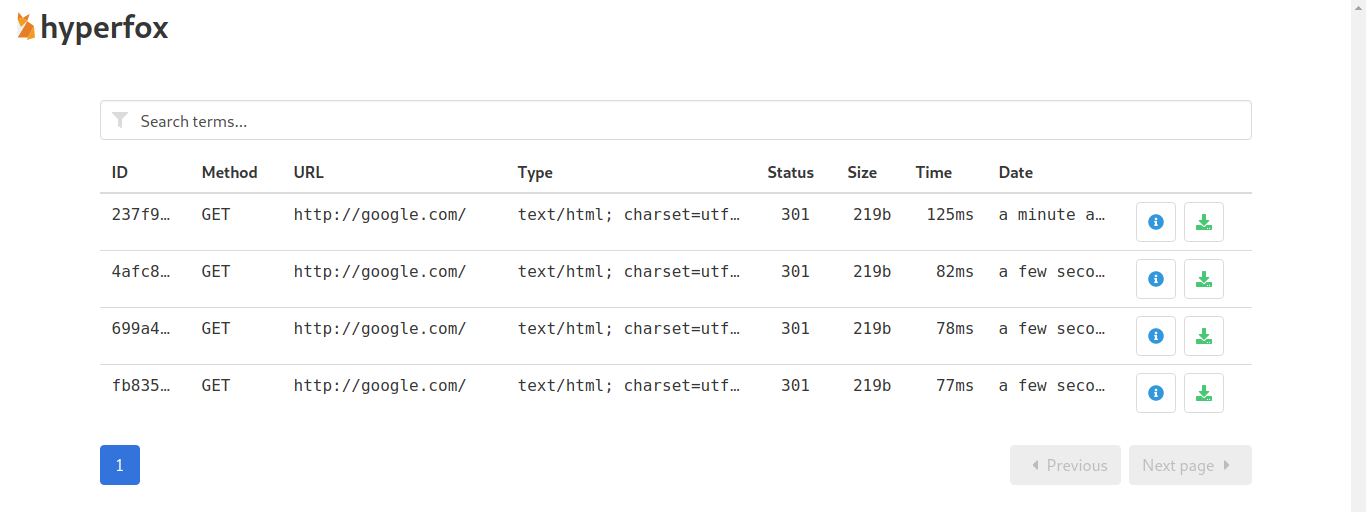 malfunkt/hyperfox
HTTP/HTTPS MITM proxy and recorder.
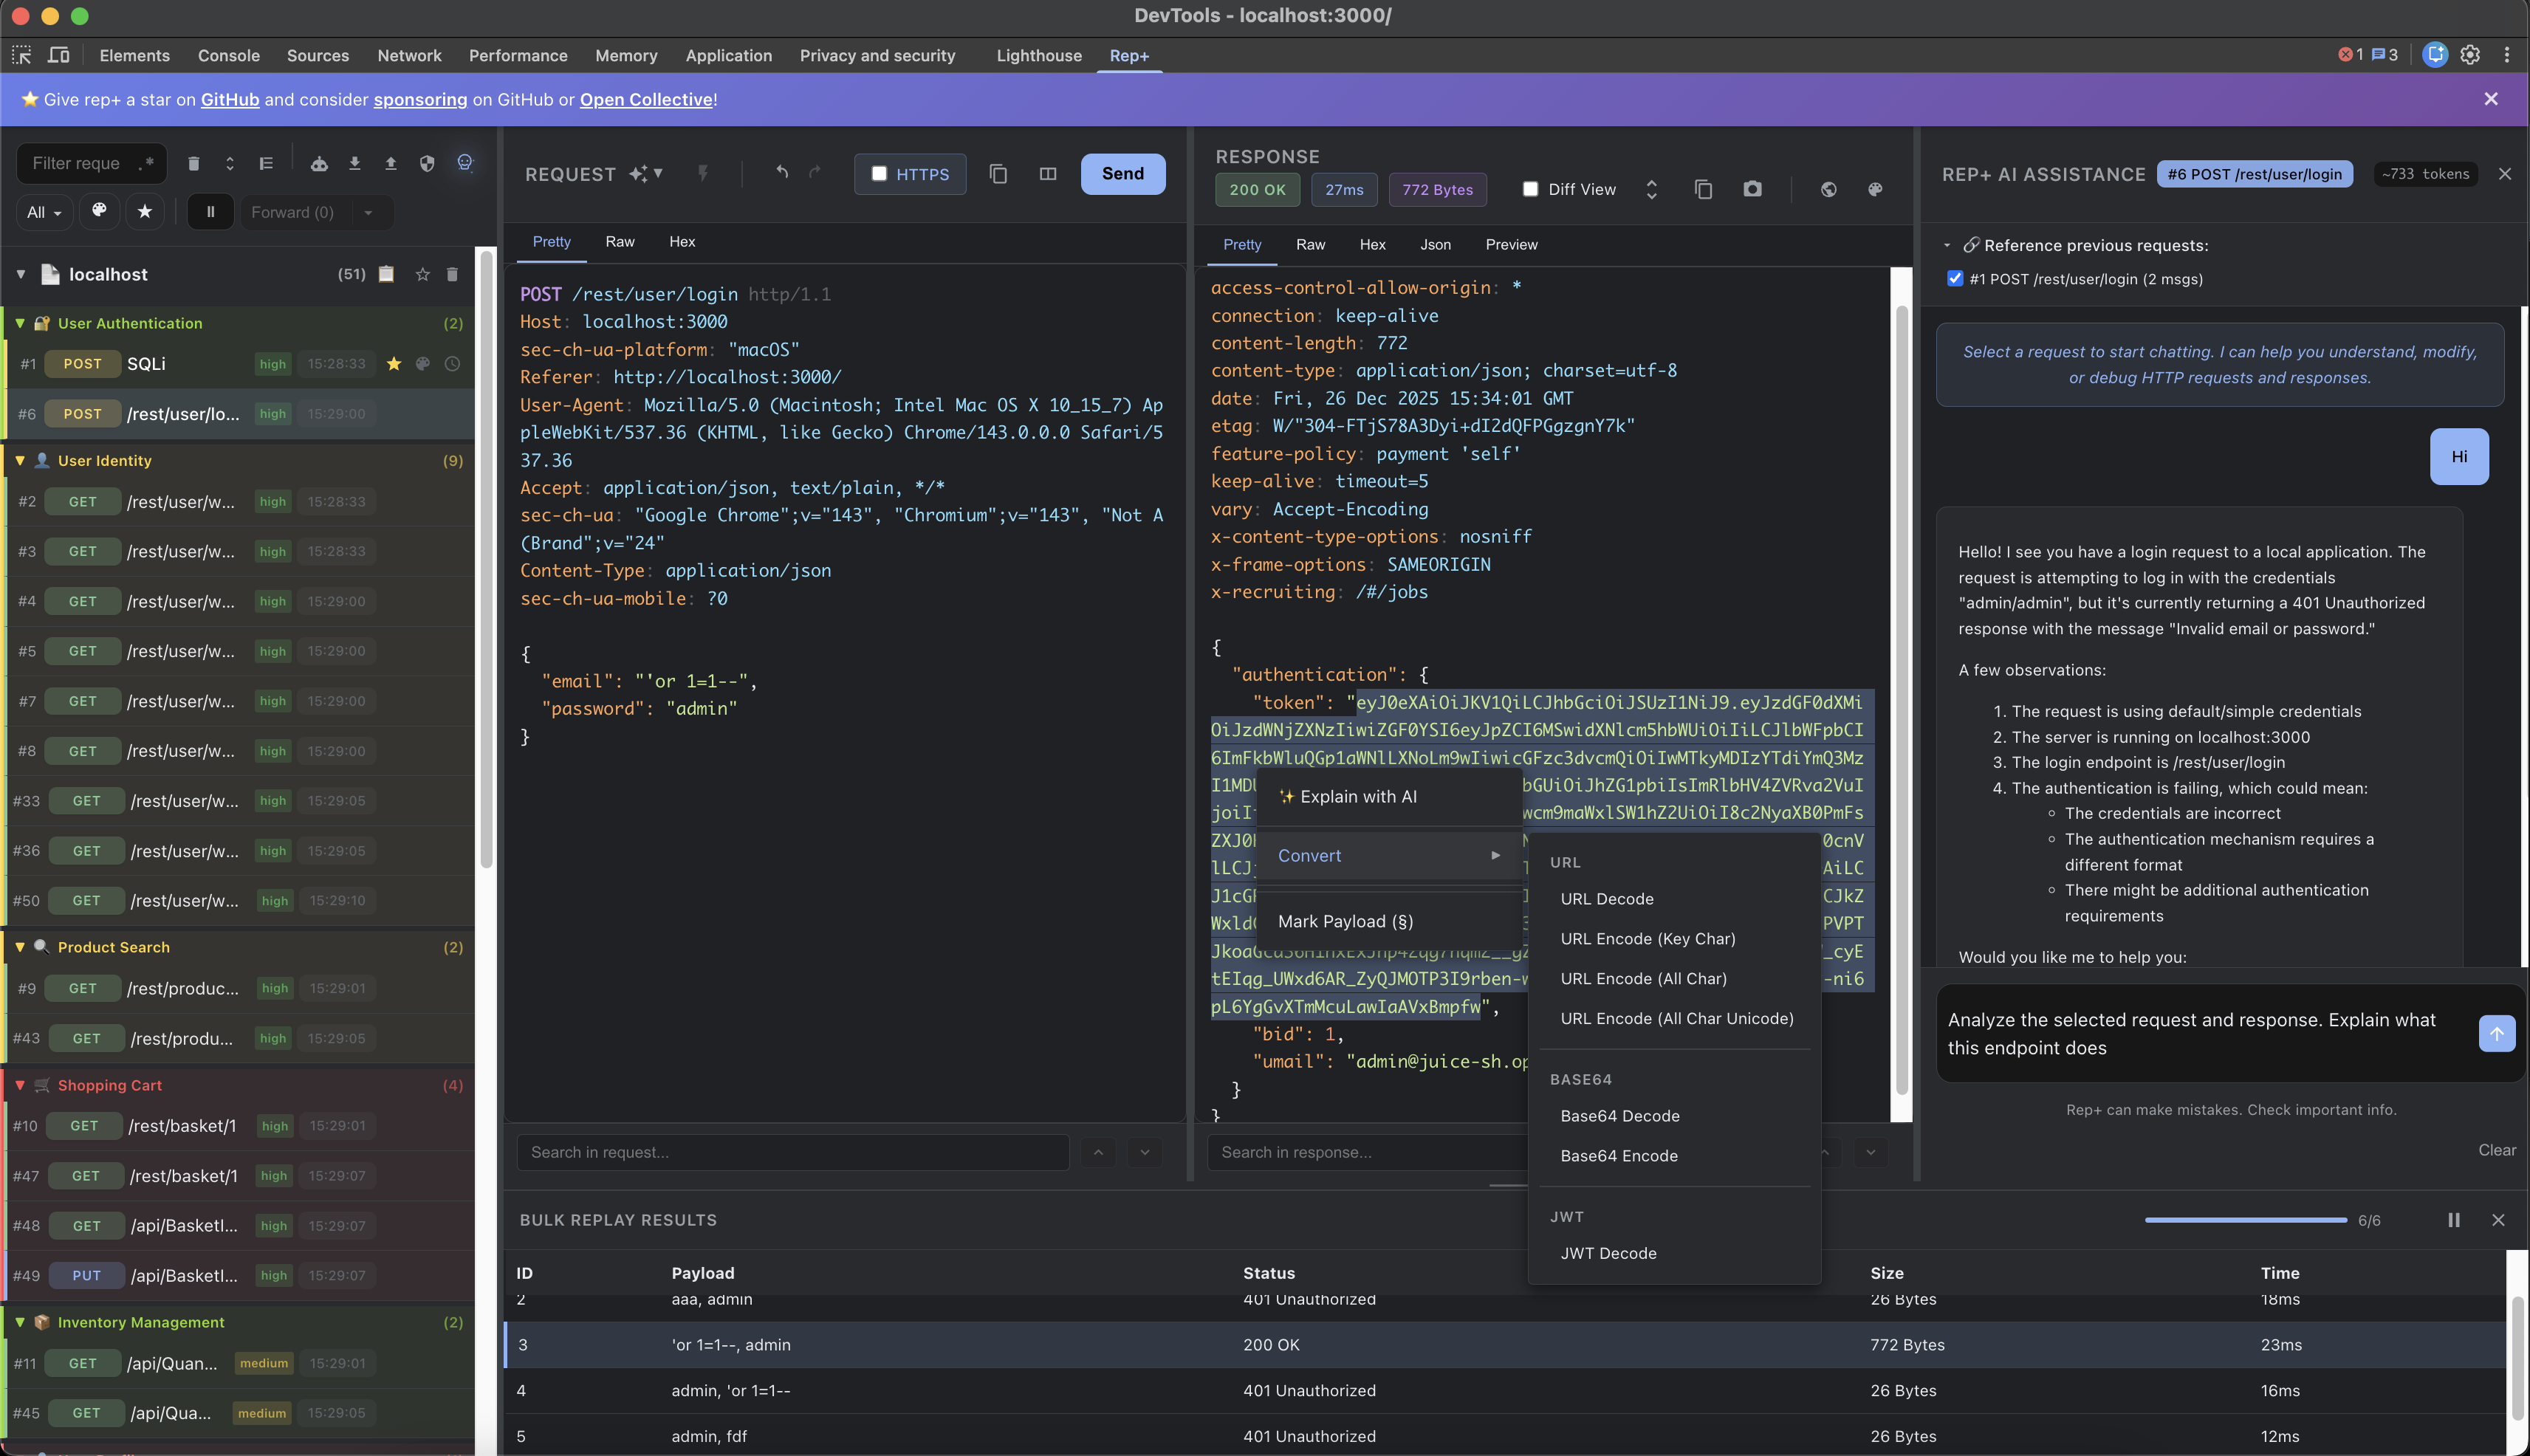 repplus/rep-chrome
rep+ — Burp-style HTTP Repeater for Chrome DevTools with built‑in AI to explain requests and suggest attacks
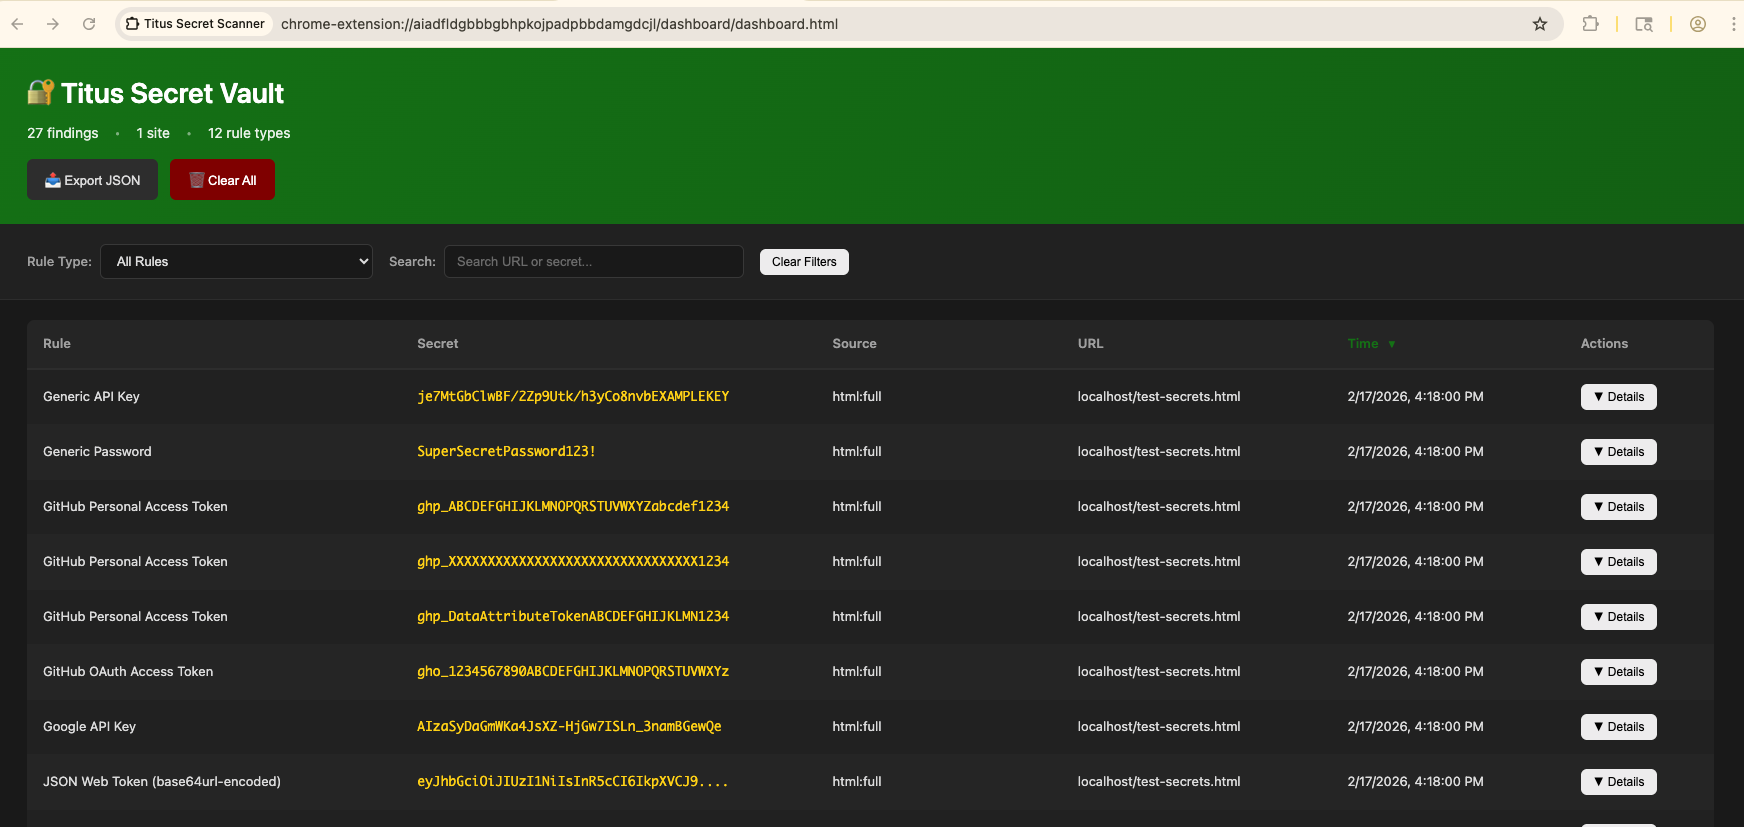 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
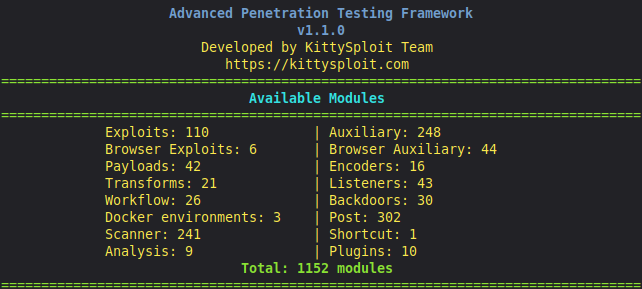 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
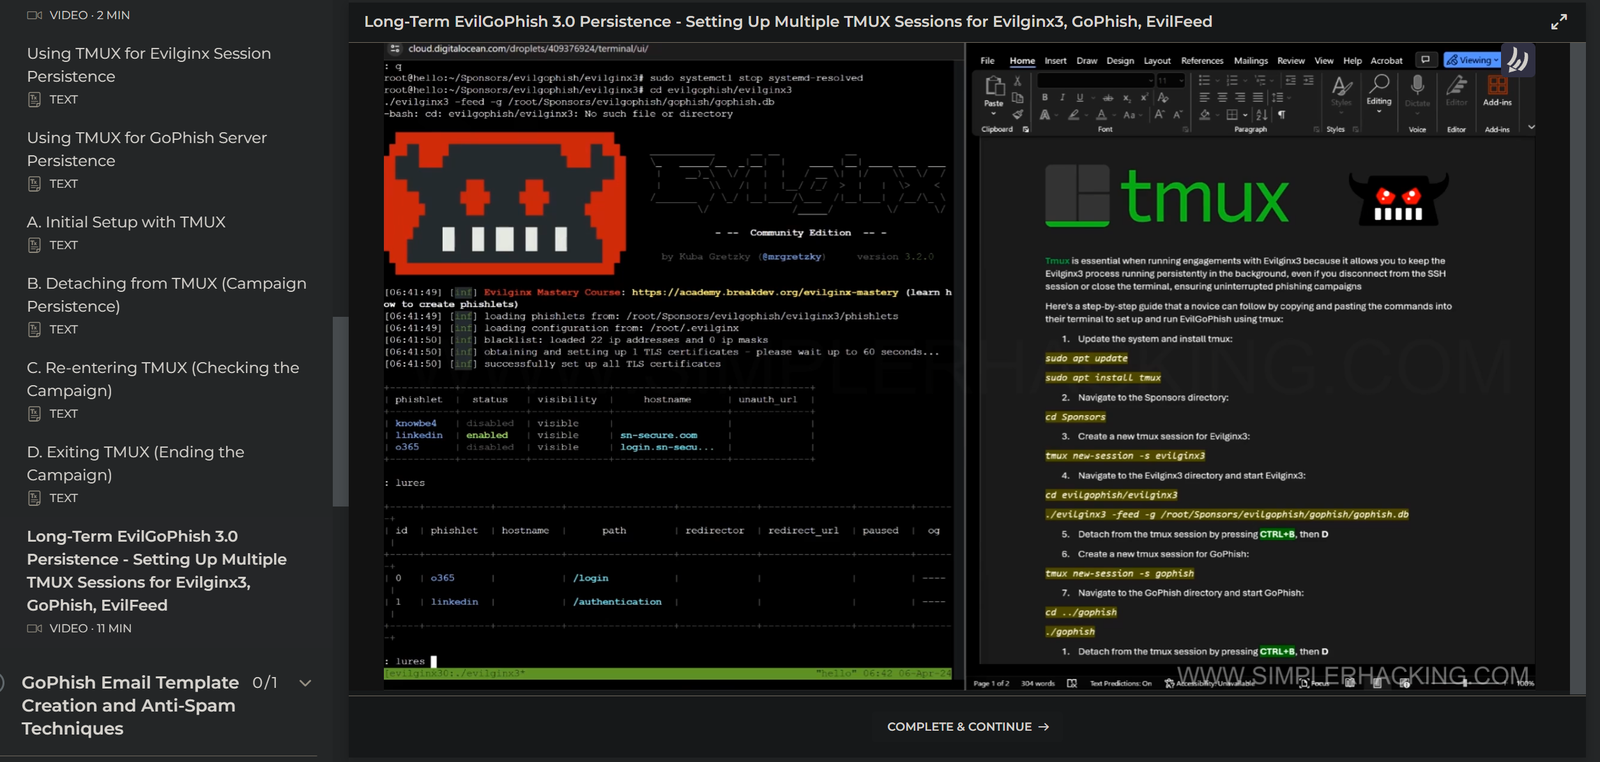 simplerhacking/evilginx3-phishlets
This repository provides penetration testers and red teams with an extensive collection of dynamic phishing templates designed specifically for use…
 muraenateam/muraena
Automates phishing and post-phishing activities with an almost-transparent reverse proxy that dynamically mirrors target web apps and interacts with…
 secretsquirrel/bdfproxy
Patch Binaries via MITM: BackdoorFactory + mitmProxy.
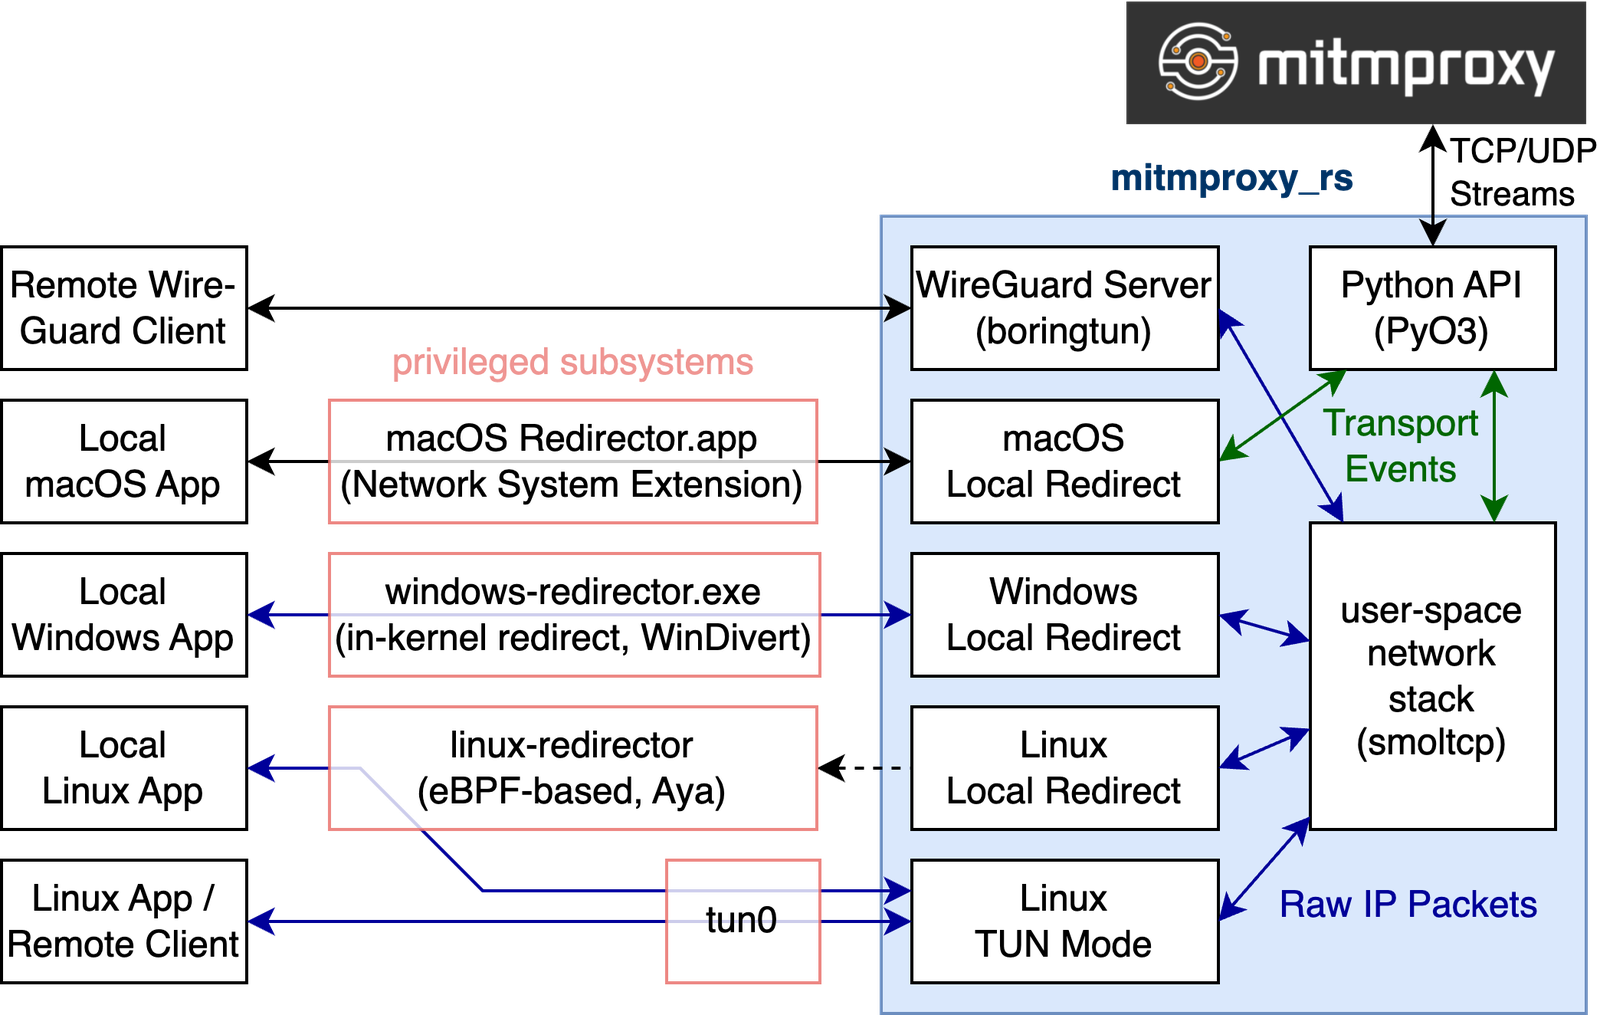 mitmproxy/mitmproxy_rs
Rust components for traffic interception and redirection, enabling WireGuard device proxying and local app redirection across macOS, Windows, and…