reDOM
A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy…

A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy…

An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.

Response Overview Extension for BurpSuite - Find exotic responses by grouping response bodies

Terminal-based HTTP intercepting proxy with TUI for capturing, inspecting, and modifying requests in real time, plus a Repeater for resending and…

Content-blind reverse proxy for exposure-protected security scanning

Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…

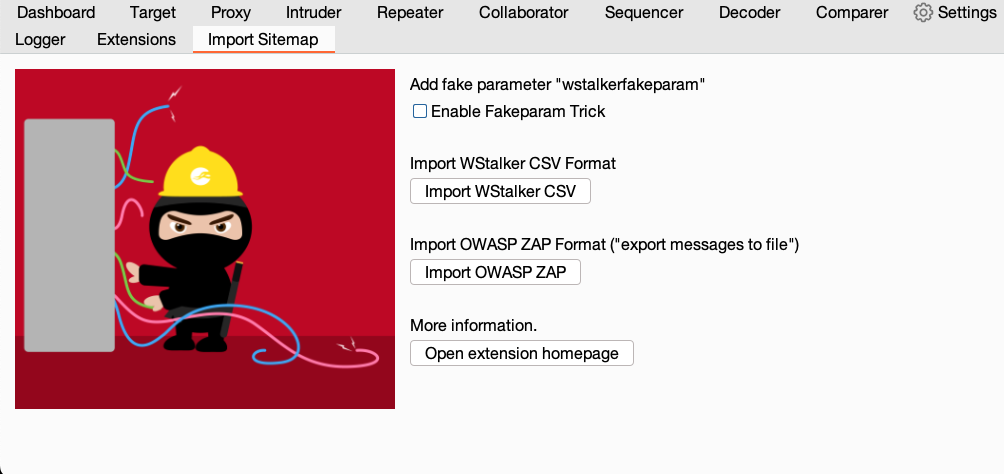
Import To Sitemap is a Burp Suite Extension to import wstalker CSV file or ZAP export file into Burp Sitemap

A Swiss Army knife for offensive security.

A proxy for net.tcp-based WCF traffic.

User-space bot and DDoS deflection for small HTTP services

Zap Extension for collaboration in Faraday

A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.

REST/JSON API to the Burp Suite security tool.

Hackable HTTP proxy for resiliency testing and simulated network conditions

Martian is a library for building custom HTTP/S proxies

Fast, AI-first web security testing toolkit in Rust: an open-source alternative to ZAP, Burp Suite and the like. Intercepting proxy, scanner, fuzzer…

LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…

evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).