
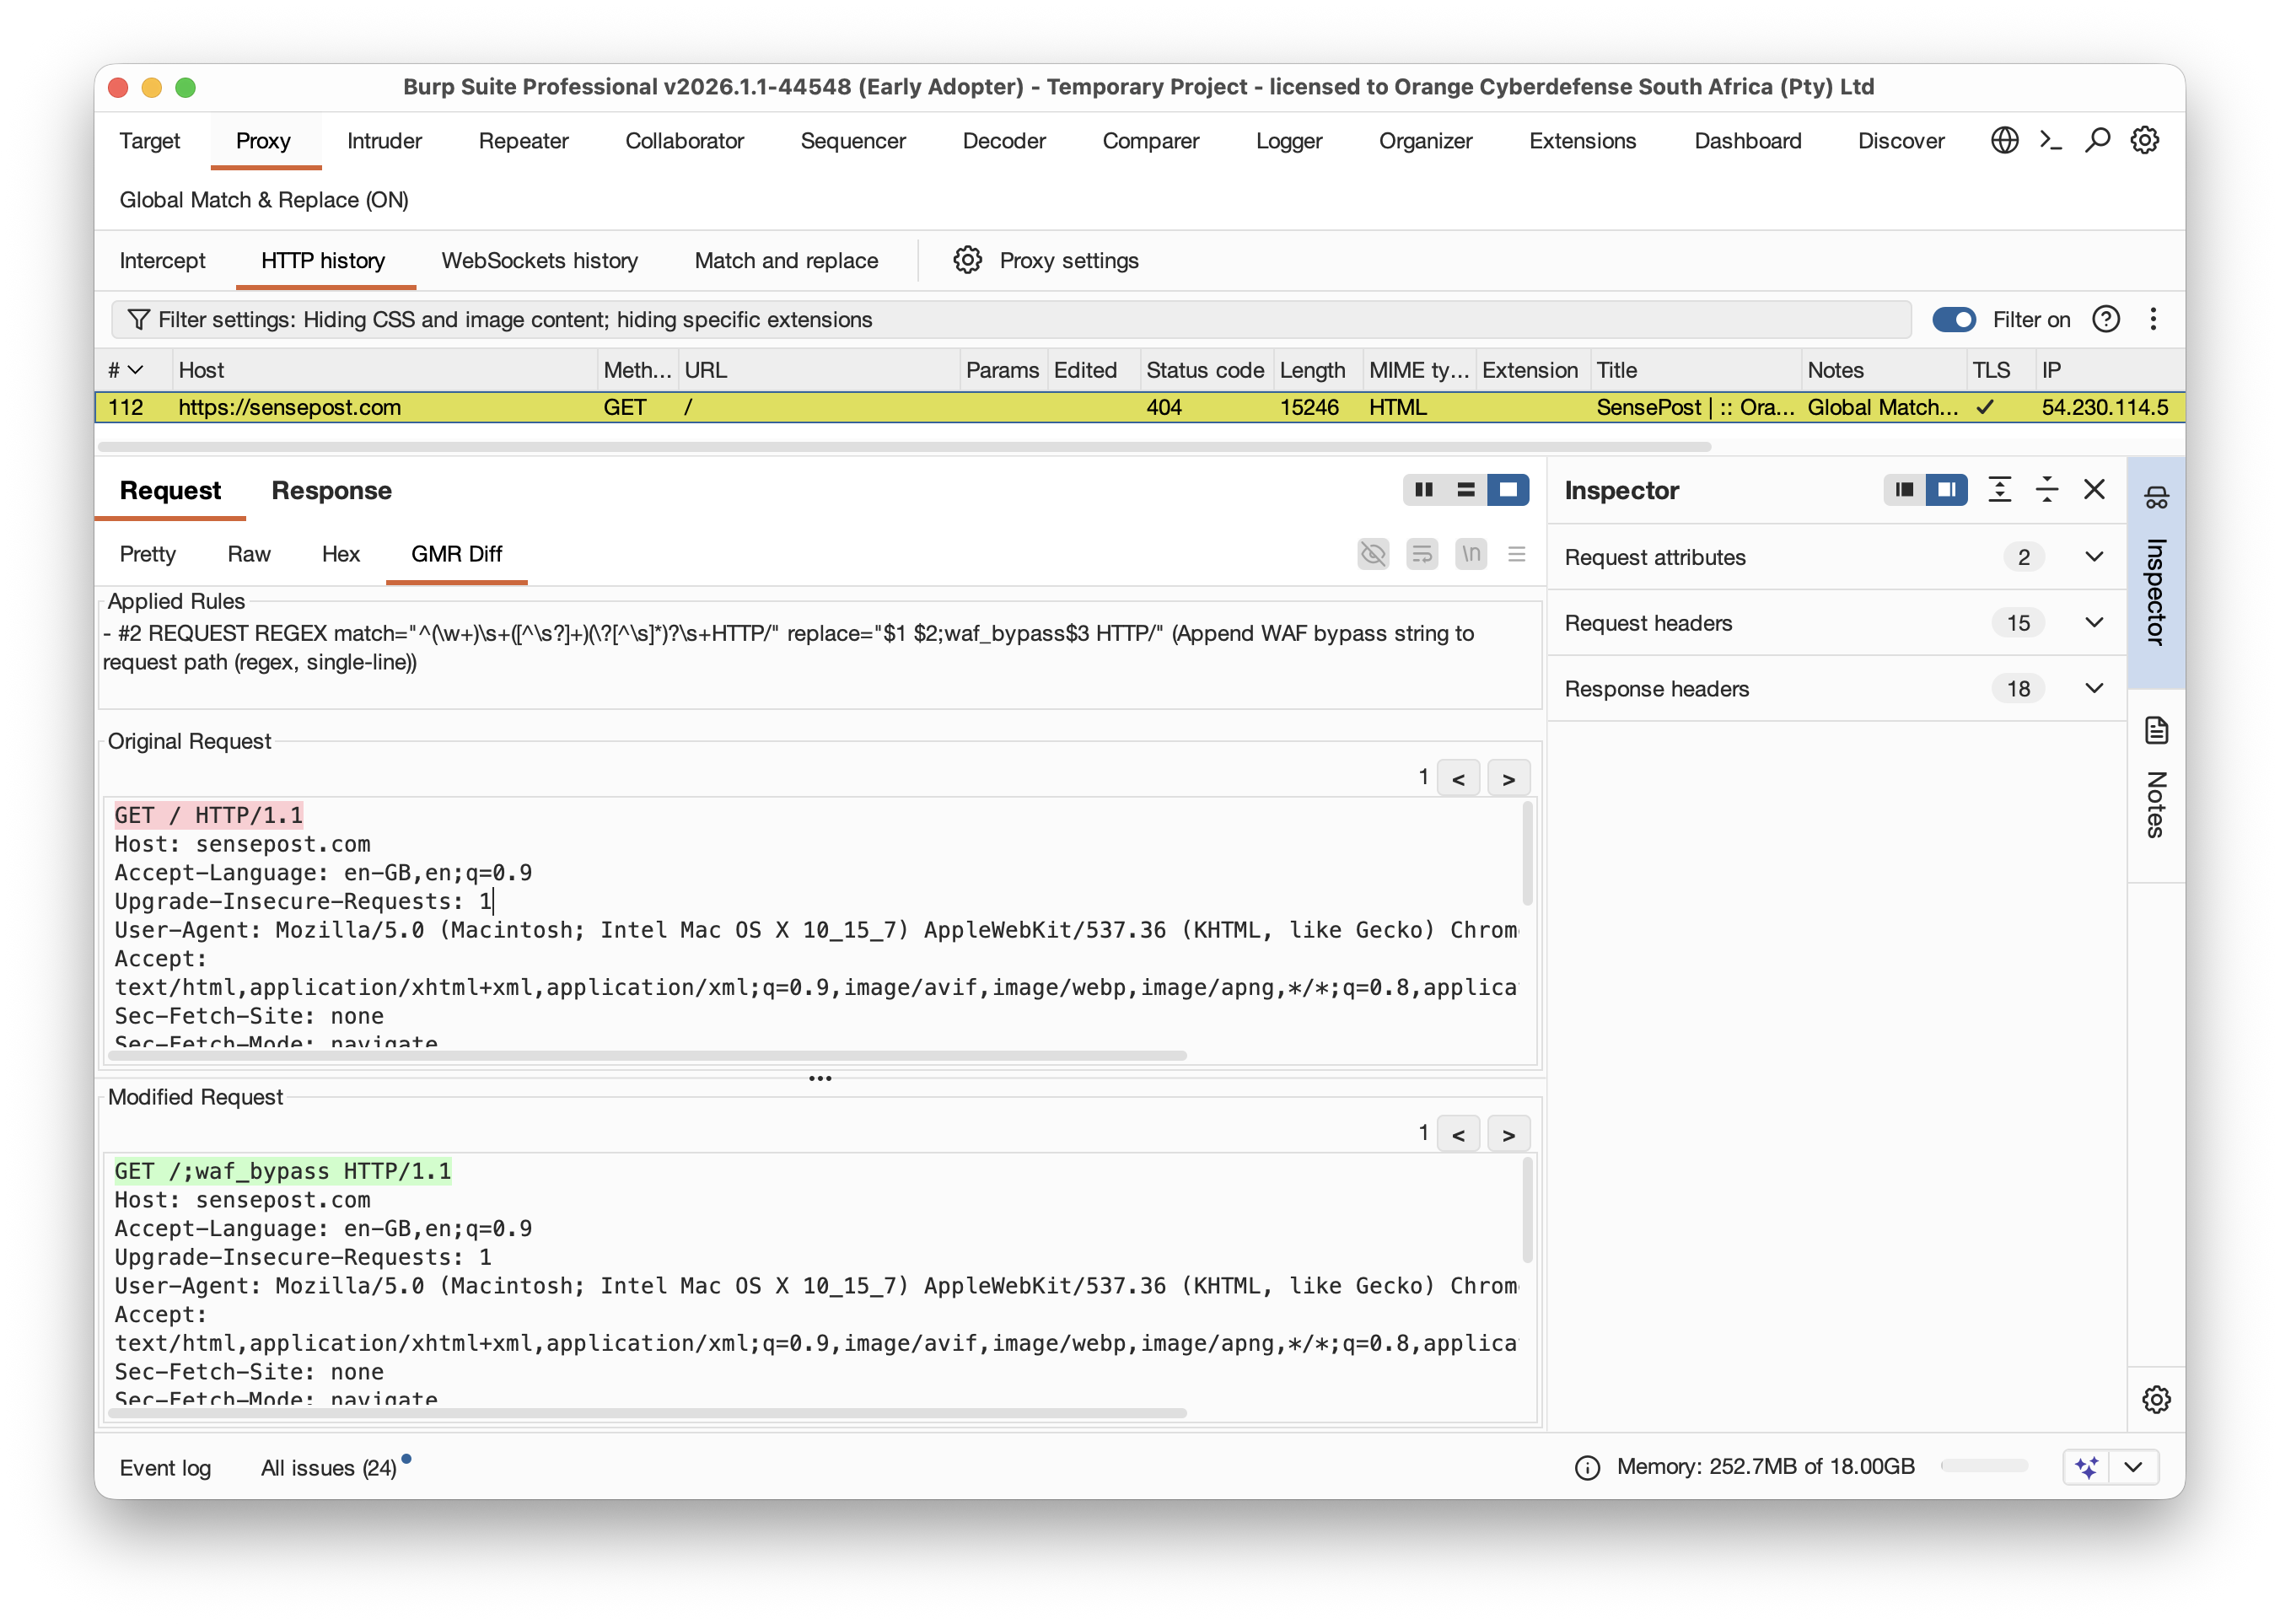
burp_global_match_replace
 singe/burp_global_match_replace
Match & Replace rules for Portswigger's Burp that operate globally across all utilities.
penetration-testingutilities-frameworksweb-proxies-interception+1
24
singe/burp_global_match_replaceMatch & Replace rules for Portswigger's Burp that operate globally across all utilities.
 caido-community/burp2caido
A tool to migrate Burpsuite HTTP history to Caido
 xnl-h4ck3r/auto-repeater
Automated HTTP Request Repeating With Burp Suite
 zaproxy/zap-api-rust
Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…
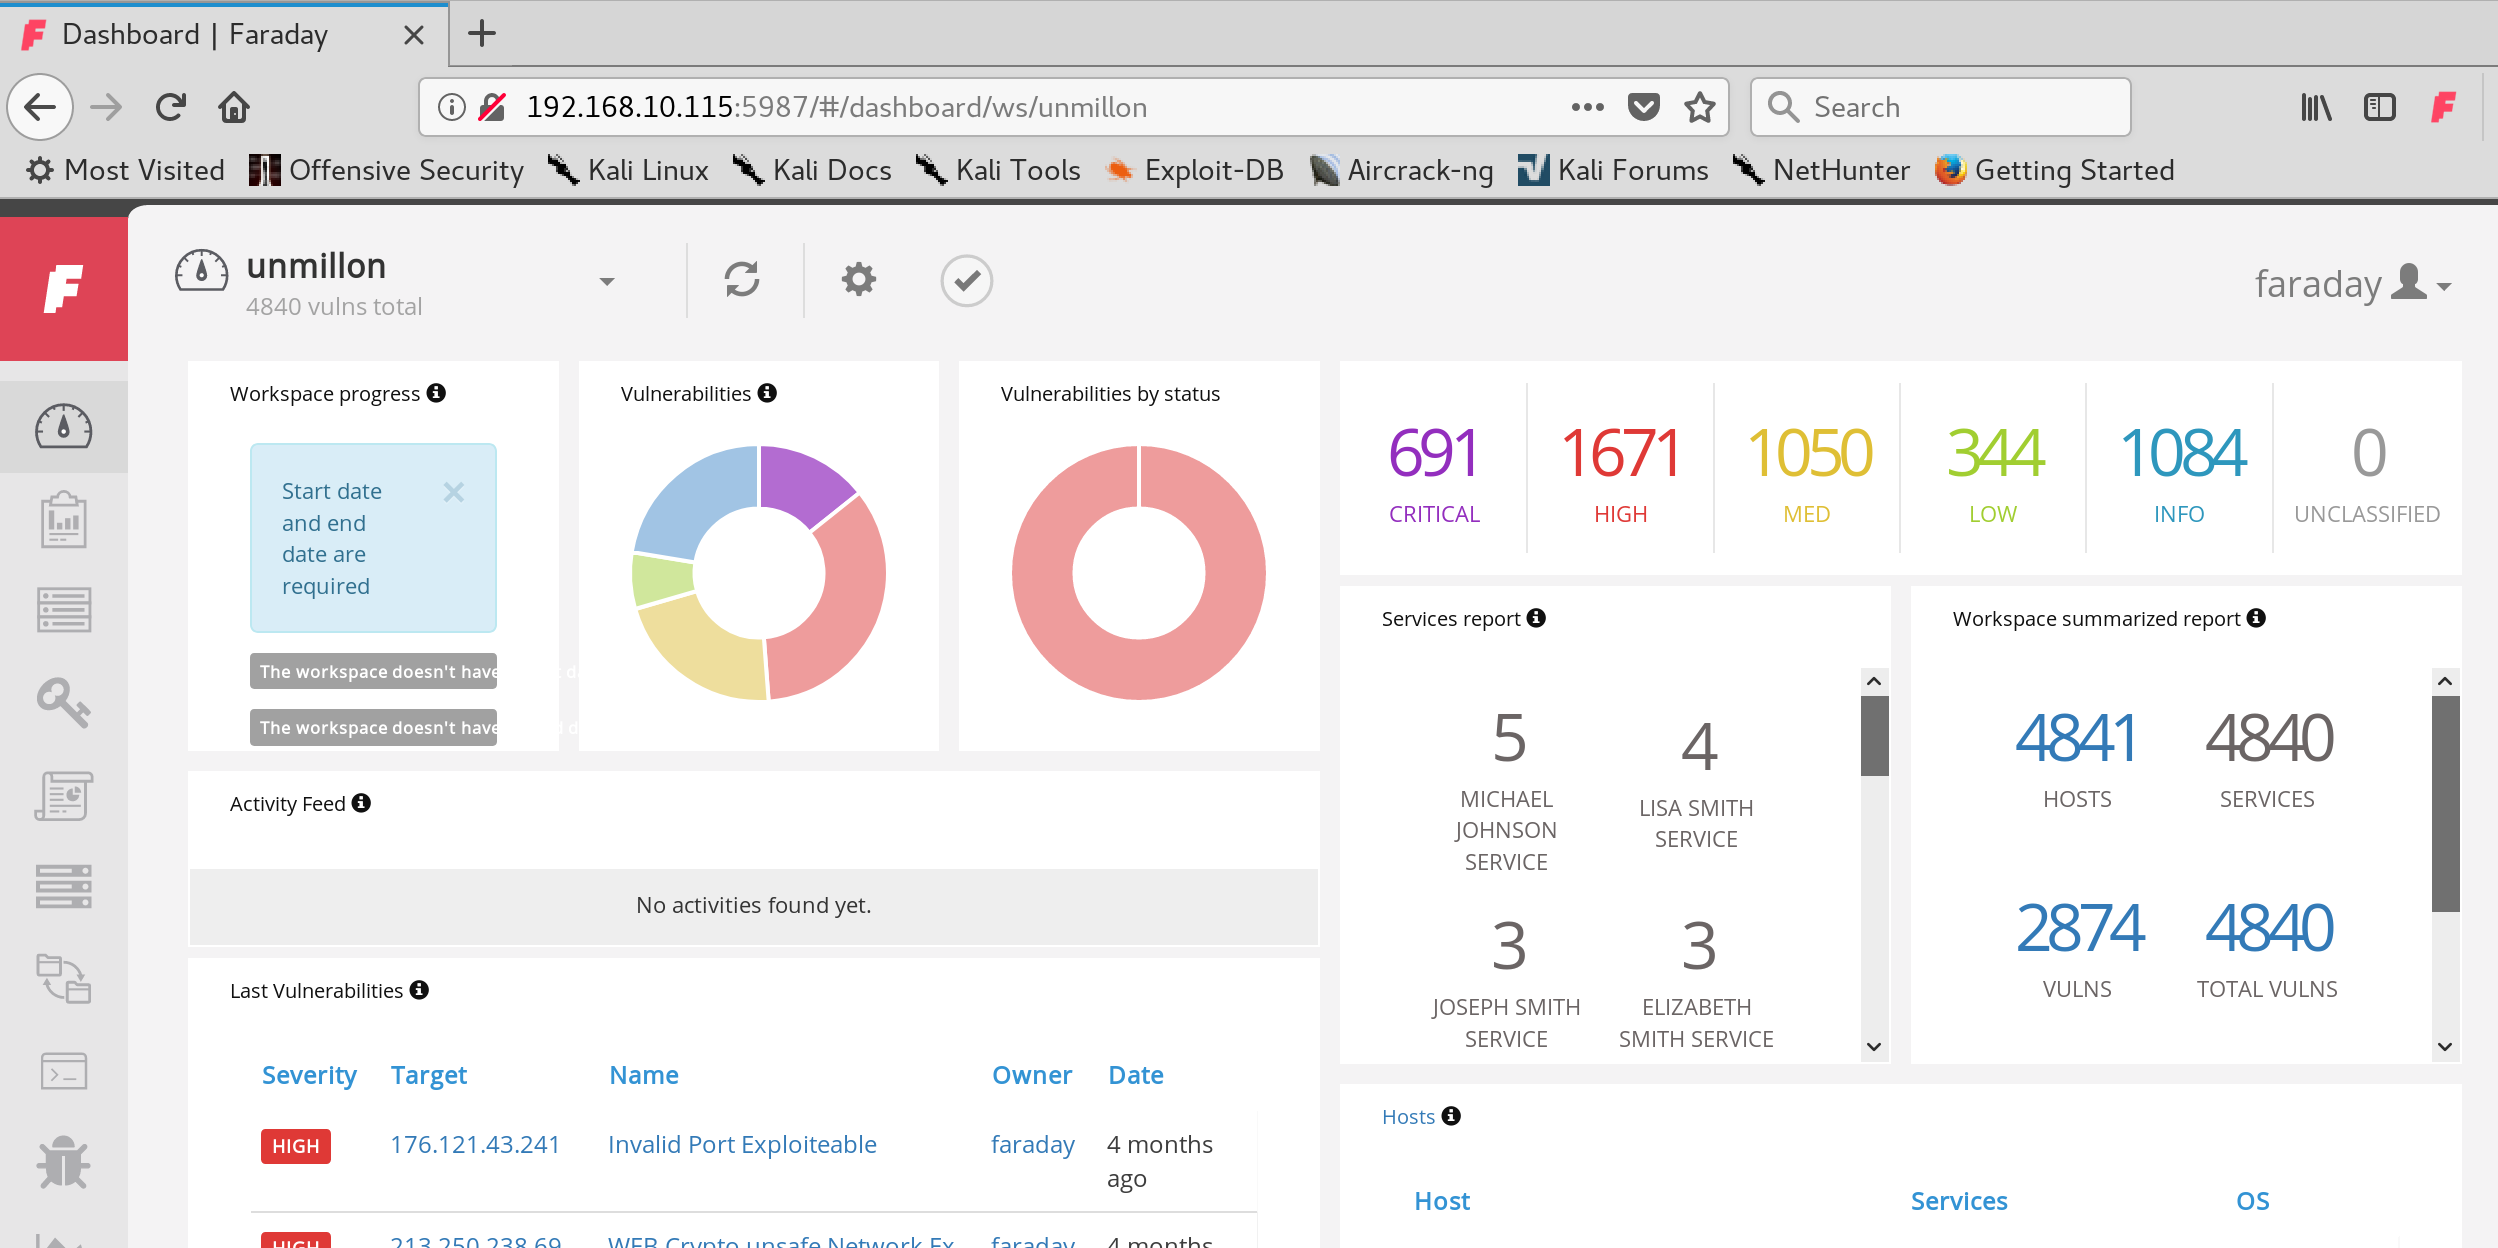 infobyte/faraday_addon
A browser extension for faradaysec platform https://faradaysec.com
 0xbartita/cookie-swapper
Burp Suite extension that auto-replaces cookies and headers in requests using configurable rules. Eliminates manual copy-pasting of session tokens…
 hemp3l/cve-2017-6640-poc
Proof of concept for CVE-2017-6640 as burp extension
 keith-amateur/cve-2022-1040
Save the trouble to open the burpsuite...
 nu11secur1ty/burpsuite-grand-master-tools
Modular toolkit for pentesters that converts Burp Suite captured HTTP requests into browsable URLs and automates workflow actions with auditable…
 ianxtianxt/proxysqlmap
From Proxy to SqlMapApi
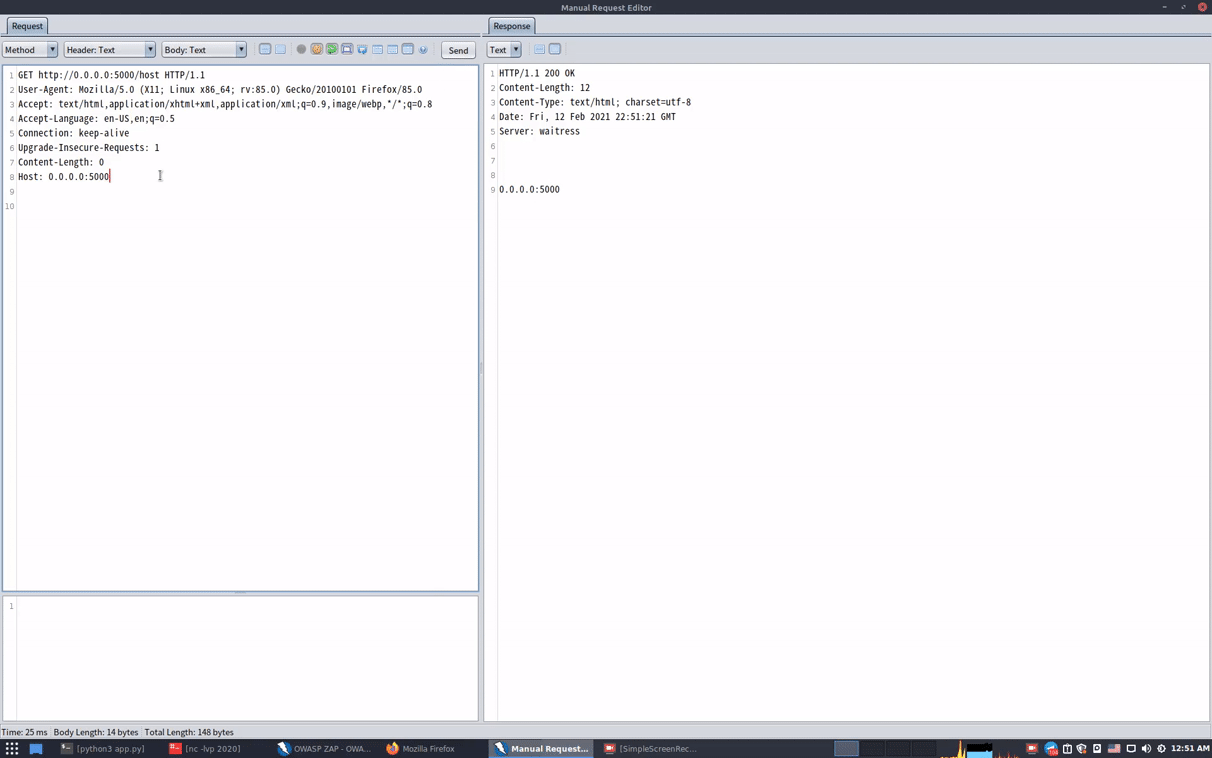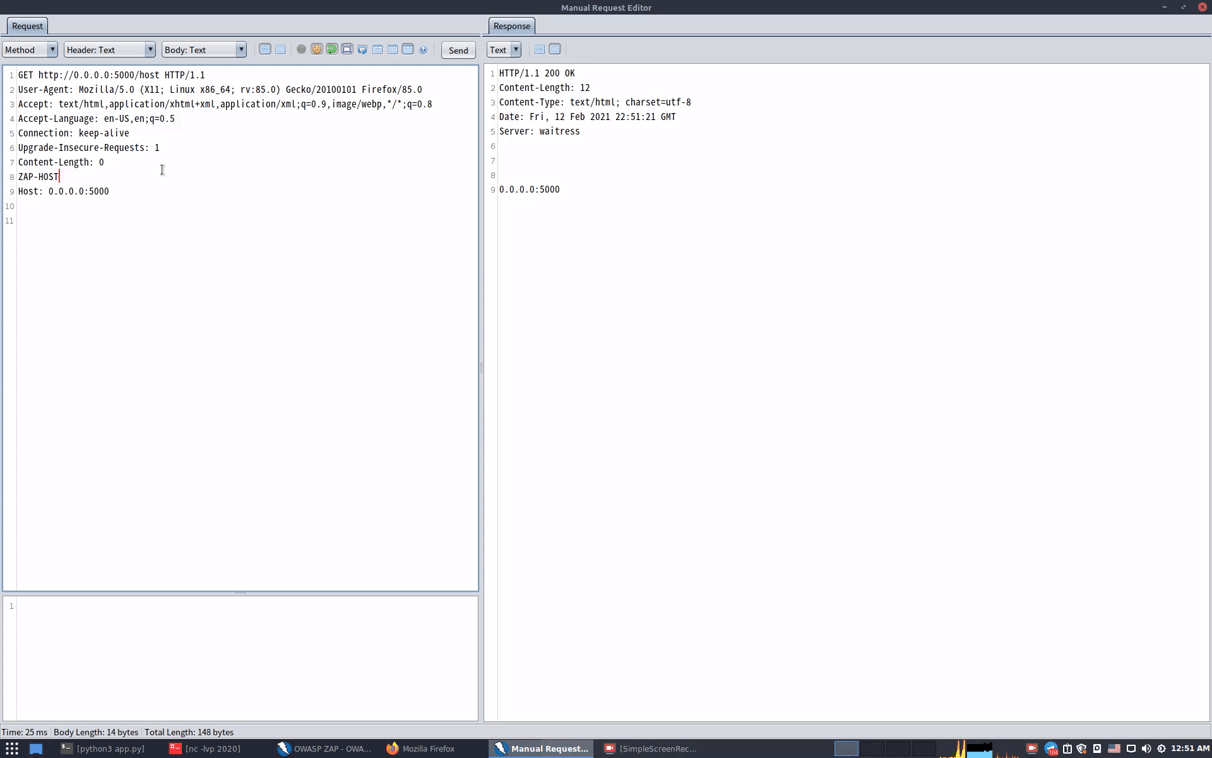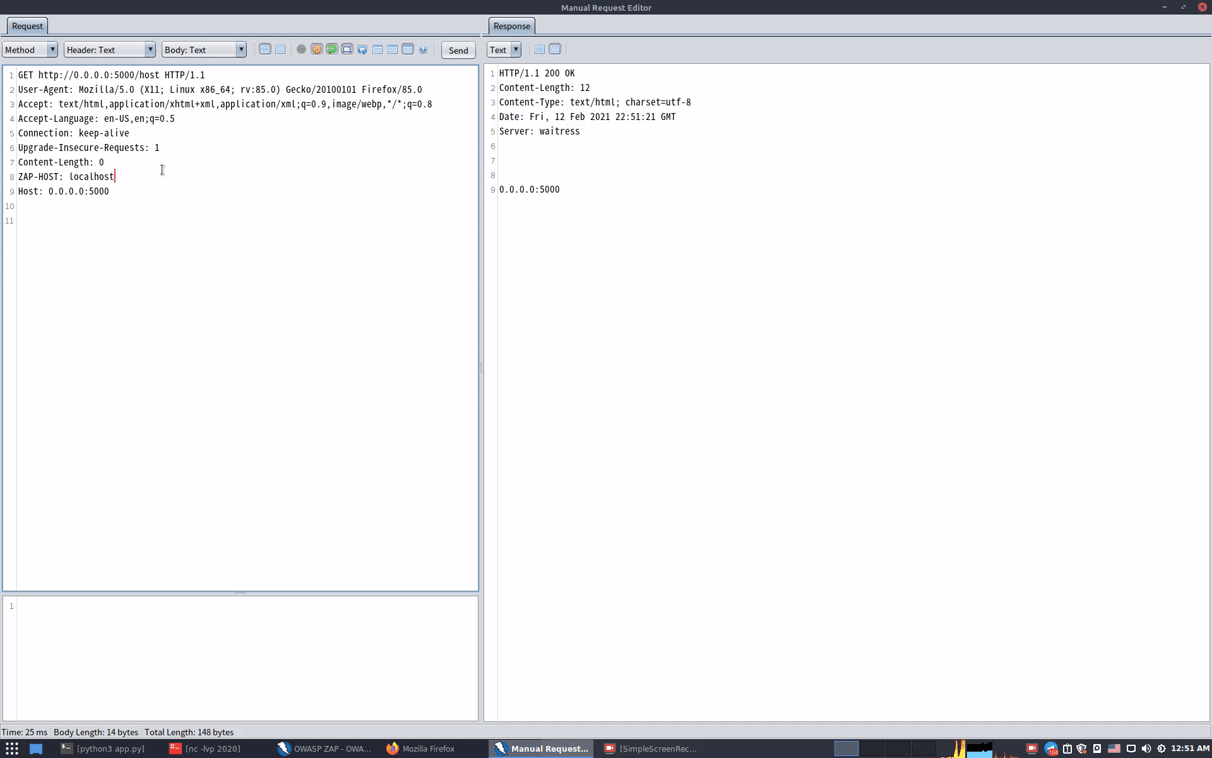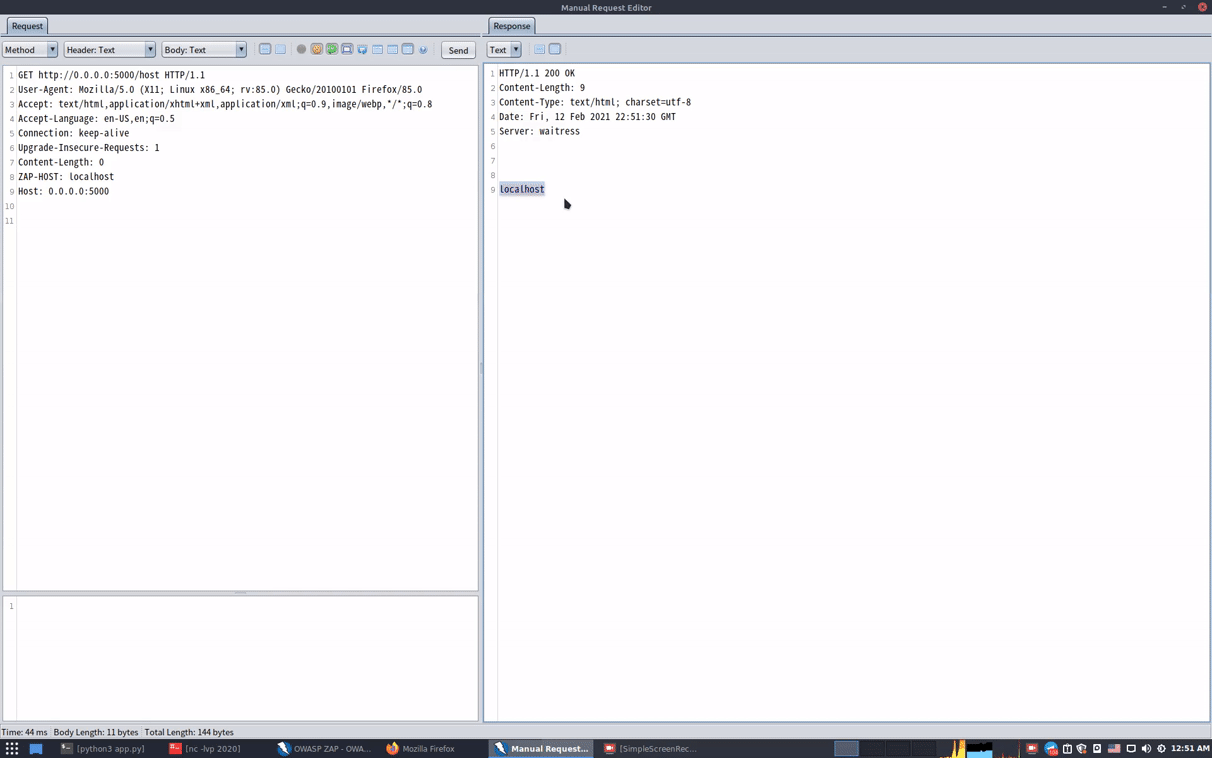 mindpatch/zaphoster
Fix host header error in zaproxy
 hackwarts12/burp-recordadora
Persists BurpSuite proxy history, Repeater requests, and Intruder payloads across sessions; exports and imports .log files for web pentesting context.
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
 ssh-mitm/ssh-mitm
Mirror moved — see GitHub and Codeberg