

coreruleset
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
anti-botids-ips-evasionmisconfiguration+4
3.3k
coreruleset/corerulesetGeneric attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
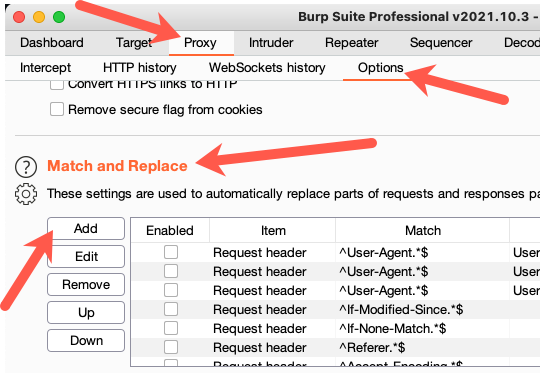 bishopfox/imperva_gzip_waf_bypass
Exploit for Imperva Cloud WAF bypass using gzip Content-Encoding header to evade WAF rules on HTTP POST requests. Includes detection script and…
 solidevil14/suricata-rule-for-detecting-cve-2025-55182
CVE‑2025‑55182 Detection
 lp008/cve-2020-13942
Exploit for Apache Unomi pre-auth RCE (CVE-2020-13942) with a Suricata detection rule for identifying exploitation attempts.
 streghstreek/cve-2020-1938
Detection rules for CVE-2020-1938 (Ghostcat) vulnerability in Apache Tomcat AJP connector, with Suricata and Bro signatures for network-based…
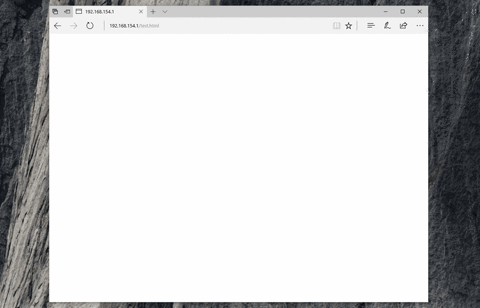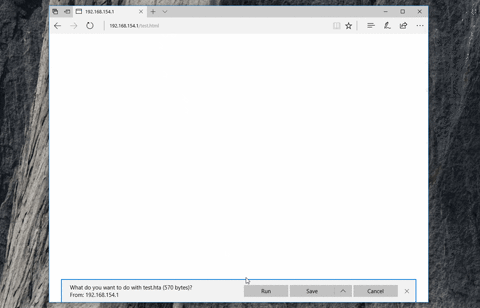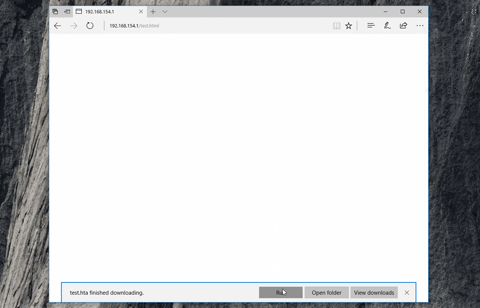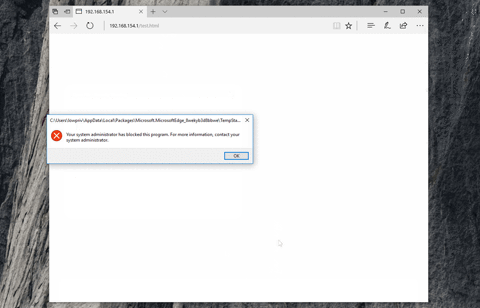 nccgroup/demiguise
HTA encryption tool for RedTeams
 assetnote/nowafpls
Burp Plugin to Bypass WAFs through the insertion of Junk Data
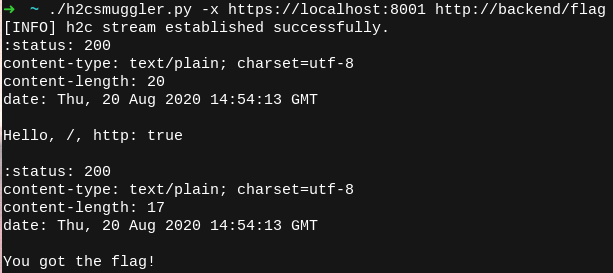 bishopfox/h2csmuggler
HTTP Request Smuggling over HTTP/2 Cleartext (h2c)
 r00t-3xp10it/morpheus
Morpheus - Automating Ettercap TCP/IP (MITM-hijacking Tool)
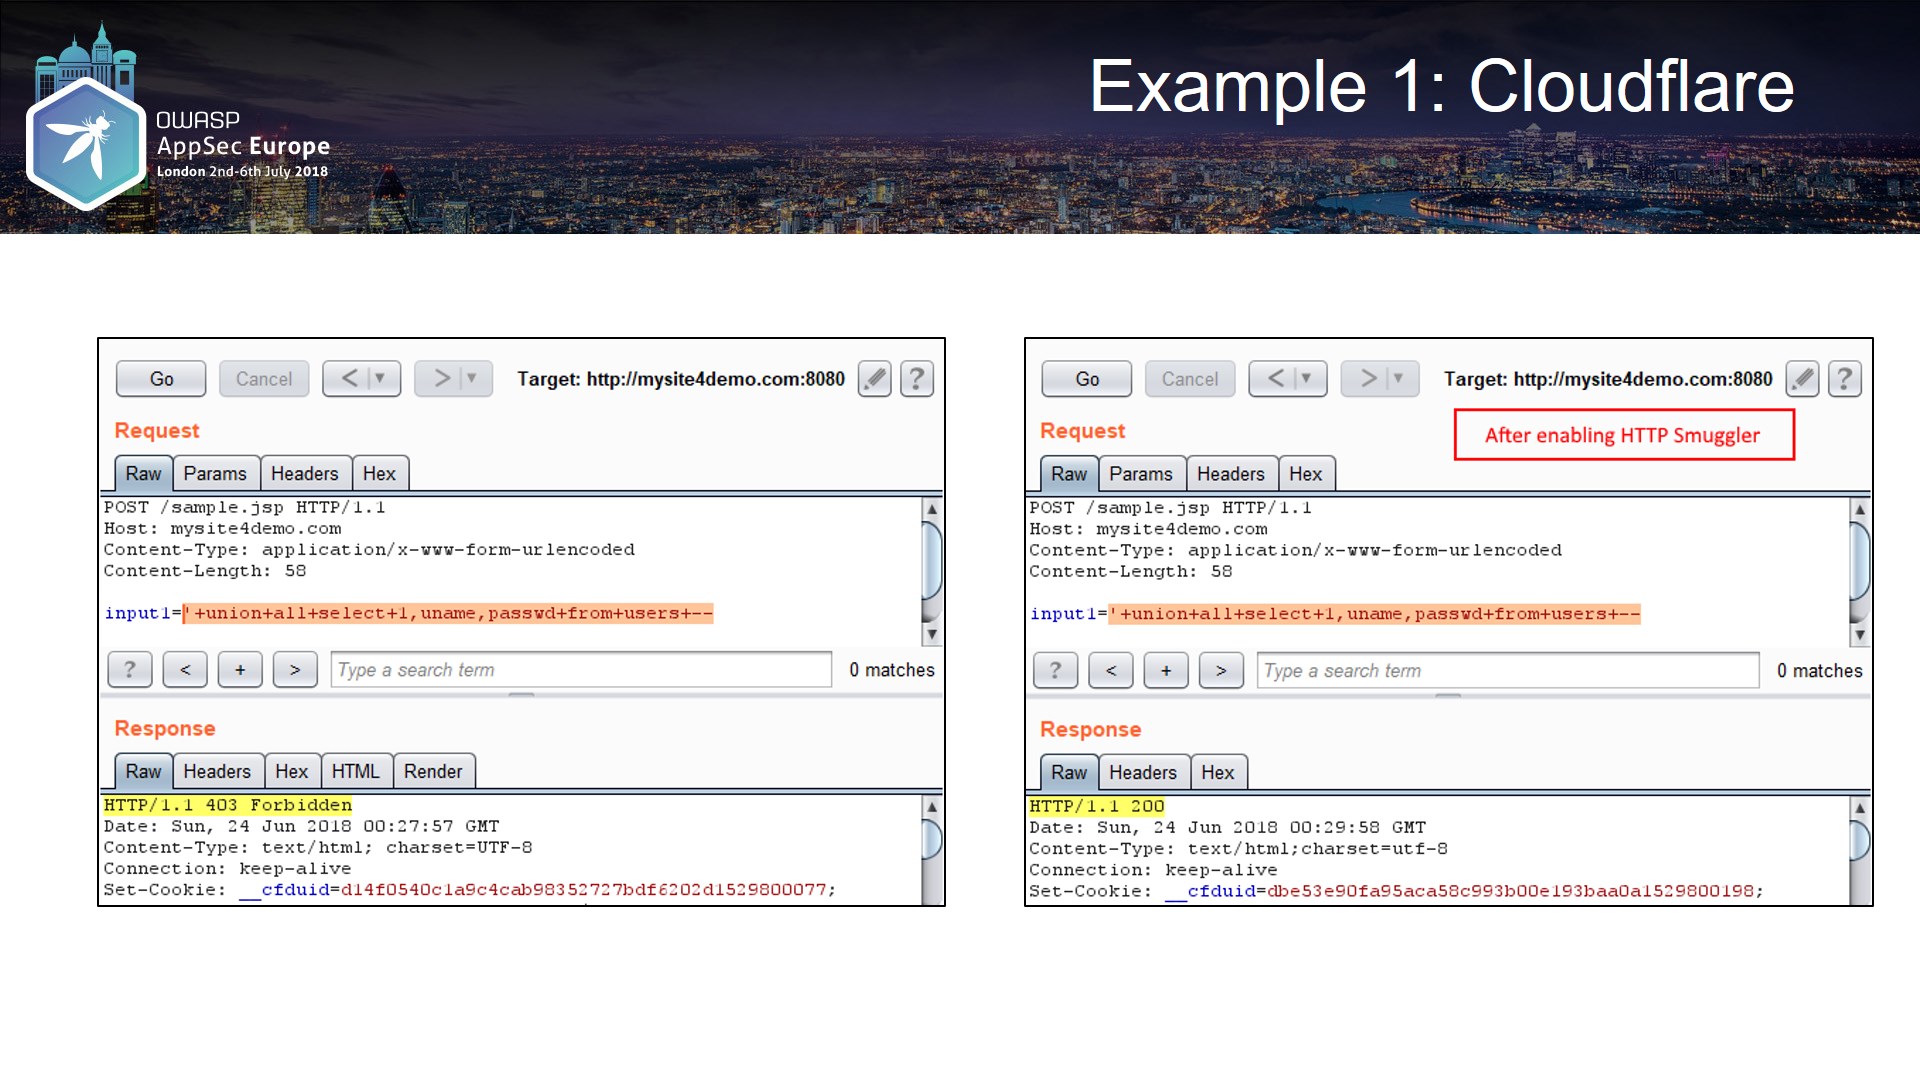 nccgroup/burpsuitehttpsmuggler
A Burp Suite extension to help pentesters to bypass WAFs or test their effectiveness using a number of techniques
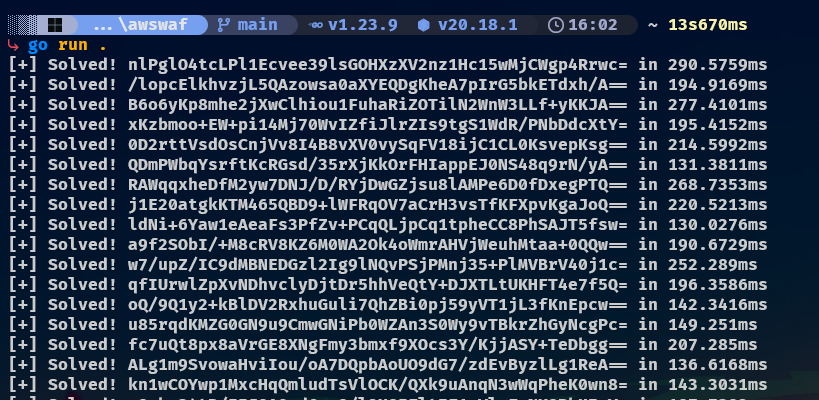 xkiian/awswaf
AWS WAF Solver, full reverse implemented in 100% Python & Golang.
 silverfoxx/pwnstar
PwnSTAR (Pwn SofT-Ap scRipt) - for all your fake-AP needs!
 jumpseclabs/tokenflare
Serverless AITM Simulation Framework for Entra ID and M365
 lnxg33k/webhandler
Bash simulator to control a server using PHP system functions.
 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.