
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
183 results
QRLJacking preview

QRLJacking

GitHubowasp/qrljacking

Social engineering attack vector and exploitation framework for hijacking user sessions via QR code login, targeting web applications like WhatsApp,…

exploit-frameworkspenetration-testingphishing+2
1.6k
1 year ago
OWASP-mth3l3m3nt-framework preview

OWASP-mth3l3m3nt-framework

GitHubalienwithin/owasp-mth3l3m3nt-framework

OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…

command-and-controlexploit-frameworkspayload-generation+3
1645 years ago
raider preview

raider

GitHubowasp/raider

OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
api-security-testingauthenticationpenetration-testing+3
1003 years ago
perwendel__spark_CVE-2016-9177_2-5-1 preview

perwendel__spark_CVE-2016-9177_2-5-1

GitHubshoucheng3/perwendel__spark_cve-2016-9177_2-5-1

Exploit for CVE-2016-9177 targeting Spark Java web framework, demonstrating directory traversal vulnerability in version 2.5.1 for security testing…
api-security-testingexploitationpenetration-testing+3
1 year ago
DeliberatelyVulnerableWebApp preview
Archived

DeliberatelyVulnerableWebApp

GitHubtimothyjxhn/deliberatelyvulnerablewebapp

A Deliberately Vulnerable Web Application built on Struts 2 (CVE-2017-5638) and Log4J (CVE-2021-44228) for testing and demonstration of OWASP Top 10…

educationexploitationlabs-practice+3
1 year ago
Spring4Shell preview

Spring4Shell

GitHubloneyers/spring4shell

Spring4Shell , Spring Framework RCE (CVE-2022-22965) , Burpsuite Plugin
api-security-testingexploitationpenetration-testing+3
44 years ago
Web-App-PenTesting preview

Web-App-PenTesting

GitHubsarthak4126/web-app-pentesting

Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
educationlabs-practicepenetration-testing+4
5 days ago
CVE-2022-23808 preview

CVE-2022-23808

GitHubdipakpanchal05/cve-2022-23808

Proof-of-concept exploit for CVE-2022-23808, a stored XSS vulnerability in phpMyAdmin 5.1.1 setup script, with payload and reproduction steps for…
exploitationpenetration-testingred-teaming+3
1151 year ago
Multi-VLAN-Enterprise-Network-Vulnerability-Assessment preview

Multi-VLAN-Enterprise-Network-Vulnerability-Assessment

GitHubklairmanraj/multi-vlan-enterprise-network-vulnerability-assessment

Multi-VLAN enterprise network vulnerability assessment using Nessus, OWASP ZAP, and Wireshark. Confirms Stored XSS on WebGoat and EternalBlue…

exploitationnetwork-mappingnetwork-security+6
5 months ago
CVE-2020-23839 preview

CVE-2020-23839

GitHubboku7/cve-2020-23839

Public PoC Disclosure for CVE-2020-23839 - GetSimple CMS v3.3.16 suffers from a Reflected XSS on the Admin Login Portal
exploitationpayload-developmentpenetration-testing+3
125 years ago
CVE-2026-21876 preview

CVE-2026-21876

GitHubdaytriftnewgen/cve-2026-21876

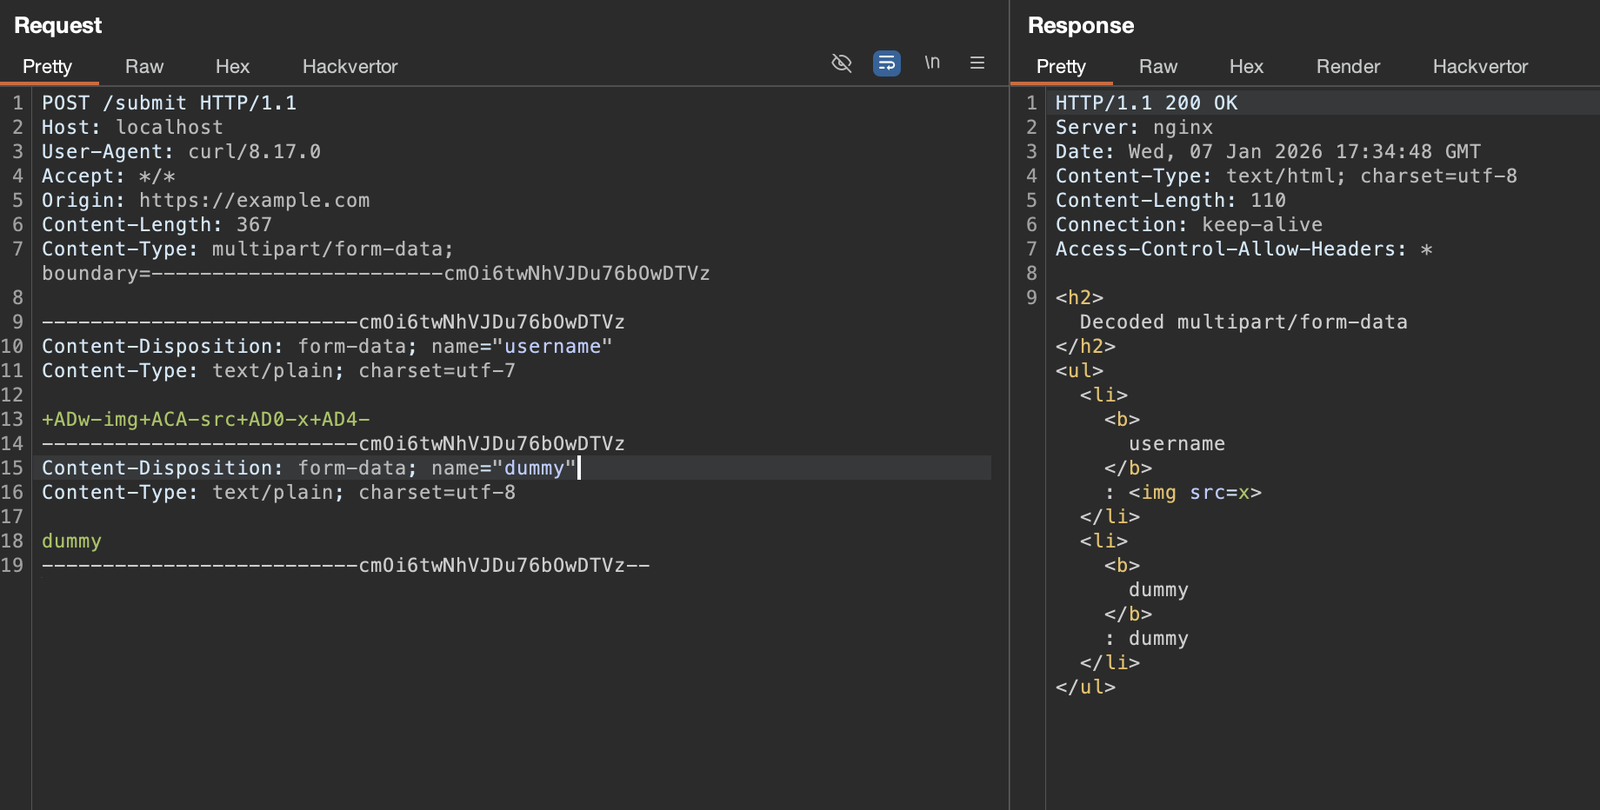
Proof-of-concept exploit for CVE-2026-21876 demonstrating multipart charset bypass of OWASP CRS WAF in Flask, ASP.NET, and Spring Boot applications.
ids-ips-evasionpenetration-testingvulnerability-analysis+3
3 months ago
CVE-2026-21876 preview

CVE-2026-21876

GitHubmefhika120/cve-2026-21876

Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.
exploitationpenetration-testingvulnerability-analysis+2
8 months ago
CVE-2024-11972-POC preview

CVE-2024-11972-POC

GitHubronf98/cve-2024-11972-poc

CVE-2024-11972 in Hunk Companion <1.9.0 allows unauthenticated attackers to exploit insecure REST API endpoints and install vulnerable plugins,…
api-security-testingcode-analysisexploitation+3
11 year ago
CVE-2024-48415 preview

CVE-2024-48415

GitHubkhaliquesx/cve-2024-48415

Proof-of-concept for CVE-2024-48415: stored XSS vulnerability in itsourcecode Loan Management System v1.0 via borrower profile fields. Includes…
educationpapers-researchvulnerability-analysis+2
1 year ago
joomscan preview

joomscan

GitHubowasp/joomscan

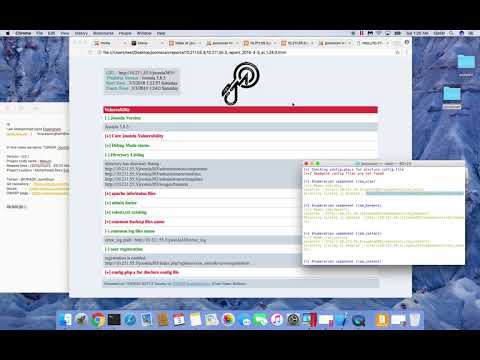
Perl-based Joomla CMS vulnerability scanner automating version enumeration, component detection, exploit matching, firewall identification, and…
information-gatheringmisconfigurationvulnerability-scanners+2
1.2k2 years ago
Vulnerable-Web-Application preview

Vulnerable-Web-Application

GitHubowasp/vulnerable-web-application

OWASP Vulnerable Web Application Project https://github.com/hummingbirdscyber

educationpenetration-testingweb-application-exploitation
4237 years ago
OFFAT preview

OFFAT

GitHubowasp/offat

Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…
api-securityapi-security-testingfuzzing+2
6731 month ago
vbscan preview
Archived

vbscan

GitHubowasp/vbscan

OWASP VBScan is a Black Box vBulletin Vulnerability Scanner

exploitationinformation-gatheringpenetration-testing+3
3257 years ago
Previous12…11Next