
svja
 theronielanddaronpodcastshow/svja
The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…
api-security-testingauthentication-authorizationeducation+5
13
theronielanddaronpodcastshow/svjaThe Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…
 alt3kx/cve-2018-7691
The SSC REST API contains Insecure Direct Object Reference (IDOR) vulnerabilities in Fortify Software Security Center (SSC) 17.10, 17.20 & 18.10
 alt3kx/cve-2018-7690
The SSC REST API contains Insecure Direct Object Reference (IDOR) vulnerabilities in Fortify Software Security Center (SSC) 17.10, 17.20 & 18.10
 l4zyfox/rise-ultimate_project_manager_e_crm
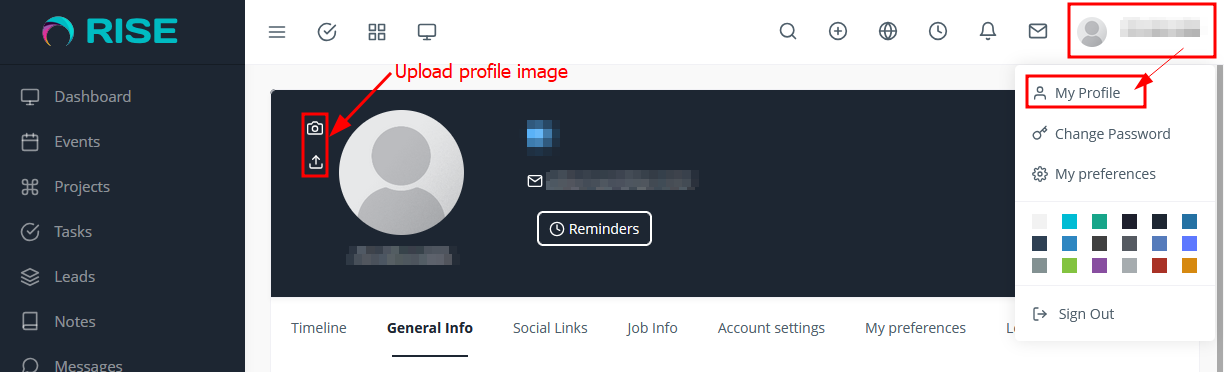
CVE-2025-3855 - RISE Ultimate Project Manager - IDOR
 owasp/offat
Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 yeswehack/vulnerable-code-snippets
Twitter vulnerable snippets
 moeinfatehi/xss_vulnerability_challenges
Dockerized PHP application providing hands-on XSS vulnerability challenges and bypass examples, including WAF, blacklist, and JavaScript validation…
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
 owasp/vbscan
OWASP VBScan is a Black Box vBulletin Vulnerability Scanner
 owasp/vulnerable-web-application
OWASP Vulnerable Web Application Project https://github.com/hummingbirdscyber
 owasp/joomscan
Perl-based Joomla CMS vulnerability scanner automating version enumeration, component detection, exploit matching, firewall identification, and…
 owasp/dvsa
a Damn Vulnerable Serverless Application
 owasp/webgoat
This is a defunct code base. The project is located at: https://github.com/WebGoat
 owasp/qrljacking
Social engineering attack vector and exploitation framework for hijacking user sessions via QR code login, targeting web applications like WhatsApp,…
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 doretox/atomicvulns
Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
 keygraphhq/shannon
Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…