
spider
 173210/spider
Exploit for CVE-2013-2842, a kernel privilege escalation vulnerability, providing local privilege escalation on affected Linux systems.
exploitationpayload-developmentpenetration-testing+2
3
173210/spiderExploit for CVE-2013-2842, a kernel privilege escalation vulnerability, providing local privilege escalation on affected Linux systems.
 abdelhakimgafernetworksec/enigm-writeup
Comprehensive penetration testing write-up and exploit details for Hack The Box - Enigma machine, covering local enumeration, OliveTin CVE-2026-27626…
 mattiapertusati/htb-facts
HackTheBox — Facts (Easy/Linux) | CVE-2025-2304 + AWS S3 + SSH Key + Facter PrivEsc
 mzfr/liffy
Local file inclusion exploitation tool
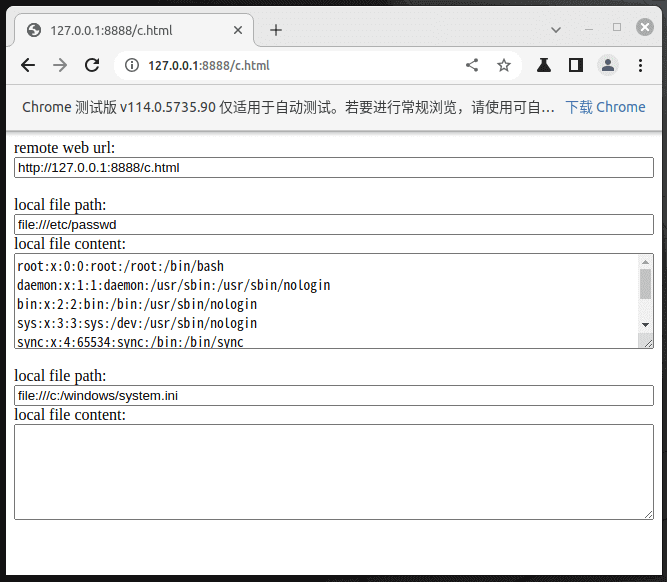 xcanwin/cve-2023-4357-chrome-xxe
[漏洞复现] 全球首款单文件利用 CVE-2023-4357 Chrome XXE 漏洞 EXP, 实现对访客者本地文件窃取. Chrome XXE vulnerability EXP, allowing attackers to obtain local files of visitors.
 royaleybovich/cve-2026-3854-lab
Local intentionally vulnerable lab with a guided workshop and CTF challenges for practicing Git push-option RCE, unsafe deserialization,…
 llamakko/cve-2015-7214
Proof-of-concept exploit for CVE-2015-7214 demonstrating Same-Origin Policy bypass in Firefox 42.0 via data and view-source URIs, with local and…
 revshellxd/lfi-destruction
This program Prompts you for the Local File Inclusion information and will automatically search the /etc/passwd and using the users names found will…
 mega-starmie/tomcat-cve-2025-24813-lab
Local reproduction lab for Apache Tomcat CVE-2025-24813, documenting exploitation conditions and AI-assisted verification of the vulnerability.
 tharana/vulnerability-exploitation
Local Root vulnerability- CVE-2019-13272 / Security Bypass Vulnerability – CVE-2019-14287/Google Android - 'Stagefright' Remote Code Execution -…
 themehackers/cve-2026-22804
This repository contains a Proof of Concept (PoC) exploit for the Stored Cross-Site Scripting (XSS) vulnerability in Termix, which can lead to Local…
 logggg2402/cve-2025-27407
Local lab and proof-of-concept exploit for CVE-2025-27407, targeting GitLab's GraphQL introspection schema loader via the Direct Transfer HTTP path.…
 lucastran05/cve-2026-29000
Local lab simulating CVE-2026-29000 JWT/JWE authentication bypass in pac4j-jwt. Provides login, token forging, and dashboard APIs for practicing web…
 brunoh6/web-threat-mitigation
Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell…
 mkelepce/cve-2020-13424
Joomla! Plugin XCloner Backup 3.5.3 - Local File Inclusion (Authenticated)
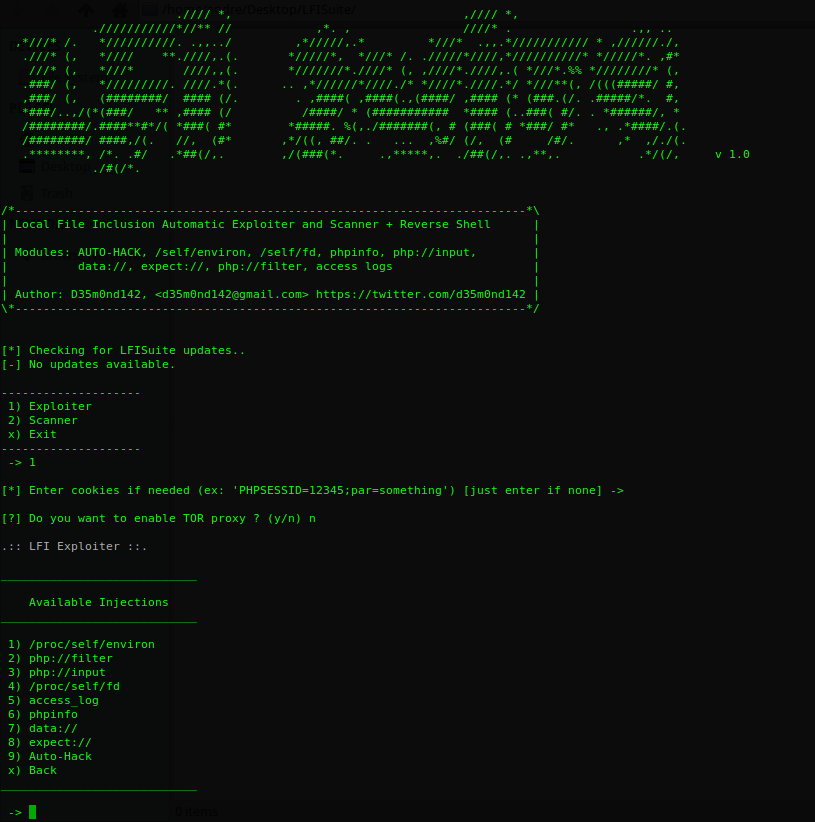 d35m0nd142/lfisuite
Totally Automatic LFI Exploiter (+ Reverse Shell) and Scanner
 lyrebirds/sagemcom-fast-3890-exploit
Exploit for Sagemcom F@ST 3890 cable modem implementing Cable Haunt vulnerability to achieve remote code execution via WebSocket-based buffer…
 u1tr0nex/cve-2026-40072-ssrf-lab
Hands-on lab for CVE-2026-40072 — SSRF vulnerability in web3.py via CCIP Read (EIP-3668)