Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/xcanwin/cve-2023-4357-chrome-xxe
Vulnerability AnalysisExploitationWeb Application ExploitationCTFLearning & EducationCurated Resources
GitHubxcanwin/cve-2023-4357-chrome-xxe

CVE-2023-4357-Chrome-XXE

[漏洞复现] 全球首款单文件利用 CVE-2023-4357 Chrome XXE 漏洞 EXP, 实现对访客者本地文件窃取. Chrome XXE vulnerability EXP, allowing attackers to obtain local files of visitors.

View Repository
23037471 year agoReviewed by Kitploit

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    614
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    476
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    389
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    334
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    257
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    247

Explore all tools

Browse our collection of tools

View all tools →
Share

Tool Introduction

  • The world's first single file exploits the CVE-2023-4357 Chrome XXE vulnerability EXP, allowing attackers to obtain local files of visitors.
  • The world's first single file exploits the CVE-2023-4357 Chrome XXE vulnerability EXP, allowing attackers to obtain local files of visitors.
File NameDescriptionExploit ScenarioWhy can a single file / single payload achieve exploitation?
d.svgSingle file exploitation, no dependency on other files1. When XSS is possible, embed the svg link in an iframe.
2. When a button is clicked, open the svg image in a new window.
Self-contained. The first entity declaration referencing an external entity is blocked, so we thought of self-including the file as an external XML document, then making a second entity declaration referencing the external entity, requiring the two reference formats to be compatible without errors, thereby bypassing the block and reading local files.
xss.htmlSingle payload exploitation, no dependency on other filesWhen XSS is possible and you don't want to upload an svg file on any website, copy the content of xss.html as the payload.object element, data:image/svg+xml;base64, data:text/xsl;base64

Interesting Sharing

  • This single-file EXP was used as the inspiration for problem design in the TPCTF 2023 Information Security Competition (jointly organized by TP-Link, Tsinghua University, and Peking University).
  • Problems: Xssbot and Xssbot but not Internet
  • Sharp-eyed contestants noticed my comment //You can send p.innerHTML by POST.: cn-sec, xmcve, jbnrz
  • Contributing interesting learning resources for new information security enthusiasts is one of the meanings of this open source project.

Vulnerability Introduction

InformationContent
Vulnerability NameChromium XXE
CVE IDCVE-2023-4357
Risk LevelHigh
Vulnerability TypeXXE
Exploit DifficultyLow

Vulnerability Description

  • The root cause of the vulnerability lies in libxslt. By default, Chromium strictly validates whether the external entity URL referenced by the entity declaration in an XML document is cross-origin. However, if Chromium first parses it as an XSL stylesheet and then uses document() to include an external XML document, Chromium does not perform cross-origin validation on the URL of this external XML document, causing local file disclosure for the visitor.

Affected Versions

  • Chrome version < 116.0.5845.96
  • Chromium version < 116.0.5845.96
  • Electron version < 26.1.0
  • WeChat for Mac version < 3.8.5.17

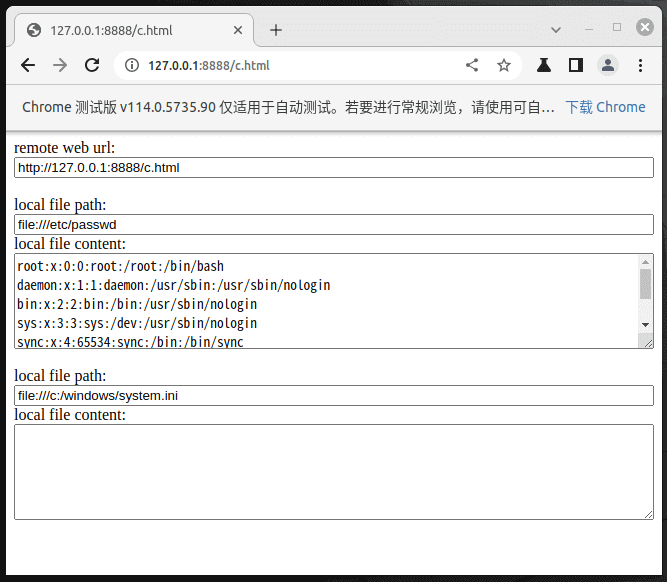
Reproduction Screenshots

Visitor EnvironmentScreenshot
Linux + Chromium
Windows + Chromium
MacOS + WeChat for Mac

Reproduction 1

  1. Visitor Environment:
Linux + Chromium
  1. Download and run Chrome
wget https://edgedl.me.gvt1.com/edgedl/chrome/chrome-for-testing/114.0.5735.90/linux64/chrome-linux64.zip
unzip chrome-linux64.zip
./chrome-linux64/chrome --no-sandbox
  1. Start Web service
wget https://codeload.github.com/xcanwin/CVE-2023-4357-Chrome-XXE/zip/refs/heads/main -O CVE-2023-4357-Chrome-XXE.zip
unzip CVE-2023-4357-Chrome-XXE.zip
python3 -m http.server 8888 -d CVE-2023-4357-Chrome-XXE-main
  1. Visit in browser
http://127.0.0.1:8888/d.svg

Reproduction 2

  1. Visitor Environment:
Windows + Chromium
  1. Download and run Chrome
https://edgedl.me.gvt1.com/edgedl/chrome/chrome-for-testing/114.0.5735.90/win64/chrome-win64.zip

./chrome-win64/chrome --no-sandbox
  1. Start Web service
https://codeload.github.com/xcanwin/CVE-2023-4357-Chrome-XXE/zip/refs/heads/main

python3 -m http.server 8888 -d CVE-2023-4357-Chrome-XXE-main
  1. Visit in browser
http://127.0.0.1:8888/d.svg

Reproduction 3

  1. Visitor Environment:
MacOS + WeChat for Mac
  1. Download and run WeChat for Mac

  2. Start Web service

wget https://codeload.github.com/xcanwin/CVE-2023-4357-Chrome-XXE/zip/refs/heads/main -O CVE-2023-4357-Chrome-XXE.zip
unzip CVE-2023-4357-Chrome-XXE.zip
python3 -m http.server 8888 -d CVE-2023-4357-Chrome-XXE-main
  1. Send to File Transfer Assistant and visit
http://127.0.0.1:8888/d.svg
Download Tool