

wpscan
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
crawlerdynamic-code-analysisinformation-gathering+7
wpscanteam/wpscanWordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 an0nlk/nosql-mongodb-injection-username-password-enumeration
Using this script, you can enumerate Usernames and passwords of Nosql(mongodb) injecion vulnerable web applications.
 ac3lives/kyocera-cve-2022-1026
An unauthenticated data extraction vulnerability in Kyocera printers, which allows for recovery of cleartext address book and domain joined passwords
 shaheemirza/tendaspill
An exploitation tool to extract passwords using CVE-2015-5995.
 0xcyp1337/cve-2026-19598-
Exploits CVE-2026-19598 in WordPress Pods plugin to create admin accounts or overwrite passwords via unauthenticated AJAX request, with mass scanning…
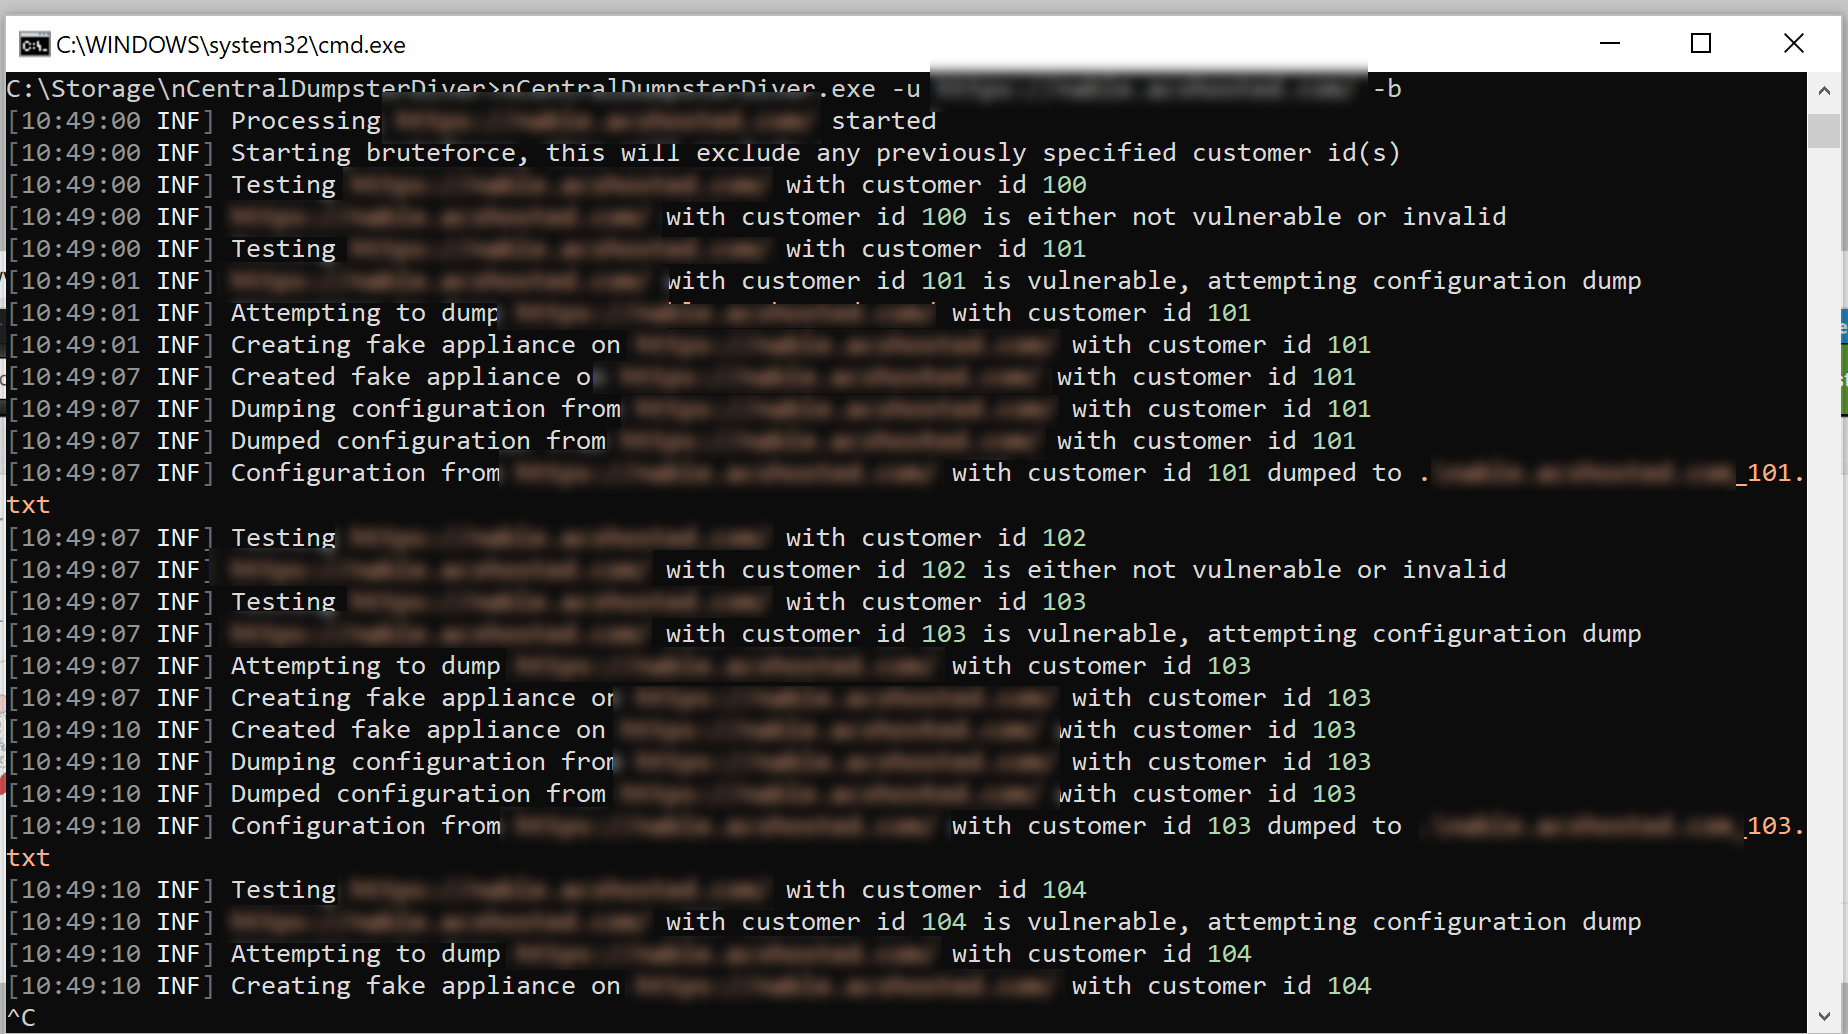 flipfloptech/ncentraldumpsterdiver
This application utilized the Self Registration feature to create a rogue agent that then dumps ApplianceConfiguration settings which may or may not…
 unpredictable21/halo-cors-csrf-cve-2026-67921
Proof-of-concept demonstrating a combined CORS misconfiguration and CSRF protection bypass in Halo CMS, enabling cross-site request forgery attacks…
 xploitgh0st/cve-2025-48932---exploit
Proof-of-concept exploit for CVE-2025-48932, a SQL injection in Invision Community <= 4.7.20. Extracts admin credentials and resets passwords via…
 h4po0n/kyocera-cve-2022-1026_soap1.1
An unauthenticated data extraction vulnerability in Kyocera printers, which allows for recovery of cleartext address book and domain joined passwords.
 simoesctt/ctt-enhanced-apache-mod_auth_digest-timing-attack-exploit
Remote timing attack exploit for Apache mod_auth_digest (CVE-2026-33006) that bypasses Digest authentication via a 33-layer temporal cascade,…
 vincent-vbg/cve-2025-58434-poc
This repository contains a Proof of Concept (PoC) Python script for CVE-2025-58434, which enables attackers to change passwords of other users…
 r3dston3/cve-2023-23752
Proof-of-concept exploit for CVE-2023-23752 (Joomla 4.0.0-4.2.8) that extracts usernames and passwords via an information disclosure vulnerability.
 primus27/wordpress-long-password-denial-of-service
Exhaust WordPress <V5.0.1 resources using long passwords (CVE-2014-9016)
 trqt/cve-2024-48322
Exploit for CVE-2024-48322 targeting RunCodes instances. Retrieves user passwords via email inbox after authentication bypass, requiring only any…
 bypazs/cve-2023-26984
An issue in the password reset function of Peppermint v0.2.4 allows attackers to access the emails and passwords of the Tickets page via a crafted…
 saykino/cve-2023-34732
Proof-of-concept exploit for CVE-2023-34732 demonstrating authenticated function abuse in Flytxt NEON-dX to brute-force and reset user passwords,…
 jas502n/grafana-cve-2021-43798
Grafana Unauthorized arbitrary file reading vulnerability
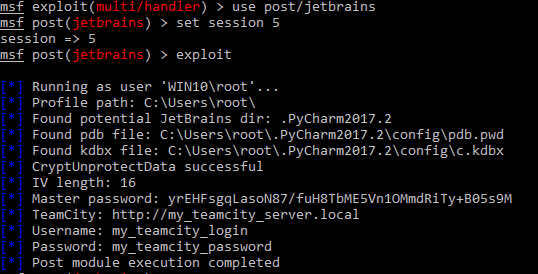 kacperszurek/pentest_teamcity
Pentest TeamCity using Metasploit