

strix
 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
ai-securityapi-security-testingcode-analysis+9
64.4k
usestrix/strixOpen-source AI penetration testing tool to find and fix your app’s vulnerabilities.
 keygraphhq/shannon
Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…
 ksharinarayanan/ssrfire
An automated SSRF finder. Just give the domain name and your server and chill! ;) Also has options to find XSS and open redirects
 papamica/waf-checker
Tests your WAF with +160 payloads
 thecyb3ralpha/bobthesmuggler
"Bob the Smuggler": A tool that leverages HTML Smuggling Attack and allows you to create HTML files with embedded 7z/zip archives. The tool would…
 silverfoxx/pwnstar
PwnSTAR (Pwn SofT-Ap scRipt) - for all your fake-AP needs!
 tuhinshubhra/shellstack
A PHP Based Tool That Helps You To Manage All Your Backdoored Websites Efficiently.
 d00movenok/htmlsmuggler
✉️ HTML Smuggling generator&obfuscator for your Red Team operations
 koadt/oss-oopssec-store
Security training for the apps you actually ship. Open your browser and start hacking.
 portswigger/css-the-bomb-inside-your-inbox
All the materials for Gareth Heyes' Black Hat talk: CSS: the bomb inside your inbox.
 whitespots/fast-security-scanners
Security checks for your researches
 fredbrave/cve-2022-46169-cacti-1.2.22
This is a exploit of CVE-2022-46169 to cacti 1.2.22. This exploit allows through an RCE to obtain a reverse shell on your computer.
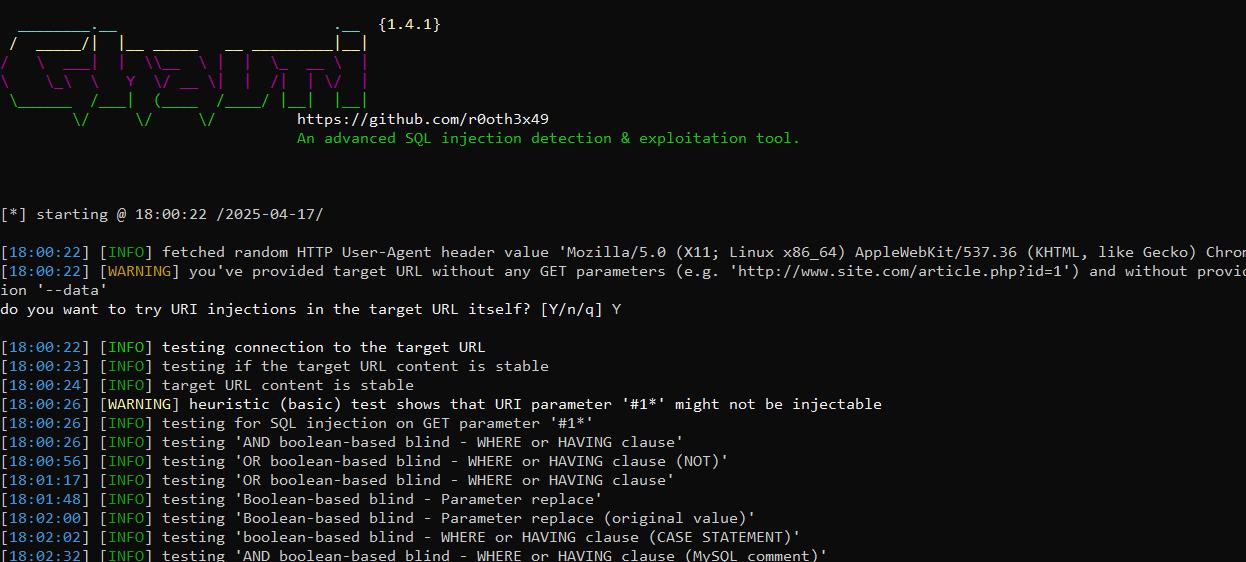 s1n6h/barcha
Barcha is your Swiss‑Army knife for SQL Injection reconnaissance 🔍. Written in Go, it automates: Shodan enumeration of SSL hosts 🕵️♂️ Liveness &…
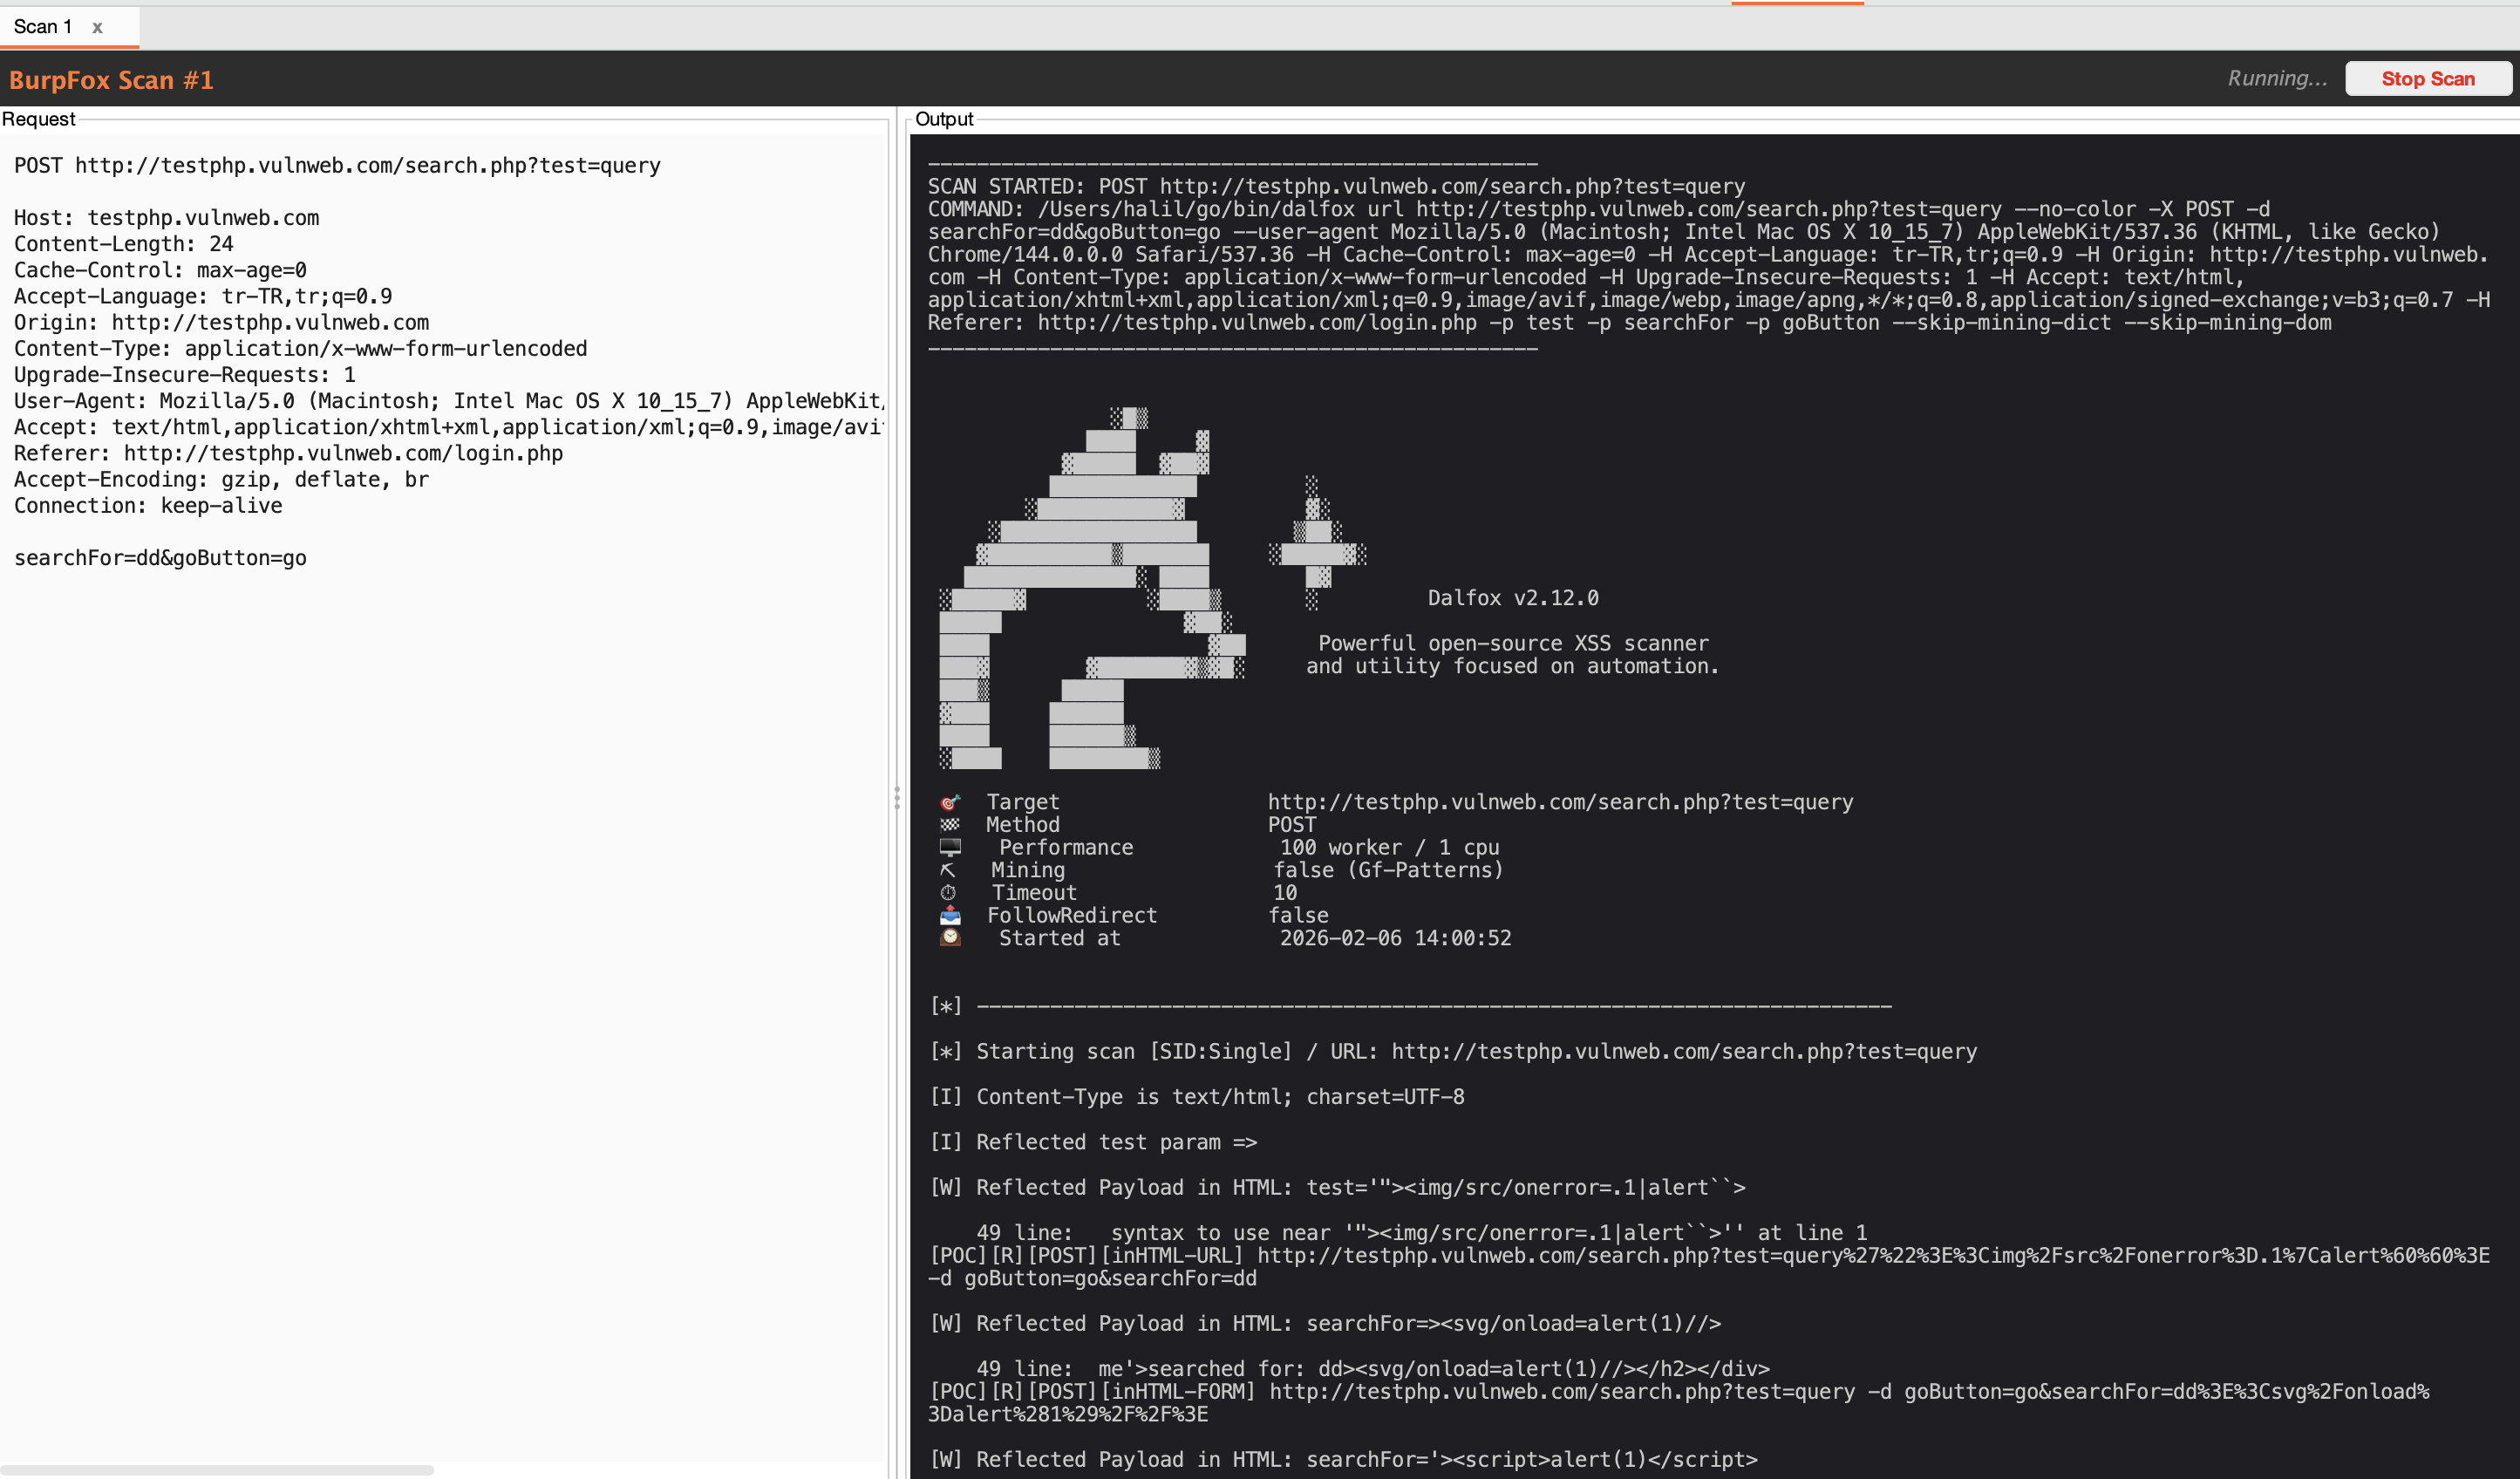 halilkirazkaya/burpfox
A Burp Suite extension that integrates Dalfox XSS scanner directly into your workflow.
 m3ssap0/springbreakvulnerableapp
WARNING: This is a vulnerable application to test the exploit for the Spring Break vulnerability (CVE-2017-8046). Run it at your own risk!
 m3ssap0/wordpress-really-simple-security-authn-bypass-vulnerable-application
WARNING: This is a vulnerable application to test the exploit for the Really Simple Security < 9.1.2 authentication bypass (CVE-2024-10924). Run it…
 logesh-git001/cve-2025-55182
"One crafted HTTP request can compromise your entire server." — React Security Team, Dec 2025
 m3ssap0/wordpress-jetpack-broken-access-control-vulnerable-application
WARNING: This is a vulnerable application to test the exploit for the Jetpack < 13.9.1 broken access control (CVE-2024-9926). Run it at your own risk!