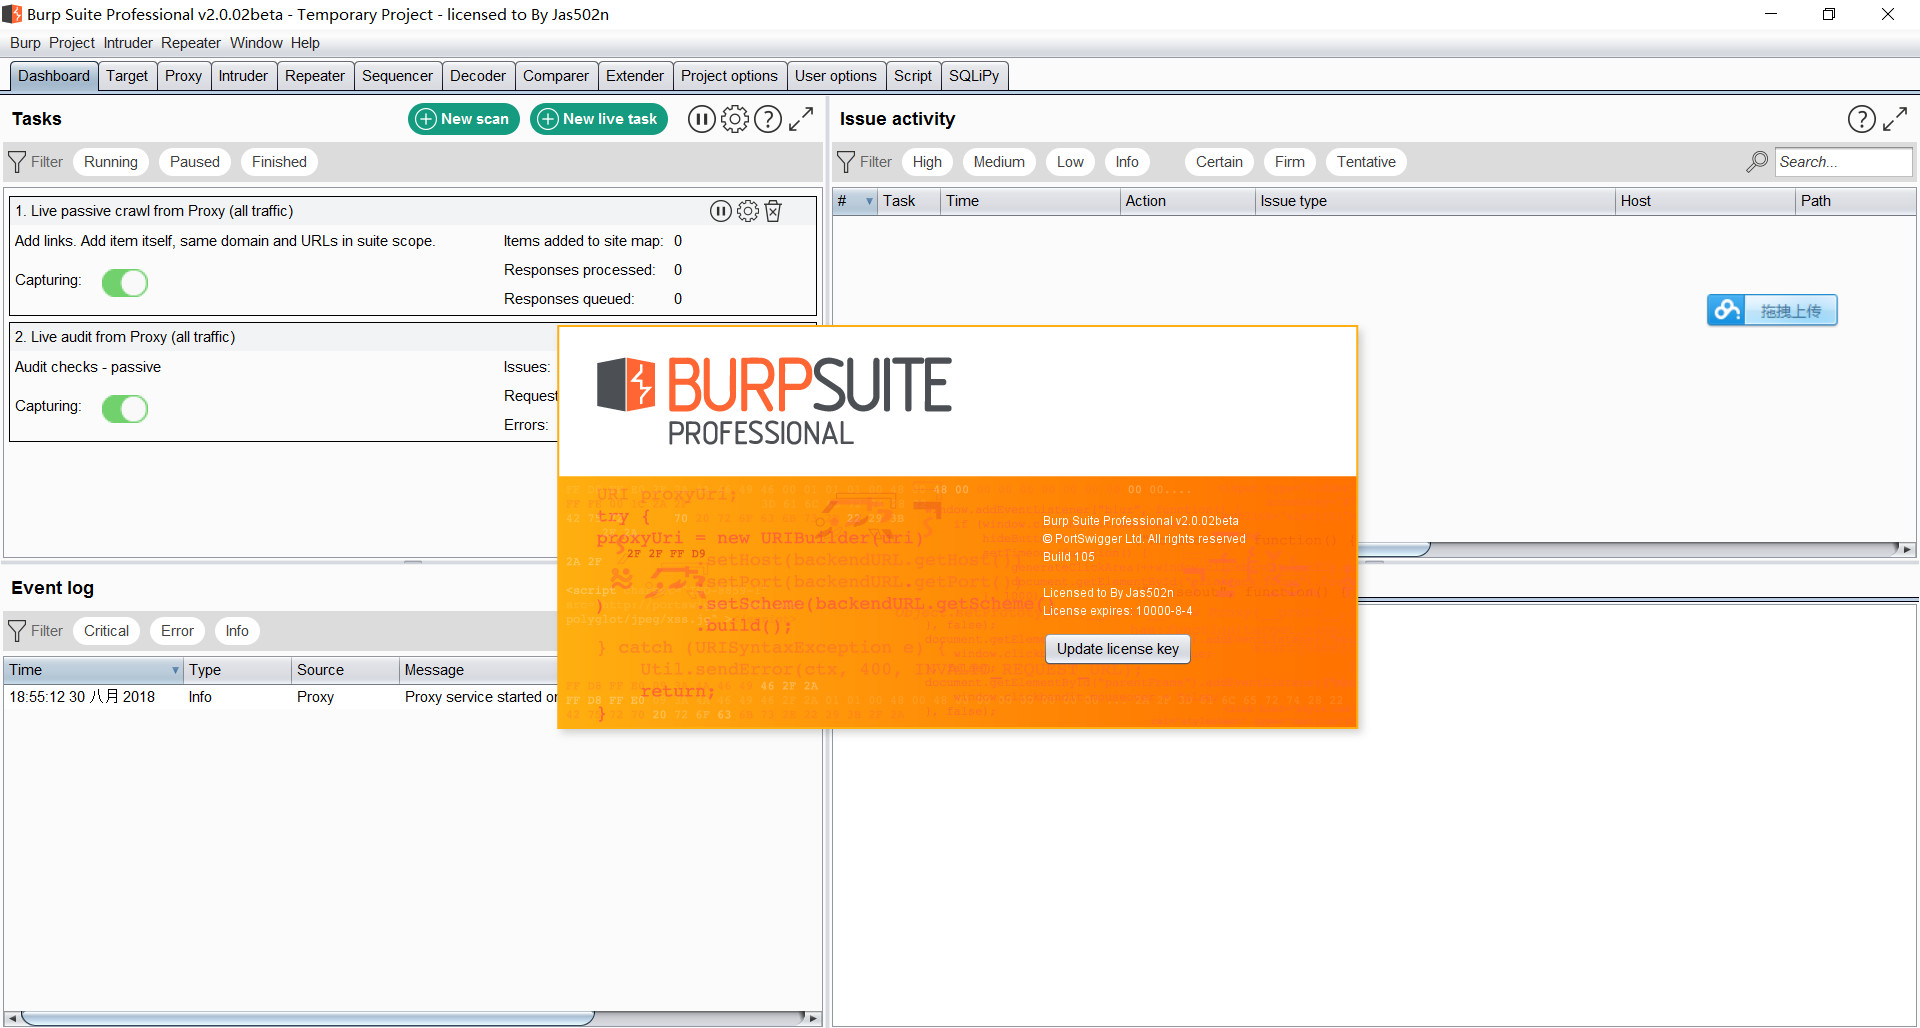
BurpSuite_Pro_v1.7.37

Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…

Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…

Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…

Next generation web scanner

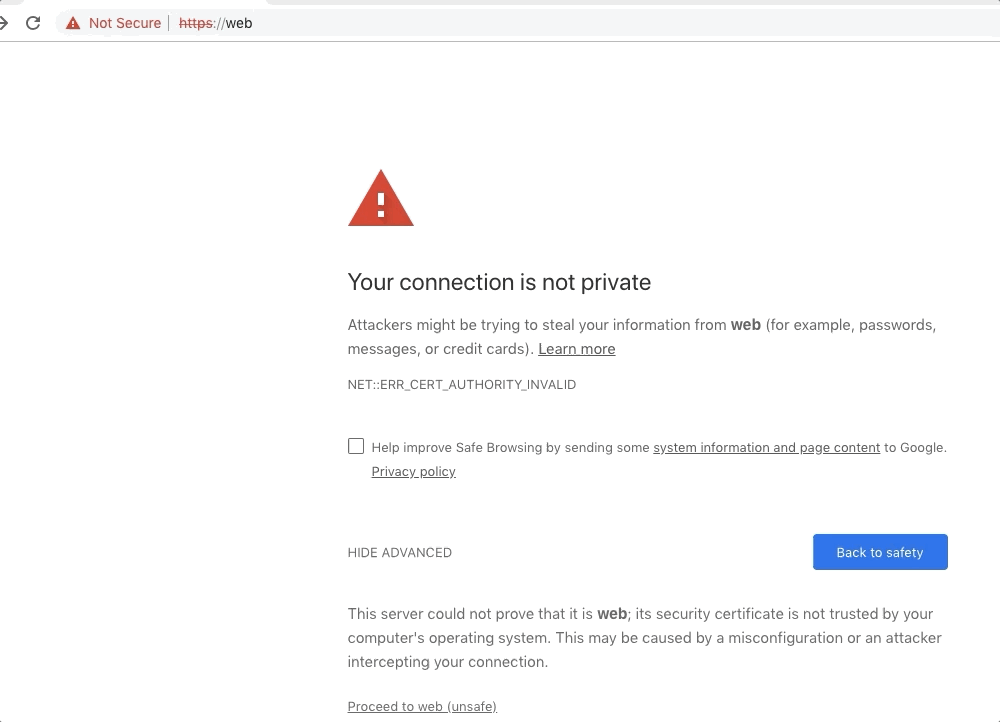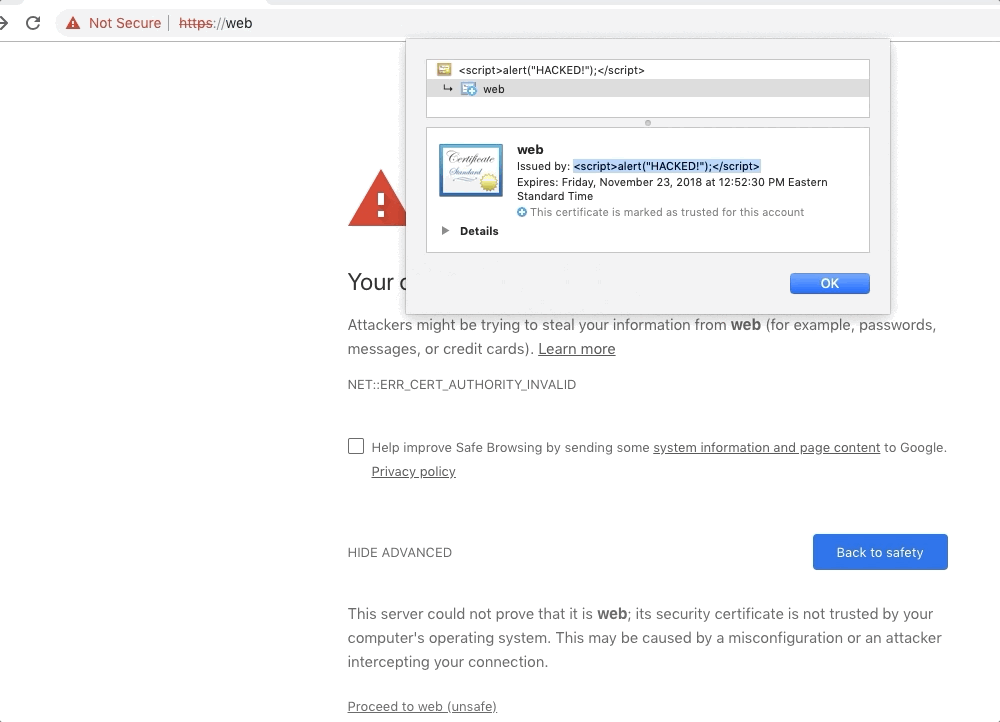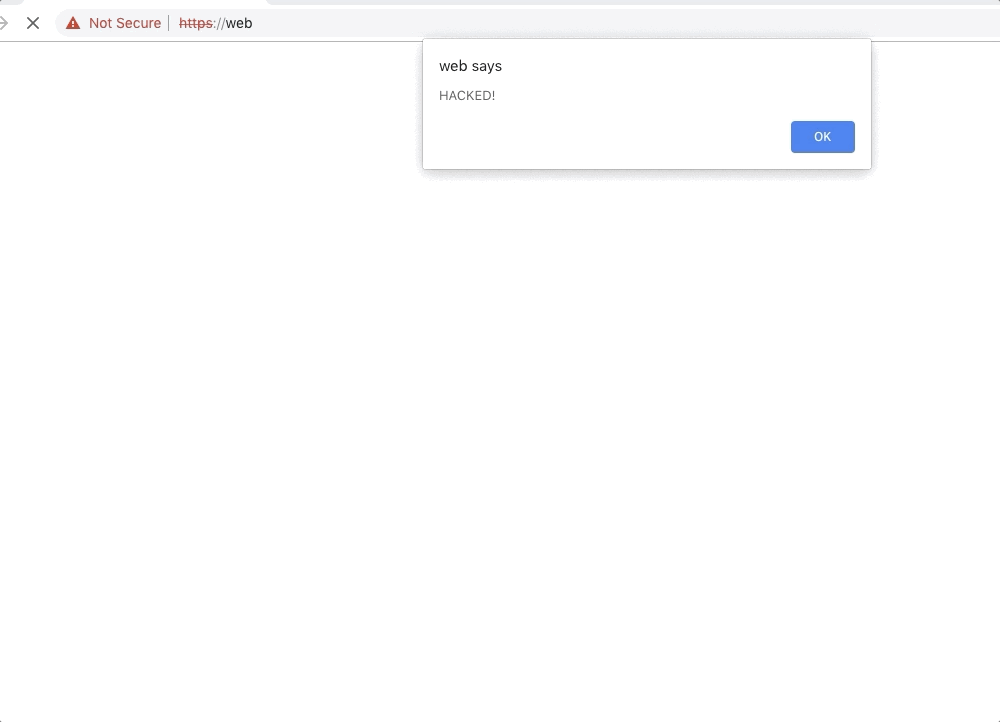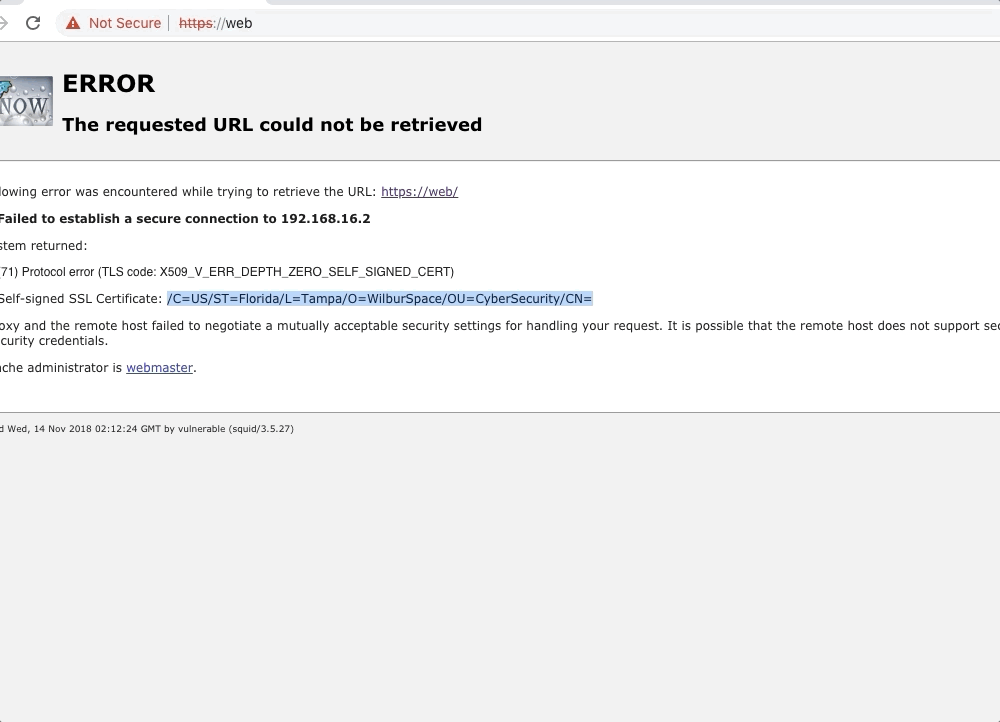
Proof-of-Concept exploit of CVE-2018-19131: Squid Proxy XSS via X.509 Certificate


Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…

Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…

a Damn Vulnerable Serverless Application

An intentionally designed broken web application based on REST API.

TInjA is a CLI tool for testing web pages for template injection vulnerabilities and supports 44 of the most relevant template engines for eight…

GUI Burp Plugin to ease discovering of security holes in web applications

Damn Vulnerable C# Application (API)

Collaborative application security testing between humans and agents via CLI and MCP

The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…

Proof-of-concept exploit for CVE-2015-9251, demonstrating a specific web application vulnerability with minimal code for testing and verification.

XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.

Demonstrates CVE-2026-31431 by poisoning the cache for a target file with attacker-controlled payload bytes, illustrating a web cache poisoning…

Proof-of-concept exploit for CVE-2019-14319, demonstrating a specific vulnerability in a web application for security testing and verification.