

coraza
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
api-securityapi-security-testingdefensive-tools+7
3.7k
corazawaf/corazaGo-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 kkhackinglearning/cve-2025-55184_testing
Python script for Testing CVE-2025-55184
 s_r_e_e_r_a_j/php-reverse-shell
This is a powerful and stealthy PHP reverse shell designed for ethical hacking and penetration testing. It establishes a reliable and quiet…
 andresriancho/w3af
Open-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
 defparam/smuggler
Python-based HTTP request smuggling and desync testing tool that detects CL.TE and TE.CL vulnerabilities using configurable mutation payloads and…
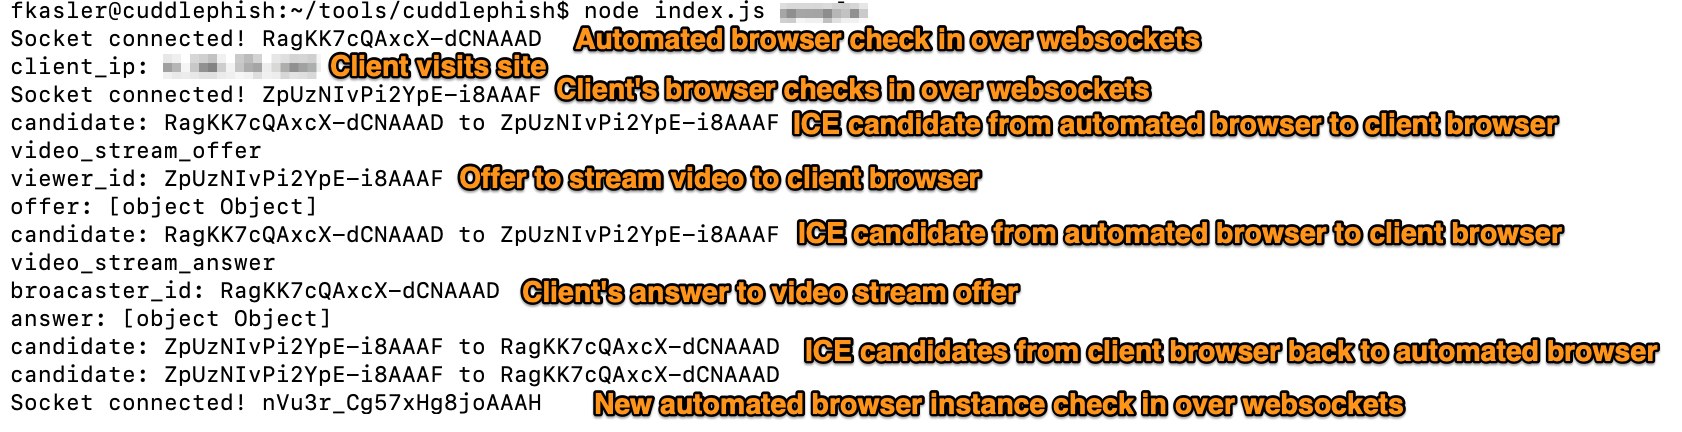 fkasler/cuddlephish
Weaponized Browser-in-the-Middle (BitM) for Penetration Testers
 dzonerzy/gowapt
Go Web Application Penetration Test
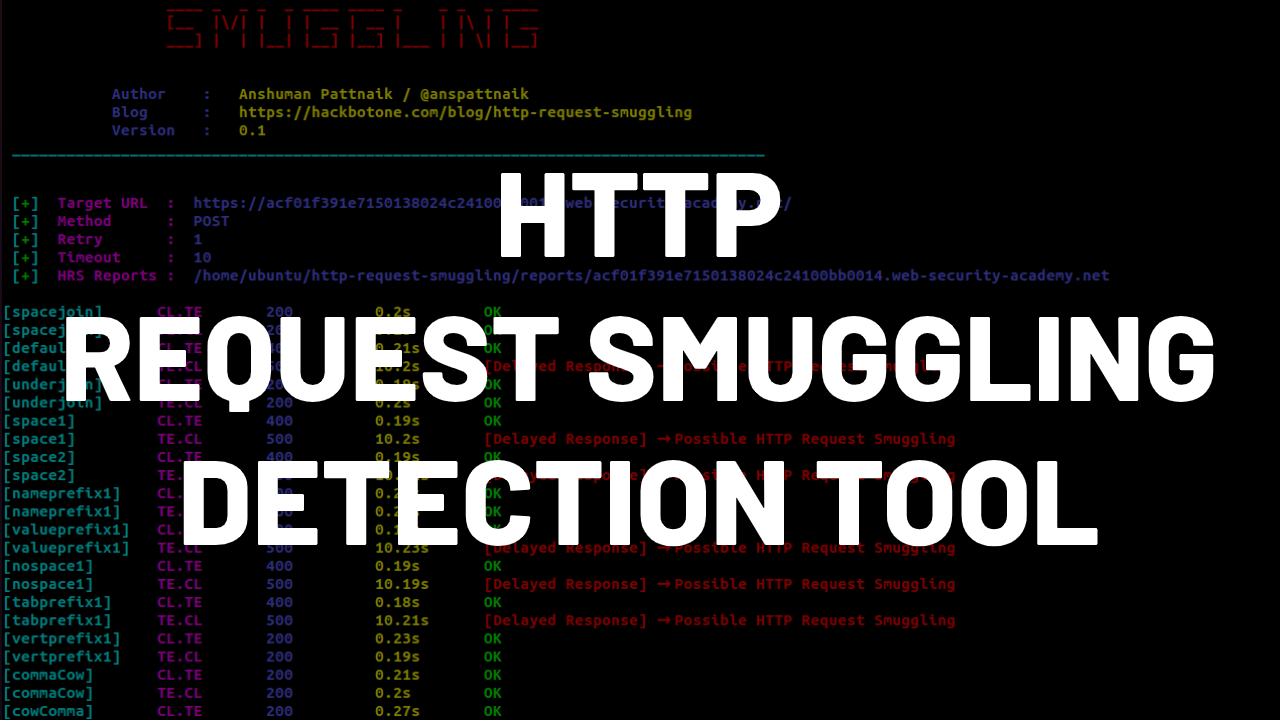 anshumanpattnaik/http-request-smuggling
CLI tool to detect HTTP Request Smuggling vulnerabilities using time-delay analysis with built-in CL.TE and TE.CL payloads for automated security…
 jas502n/cve-2020-14882
Weblogic CVE-2020-14882 unauthorized RCE exploit with patch bypass, command execution, and webshell deployment for penetration testing.
 shadow-workers/shadow-workers
Shadow Workers is a free and open source C2 and proxy designed for penetration testers to help in the exploitation of XSS and malicious Service…
 linhlhq/cve-2019-0604
Proof-of-concept exploit for CVE-2019-0604, a remote code execution vulnerability in Microsoft SharePoint. Provides a working implementation for…
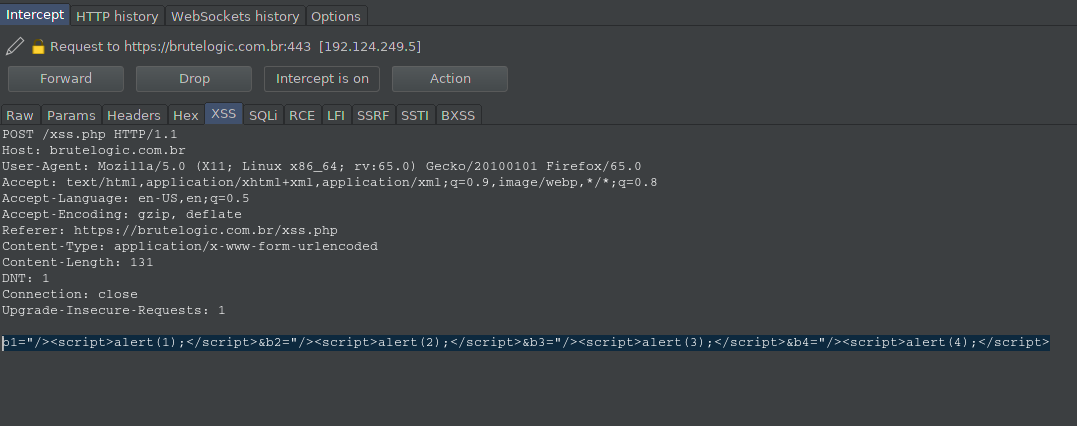 p3n73st3r/ghazi
Ghazi is a BurpSuite Plugins For Testing various PayLoads Like "XSS,SQLi,SSTI,SSRF,RCE and LFI" through Different tabs , Where Each Tab Will Replace…
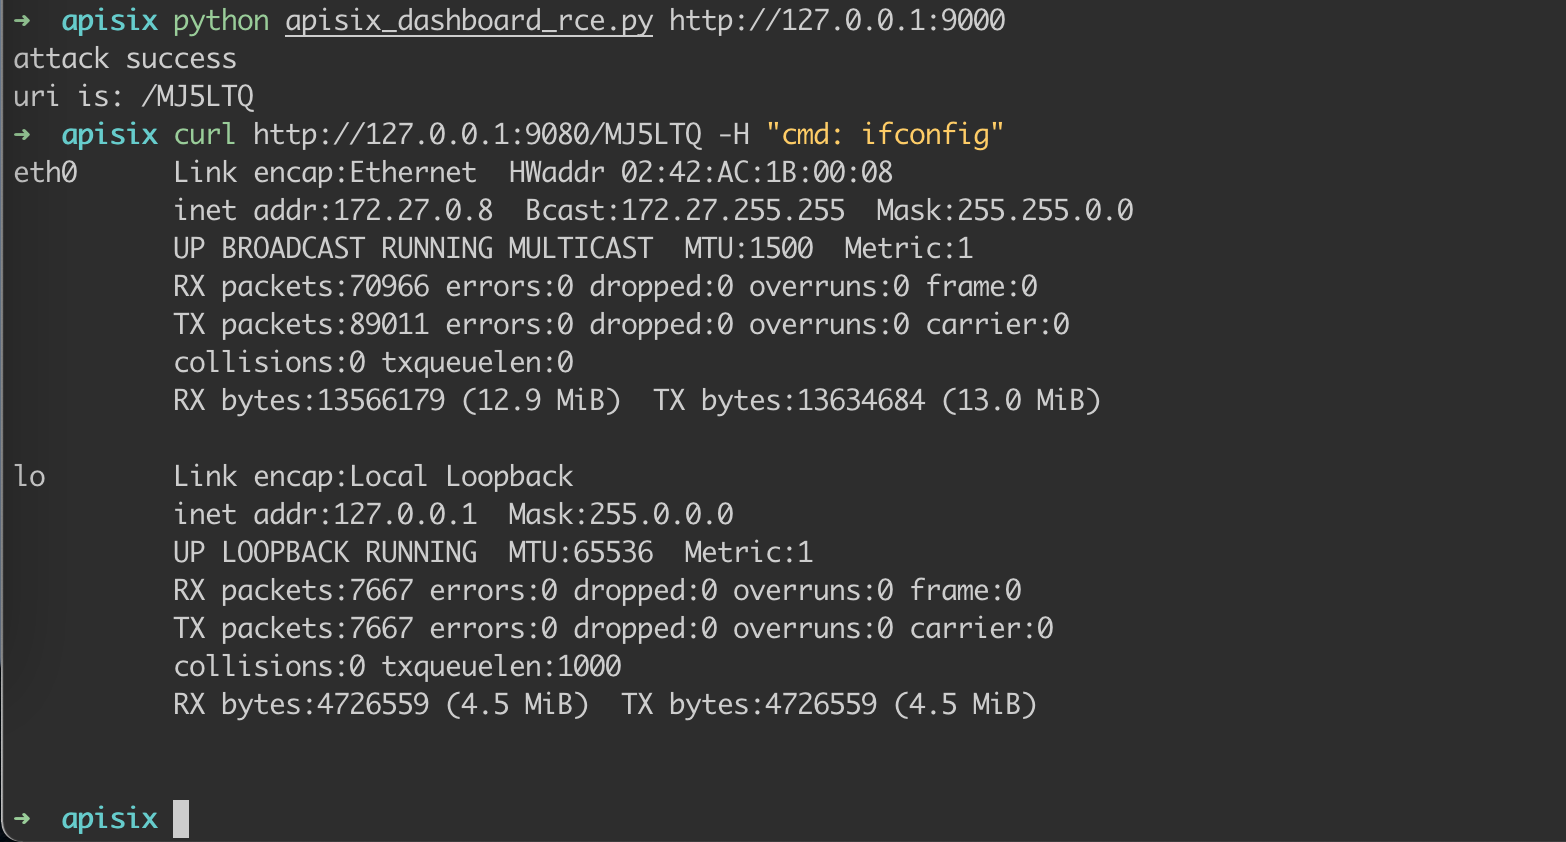 wuppp/cve-2021-45232-exp
Exploit for CVE-2021-45232 targeting Apache APISIX Dashboard remote code execution vulnerability. Provides proof-of-concept for security testing and…
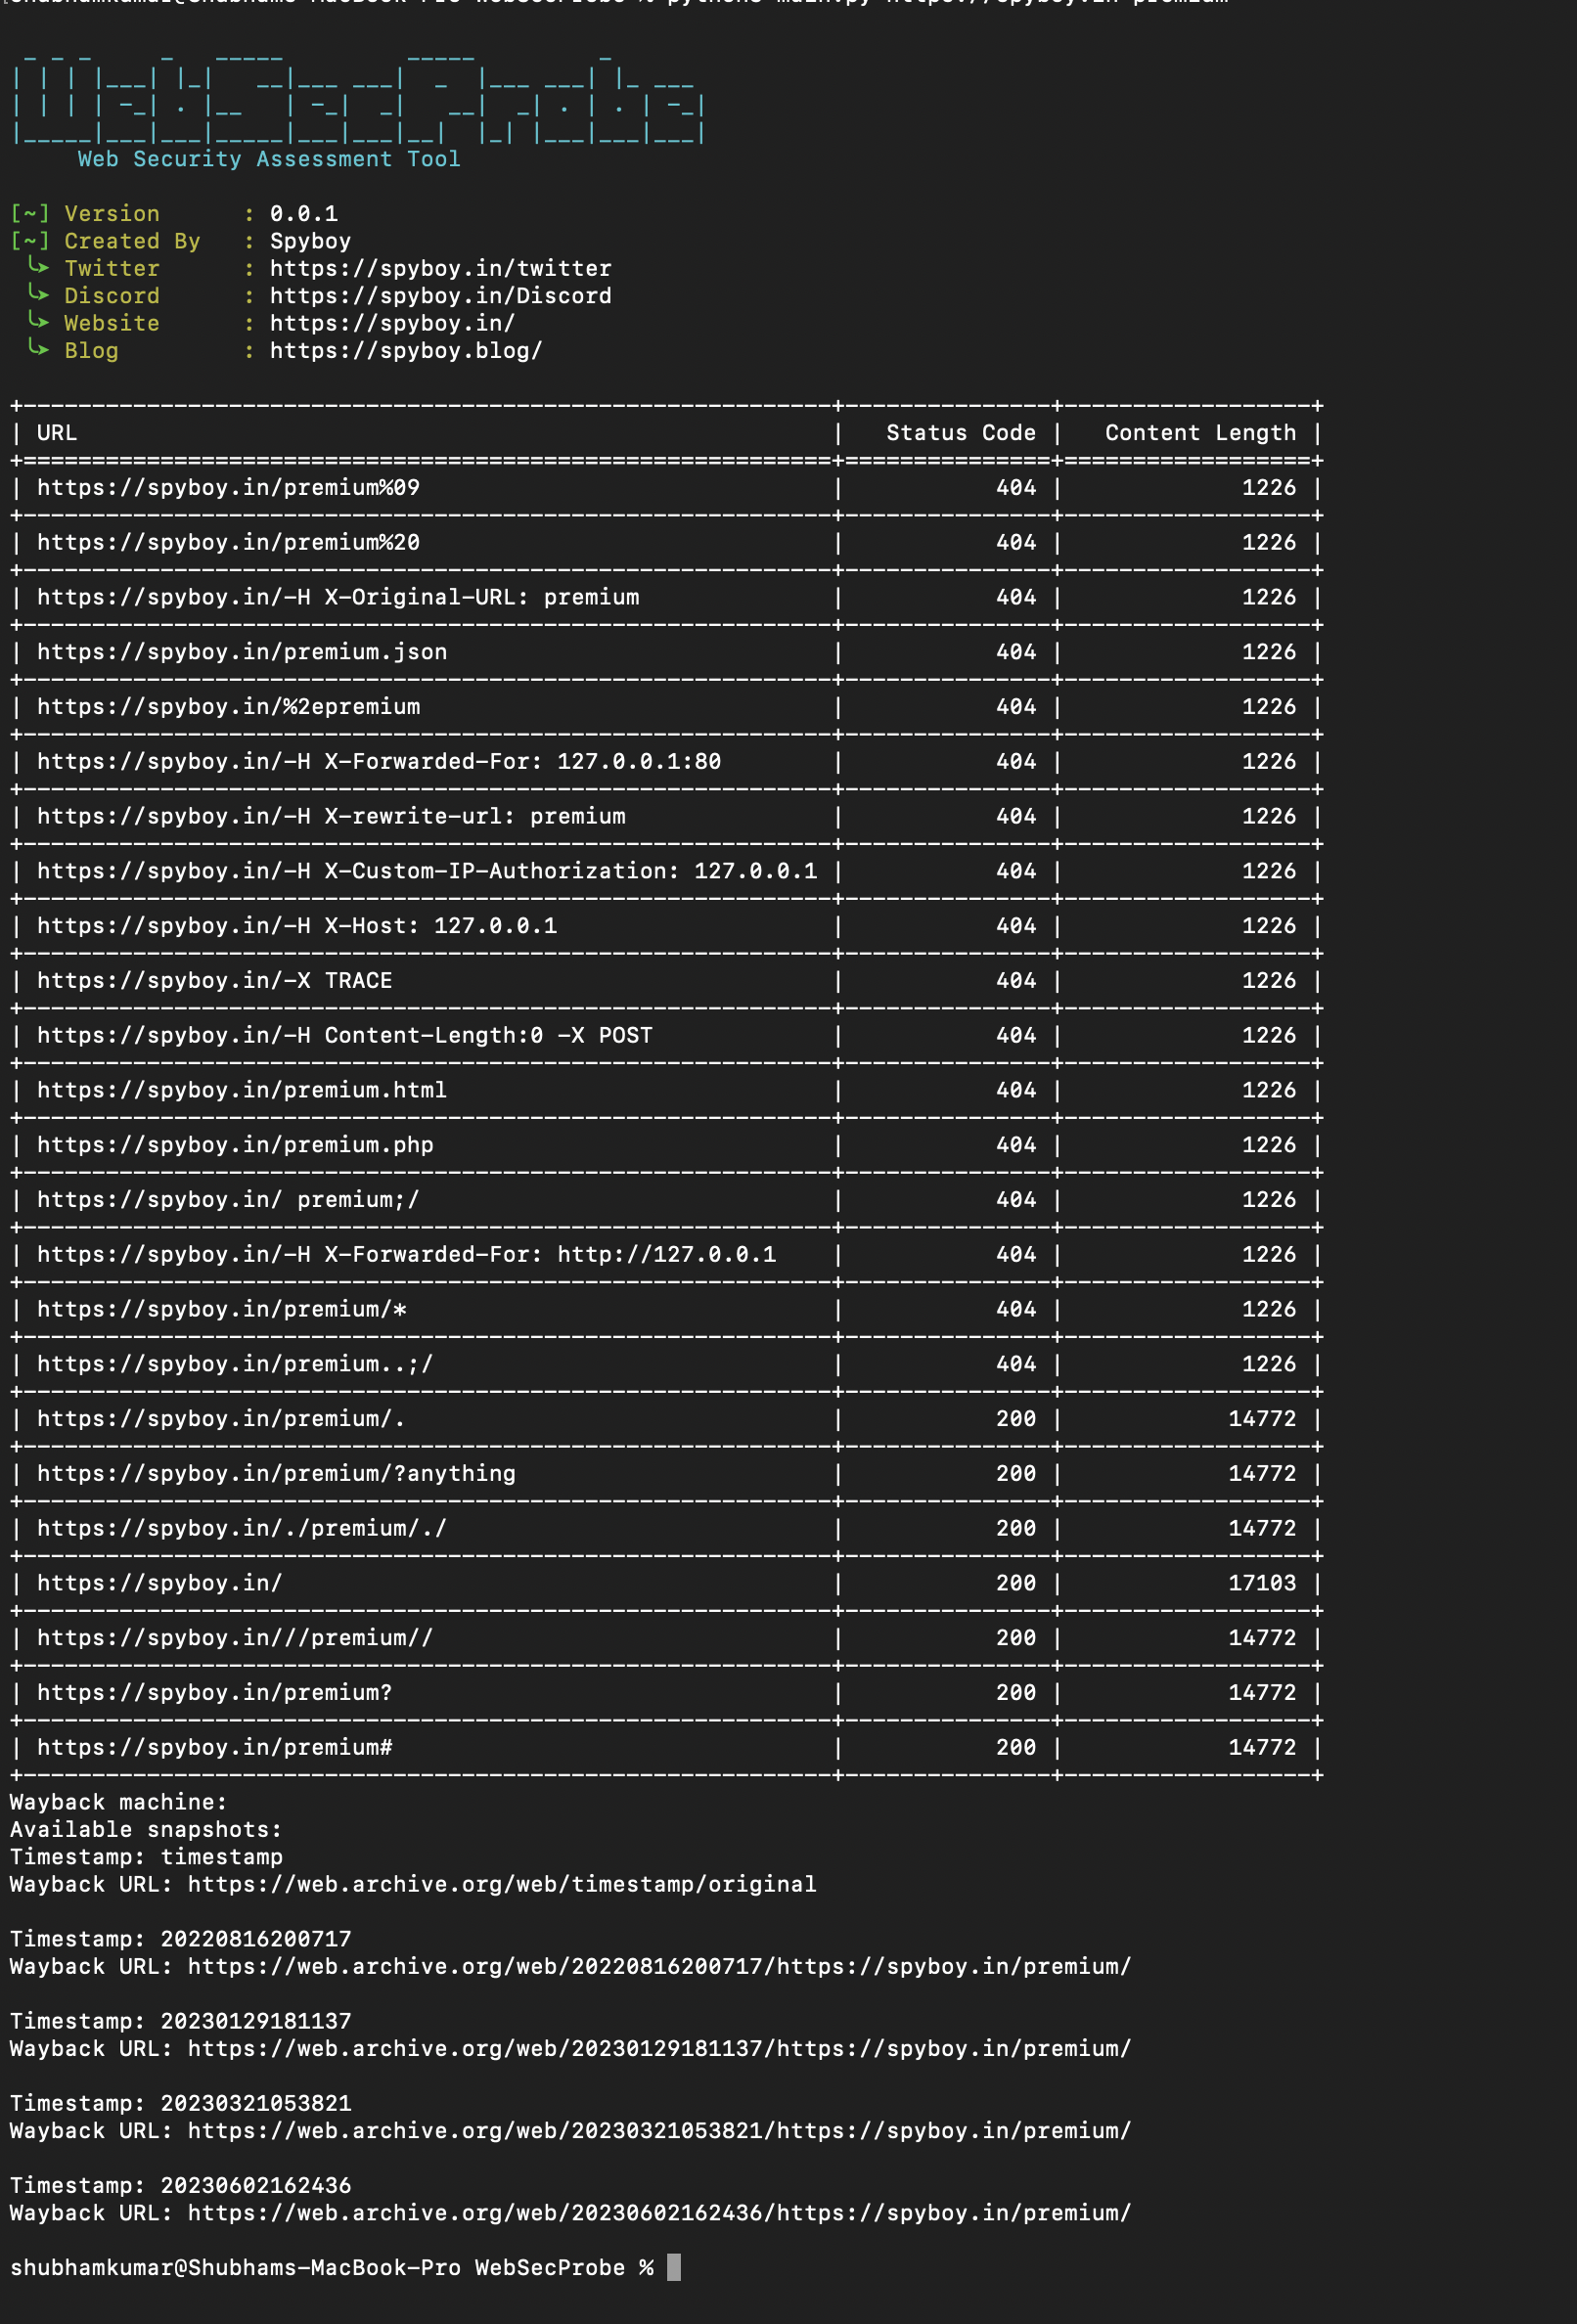 spyboy-productions/websecprobe
Security testing tool for analyzing HTTP 403 responses and identifying access control misconfigurations in web applications.
 epotseluevskaya/aspx_webshell_coffloader
ASPX web shell with COFF loader for executing Beacon Object Files (BOFs) on target servers via a semi-interactive Python client, designed for…
 dipakpanchal05/cve-2022-23808
Proof-of-concept exploit for CVE-2022-23808, a stored XSS vulnerability in phpMyAdmin 5.1.1 setup script, with payload and reproduction steps for…
 mistymntncop/cve-2025-5419
Proof-of-concept exploit for CVE-2025-5419, demonstrating a critical vulnerability with a JavaScript-based implementation for security testing and…
 exploits-forsale/cve-2024-21345
Proof-of-concept exploit for CVE-2024-21345, demonstrating a specific vulnerability with functional code for security testing and validation.