
Archived
CVE-2023-31445-Unprivileged-Information-Disclosure
 dodge-mptc/cve-2023-31445-unprivileged-information-disclosure
Repository contains description for CVE-2023-31445
information-gatheringosintpenetration-testing+3
dodge-mptc/cve-2023-31445-unprivileged-information-disclosureRepository contains description for CVE-2023-31445
 paulsec/hqlmap
(Deprecated) HQLmap, Automatic tool to exploit HQL injections
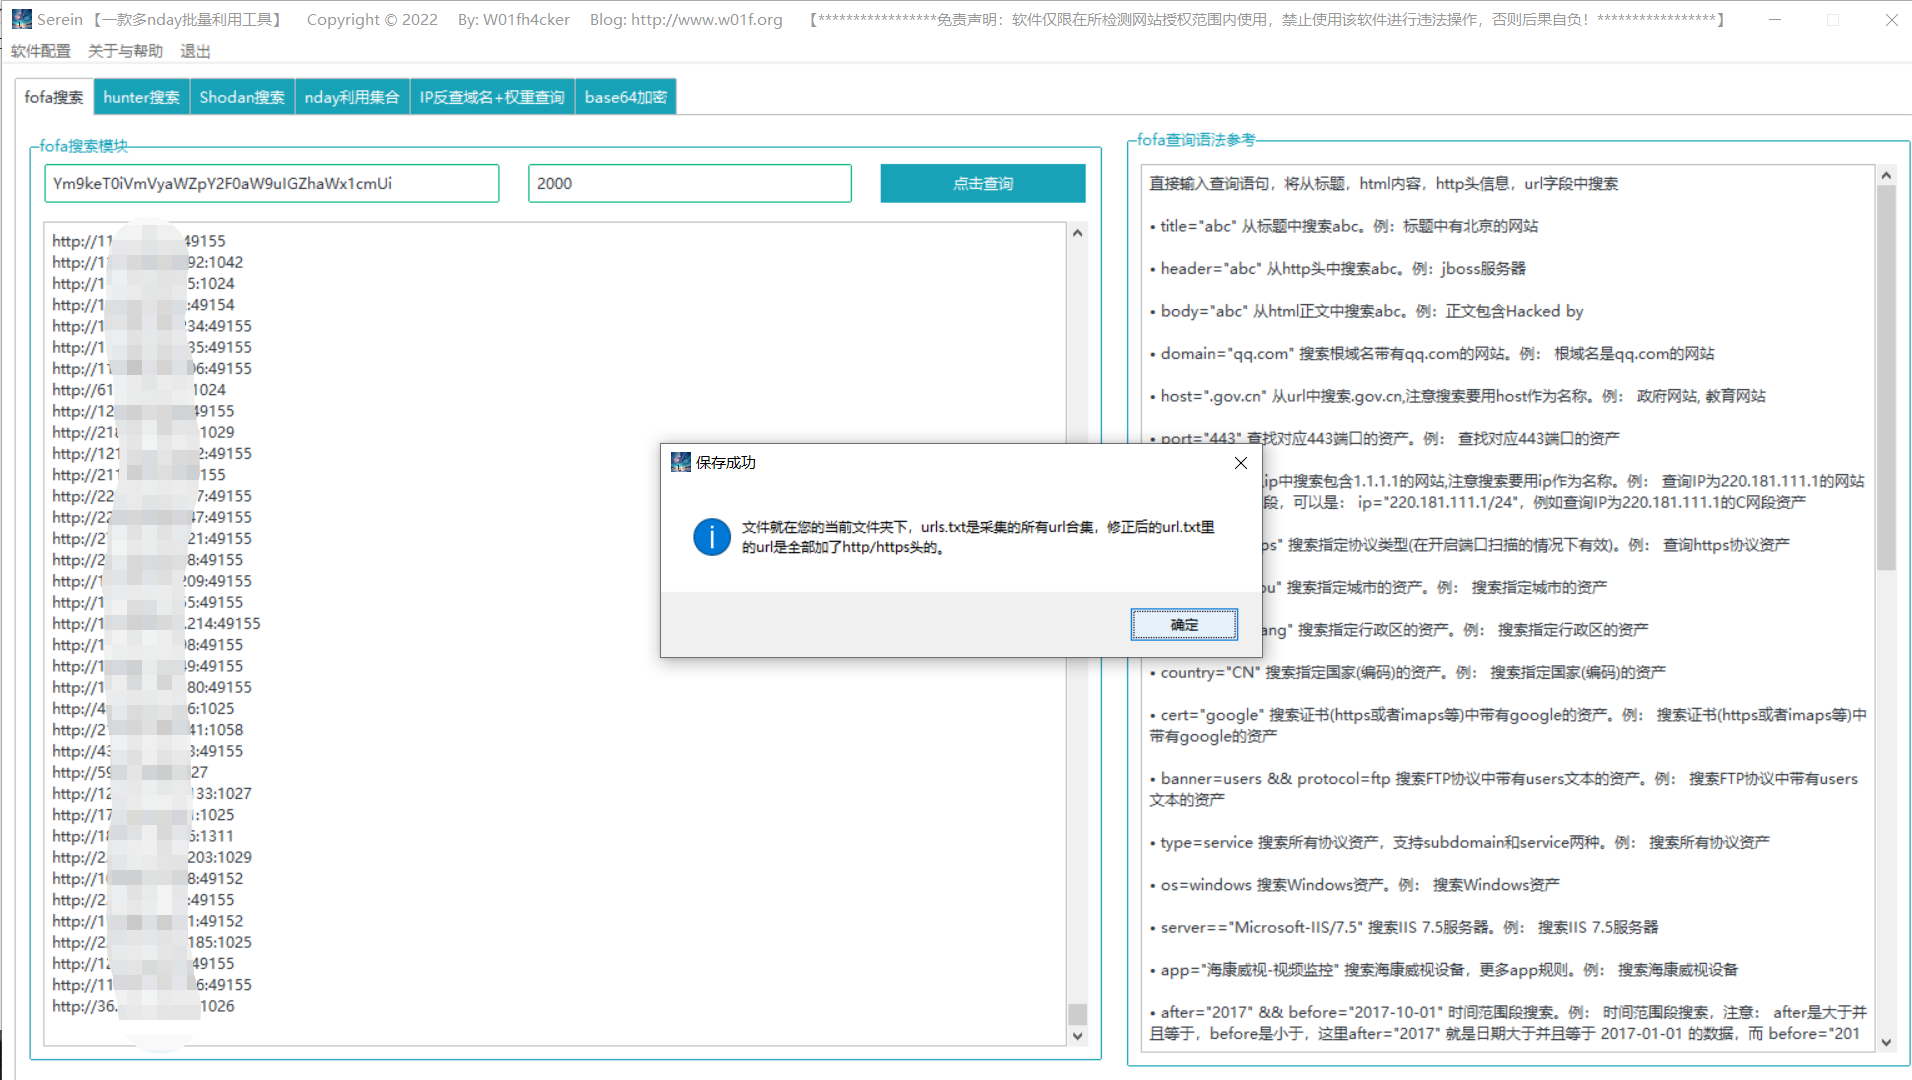 w01fh4cker/serein
【懒人神器】一款图形化、批量采集url、批量对采集的url进行各种nday检测的工具。可用于src挖掘、cnvd挖掘、0day利用、打造自己的武器库等场景。可以批量利用Actively Exploited Atlassian Confluence 0Day…
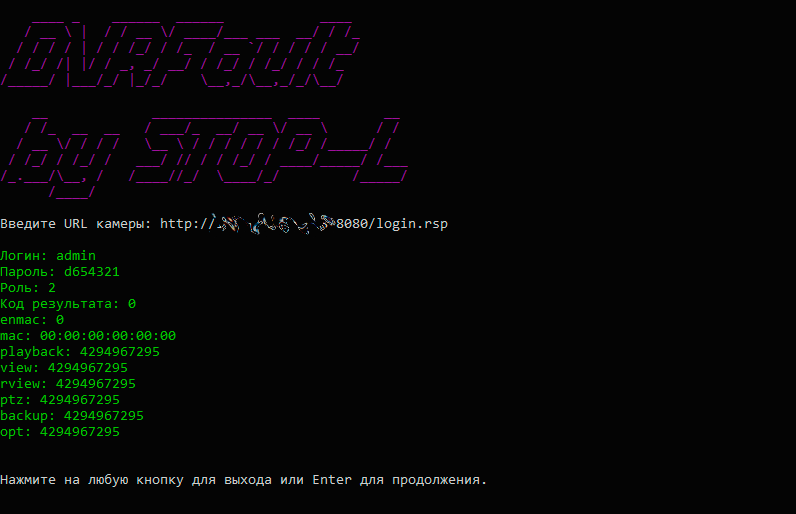 st0pl/dvrfaultnet
.NET console application that exploits CVE-2018-9995 vulnerability
 bytereaper77/cve-2025-5964-
C PoC language for emulating path traversal vulnerability (CVE-2025-5964) in M-Files25.6.14925.0
 kavishgr/xmlrpc-bruteforcer
An XMLRPC brute forcer targeting Wordpress written in Python 3. (DISCONTINUED)
 and0x00/cve-2021-32789
💣 Wordpress WooCommerce users dump exploit.
 awnumar/blind-sql-bitshifting
A blind SQL injection module that uses bitshfting to calculate characters.
 0x5ecf4ult/cve-2020-3452
CVE-2020-3452 exploit
 bytereaper77/cve-2025-6907
a standalone C-based SQL Injection exploit targeting the CVE‑2025‑6907 vulnerability in the CODE_PROJECT service.
 bouquets-ai/cve-2022-22965-guitools
spring-core单个图形化利用工具,CVE-2022-22965及修复方案已出
 bytereaper77/cve-2025-11077
Exploit blind SQL Injection in (Online Learning Management System)
 bytereaper77/cve-2025-6082
Proof‑of‑Concept exploits the Full Path Disclosure bug in the “Birth Chart Compatibility” WordPress plugin (<=v2.0)
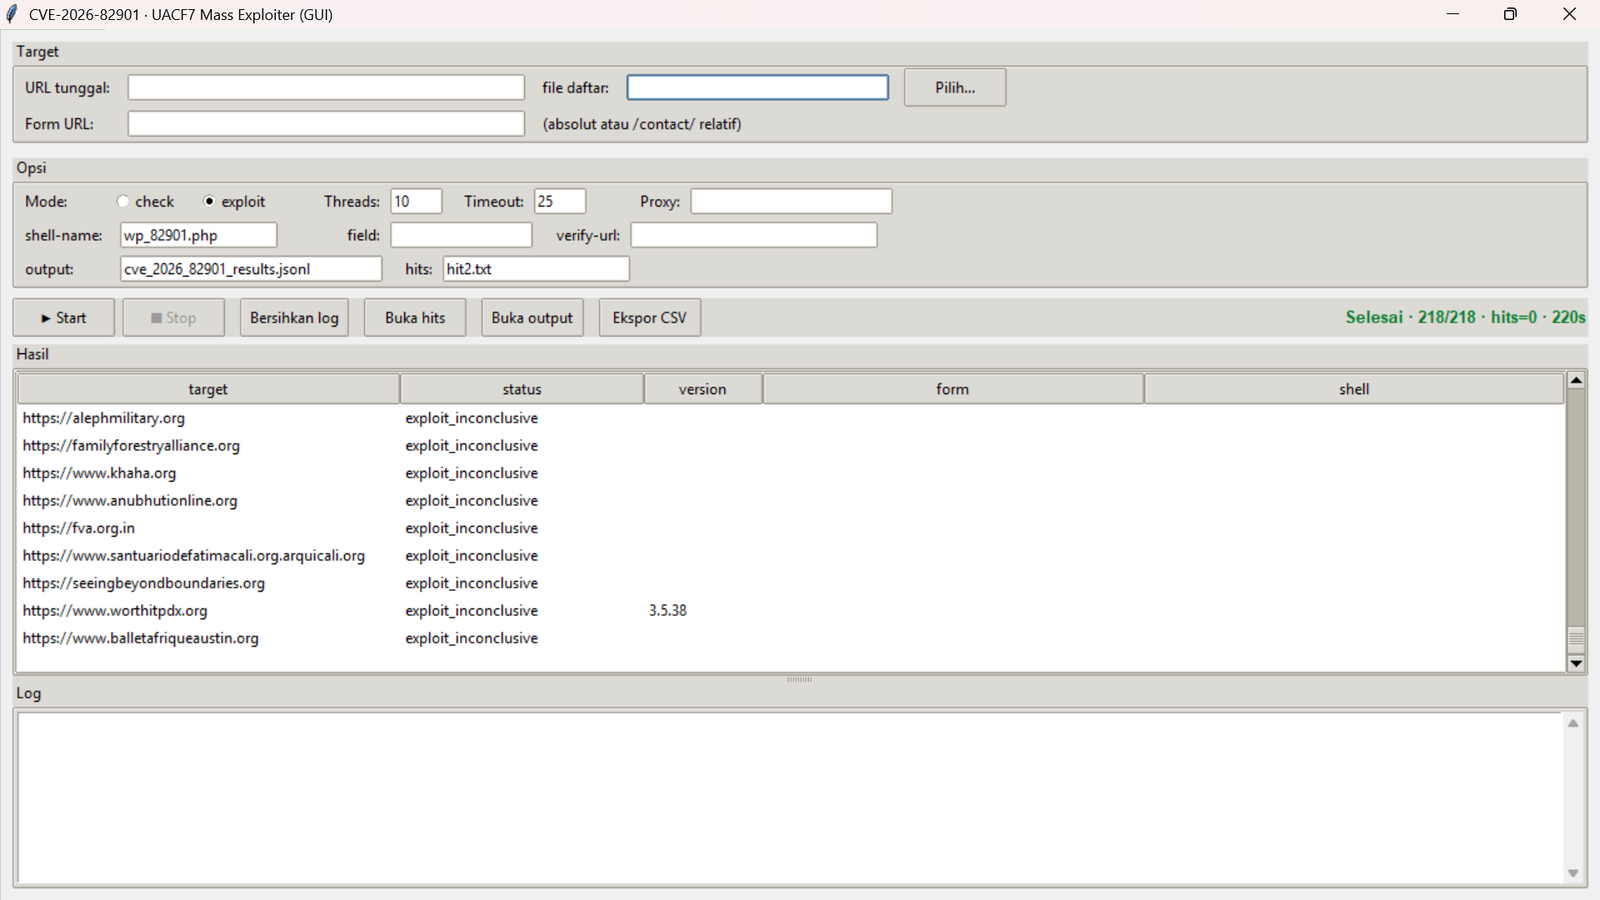 tonydelouvre/cve-2026-82901
GUI and CLI mass scanner and exploiter for CVE-2026-82901, an unauthenticated arbitrary file upload in the Ultra Addons for Contact Form 7 WordPress…
 wuyou6956-glitch/cve-2026-85706
Python PoC and writeup for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE via Workhorse path-encoding bypass on repository…
 wayang1337/cve-2026-85097
Bricksforge <= 3.1.8.9 Unauthenticated Arbitrary File Upload
 murrez/cve-2026-82384
Python PoC for CVE-2026-82384: detects and exploits unauthenticated XML-RPC Java deserialization in Apache Roller 6.1.5 via ysoserial payloads, with…
 murrez/cve-2026-97163
Python PoC for CVE-2026-97163: fingerprints Joomla UP plugin versions and probes com_ajax install triggers for unauthenticated remote action…