
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
86 results
CVE-2026-85246 preview

CVE-2026-85246

GitHuboscerd/cve-2026-85246

Runnable Spring Boot reproducer for CVE-2026-85246, demonstrating camel-mina consumer exception disclosure over the socket and verifying the…
defensive-toolseducationexploitation+3
12 days ago
CVE-2026-73314 preview

CVE-2026-73314

GitHubbombobombone/cve-2026-73314

Proof-of-concept exploit for CVE-2026-73314, a PayPal REST webhook signature verification bypass in XenForo before 2.3.13, allowing unauthorized…
exploitationvulnerability-analysisweb-application-exploitation+1
1 month ago
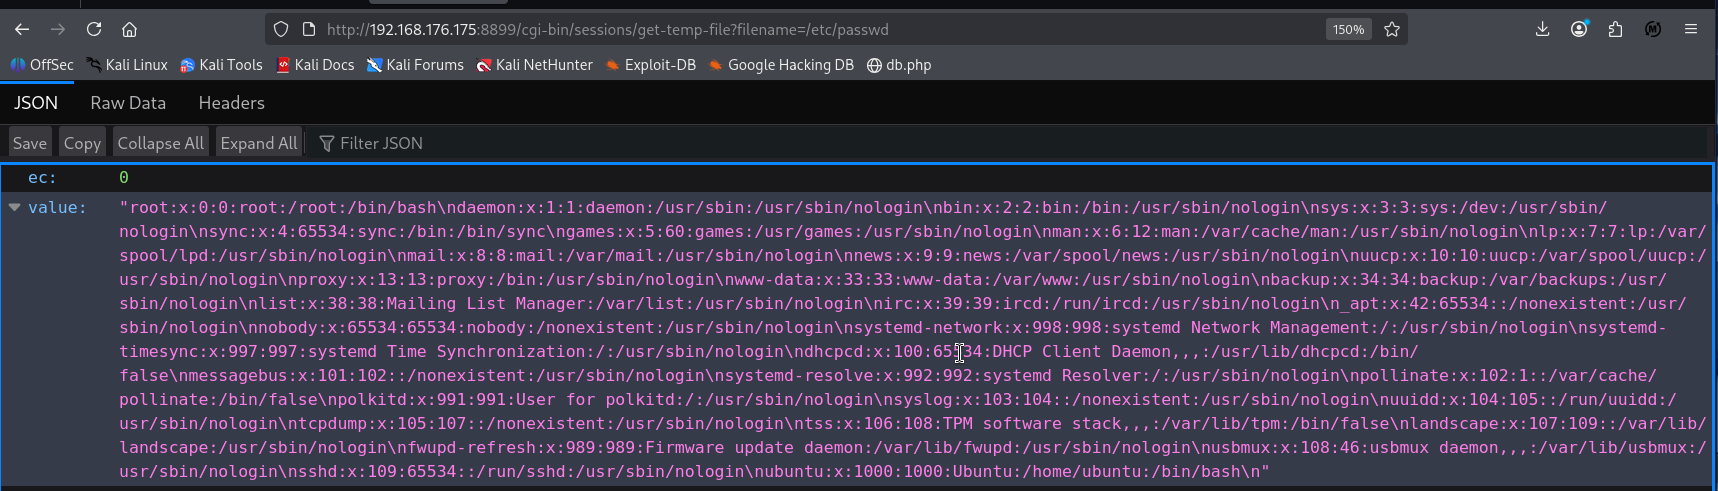
CVE-2025-5880 preview

CVE-2025-5880

GitHubac8999/cve-2025-5880

PoC for a Path Traversal vulnerability in Whistle v2.9.98 via the /cgi-bin/sessions/get-temp-file endpoint. (Unpatched)
exploitationvulnerability-analysisweb-application-exploitation
2 months ago
CVE-2026-66066 preview

CVE-2026-66066

GitHubhackspeak/cve-2026-66066

CVE-2026-66066 (KindaRails2Shell) PoC - Rails Active Storage/libvips arbitrary file read to RCE; for authorized security testing
exploitationinformation-gatheringpenetration-testing+5
42 months ago
CVE-2026-66066 preview

CVE-2026-66066

GitHubshinthink/cve-2026-66066

CVE-2026-66066 — KindaRails2Shell: Rails Active Storage/libvips Arbitrary File Read → RCE. MATLAB/HDF5 dual-identity file → SECRET_KEY_BASE theft →…
exploitationpenetration-testingreconnaissance+3
12 months ago
CVE-2026-11114-Node.js-vm-Sandbox-Escape-via-Proxy preview

CVE-2026-11114-Node.js-vm-Sandbox-Escape-via-Proxy

GitHubgeorge0papasotiriou/cve-2026-11114-node.js-vm-sandbox-escape-via-proxy

PoC exploit for CVE-2026-11114 demonstrating Node.js vm sandbox escape via Proxy to achieve remote code execution against a vulnerable HTTP /eval…
exploitationvulnerability-analysisweb-application-exploitation
2 months ago
KindaRails2Shell preview

KindaRails2Shell

GitHub0xsha/kindarails2shell

Single-file PoC for Rails CVE-2026-66066: arbitrary file read, secret recovery, threaded scanning, and conditional RCE via signed image variations.
exploitationlabs-practicepayload-development+4
53 months ago
CVE-2026-66066-POC preview

CVE-2026-66066-POC

GitHubzer0sumgam3/cve-2026-66066-poc

PoC for CVE-2026-66066 in Ruby on Rails
educationexploitationlabs-practice+3
233 months ago
CVE-2026-67184-Unauthenticated-NULL-Pointer-Dereference-Crashes-the-Server-TinyWeb- preview

CVE-2026-67184-Unauthenticated-NULL-Pointer-Dereference-Crashes-the-Server-TinyWeb-

GitHubtheopaid/cve-2026-67184-unauthenticated-null-pointer-dereference-crashes-the-server-tinyweb-

Security Advisory: Unauthenticated NULL Pointer Dereference Crashes the Server (TinyWeb)
educationexploitationpapers-research+2
13 months ago
CVE-2026-53913 preview

CVE-2026-53913

GitHuboscerd/cve-2026-53913

PoC reproducer for CVE-2026-53913 (Apache Camel camel-keycloak): KeycloakSecurityPolicy fails open in the Basic Setup — with no required…
authenticationcode-analysisexploitation+3
13 months ago
cve-2019-5420-POC preview

cve-2019-5420-POC

GitHubwildwestcybersecurity/cve-2019-5420-poc

cve-2019-5420 POC simple ruby script
educationexploitationpayload-generation+3
13 months ago
CVE-2019-12086 preview

CVE-2019-12086

GitHubal1ex/cve-2019-12086

jackson unserialize
database-securityexploitationpayload-generation+2
14 months ago
CVE-2026-5203 preview

CVE-2026-5203

GitHubcaginkyr/cve-2026-5203

Exploit for CVE-2026-5203 in CMS Made Simple, leveraging path traversal and arbitrary file upload to achieve remote code execution with an…
exploitationpayload-generationpenetration-testing+2
5 months ago
CVE-2026-23918-Apache-HTTP-Server-DoubleFree-PoC preview

CVE-2026-23918-Apache-HTTP-Server-DoubleFree-PoC

GitHubcyfare/cve-2026-23918-apache-http-server-doublefree-poc

Proof-of-concept exploit for CVE-2026-23918, a double-free vulnerability in Apache HTTP Server, demonstrating remote crash via crafted requests.
exploitationpenetration-testingvulnerability-analysis+2
5 months ago
cve-2026-32699-facturascripts-nick-bypass preview

cve-2026-32699-facturascripts-nick-bypass

GitHubturkios/cve-2026-32699-facturascripts-nick-bypass

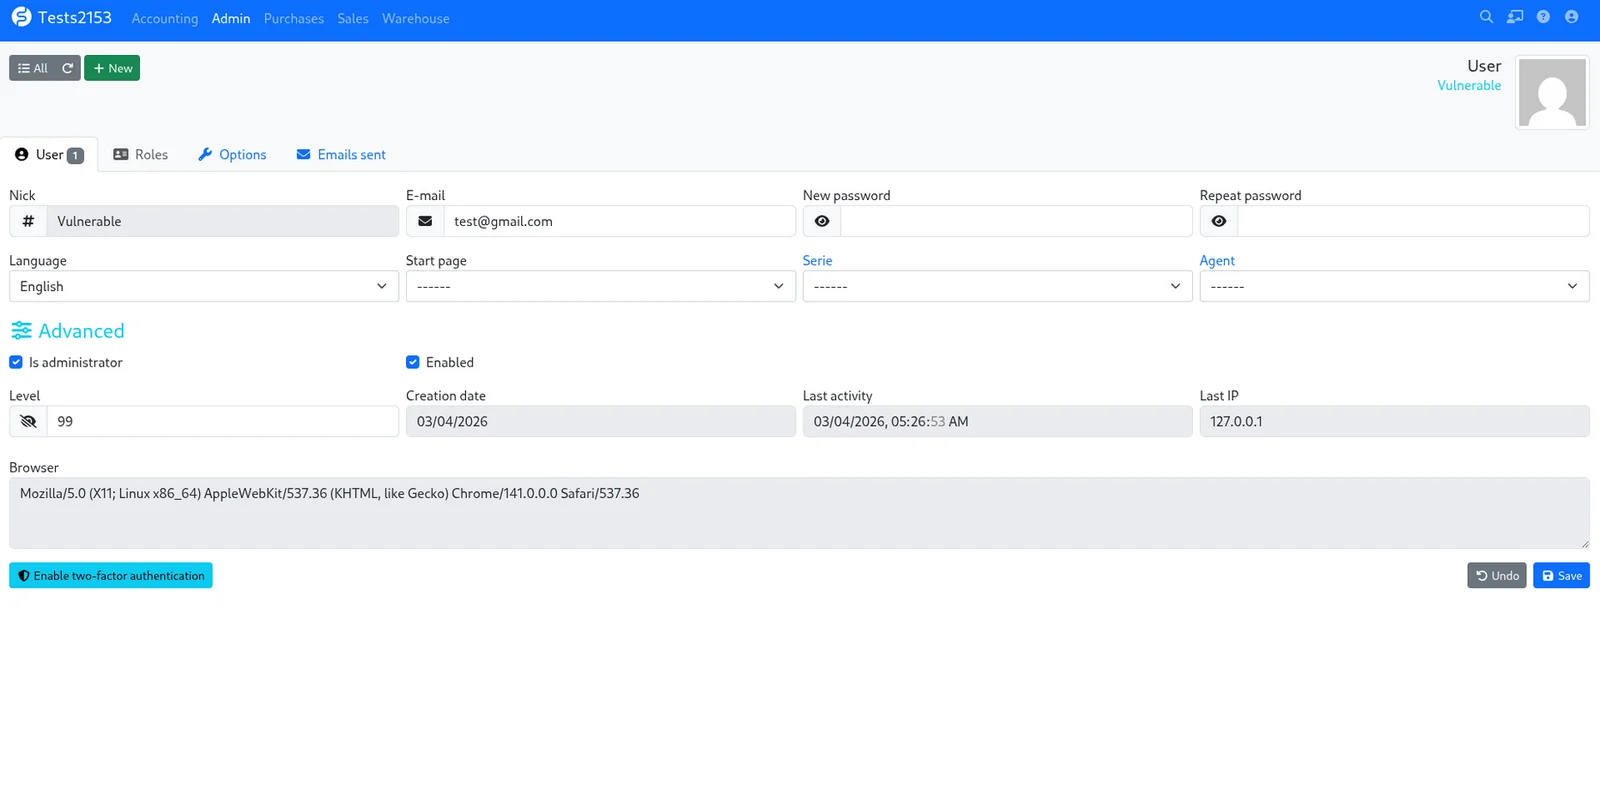
Broken Access Control in FacturaScripts EditUser controller allows authenticated users to rename any account (including admin) by modifying the…
authentication-authorizationexploitationpenetration-testing+3
6 months ago
bitbucket-test preview

bitbucket-test

GitHubjohangabrielson/bitbucket-test

Investigating CVE-2022-36804
educationexploitationlabs-practice+3
6 months ago
Alternative-Approach-Reverse-Shell-Callback-Test-InvokeAI-RCE preview

Alternative-Approach-Reverse-Shell-Callback-Test-InvokeAI-RCE

GitHublu3ky13/alternative-approach-reverse-shell-callback-test-invokeai-rce

This repository contains alternative payload approaches for the InvokeAI RCE vulnerability (CVE-2024-12029) when SSH key injection fails. The…
command-and-controleducationexploitation+5
6 months ago
CVE-2026-34486 preview

CVE-2026-34486

GitHub404-src/cve-2026-34486

Exploit for Apache Tomcat EncryptInterceptor bypass leading to unauthenticated RCE via Java deserialization on port 4000. Includes lab setup,…

educationexploitationpenetration-testing+3
106 months ago
Previous12345Next