

G0BurpSQLmaPI
 nu11secur1ty/g0burpsqlmapi
CLI tool for generating SQL injection PoC requests, automating sqlmap attacks, and managing modular exploit scripts with interactive menu and…
exploitationpayload-generationpenetration-testing+2
3
nu11secur1ty/g0burpsqlmapiCLI tool for generating SQL injection PoC requests, automating sqlmap attacks, and managing modular exploit scripts with interactive menu and…
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 abraxas/cve-2026-82226
Proof-of-concept and lab for CVE-2026-82226, an unauthenticated PHP object injection in Tickera <= 3.6.0.2 via POST /cart/, with Docker reproduction…
 abraxas/cve-2026-15583
Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…
 watchtowrlabs/watchtowr-vs-citrix-netscaler-cve-2026-88772
Detection artifact generator for Citrix NetScaler CVE-2026-88772 that builds a DTLS pre-auth buffer overflow payload to verify remote code execution.
 watchtowrlabs/watchtowr-vs-citrix-netscaler-cve-2026-88771
Detection artifact generator for Citrix NetScaler CVE-2026-88771, exploiting a pre-auth command injection to achieve remote code execution against…
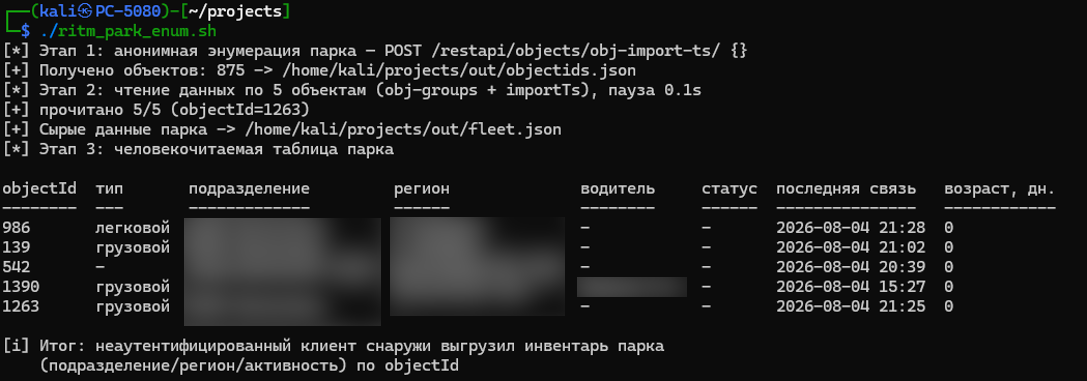 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.
 eqstlab/cve-2026-85706
PoC and Docker lab for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE via the commits API route bypass and urlencoded error…

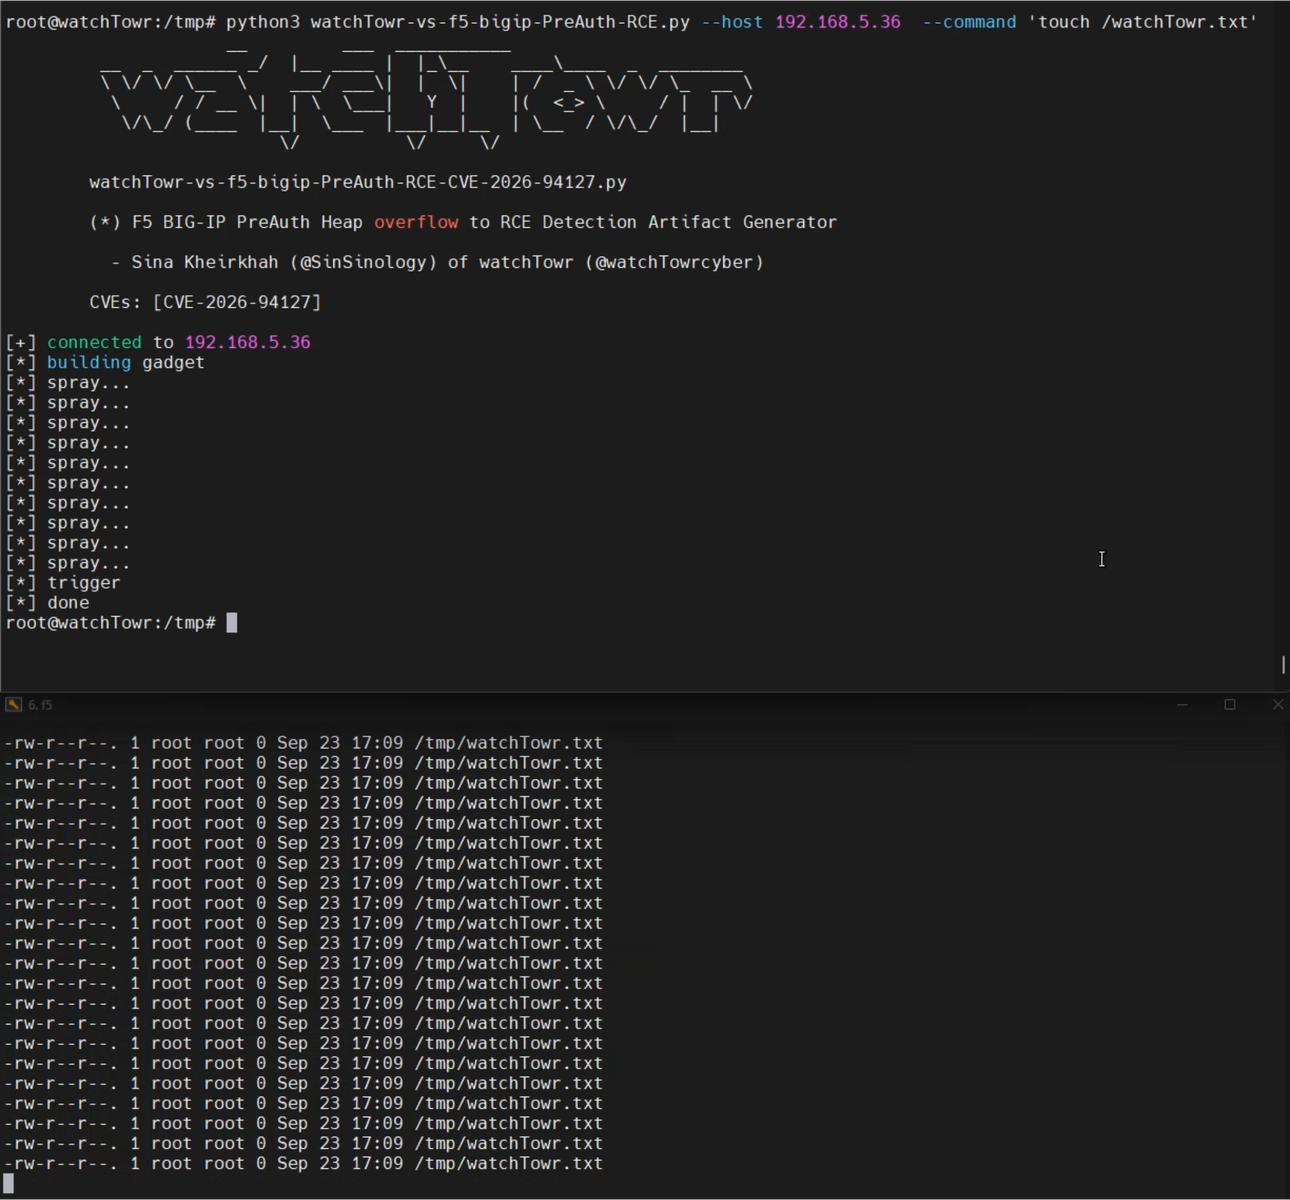 watchtowrlabs/watchtowr-vs-f5-bigip-preauth-rce-cve-2026-94127
Python detection artifact generator and PoC for CVE-2026-94127, a pre-auth RCE in F5 BIG-IP reachable via OAuth-configured virtual servers, with…
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 r3vpwnx/cve-2025-58434
Exploit chain for Flowise 3.0.5: unauthenticated account takeover via password-reset token disclosure (CVE-2025-58434) chained to CustomMCP…
 romain-deperne/cve-2026-40864
Proof-of-concept for CVE-2026-40864: JupyterHub XSRF bypass via cross-origin form POST exploiting Sec-Fetch-Mode: no-cors. Includes PoC HTML, root…
 feartheploto/gitlab-cve-2023-7028
Mock vulnerable GitLab instance reproducing CVE-2023-7028 password reset hijack. Demonstrates array-based email parameter exploitation and account…
 0xlyvio/cve-2020-10770-keycloak-exploit-poc
Step-by-step guide to reproduce the Keycloak blind SSRF vulnerability (CVE-2020-10770) with Docker setup, listener configuration, and mitigation…
 ming1700/cve-2026-38192
pluck-CMS-4.7.20-code-injection-vulnerability
 biitts/cve-2026-82286-gpt-crawler-arbitrary-file-write
CVE-2026-82286 — gpt-crawler <=1.5.1 unauthenticated arbitrary file write via outputFileName (POST /crawl). PoC + self-contained Docker lab. CVSS…
 eqstlab/cve-2026-72898
Unauthenticated blind SQL injection exploit for Metabase, exploiting a raw SQL injection in the password reset endpoint to extract data via…