

Vigil
 vigiloss/vigil
AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
ai-securitycode-analysisexploitation+9
33
vigiloss/vigilAI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
 wtfkimi/cve-2026-77078
Example repository demonstrating how to exploit CVE-2026-77078 in multer, with usage instructions in English and Russian.
 s3v3n-jg/cve-2026-76461
Intentionally vulnerable Python lab demonstrating unsafe YAML deserialization leading to code execution, with three difficulty levels, exploit…
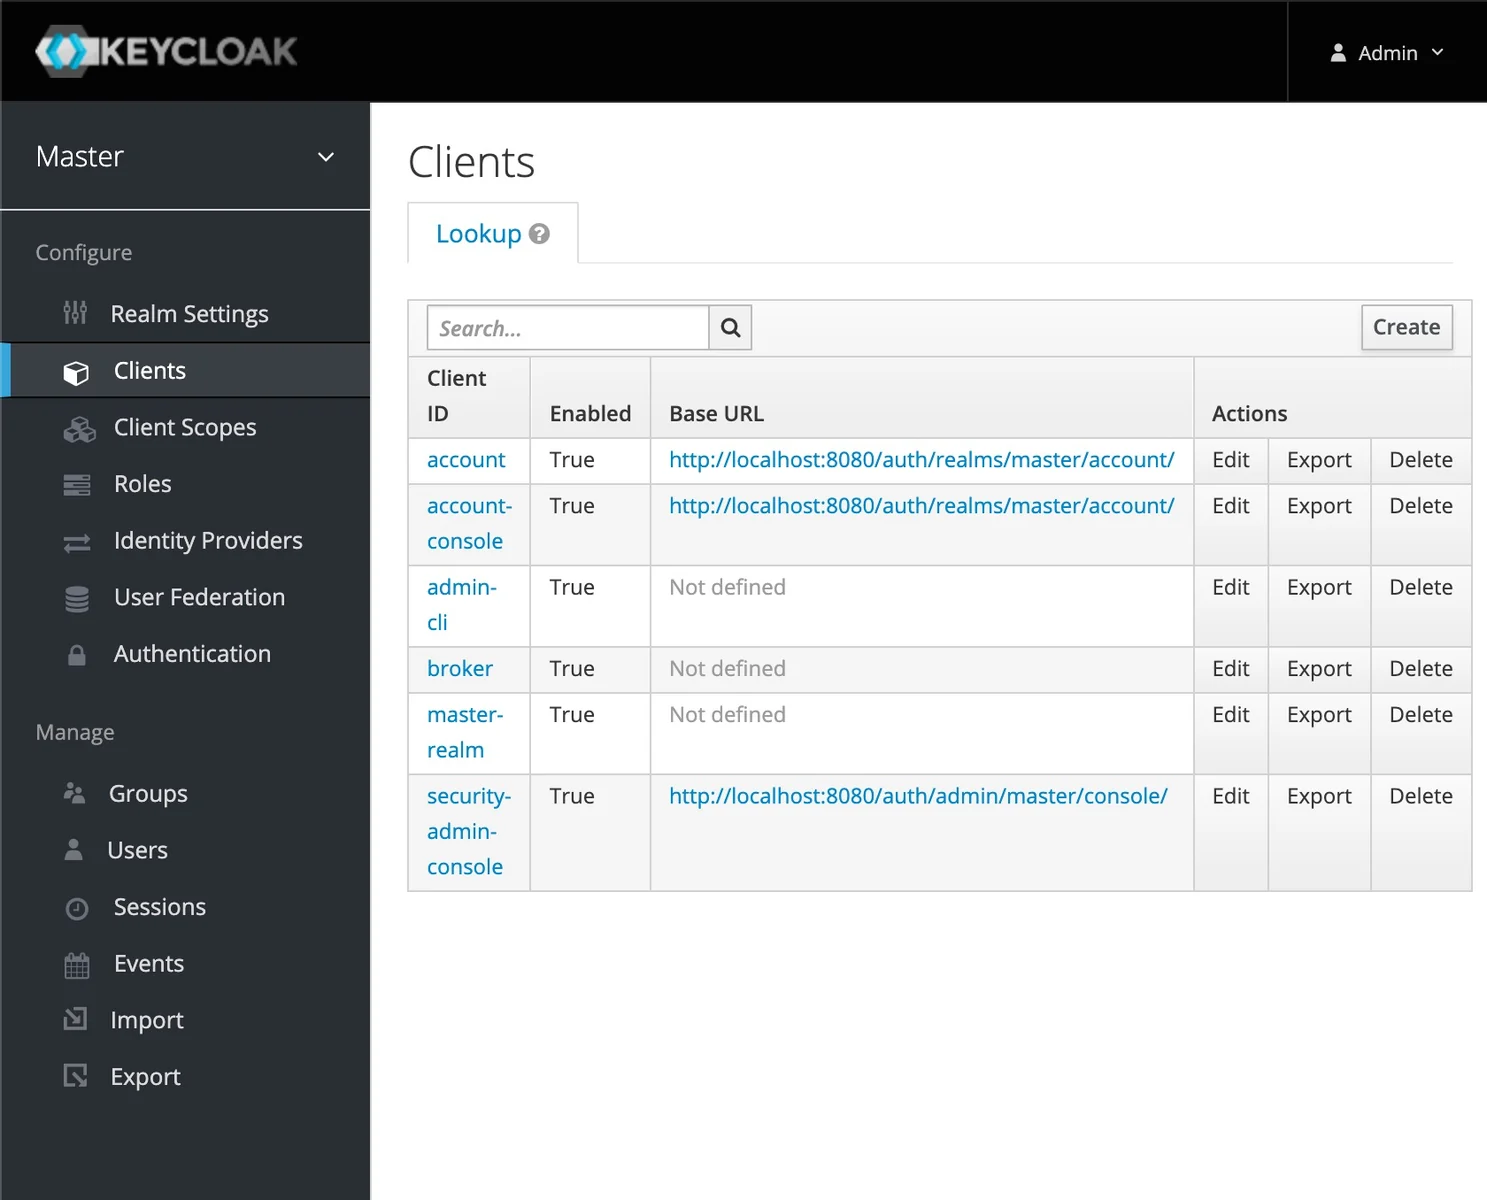 0xlyvio/cve-2020-10770-keycloak-exploit-poc
Step-by-step guide to reproduce the Keycloak blind SSRF vulnerability (CVE-2020-10770) with Docker setup, listener configuration, and mitigation…
 oscerd/cve-2026-71300
Proof-of-concept reproducer for Apache Camel camel-atmosphere-websocket dispatch header injection (CVE-2026-71300), demonstrating how an injected…
 makarov05bm/wsgoat
The vulnerable application that will teach you how to hack WebSockets
 george0papasotiriou/cve-2026-1010-websocket-connection-smuggling-via-malformed-upgrade-header
Proof-of-concept exploit for CVE-2026-1010, demonstrating WebSocket connection smuggling and request splitting through a malformed Upgrade header…
 benedictejepu/cve-2024-24945-nginx-rift---tryhackme-lab-walkthrough
This lab demonstrates the exploitation of CVE-2024-24945, a heap corruption vulnerability affecting NGINX. The objective was to understand how memory…
 baburkin/struts-uploader-vulnerability
Research of exploit options for CVE-2024-53667 and their remediation
 jenderal92/zimbra-valid-login-checker
Lightweight Python script to test username/password combinations against Zimbra webmail login pages for security assessments and password auditing.
 0xdak/cve-2026-32136_exploit
Proof-of-concept exploit for CVE-2026-32136: unauthenticated authentication bypass in AdGuard Home via HTTP/2 cleartext (h2c) upgrade. Demonstrates…
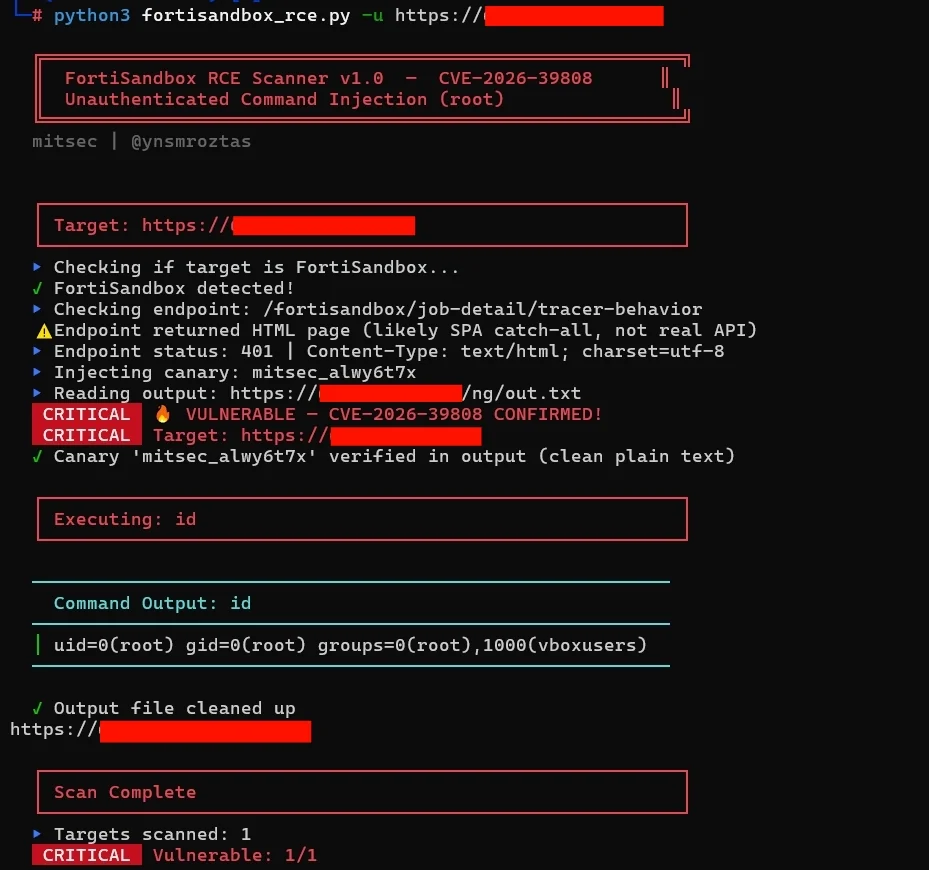 ynsmroztas/fortisandbox-rce-exploit-cve-2026-39808
Unauthenticated RCE scanner for FortiSandbox CVE-2026-39808 with canary-based verification, command execution, and pipeline integration for mass…
 cybermaksx/cve-2022-46364-proof-of-the-concept
This vulnerability allows an attacker to perform SSRF (Server-Side Request Forgery) attacks on Apache CXF webservices that accept MTOM/XOP requests.…
 echosecure/vuln-chain-lab
PoC Docker lab: chaining file upload bypass + stored XSS to create admin accounts. Educational resource for pen testers.
 ahmadf77/cve-2026-23744
Python exploit script for CVE-2026-23744 that delivers a reverse shell to a specified target URL, requiring a netcat listener for command-and-control.
 zenniskayy2k4/cve-2024-36039_poc
PoC for CVE-2024-36039: Demonstrating SQL Injection via PyMySQL Object-to-String serialization flaw
 lavanya2085/solar-exploiting-log4j
This repository provides a detailed walkthrough of the *Solar Exploiting Log4j room* on TryHackMe, focusing on exploiting the critical Log4Shell…
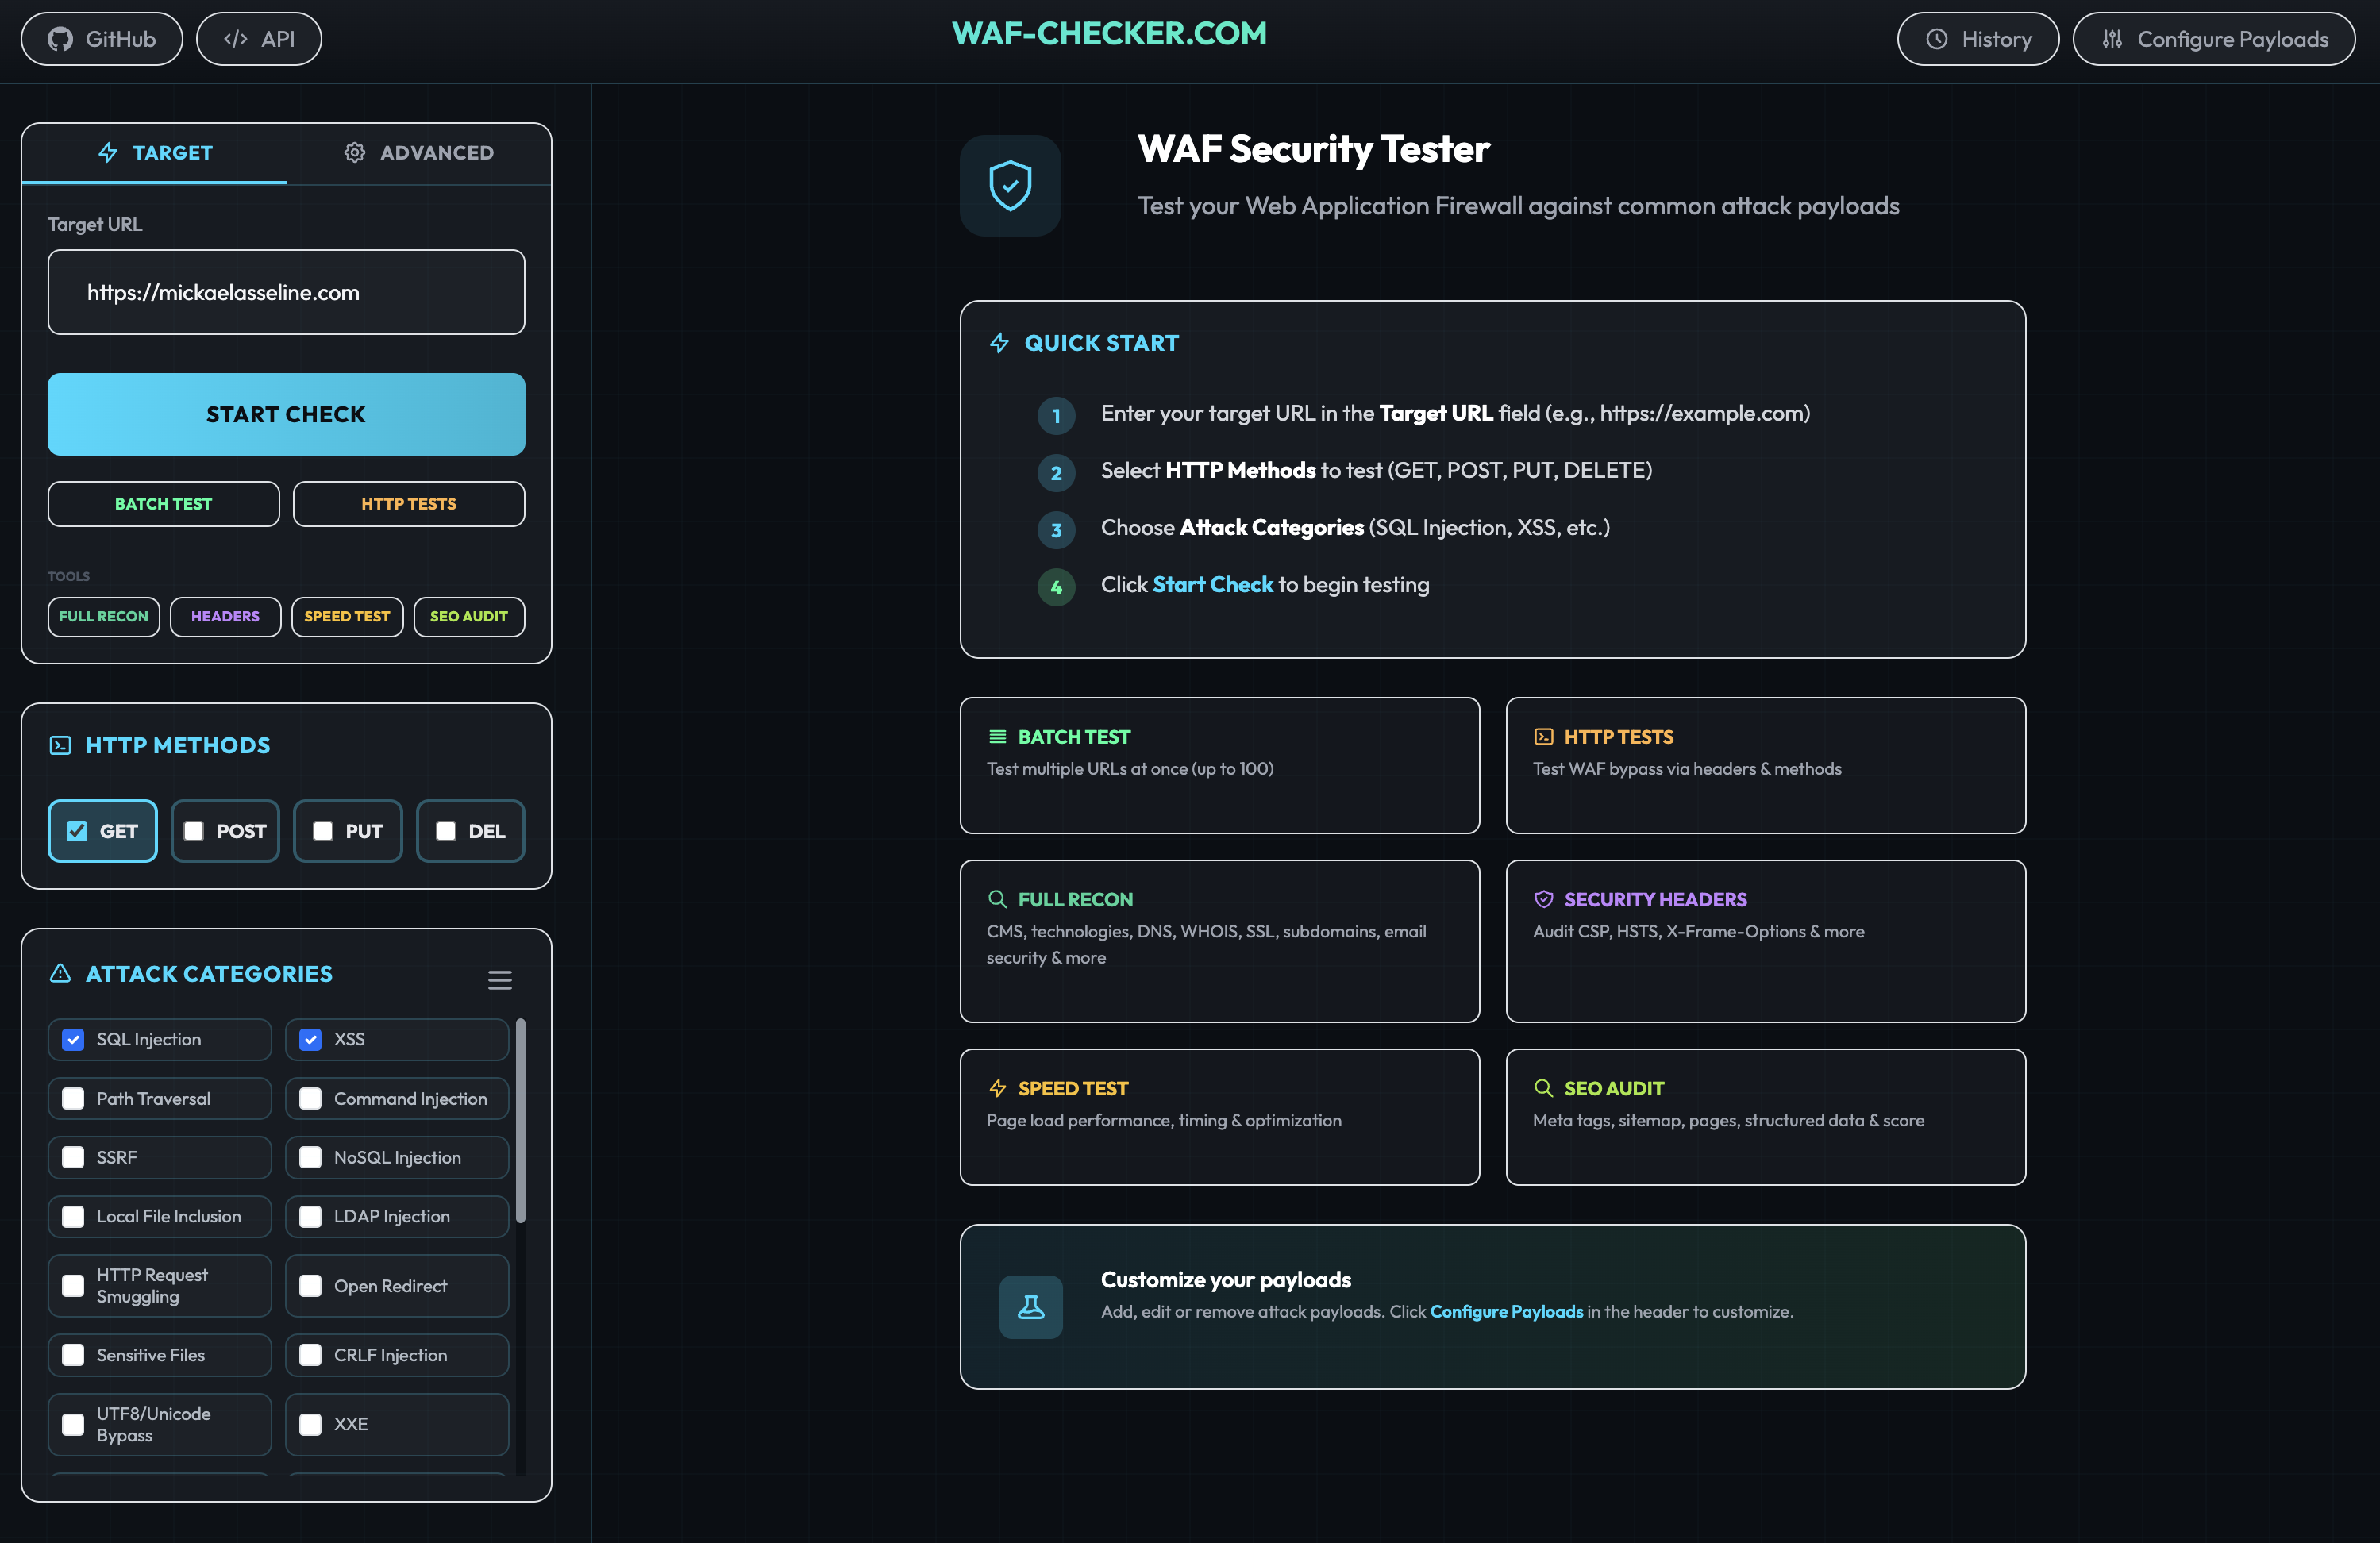 papamica/waf-checker
Tests your WAF with +160 payloads